
Method for authentication of elements of a group
A component and verification request technology, which is applied in the field of component verification to achieve the effect of reducing time and storage space
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2006-04-12
- Estimated Expiration
- Not applicable · inactive patent
Smart Images
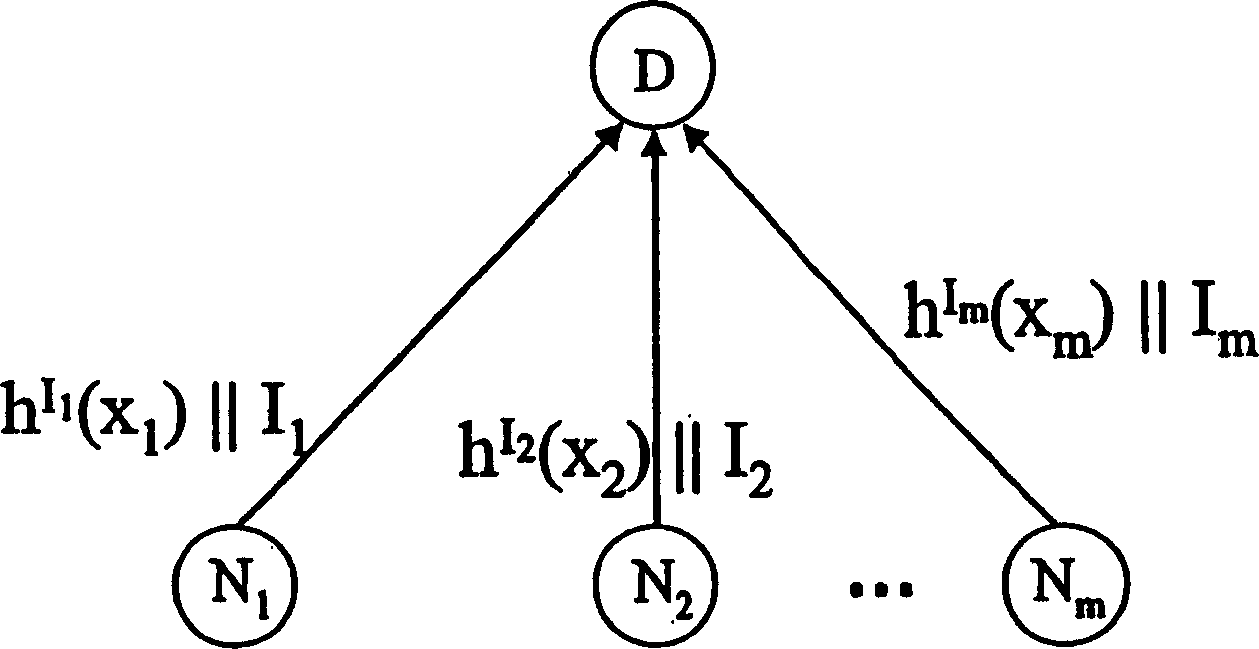
Figure 1 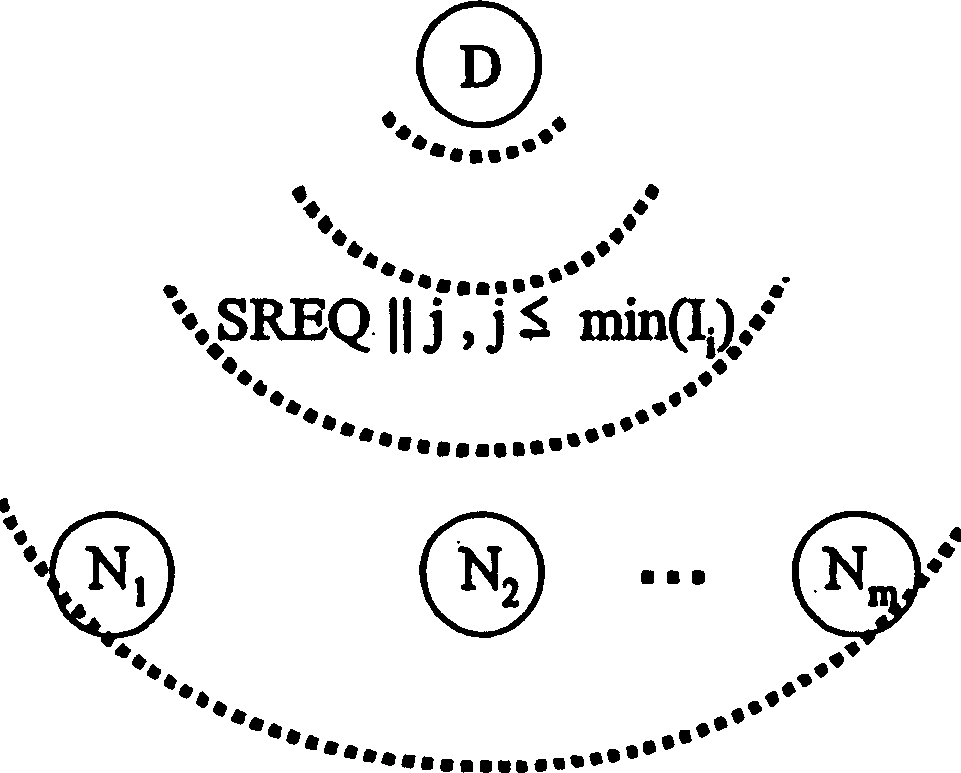
Figure 2 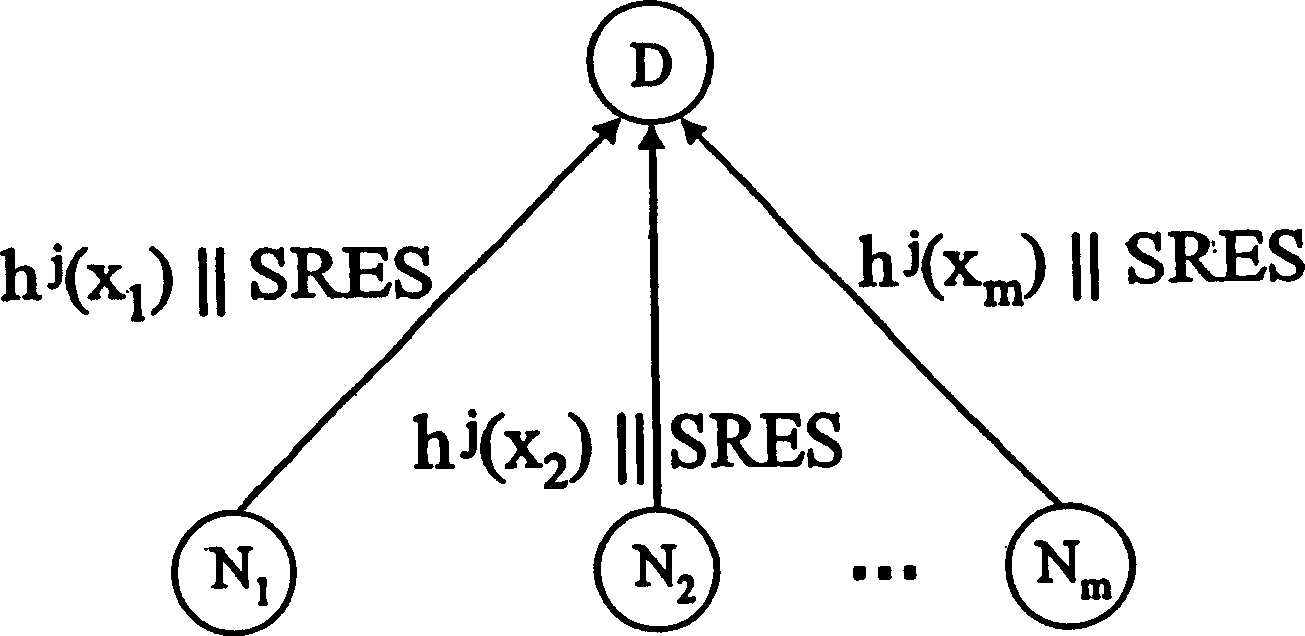
Figure 3
Abstract
Description
technical field
[0001] The present invention relates to a method of authenticating components, more particularly to a method of authenticating preferably sensor nodes in a wireless sensor network, wherein said group has a specific element in it - a bootstrap element, with which the group Each element in can exchange information and verify components against the bootstrap element. Background technique
[0002] In fact, different verification methods have been disclosed for a long time. In these cases, authentication is used to provide identity and to prevent unauthorized entities from being able to generate information that should only be generated by defined groups. In order to prove its authorization, a party must prove certain characteristics to a second party during the verification process. Once the required proof is given, ie, the verification process is successful, a party identified as authorized may be allowed access to information that is not publicly accessible. ...
Examples
Embodiment Construction
[0024] refer to figure 1 , shows the initialization phase before the actual verification process. The group shown includes a leading element D and a total of m components N i (here, i=1,...,m), where, for clarity, only three elements N are shown 1 , N 2 and N m . It should be appreciated that initialization occurs in a protected environment where potential attacks can be excluded. In the case of wireless sensor networks, the initialization phase can be performed in the ensemble, or in parts thereof, before configuring the individual sensor nodes.
[0025] During the initialization phase, the component N i First of all, they are all unified to the shared hash function h(). In addition, each component N i (where i=1,...,m) defines a key x known only to the component itself i . For example, key x i Can be component N i generated random number. According to the key x i , each component N i Perform the hash function iteratively, that is, for the first pair of keys xi...