
A method for Android system vulnerability detection based on vulnerability poc
A vulnerability detection, Android system technology, applied in computer security devices, instruments, computing, etc., can solve the problems of low detection efficiency, incomplete detection content, and poor user experience, so as to achieve comprehensive detection content and vulnerability maintenance workload. Less, improve the effect of user experience
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Patents(China)
- Current Assignee / Owner
- Publication Date
- 2020-12-11
Smart Images
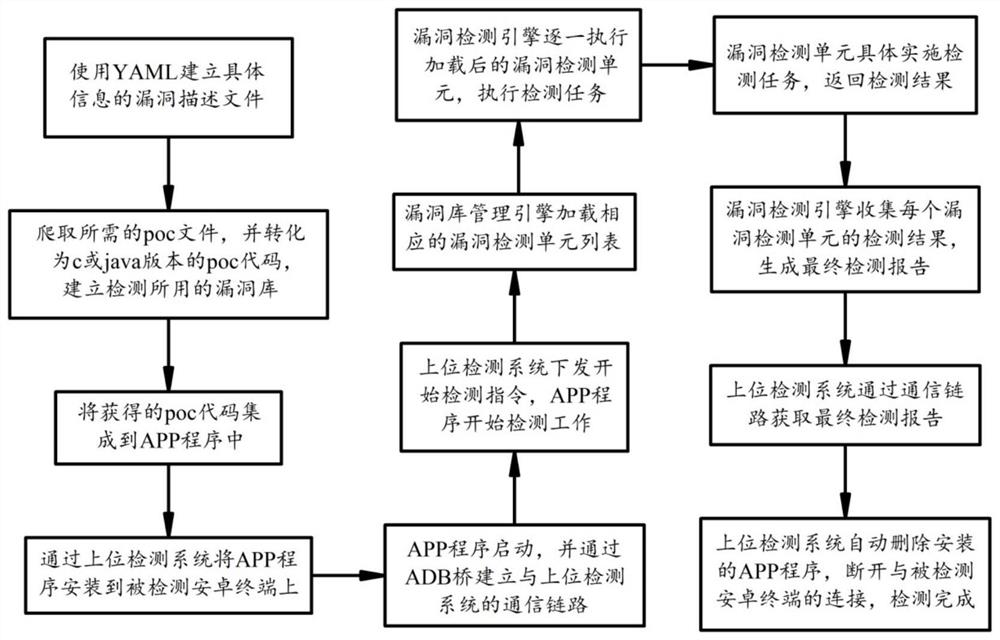
Figure 1
Abstract
Description
technical field
[0001] The invention belongs to the technical field of Android system security protection, and in particular relates to a method for detecting Android system vulnerabilities. Background technique
[0002] With the increasing popularity of the Internet and smart mobile terminals in people's lives, mobile security issues and hidden dangers are becoming more and more serious. At present, the incidents of implanting malicious codes on mobile terminals for cybercrime are on the rise, and users of mobile terminals are facing unprecedented security risks. Especially for smartphones with Android system, based on the open source of the source code, the security risks of various smart products developed by it have attracted people's attention. Vulnerabilities in the Android system may be exploited by various viruses and Trojan horses, resulting in many damages such as online banking theft, monitoring, unreasonable fee deductions, privacy leaks, and becoming a source o...
Examples
Embodiment Construction
[0036] All the features disclosed in this specification, except mutually exclusive features and / or steps, can be combined in any way.
[0037] Combine below figure 1 The present invention will be described in detail.
[0038] A method for realizing Android system vulnerability detection based on the vulnerability POC belongs to the category of active detection, and the executor of the detection is an APP program, including the following steps:
[0039] Step 1 (S1): crawl the required vulnerability information from CVE and other public vulnerability websites, and use YAML to create a vulnerability description file with specific information;
[0040] Step 2: Crawl the required poc file from the public vulnerability website, and convert it into c or java version of the poc code, and use YAML and poc code to build the vulnerability library used for detection;
[0041] Step 3: Develop an APP program for detection. The APP program has functions such as vulnerability library manage...