

Patents
Literature
5399 results about "Source code" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
In computing, source code is any collection of code, possibly with comments, written using a human-readable programming language, usually as plain text. The source code of a program is specially designed to facilitate the work of computer programmers, who specify the actions to be performed by a computer mostly by writing source code. The source code is often transformed by an assembler or compiler into binary machine code understood by the computer. The machine code might then be stored for execution at a later time. Alternatively, source code may be interpreted and thus immediately executed.
Web application internationalization
InactiveUS7784026B1Eliminate needEasy constructionExecution for user interfacesMemory systemsMeta levelWeb page
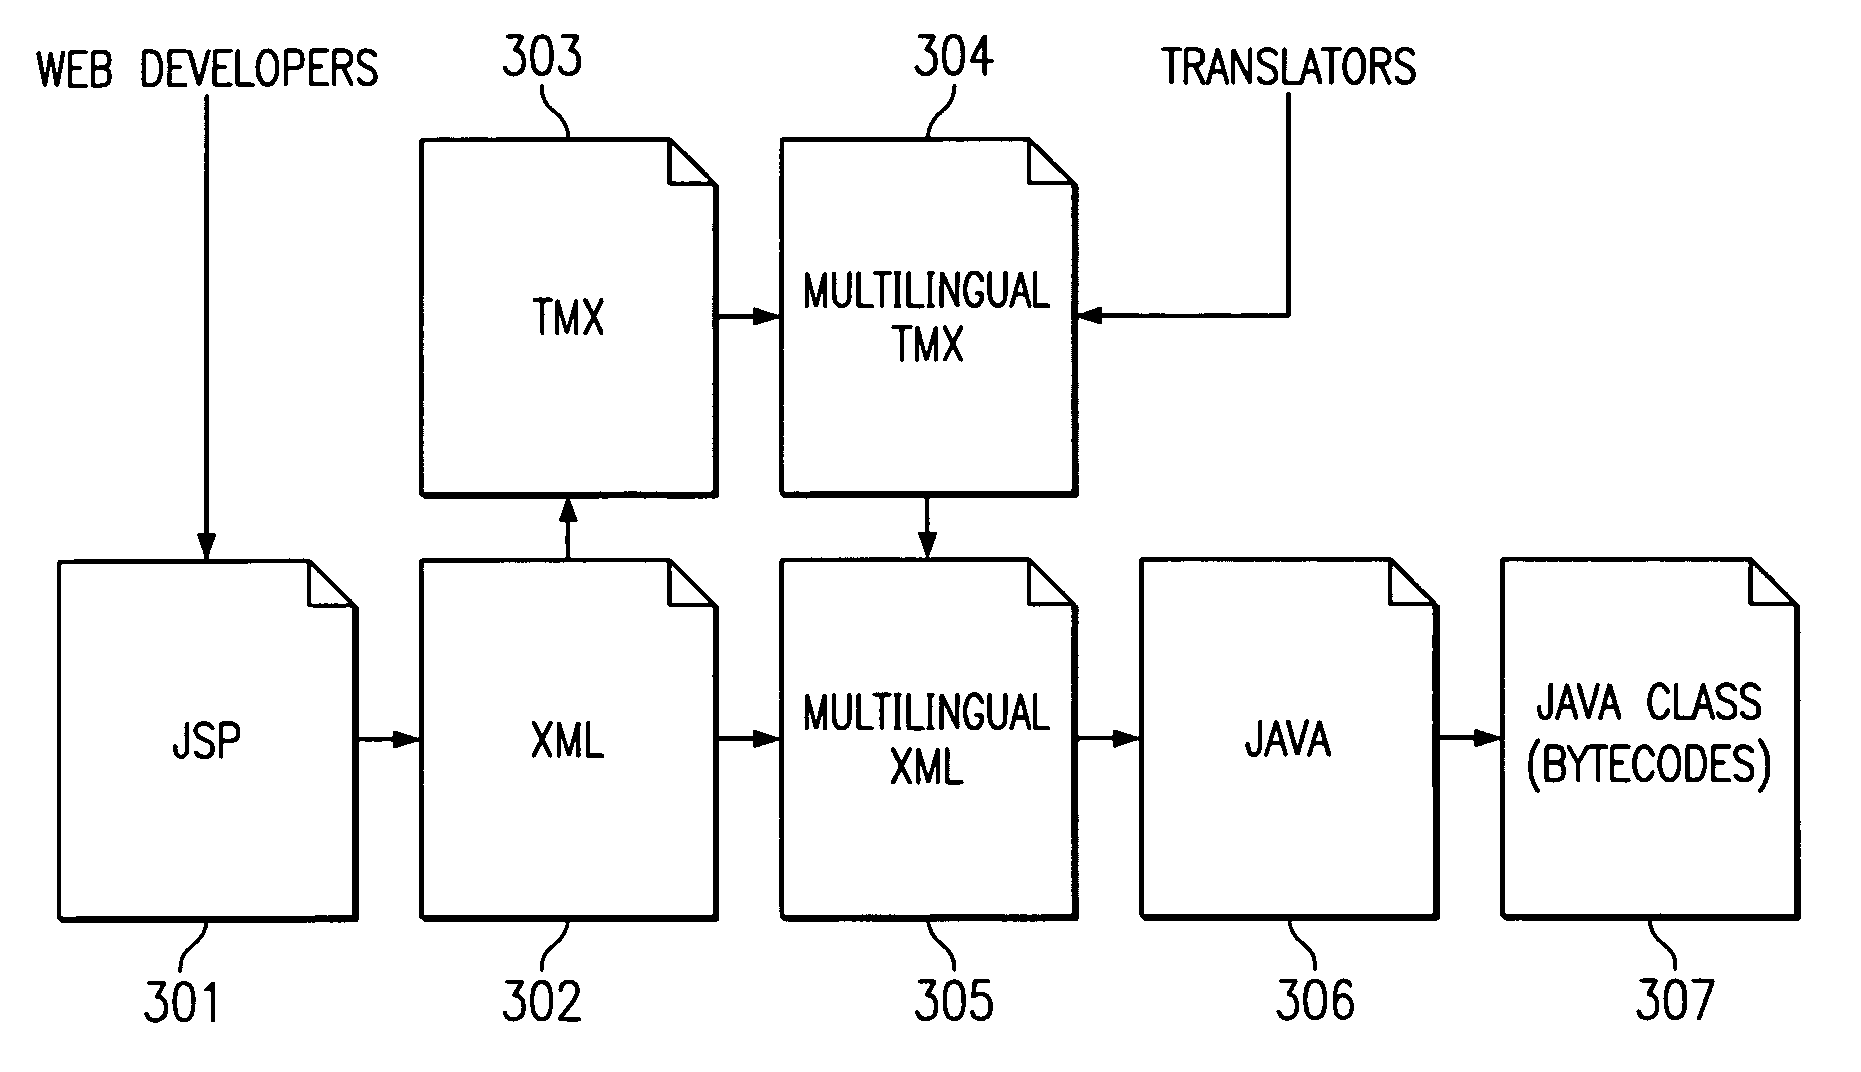
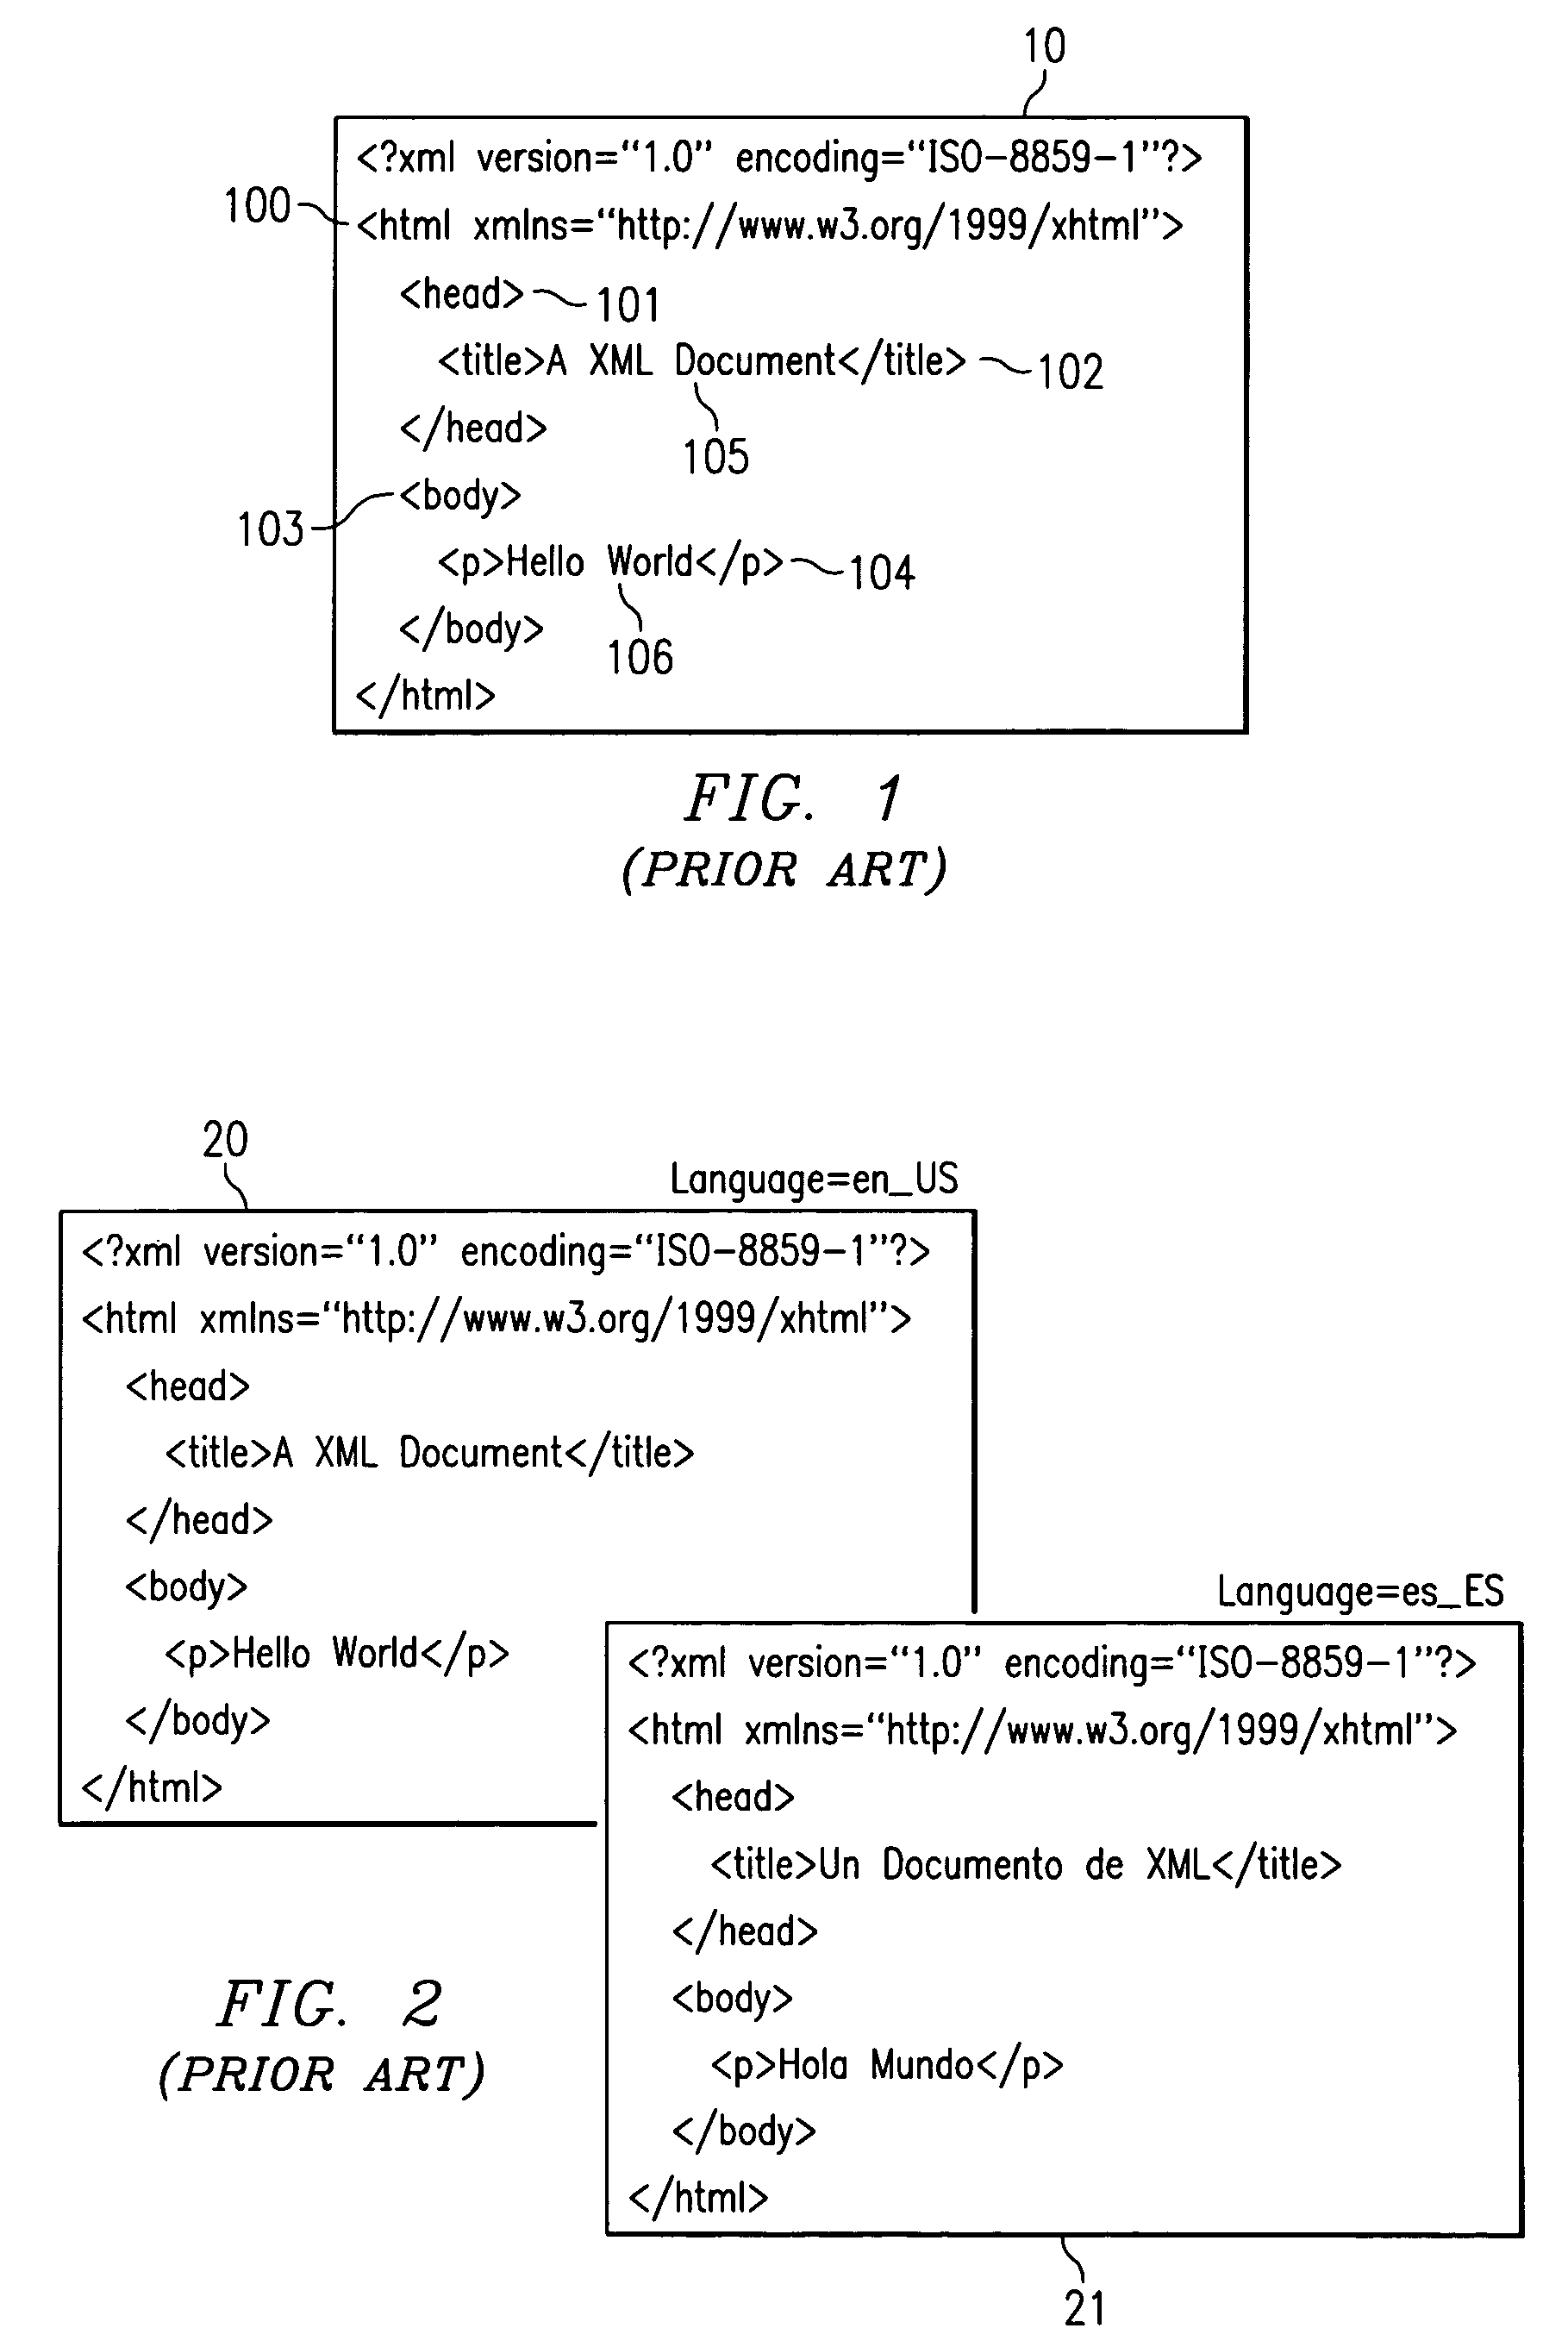
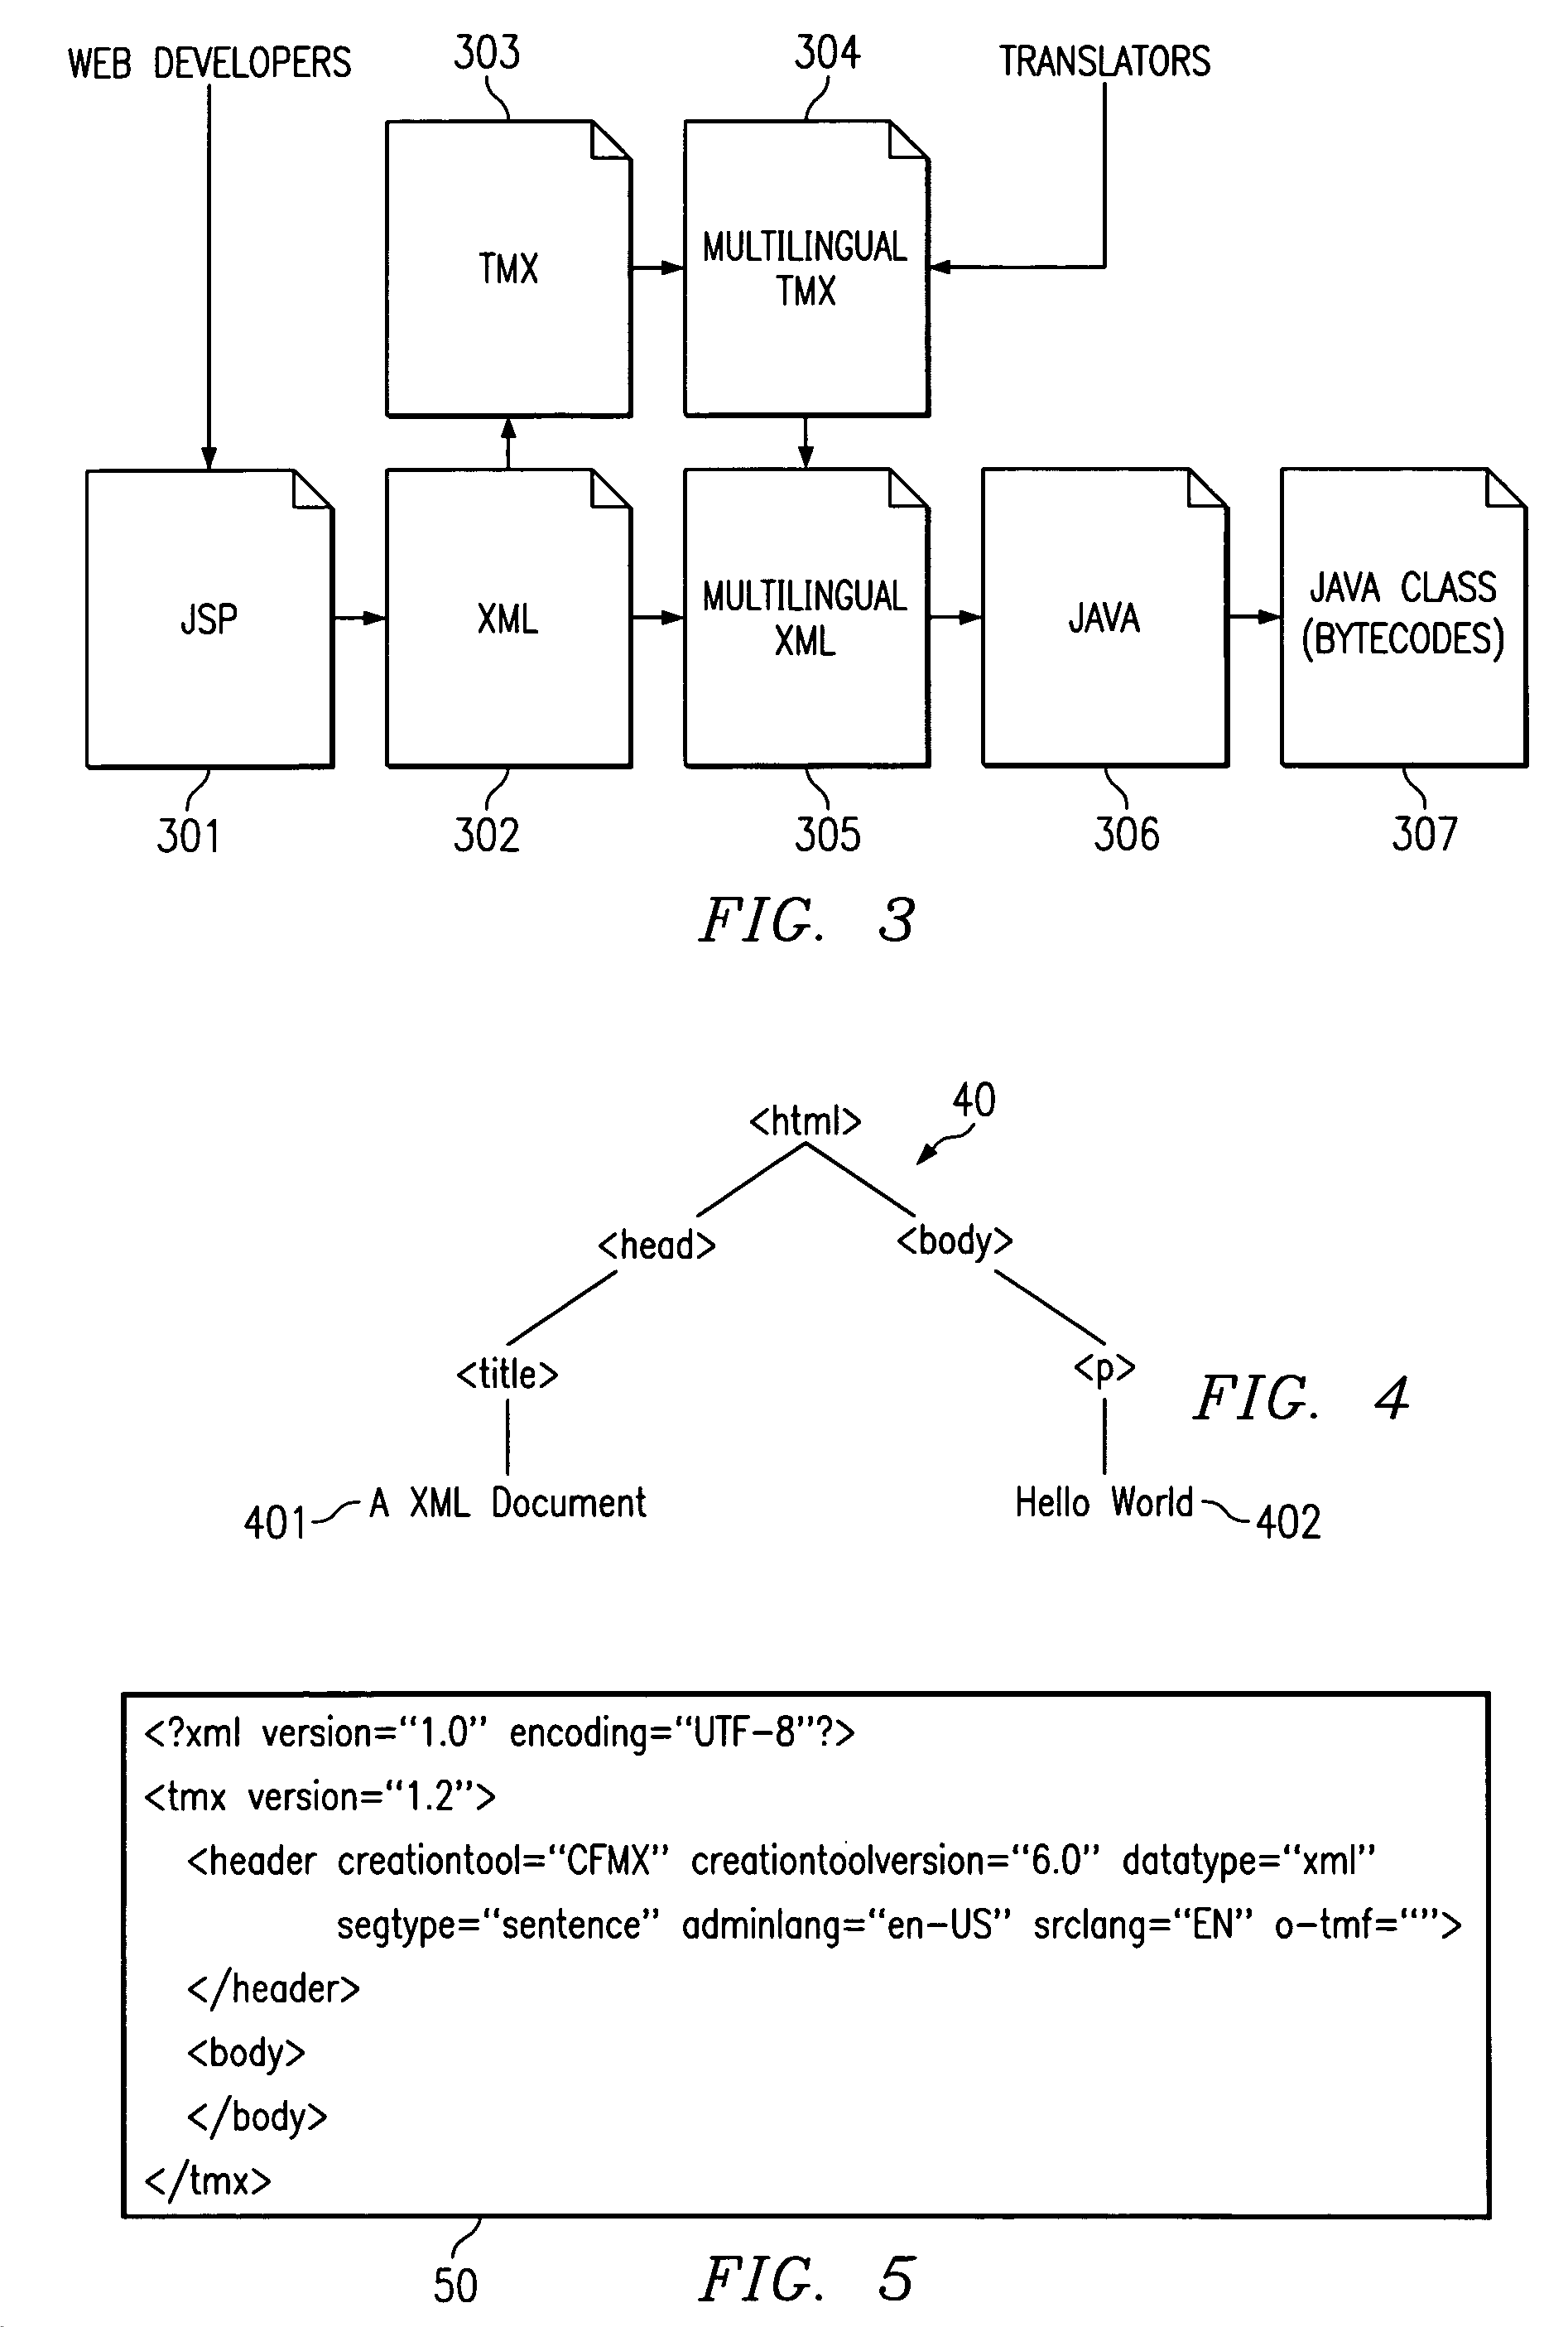
A system and method is described for internationalization of web pages by extracting translatable content from extensible mark-up language (XML), or similar data-centric meta-language representations of web pages or data used to build web pages. The extracted translatable content is stored in a translation task repository (TTR) accessible by the web developer and the translator. The XML representation is then modified to include selection control logic to select the appropriate translations for insertion into the final web page. The translator accesses the TTR to translate the appropriate content and saves the translations back to the TTR associated with the original translatable data. The translations are obtained from the TTR as selection cases for the selection control logic of the XML representation. As the XML is converted into the web source code, the selection logic and translations are embedded therein facilitating building the web site in multiple different languages.
Owner:ADOBE INC
Dynamic generation of features based on software testing
An example operation may include one or more of receiving, via a user interface, a request to test a software program, reading source code of the software program and identifying a vulnerability in the source code based on the reading, generating repair code for fixing the identified vulnerability based on execution of a generative artificial intelligence (GenAI) model on the source code and a repository of repair code used to repair previous vulnerabilities, and displaying information about the repair code via the user interface.

Owner:THE TORONTO DOMINION BANK
Security testing based on generative artificial intelligence
An example operation may include one or more of executing tests on a software application via a test environment of a test platform and logging results of the tests in a log file, identifying a new feature to be added to the software application based on execution of a machine learning model on logged results of the tests stored in the log file, generating source code for the new feature to be added to the software application based on execution of a generative artificial intelligence (GenAI) model on the new feature and a repository of source code, and displaying the generated source code via a user interface of the software application.

Owner:THE TORONTO DOMINION BANK
Correcting security vulnerabilities with generative artificial
An example operation may include one or more of monitoring communications that occur with user devices over a shared computer network, detecting a security threat from the monitored communications, generating a software program to simulate the security threat over the shared computer network based on execution of a generative artificial intelligence (GenAI) model on a description of the security threat and a repository of source code, installing the source code for simulating the security threat on a system associated with the computer network, and executing the source code for simulating the security threat via the system.

Owner:THE TORONTO DOMINION BANK
System and methods for managing user accessibility of webpages
A computer-implemented method is disclosed. The method includes: obtaining web content of a webpage; determining whether the web content complies with defined first requirements for user accessibility; in response to determining that the web content does not comply with the first requirements: identifying non-compliant web content elements of the webpage; and presenting, via a user interface of a source code editor: indications of first portions of source code for the webpage corresponding to the non-compliant web content elements; and a user interface element representing an action for altering one or more of the non-compliant web content elements.

Owner:THE TORONTO DOMINION BANK
Service design coordination among developers
An example operation may include one or more of receiving a first code base and a second code base from a software repository, wherein each of the first and second code bases comprise source code of a plurality of different software programs, identifying a source code within the first code base that is interdependent with a source code within the second code base based on execution of a generative artificial intelligence (GenAI) model on the first and second code bases, determining a software component to connect the source code within the first code base to the source code within the second code base, and displaying an identifier of the software component via a user interface.

Owner:THE TORONTO DOMINION BANK
Code-change based prompt for code repair
ActiveUS20240403438A1Platform integrity maintainanceNon-redundant fault processingAlgorithmTheoretical computer science
A source code repair system generates a prompt including a few-shot examples of code changes made previously to correct a particular source code vulnerability. The prompt is given to a large language model to generate repair code for a source code snippet having the same vulnerability. Code changes made for a particular source code vulnerability, in the form of code diffs, are clustered into groups of closely related code change embeddings. A select few of the code diffs in each group having a closest mean of the cluster are used as the few-shot examples for the corresponding source code vulnerability.

Owner:MICROSOFT TECHNOLOGY LICENSING LLC
LLM integrations for data visualization in spreadsheet environments
Technology is disclosed herein for the integration of spreadsheet environments with an LLM service. In an implementation, an application receives a natural language input from a user associated with visualization of data hosted by the application. The application generates a prompt for a large language model (LLM) service based on the user input and the visualization and submits the prompt to the LLM service. The application receives a reply to the prompt from the LLM service and modifies the visualization based on the reply from the LLM service. In an implementation, the data includes spreadsheet data and the visualization includes a chart. In some implementations, to modify the visualization, the application generates source code based on the reply from the LLM service when the classification of the natural language input is a command.

Owner:MICROSOFT TECHNOLOGY LICENSING LLC
Localizing vulnerabilities in source code at a token-level
ActiveUS20240411666A1Software testing/debuggingComputer security arrangementsLinguistic modelTheoretical computer science
A vulnerability detection and repair system utilize a classifier model to detect a software vulnerability in a source code snippet and the tokens in the source code snippet attributable to the vulnerability. A large language model is then given the vulnerable source code snippet, its vulnerability type, the vulnerability tokens, and a few-shot examples to determine whether or not the source code snippet includes the identified vulnerability. The few-shot examples include positive and negative samples of the type of vulnerability to guide the large language model towards the correct output.

Owner:MICROSOFT TECHNOLOGY LICENSING LLC
Zero-code software development and test system based on artificial intelligence
PendingCN119148988ALower technical barriersquality improvementSemantic analysisSoftware testing/debuggingCode generationTest script
The invention relates to the technical field of software development, in particular to a zero-code software development and test system based on artificial intelligence, and provides the following scheme that the system comprises a natural language analysis module, a code generation module, a code optimization module, an intelligent test module and a cross-platform deployment module. The natural language analysis module analyzes the natural language description input by the user into a software development requirement document; the code generation module generates source codes based on the demand document and can select a programming language and a framework; the code optimization module is used for performing static analysis and reconstruction optimization on the generated codes; the intelligent test module automatically generates a test script through interface model extraction, case generation and case analysis logic, executes a test and feeds back a test result; and the cross-platform deployment module realizes automatic packaging, compatibility check, deployment configuration and release management of software. The invention aims to simplify the software development process and improve the development efficiency and quality.

Owner:JIANGSU LINGHAO NETWORK TECH CO LTD +1
Systems and Methods for Software Development Using Machine Learning Models
PendingUS20240427566A1Version controlSoftware testing/debuggingTheoretical computer scienceEngineering
Systems and methods for software development using machine learning models are disclosed. In one embodiment, a method for programmatically generating source code using a machine learning model includes obtaining a set of project configuration information that defines a programming task, indexing original source code in a code repository, advancing the programming task by constructing a prompt to a machine learning model to obtain new source code as an output, writing the new source code to the code repository, identifying an intervention request that requires human input to complete the programming task, obtaining human input for the intervention request from a human using digital communications as an outcome, and writing the intervention request and outcome to an intervention database.

Owner:PROVOKE SOLUTIONS LLC
Systems and methodologies for auto labeling vulnerabilities
A system and methodology for automated security assessment of microservices includes a microservice composition model, data gathering, security assessment, and labeling components. It treats microservices as separate projects, collecting source code, dependencies, and runtime information. The security assessment employs tools to analyze code, track vulnerabilities, and identify risks. Predefined rules categorize microservices and assign security state labels. A hidden Markov model predicts security states based on historical data, enabling proactive security management and risk mitigation.


Owner:CLOUDBLUE LLC
Source code detection method
InactiveCN119442240AAccurate detectionincrease coverageSoftware testing/debuggingPlatform integrity maintainanceCluster algorithmSupport vector machine
The invention relates to the technical field of software engineering, in particular to a source code detection method, which comprises the steps of source code preprocessing, code dependency analysis, semantic understanding and analysis, code quality evaluation, dynamic behavior simulation, intelligent vulnerability detection and the like to realize comprehensive detection of potential vulnerabilities and quality problems in source codes. A support vector machine and a K-means clustering algorithm are combined, known and unknown vulnerabilities can be effectively recognized, in addition, a continuous optimization feedback mechanism is introduced, a mixed vulnerability detection model can be continuously optimized according to repair operation and feedback information of a developer, the detection accuracy is improved, and the coverage range is expanded. The generated comprehensive detection report covers code structures, vulnerability positioning, quality problems and optimization suggestions, supports integration of various output formats and development tool chains, helps developers to efficiently repair problems, and improves code quality and project progress; according to the method, the comprehensiveness, the self-adaptability and the user experience of code detection are effectively improved.

Owner:HLJ E LINK NETWORK CORP LTD
Software architecture code generation method and system based on large language model
The invention relates to the technical field of computer processing, in particular to a software architecture code generation method and system based on a large language model, and provides the following scheme: obtaining demand information input by a user, analyzing demands by using a natural language processing technology, and extracting functional elements; performing classification processing on the functional elements through a clustering algorithm to generate a functional module group; mapping the function module group to a system architecture layer, and generating an architecture diagram represented by UML (Unified Modeling Language); and generating a corresponding source code according to the UML graph, and optimizing the source code. The optimization strategy comprises static analysis of format problems and potential vulnerabilities in identification codes and performance optimization of complex functions. Through combination of the large language model and the automatic code generation and optimization technology, the software development efficiency is improved, manual intervention is reduced, and the correctness and maintainability of the generated code are ensured.

Owner:未分类(SHANGHAI) TECHNOLOGY CO LTD
Identification of Variants of Artificial Intelligence Generated Malware
Source code for a type of malware is received. For example, the source code may be source code from a type of computer virus. An Artificial Intelligence (AI) algorithm is identified. For example, the AI algorithm may be ChatGPT. The source code of the type of malware is run through the AI algorithm to produce mutated source code for the type of malware. A prediction algorithm is used to predict a signature of the mutated source code for the type of malware. For example, the prediction algorithm is trained using existing source code of different types of malware to generate a prediction model. The signature of the mutated source code for the type of malware is then compared to a signature of a potentially new type of malware to determine if the signatures are similar.

Owner:MICRO FOCUS LLC
Security data penetration testing method
ActiveCN119377969AError detection/correctionPlatform integrity maintainanceDynamic monitoringMemory model
The invention provides a security data penetration test method. The method comprises the steps of pre-establishing a multi-thread application program race condition vulnerability feature library, performing static analysis on source codes of a target application program, identifying potential race condition vulnerability points, and obtaining a preliminary vulnerability candidate set; for monitored suspected race condition events, abstracting event context information into constraint conditions, exploring an input combination of suspected static conditions by using a constraint solver, and determining a minimum input set of stable triggering race conditions; aiming at memory models and synchronous primitives of different programming languages, obtaining a race condition inverse mode, and extracting universal utilization primitives covering various race condition vulnerabilities; in the penetration test process, static analysis, dynamic monitoring and symbolic execution are applied to mine race condition vulnerabilities of a target application system, the availability of the vulnerabilities is verified, and evaluation of system security is assisted to be completed.

Owner:JIANGXI LIANCHUANG ELECTROACOOUSTIC CO LTD
Automated code scanning for pre-emptive issue detection and resolution
ActiveUS20240419575A1Software testing/debuggingReverse engineeringAlgorithmTheoretical computer science
An issue source scanning system scans a source of information about an issue to identify characteristics of code which indicate that the issue will manifest in code. A code scanning system scans code to match the identified characteristics against the code to determine whether the source code includes the identified characteristics. The code scanning system automatically generates a suggested operation to perform based upon a match between the identified characteristic and the code.

Owner:MICROSOFT TECHNOLOGY LICENSING LLC
Methods and systems for security software patch type detection
Methods and systems are provided for security patch type detection of software patches. A software patch for a software product may be received. For example, the software patch may be received by a computing device. A pre-patch code property graph and a post-patch code property graph may be determined. For example, the pre-patch code property graph and the post-patch code property graph may be determined based on the software patch and / or the pre-patch source code and the post-patch source code respectively. A combined patch code property graph may be determined. For example, the combined patch code property graph may be determined based on the pre-patch code property graph and the post-patch code property graph. A patch type for the software patch may be determined. For example, the patch type may be determined based on the combined patch code property graph and / or a machine-learning prediction model.

Owner:GEORGE MASON UNIVERSITY
Source code vulnerability detection and repair through machine learning
A neural classifier model is used to detect cybersecurity vulnerabilities in the source code predicted by a deep learning code generation model having been trained on source code possibly containing security bugs. Upon the classifier model classifying a given source code snippet as likely containing a cybersecurity vulnerability, a proposed repair for the cybersecurity vulnerability is predicted from a neural decoder transformer model having been trained on non-vulnerable source code. The neural decoder transformer model is used to predict source code that repairs the cybersecurity vulnerability given the source code classified with a cybersecurity vulnerability.


Owner:MICROSOFT TECHNOLOGY LICENSING LLC
Causal chain-based front-end state anomaly detection method and system
The embodiment of the invention discloses a causal chain-based front-end state anomaly detection method and system. The method comprises the following steps: S1, identifying a calling relation among an event monitor, an asynchronous task and a state change logic by analyzing a source code, and constructing an expected causal chain model; s2, dynamically verifying whether the actually occurring causal chain conforms to an expected model or not during the application running period; wherein in the step S1, the analysis of the source code comprises but is not limited to an AST technology; in the step S2, the hijacking mode of the key function comprises but is not limited to a Proxy mechanism, function packaging and a Hook technology. According to the method, the expected causal chain model is constructed, the actual path is dynamically verified during operation, system inconsistency caused by causal chain abnormity is avoided, the AI model is utilized to generate the repair strategy suggestions, a traditional low-efficiency troubleshooting process depending on logs and breakpoint debugging is upgraded to intelligent decision, and the repair efficiency is remarkably improved.

Owner:HANGZHOU ANQUAN DIGITAL INTELLIGENCE TECH CO LTD
Code vulnerability detection method based on efficient parameter fine tuning of code pre-training model
ActiveCN119441006AImprove training efficiencyreduce gapTransformation of program codeInternal combustion piston enginesData setAlgorithm
The invention relates to the technical field of software reliability guarantee, in particular to a code vulnerability detection method based on efficient parameter fine tuning of a code pre-training model, which comprises the following steps: preprocessing source codes of a vulnerability data set; s2, converting the preprocessed source code, and extracting a token sequence and a code attribute graph path corresponding to the source code; s3, constructing a code vulnerability detection model, wherein the code vulnerability detection model comprises a semantic feature extractor, a structural feature extractor, a feature fusion layer and a classifier; s4, jointly training a code vulnerability detection model by using the token sequence corresponding to the extracted source code and the code attribute graph path; and S5, through the optimized code vulnerability detection model, outputting a result that whether the source code to be detected has vulnerabilities or not. According to the method, the model is finely adjusted through efficient parameter fine adjustment, training resources are saved, good performance is obtained, and the code vulnerability detection efficiency and accuracy are improved by fusing and learning semantic and structural features of source codes at the same time.

Owner:SOUTH CHINA UNIV OF TECH
Test case determination method and device, computer readable storage medium and processor
The invention discloses a test case determination method and device, a computer readable storage medium and a processor. The method comprises the following steps: identifying a source code of software by utilizing a pre-trained large model to obtain a plurality of functional modules in the software and a dependency relationship among the plurality of functional modules; in response to updating of the source code of the software, determining a code updating part in the source code; determining a test case matched with the code updating part from a test case library of the software based on the code updating part and a dependency relationship among the plurality of functional modules, the test case being used for testing the code updating part; based on a test result of the test case, adjusting a selection strategy of the test case; and re-determining the test case for testing the code updating part based on the adjusted selection strategy of the test case. The technical problem that a traditional regression test strategy is low in test efficiency is solved.

Owner:CHINA TELECOM ARTIFICIAL INTELLIGENCE TECHNOLOGY (BEIJING) CO LTD
System and method for transpilation of source code using machine learning
PendingUS20240411535A1Code compilationSource to sourceSoftware engineeringSchema for Object-Oriented XML
The disclosed system and method automate the transpilation of query source code to a distributed data processing system. The process involves instantiating transpiler libraries and source code, executing the source code, and transpiling the source code into a transpiled code using the transpiler libraries. A machine learning algorithm is utilized to control the operation of the transpilation process wherever different transpilation options are available as an automated mechanism for adapting transpilation based on tracked downstream operational characteristics. The system is configured for automatic source code generation in the target language as an output, which can then be deployed to a distributed data processing or query system. Variants are described using a combination of test and production environments for initial testing and tuning of the machine learning model architecture until a performance threshold is met. A same code segment may be transpiled periodically for continual automatic optimization.

Owner:HSBC GRP MANAGEMENT SERVICES LTD
Dynamic project planning for software development projects
ActiveUS20250045048A1Software testing/debuggingSoftware metricsSoftware engineeringSoftware development
Methods, systems, and apparatus, including computer programs encoded on computer storage media, for generating and updating project plans for software development projects. In one aspect, a method includes obtaining data indicative of initial project plan parameters associated with a software development project; identifying multiple program modules associated with the software development project; obtaining, for a first set of modules of the multiple modules, corresponding source code segments; executing a quality assessment process to compute, for each corresponding source code segment, a corresponding quality score; identifying, based on the quality scores, that at least a subset of the corresponding source code segments are integrable into a corresponding first subset of the first set of modules; and generating a revised project plan by generating updates to the initial project plan parameters by accounting for the corresponding source code segments being integrated in to corresponding ones of the first set of modules.

Owner:ACCENTURE GLOBAL SOLUTIONS LTD
Conversation-driven regression test generation method based on code big language model
PendingCN119046134AOpen the doorSoftware testing/debuggingCode compilationRegression testingLinguistic model
The invention discloses a dialogue-driven regression test generation method based on a code big language model, and belongs to the technical field of computers. Collecting and preparing a data set oriented to a C language program, wherein the data set comprises a source code, a corresponding test demand natural language description, a test case data constraint and an official test case example; determining an appropriate large language model; selecting a to-be-tested function from the data set and starting to generate a test case; prompt templates oriented to different types of C language programs are designed to guide the model to generate test cases of specific types and standard formats; performing semantic analysis on the test requirements by using the large language model and feeding back an analysis result to the large language model to deepen the understanding of the large language model on the test requirements; detecting whether the test input parameters for generating the test case are in one-to-one correspondence with the tested function parameters, and guiding the large model to correct the data type of the test case; and testing the generated test case, and generating a case quality evaluation report.

Owner:BEIJING JIAOTONG UNIV
Systems and methods for detecting vulnerabilities in software in real time
Systems and methods for detecting vulnerabilities in software in real time. In some aspects, the system receives a training dataset, including first source code, first runtime data flow, a set of sample vulnerable libraries, and a set of sample replacement software libraries. Using the training dataset, the system trains a vulnerability detection model. The system receives second source code being tested in a development environment and collects the second source code and second runtime data flow. The system processes the second source code and second runtime data flow using the vulnerability detection model to identify novel vulnerable software libraries and / or known vulnerable software libraries. The system generates suggestions to replace the known and / or novel vulnerable software libraries. In response to detecting a user choosing a first replacement library in place of a first vulnerable library, the system replaces the first vulnerable library with the first replacement library.

Owner:CAPITAL ONE SERVICES LLC
System and method for source code transformation
There is disclosed herein a method of providing protected access to a third-party generative artificial intelligence (GAI) for software development including transforming a source code input (a transformed source code) via a one-way transform, wherein an enterprise has a proprietary interest in the source code input, and wherein the one-way transform is not internally reversible; providing the transformed source code to the third-party GAI, in association with a query for the third-party GAI, wherein the third-party GAI is controlled by a party other than the enterprise; receiving from the third-party GAI a response to the query; and presenting the response to a human user via a human interface device (HID).

Owner:MCAFEE LLC
Intelligent risk identification and self-adaptive repair method, system and equipment for software supply chain and medium
PendingCN120910864APlatform integrity maintainanceNeural architecturesCode snippetRisk identification
The invention discloses an intelligent risk identification and self-adaptive repair method, system and device for a software supply chain and a medium, belongs to the field of network security and automatic software engineering, and aims to solve the technical problem of how to accurately and comprehensively identify software code supply chain risks including code snippets. A reliable and efficient automatic closed-loop repair scheme is provided, and the technical defects that in the prior art, the software code supply chain recognition range is limited, the repair process is rigid and the reliability is low are overcome. Analyzing the declarative dependency; meanwhile, semantic traceability based on artificial intelligence is carried out on the code snippets, and a global software material list is generated; and performing intelligent mapping on the software components in the global software bill of materials and the vulnerability database to identify risks.

Owner:SHANDONG ZHENBAI INFORMATION TECHNOLOGY CO LTD
Business module source code generation method and system based on large model business reasoning
ActiveCN120929089AError detection/correctionSoftware metricsCode generationTheoretical computer science
The invention provides a business module source code generation method and system based on large model business reasoning, and belongs to the technical field of code generation. The business module source code generation method comprises the steps that semantic analysis is conducted on business requirements, and a business association graph with weights is constructed; performing module division, and decomposing a complete task into a plurality of sub-tasks; calling a coordination agent, distributing a corresponding module code generation agent based on a large model for each decomposed subtask, and injecting context information to generate a corresponding module code; wherein the module code generation agent learns a corresponding relationship between tasks and injected context information and codes in advance based on field self-adaptive staged training; and calling the verification agent to perform code quality verification. The method has the beneficial effects that the module division is performed based on the business association graph with the weight, the multi-agent collaborative code generation is constructed by adopting the field-adaptive staged training, and the quality of the generated code is verified, so that the code generation efficiency and quality are improved.

Owner:SHANGHAI RUICHENG SOFTWARE CO LTD
Code peculiar smell detection method and system based on AST code measurement and code semantics
PendingCN119248277Aaddress limitationsovercome limitationsEnsemble learningNeural learning methodsCode smellTheoretical computer science
The invention provides a code peculiar smell detection method and system based on AST code measurement and code semantics. The method comprises the following steps of: firstly, constructing a FA-AST (Flow-Augmented Abstraction Syntax Tree) by analyzing a code snippet, and extracting three types of AST-based code metrics, namely a structure metric, a syntactic metric and a semantic metric from the FA-AST; then, a deep learning model is used for capturing contextual information and a dependency relationship of the code from the source code so as to extract code semantics; and finally, by fusing AST-based code measurement and code semantics, inputting a classification model to carry out training and testing so as to identify the peculiar smell in the code and evaluate the severity of the peculiar smell. Compared with software code measurement extracted by a traditional static code analysis tool, the AST-based code measurement provided by the invention is more comprehensive and easier to extract, and has obvious advantages in the aspect of improving the code odor detection precision and efficiency.

Owner:HANGZHOU DIANZI UNIV +1