
Patents
Literature
972results about "Unauthorized memory use protection" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
Core AI Serving Platform Enhancements
PendingUS20260148163A1Memory architecture accessing/allocationMathematical modelsModularityTerm memory
A computer system implements a unified framework integrating an adaptive elastic funnel (AEF) with a convergent intelligence fabric (CIF) for flexible and contextualized multi-agent AI and human collaboration at scale. The system provides a universal multi-modal key-value subsystem for sharing partial computations across agents, implements a hybrid greedy / non-greedy placement strategy for dynamic memory management, orchestrates dynamic computational workflows and tensor workflows using hierarchical tensor-fragment scheduling, enables cross-agent orchestration with policy-based privacy preservation, and incorporates quantum-resistant secure memory enclaves. The architecture supports continuous learning without catastrophic forgetting, compositional reasoning across modalities, and secure task execution in distributed environments. This integration enables unprecedented computational efficiency, secure collaboration, and adaptive intelligence in high-dimensional decision-making environments while supporting incremental adoption through modular interfaces.

Owner:QOMPLX INC
Data storage device and method for using a dynamic floating flash region to secure a firmware update
A data storage device and method are provided for using a dynamic floating flash region to secure a firmware update. In one embodiment, a data storage device is provided comprising a first non-volatile memory, a second non-volatile memory, and a controller. The controller is configured to communicate with the first and second non-volatile memories and further configured to: determine addresses in the second non-volatile memory to store portions of a firmware update, wherein the addresses are determined on-the-fly as opposed to being predetermined; and store the portion of the firmware update in the addresses in the second non-volatile memory. Other embodiments are provided.

Owner:WESTERN DIGITAL TECHNOLOGIES INC
Low-latency RDMA acceleration system based on memory registration
PendingCN120469941AMemory adressing/allocation/relocationUnauthorized memory use protectionInformation processingComputer architecture
The invention belongs to the field of computer systems, and provides a low-latency RDMA (Remote Direct Memory Access) acceleration system based on memory registration, which comprises the following steps of: registering a memory region applied by an application program by utilizing a memory pin technology in a kernel; receiving a remote direct memory access (RDMA) work request initiated by an application program, and packaging information comprising a source virtual address and a target virtual address in the request to form a work queue element; the assembly line is used for processing data receiving from a remote system and sending of local data, and hardware logic used for table look-up, QoS detection and message processing is embedded in the assembly line; the server manages the working queue, the data transmission state and the abnormal information processing in a unified manner, and is used for adjusting the transmission parameters of the RDMA acceleration system in real time according to the received context signal; a standardized software calling interface is provided, and cooperative control between software and hardware is achieved.

Owner:SICHUAN TOURISM UNIV
Integrated key revocation with a field loading process and / or related safety checks related to an asset system
ActiveUS12417191B2Memory architecture accessing/allocationKey distribution for secure communicationData fileEngineering
Various embodiments relate to integrated key revocation with a field loading process and / or related safety and security checks related to an asset system. In an implementation, a data loading request to store a data file via a target storage device of an asset is received. The data file can be signed based on a first key. In response to the data loading request, a key identifier for the first key associated with the data file is compared against (i) a list of key identifiers stored in a key revocation list and (ii) a one-time programmable (OTP) memory of the asset. Additionally, in response to a determination that the data file is successfully authenticated against the key revocation list and the OTP memory, a key revocation process is performed with respect to a second key for the data file associated with the data loading request.

Owner:HONEYWELL INTERNATIONAL INC
Cost-efficient solid state disk based on host end resource borrowing and host
InactiveCN120610655AMemory architecture accessing/allocationInput/output to record carriersConfidentialityTerm memory
The invention discloses a cost-effective solid state disk based on host end resource borrowing and a host. The hard disk comprises a nonvolatile memory, a memory resource, a CXL TSP characteristic module, a CXL driven communication module, a load detection module and a firmware binary code. The firmware binary code is stored in a nonvolatile memory and is used for executing a solid state disk management function by borrowing computing resources of a host after being uploaded to an enclave of the host; the communication module driven by the CXL is responsible for performing communication interaction with an SGX enclave in a host end; the CXL TSP characteristic module is used for ensuring confidentiality and integrity of communication interaction; the load detection module is used for monitoring the load of the I / O request, and when the load is higher than a threshold value, a daemon thread located at a host end is notified to load a firmware binary code to a host and start the host; the nonvolatile memory is used for storing data. According to the invention, efficient and safe host end resource use can be realized.

Owner:PEKING UNIV
Method for disguising and hiding data in memory address
InactiveCN120469942AUnauthorized memory use protectionDigital data protectionMemory addressAlgorithm
The invention discloses a method for disguising and hiding data in a memory address, and relates to the technical field of data protection and memory management. The method comprises the steps of obtaining a real numerical value of a target variable needing to be protected; splitting the real numerical value into a plurality of sub-numerical values, and storing the plurality of sub-numerical values in a group of newly allocated storage units in a memory; and when the target variable needs to be used, restoring the real numerical value of the target variable from the plurality of sub-numerical values. The target variable still allocates an address in the memory, but stores the disguise value. The sub-values can be generated through multiple attenuation modes and written into a protection array which is the same as the target variable data in type. The sub-values can be stored in a random index or sequential storage mode, and the protection array can be re-declared during each assignment or reused when conditions are met. According to the method, the hiding performance and the tamper-resistant capability of the data in the memory are effectively improved, and the method is suitable for an application scene in which safety protection is carried out on the local operation data.

Owner:ZHONGBO INFORMATION TECH RES INST CO LTD
Method and equipment for realizing firmware trusted platform module on RISC-V platform
PendingCN120632834AUnauthorized memory use protectionProgram/content distribution protectionCommunications securityOperational system
The invention provides a method and equipment for realizing a firmware trusted platform module on an RISC-V platform, the functions of the trusted platform module are realized without extra hardware extension through cooperation of software and firmware in combination with a PMP mechanism, a PUF and a hardware timer of the RISC-V platform, and the realization mode comprises an isolation execution process, a hardware execution process and a hardware execution process. An fTPM isolation memory area is configured in the starting stage through a PMP mechanism, and access to fTPM codes and data is limited; a static data protection process: generating a device key by using a PUF (Physical Unclonable Function), and carrying out encryption and integrity protection on fTPM persistent data in combination with a Flash locking mechanism; the trusted starting process comprises the steps of adopting a DME mechanism, ensuring and maintaining the integrity of a starting metric chain and supporting a PCR register function; the efficient communication process comprises the steps of dynamically adjusting the PMP permission of a shared memory area through a dynamic permission exchange page mechanism, and realizing zero-copy communication between the fTPM and an operating system or an application program; and the secure clock process comprises the step of constructing an independent trusted clock source based on a hardware timer of the RISC-V platform.

Owner:WUHAN UNIV
Crypto-agile firmware update
PendingUS20250291739A1Memory architecture accessing/allocationMemory adressing/allocation/relocationSoftware engineeringOne time programmable
Examples described herein relate to updating a cryptographic process. In some examples, circuitry is to update a cryptographic process by a write of a firmware image to a non-volatile memory; authenticate the firmware image based on a hash value stored in One Time Programmable Memory (OTPM); and permit execution of the authenticated firmware image to perform the cryptographic process.

Owner:INTEL CORP
Memory management
A target virtual address is translated to a target physical address for a memory access request. At least for write requests, the memory access request is rejected when a target stage-1 translation table entry specifies that a target memory region corresponding to the target virtual address is a guarded control stack (GCS) region for storing a GCS data structure for protecting return state information, and the memory access request is not a GCS memory access request triggered by one of a restricted subset of GCS-accessing instruction types. When an anti-aliasing property is specified for the target memory region and the target stage-1 translation table entry or another stage-1 translation table entry used to locate the target stage-1 translation table entry is an unhardened entry unprotected by a translation hardening mechanism, the memory access request is rejected. In at least one operating state, a GCS memory access request is rejected when the anti-aliasing property is not specified for the target memory region.

Owner:ARM LTD
An authentication code generating class of instructions
PendingGB2639988AMemory architecture accessing/allocationUnauthorized memory use protectionCode generationComputer architecture
There is provided an apparatus, a method, and a computer program. The apparatus is provided with instruction decoding circuitry to decode instructions and processing circuitry to perform a processing operation in response to a decoded instruction. In response to an authentication code generating instruction, the processing circuitry is configured to generate an authentication code associated with an 10 authentication target value. For at least one type of the authentication code generating instruction, the processing circuitry is configured to generate an authentication code, when operating in a first code generation mode, by applying a code generating function to: a key; the authentication target value; a first modifier dependent on a stack pointer, and / or a second modifier dependent on a program counter address; and a further 15 modifier dependent on a further value obtained from an architecturally visible register different from the stack pointer register and the program counter register.


Owner:ARM LTD
Memory system and storage system managing first and second account information for authentication of first and second accounts
ActiveUS12493419B2Memory architecture accessing/allocationInput/output to record carriersInformation controlData transport
According to one embodiment, a memory system includes a nonvolatile memory and a controller. The controller manages first account information to be used for authentication of a first account and second account information to be used for authentication of a second account. The controller receives third account information from a host device. When the third account information matches the first account information, the controller permits access to at least a partial storage area of the nonvolatile memory based on a request from the host device and transmits first data that includes the second account information to a first memory system.

Owner:KIOXIA CORP
Techniques associated with mapping system memory physical addresses to isolation domains for uniform memory access by a system
PendingUS20260064605A1Memory architecture accessing/allocationMemory adressing/allocation/relocationUniform memory accessAddress decoder
Examples include techniques associated with mapping system memory physical addresses to isolation domains for uniform memory access (UMA) by a system. Examples include mapping separate system memory physical addresses ranges associated with memory devices communicatively coupled with at least one compute die of the system through an input / output (I / O) die of the system. The separate system memory physical addresses to be mapped to isolation domains and address decoder information is generated to indicate the mapping of the separate system memory physical address ranges to the isolation domains.

Owner:INTEL CORP
Privilege level assignments to groups
PendingUS20260030177A1Specific access rightsUnauthorized memory use protectionSoftware engineeringPrivilege level
According to examples, an apparatus may include a memory on which is stored machine-readable instructions that may cause a processor to determine, for each of a plurality of members in a group, a respective least privilege level for a resource and determine, based on the determined respective least privilege levels, a privilege level to be assigned to the group for the resource. The instructions may also cause the processor to assign the determined privilege level to the group for the resource and apply the assigned privilege level to the members of the group for the resource.

Owner:MICROSOFT TECHNOLOGY LICENSING LLC
Mark protection instruction
PendingCN120693595AError detection/correctionUnauthorized memory use protectionComputer hardwareMemory address
Access control circuitry (15) compares, in response to a memory access request, a flag value determined based on a flag portion (40) of an address pointer (42) with an allocation flag (32) associated with a memory location identified by a memory address determined from the address pointer. In response to the comparison indicating a given result, a marker error response is performed. A processing circuit (4) executing a flag protection instruction detects whether an operation involves an attempt to set a bit in an identification portion (74) of an output value to a value other than a value in a corresponding bit in an input operand. When the processing circuitry detects the attempt, the processing circuitry sets a given portion of the output value to an error indication value. The identification portion is part of an output value that is to be used as a flag portion if the output operand is used as an address pointer for the memory access instruction.

Owner:ARM LTD
System and method for trusted execution environment, electronic device and storage medium
PendingCN121051778AMemory adressing/allocation/relocationUnauthorized memory use protectionSecure communicationSoftware engineering
The embodiment of the invention provides a trusted execution environment system and method, an electronic device and a storage medium, the system comprises a processor, an enclave protection unit and a memory, the enclave protection unit is connected with the processor and the memory through a data bus, and the processor is used for storing the enclave protection unit in a secure mode. In response to a request message for creating a user enclave sent by the user equipment, creating a corresponding user enclave in the memory, and sending an access address of the user enclave to the user equipment and the enclave protection unit, the user enclave being used for storing encrypted user sensitive data; and the enclave protection unit is used for receiving an access request message sent by the user equipment to the user enclave, and accessing the user enclave according to an access address in the access request message, so that the problems that the TEE capabilities of CPUs of different system architectures are not uniform, a uniform security communication mechanism is lacked and only a solution of software TEE is supported in related technologies can be solved.

Owner:ZTE CORP
A method and apparatus for improving data card security
InactiveCN102270183Aimprove securityUnauthorized memory use protectionRecord carriers used with machinesPasswordComputer terminal
This invention discloses a method and apparatus for improving the security of data cards, relating to the field of information security, and is invented to enhance the security of information stored in data cards. The method includes: binding a data card inserted into a first terminal to the first terminal; generating a decryption password; when a read / write operation is required on the data card, determining whether a second terminal requiring the read / write operation is the first terminal, and if so, decrypting the data card using the decryption password. This invention is mainly applicable to various data cards.
Owner:YULONG COMPUTER TELECOMM SCI (SHENZHEN) CO LTD
Protecting execution environments within domains
ActiveUS20250265202A1Memory architecture accessing/allocationUnauthorized memory use protectionComputer hardwareMemory address
There is provided an apparatus that includes processing circuitry for performing processing in one of a fixed number of at least two domains. One of those domains is subdivided into a variable number of execution environments and memory protection circuitry uses a key input to perform encryption or decryption on the data of a memory access request issued to a memory address from within a current one of the domains. The key input is different for each of the domains and for each of the execution environments, the key input for each of the domains is fixed at boot time of the apparatus, and the key input for each of the execution environments is dynamic.

Owner:ARM LTD
Memory system resource partitioning and monitoring (MPAM) configuration using secure processor
PendingCN121569279AMemory architecture accessing/allocationResource allocationCoprocessorComputing systems
Various embodiments include systems and methods for allocating memory resources in a computing system that includes memory system resource partitioning and monitoring (MPAM) features. The computing system may transition from an MPAM configuration controlled using a CPU to using an MPAM configuration managed by an external entity, such as a CPU co-processor (CPCP). The computing system may centralize MPAM operations, introduce various control modes, and / or notify the autonomous decision process in conjunction with the use of system sensors and parameters.

Owner:QUALCOMM INC
Maintenance operations across subdivided memory domains
An apparatus is provided in which processing circuitry performs processing in one of a fixed number of at least two domains. One of the domains is subdivided into a variable number of execution environments one of which is a management execution environment configured to manage the execution environments. Memory protection circuitry defines a point of encryption after at least one unencrypted storage circuit of a memory hierarchy and before at least one encrypted storage circuit of the memory hierarchy. The at least one encrypted storage circuitry uses a key input to perform encryption or decryption on the data of a memory access request issued from within a current one of the domains. The key input is different for each of the domains and for each of the execution environments and the management execution environment is configured to inhibit issuing a maintenance operation to the at least one encrypted storage circuit of the memory hierarchy.

Owner:ARM LTD
Enabling large frames for secure virtual machines
PCT designated stageWO2026027398A1Unauthorized memory use protectionSoftware simulation/interpretation/emulationSoftware engineeringTrusted Computing
The computer-implemented methods, computer program products, and computer systems include computer operations that include executing, in a trusted computing environment, a call from a host in an untrusted computing environment, where the call is to determine a status of a large page of memory for use by a secure guest, where the secure guest is managed by the host in the untrusted computing environment. The executing includes determining that all small pages comprising the large page and the large page meet pre-defined security requirements. The executing also includes, based on the determining, setting security properties of the large page and the small pages comprising the large page to enable translation for the large page for a given block of memory of the secure guest. The executing also includes storing in a computing element, a designation identifying the large page as belonging to the secure guest.


Owner:INTERNATIONAL BUSINESS MACHINE CORPORATION +1
Memory management device and memory management method
PendingUS20250291802A1Digital data information retrievalUnauthorized memory use protectionAddress resolutionEngineering
A memory management method is provided. The method includes a memory allocation stage and an address resolution stage. The memory allocation stage includes receiving a memory allocation request from the application program, allocating a buffer with the specified size in the memory in response to the memory allocation request, and generating a buffer pointer for the buffer, and return the buffer pointer to the application program. The buffer is a device buffer is allocated for one or more accelerator devices, or a CPU buffer allocated for a CPU. The address resolution stage includes receiving a memory access request from the application program, determining whether the search pointer corresponds to the device buffer or the CPU buffer based on the buffer pointer and the specified size, allowing access to the corresponding device buffer or CPU buffer.

Owner:MEDIATEK INC
Exception return state lock parameter
ActiveUS20250284495A1Unauthorized memory use protectionConcurrent instruction executionStatus registerReliability engineering
An apparatus comprises exception return state register storage, and processing circuitry. In response to a guarded control stack (GCS) exception return state push instruction, the processing circuitry obtains exception return state information from the exception return state register storage and push the state information to a GCS data structure. In response to a GCS exception return state pop instruction, the processing circuitry obtains GCS-protected exception return state information from the GCS data structure. In at least one operating state, the processing circuitry detects, in response to an attempt to modify the exception return state information stored in the exception return state register storage, whether an exception return state lock parameter is in a locked state or an unlocked state, and signals a fault when it is in the locked state.

Owner:ARM LTD
Virtualization-based platform protection technology
ActiveUS20250390443A1Memory architecture accessing/allocationProgram initiation/switchingData processing systemVirtualization
A data processing system (DPS) uses platform protection technology (PPT) to protect some or all of the code and data belonging to certain software modules. The PPT may include a virtual machine monitor (VMM) to enable an untrusted application and a trusted application to run on top of a single operating system (OS), while preventing the untrusted application from accessing memory used by the trusted application. The VMM may use a first extended page table (EPT) to translate a guest physical address (GPA) into a first host physical address (HPA) for the untrusted application. The VMM may use a second EPT to translate the GPA into a second HPA for the trusted application. The first and second EPTs may map the same GPA to different HPAs. Other embodiments are described and claimed.

Owner:INTEL CORP
Electronic data destruction system
PendingCN120762592AInput/output to record carriersUnauthorized memory use protectionSoftware engineeringVoltage clamp
The embodiment of the invention provides an electronic data destruction system, which comprises the following steps of: covering and erasing stored data to generate a logic destruction state; the main storage power line and / or the key control chip are / is burnt out in a voltage clamping and / or current fusing mode through the self-destruction circuit. By means of logic erasing and physical destroying, data destroying is thorough and irreversible, a data reconstruction path is thoroughly blocked, and irrecoverability of data is fundamentally ensured.

Owner:SHENZHEN LONGQIN INFORMATION TECH CO LTD
Isolated address region assignment updating instruction
PCT designated stageWO2025210329A1Memory architecture accessing/allocationUnauthorized memory use protectionTheoretical computer sciencePhysical address
In response to instruction decoding circuitry decoding an isolated address region assignment updating instruction specifying a target physical address and an updated isolated address region assignment for the target physical address, at least one memory system request is issued to request an update to isolated address region assignment information which defines access control information for controlling access to the target physical address, to set the isolated address region assignment information to indicate one of a plurality of isolated address region assignments selected based on the updated isolated address region assignment specified by the instruction. The plurality of isolated address region assignments include at least one more secure isolated address region assignment for which associated data is to be isolated from being observable by program code associated with at least one less secure isolated address region assignment.

Owner:ARM LTD
Memory access locking and logging for trusted execution environments
PendingUS20250383997A1Memory architecture accessing/allocationUnauthorized memory use protectionControl memoryOperating system
This disclosure describes approaches for securing memory among non-secure / secure processing environments such as in a TrustZone-M processor architecture. An example method of controlling memory access includes: configuring a memory locking service in a computing device having a secure processing environment and a non-secure processing environment, and executing the memory locking service in the secure processing environment; receiving a request with the memory locking service to lock a specified memory region of the computing device, with the specified memory region being associated with the non-secure processing environment; associating the specified memory region with the secure processing environment (e.g., by using a Security Attribution Unit to upgrade the region to secure memory); subsequently, identifying an access attempt to the specified memory region, with the access attempt being received from the non-secure processing environment; and controlling the access attempt to the specified memory region, based on a policy.

Owner:ANALOG DEVICES INC
Nonvolatile memory device and memory system
ActiveUS12423246B2Input/output to record carriersUnauthorized memory use protectionData controlMemory cell
A nonvolatile memory device includes a memory cell array to store an original setting data, a page buffer circuit connected to the memory cell array through a plurality of bit-lines, a secure buffer and a control circuit. The secure buffer includes an access control circuit and a plurality registers with restricted access, and the plurality registers store the original setting data that is dumped-down from the memory cell array through the page buffer circuit in an initialization sequence. The control circuit controls the page buffer circuit and the secure buffer. The plurality registers include a first register and second registers. The access control circuit, in response to the first register being accessed, accesses at least a portion of the second registers concurrently with accessing the first register.

Owner:SAMSUNG ELECTRONICS CO LTD
Hardware enforcement of boundaries on the control, space, time, modularity, reference, initialization, and mutability aspects of software
PendingUS20250321739A1Resource allocationUnauthorized memory use protectionComputer hardwareSource transformation
Modifications to existing computer hardware, compiler changes or source-to-source transforms performed during the software build process, and a collection of libraries and modifications to existing standard system software and libraries. The invention allows a program author to enforce various kinds of locality of causality in software to provide enforcement of boundaries for the following aspects of a computer program: control, space, time, modularity, reference, initialization, and mutability. Where these properties do not suffice to guarantee a property at static time, dynamic checks may be added and the constraints on control flow prevent such dynamic checks from being avoided by the program.

Owner:WHOLE SKY TECH CO
Electronic device including a storage device and a host device and methods of operation
PendingUS20250356063A1Memory architecture accessing/allocationUnauthorized memory use protectionData segmentEngineering
A storage device for providing a security function may include: a nonvolatile memory device including a Replay Protected Memory Block (RPMB); and a memory controller configured for receiving, from an external host, a command UFS Protocol Information Unit (UPIU) including a host RPMB message, and storing data in the RPMB according to authentication performed using the host RPMB message. The command UPIU may include a basic header segment commonly included in UPIUs transmitted / received between the external host and the memory controller, and the basic header segment may include a data segment length field as information indicating that the host RPMB message has been included in the command UPIU.


Owner:SK HYNIX INC
Personalized interactive communication method and system
InactiveUS20080047021A1Random number generatorsUser identity/authority verificationPersonalizationApplication software
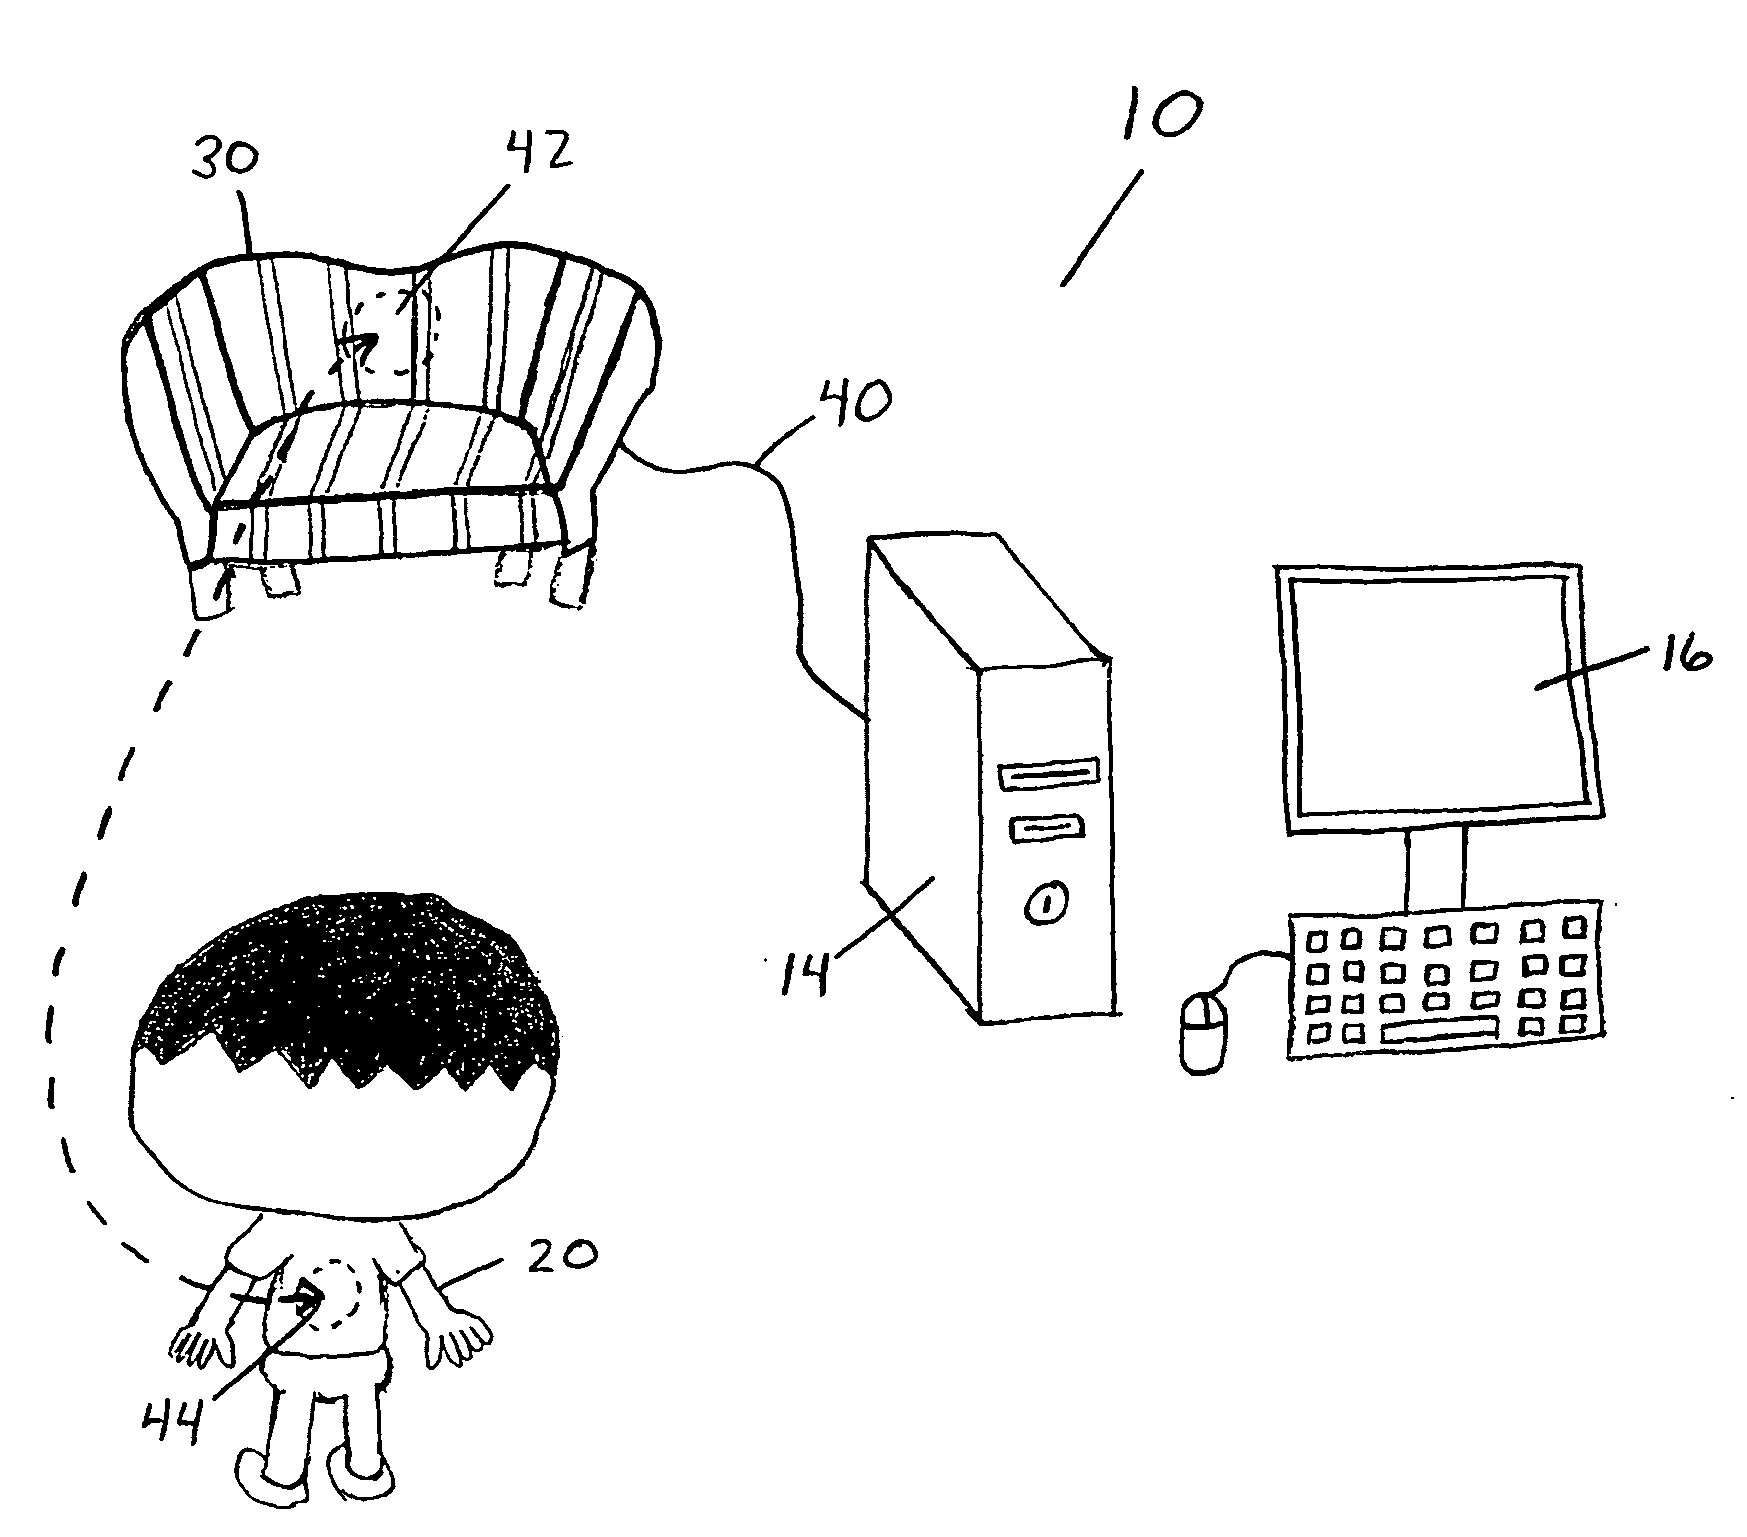
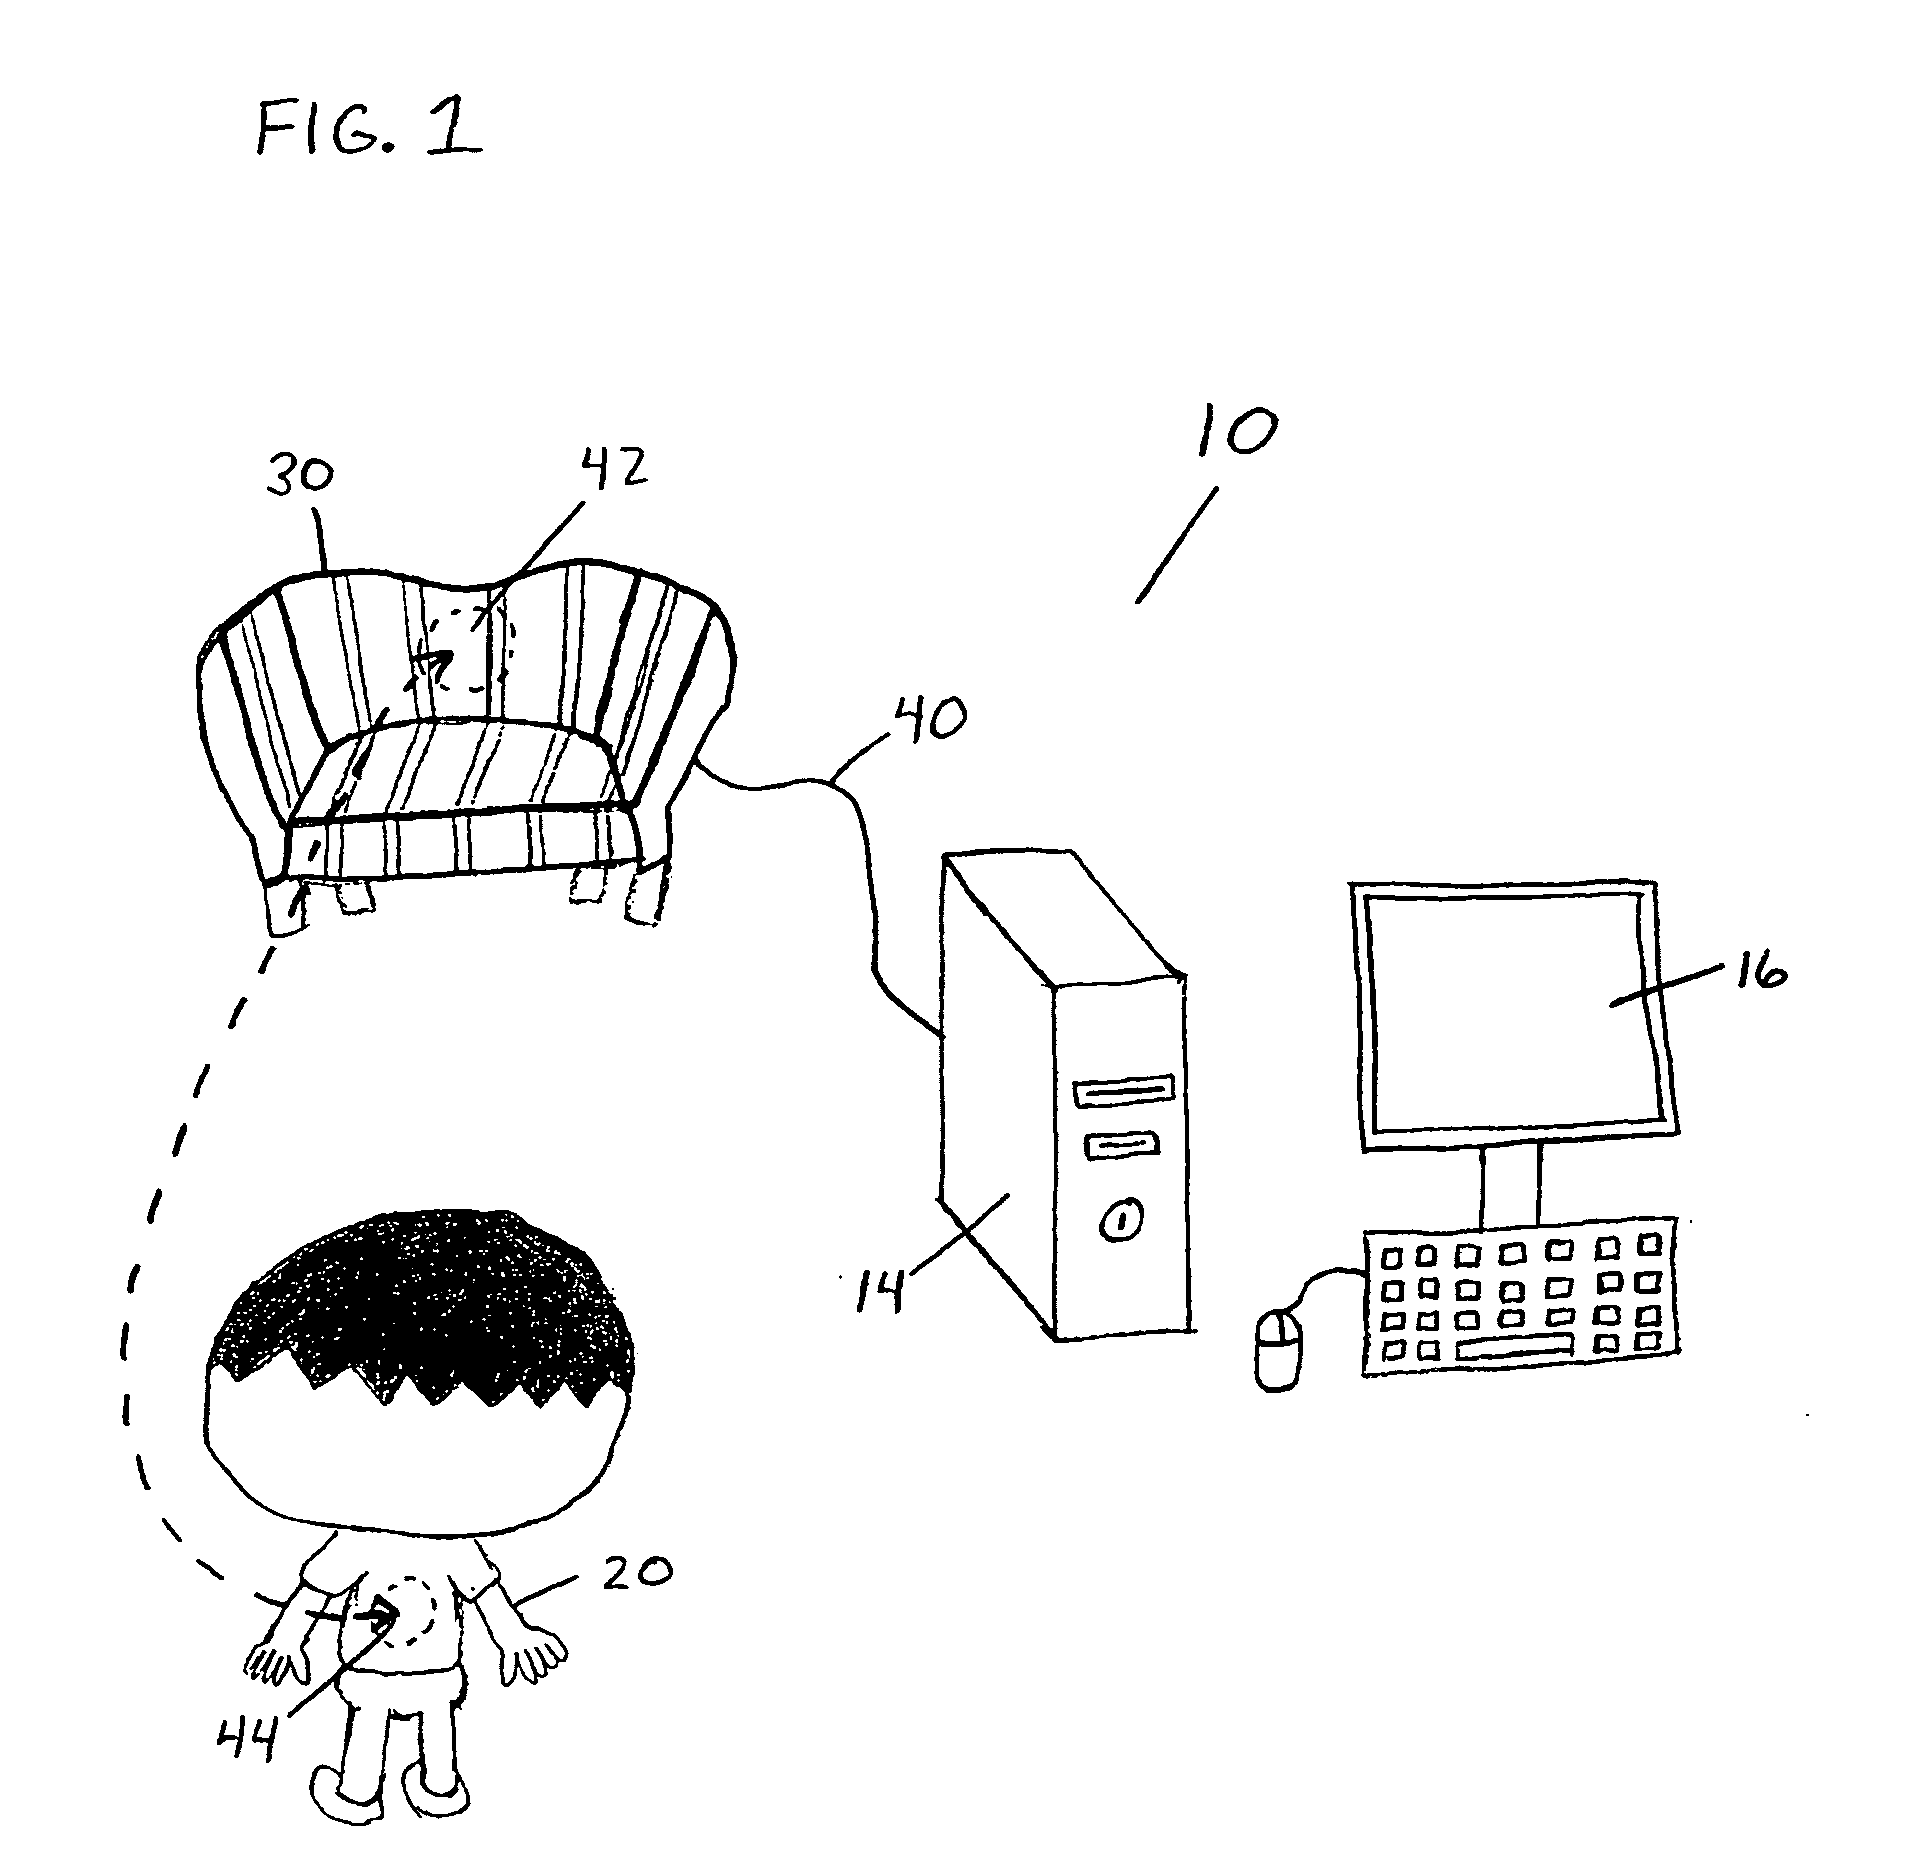
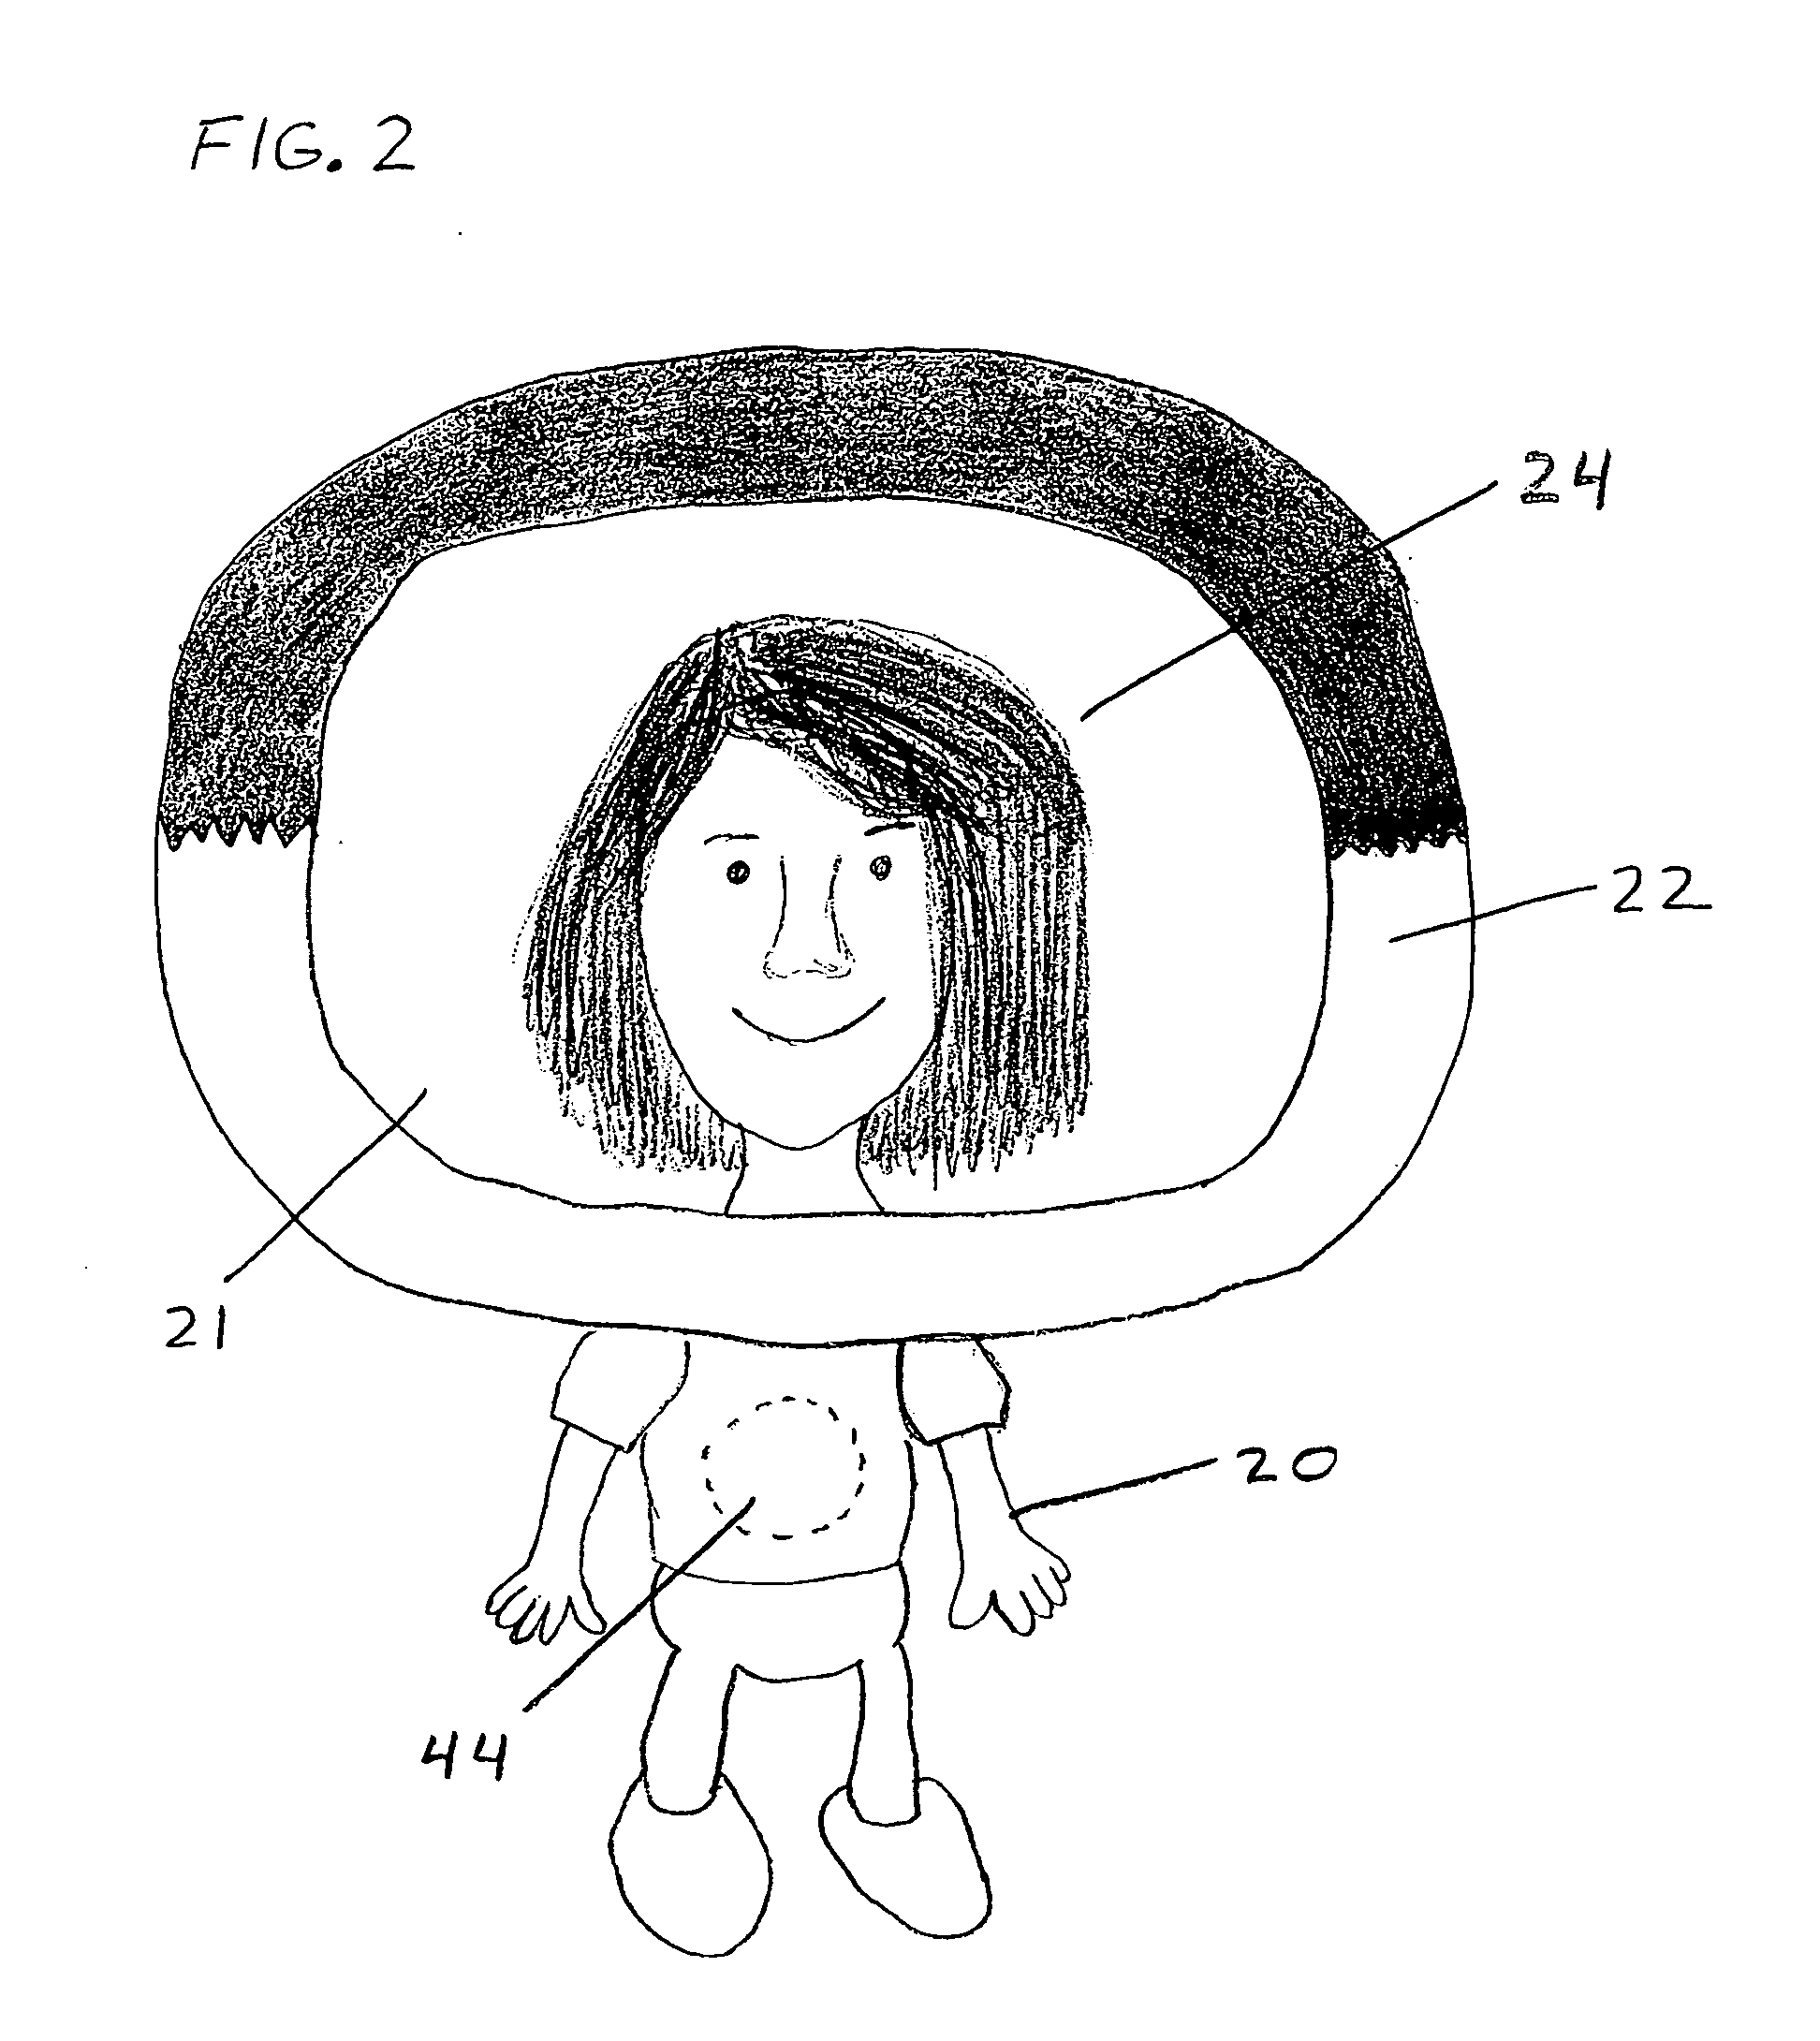
An interactive communication apparatus, which connects to a computer, comprises an interactive communication device, having a tag, that is removably placed on or adjacent to an interactive communication device holder, having a sensor, wherein the tag communicates information to the sensor. The interactive communication system enables a user to transfer, store or retrieve information about and / or to a person that is identified with that interactive communication device. Once the interactive communication device is placed on or adjacent to the interactive communication device holder, certain communication applications, which include, photo slideshow, chat, e-mails, music, videos, and RSS feed, launch. The user can terminate the applications by removing the interactive communication device from the interactive communication device holder. The user can access content related to a new person by placing another interactive communication device, that corresponds to the new person, on or adjacent to the interactive communication device holder.
Owner:METTA CONCEPTS