

Patents
Literature
1342 results about "Web application" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
In computing, a web application or web app is a client–server computer program that the client (including the user interface and client-side logic) runs in a web browser. Common web applications include webmail, online retail sales, online banking, and online auction.
Web application internationalization
InactiveUS7784026B1Eliminate needEasy constructionExecution for user interfacesMemory systemsMeta levelWeb page
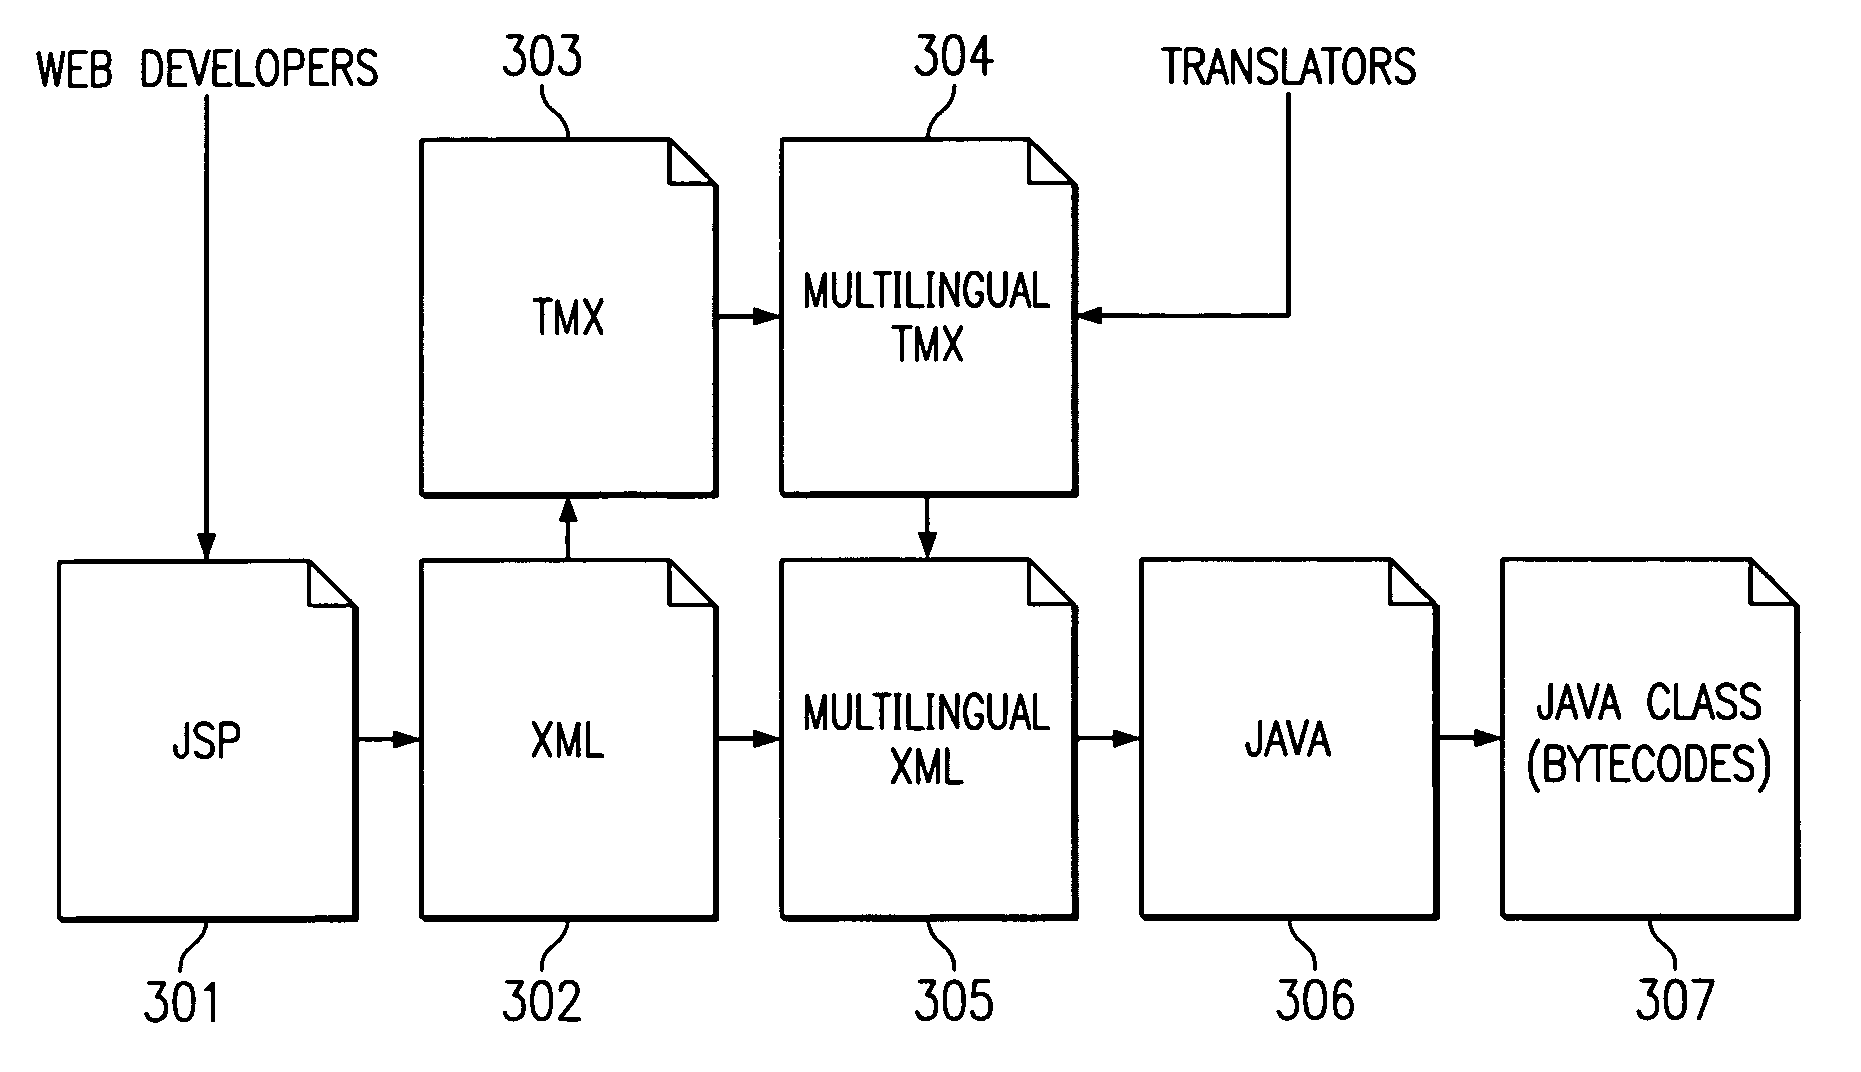
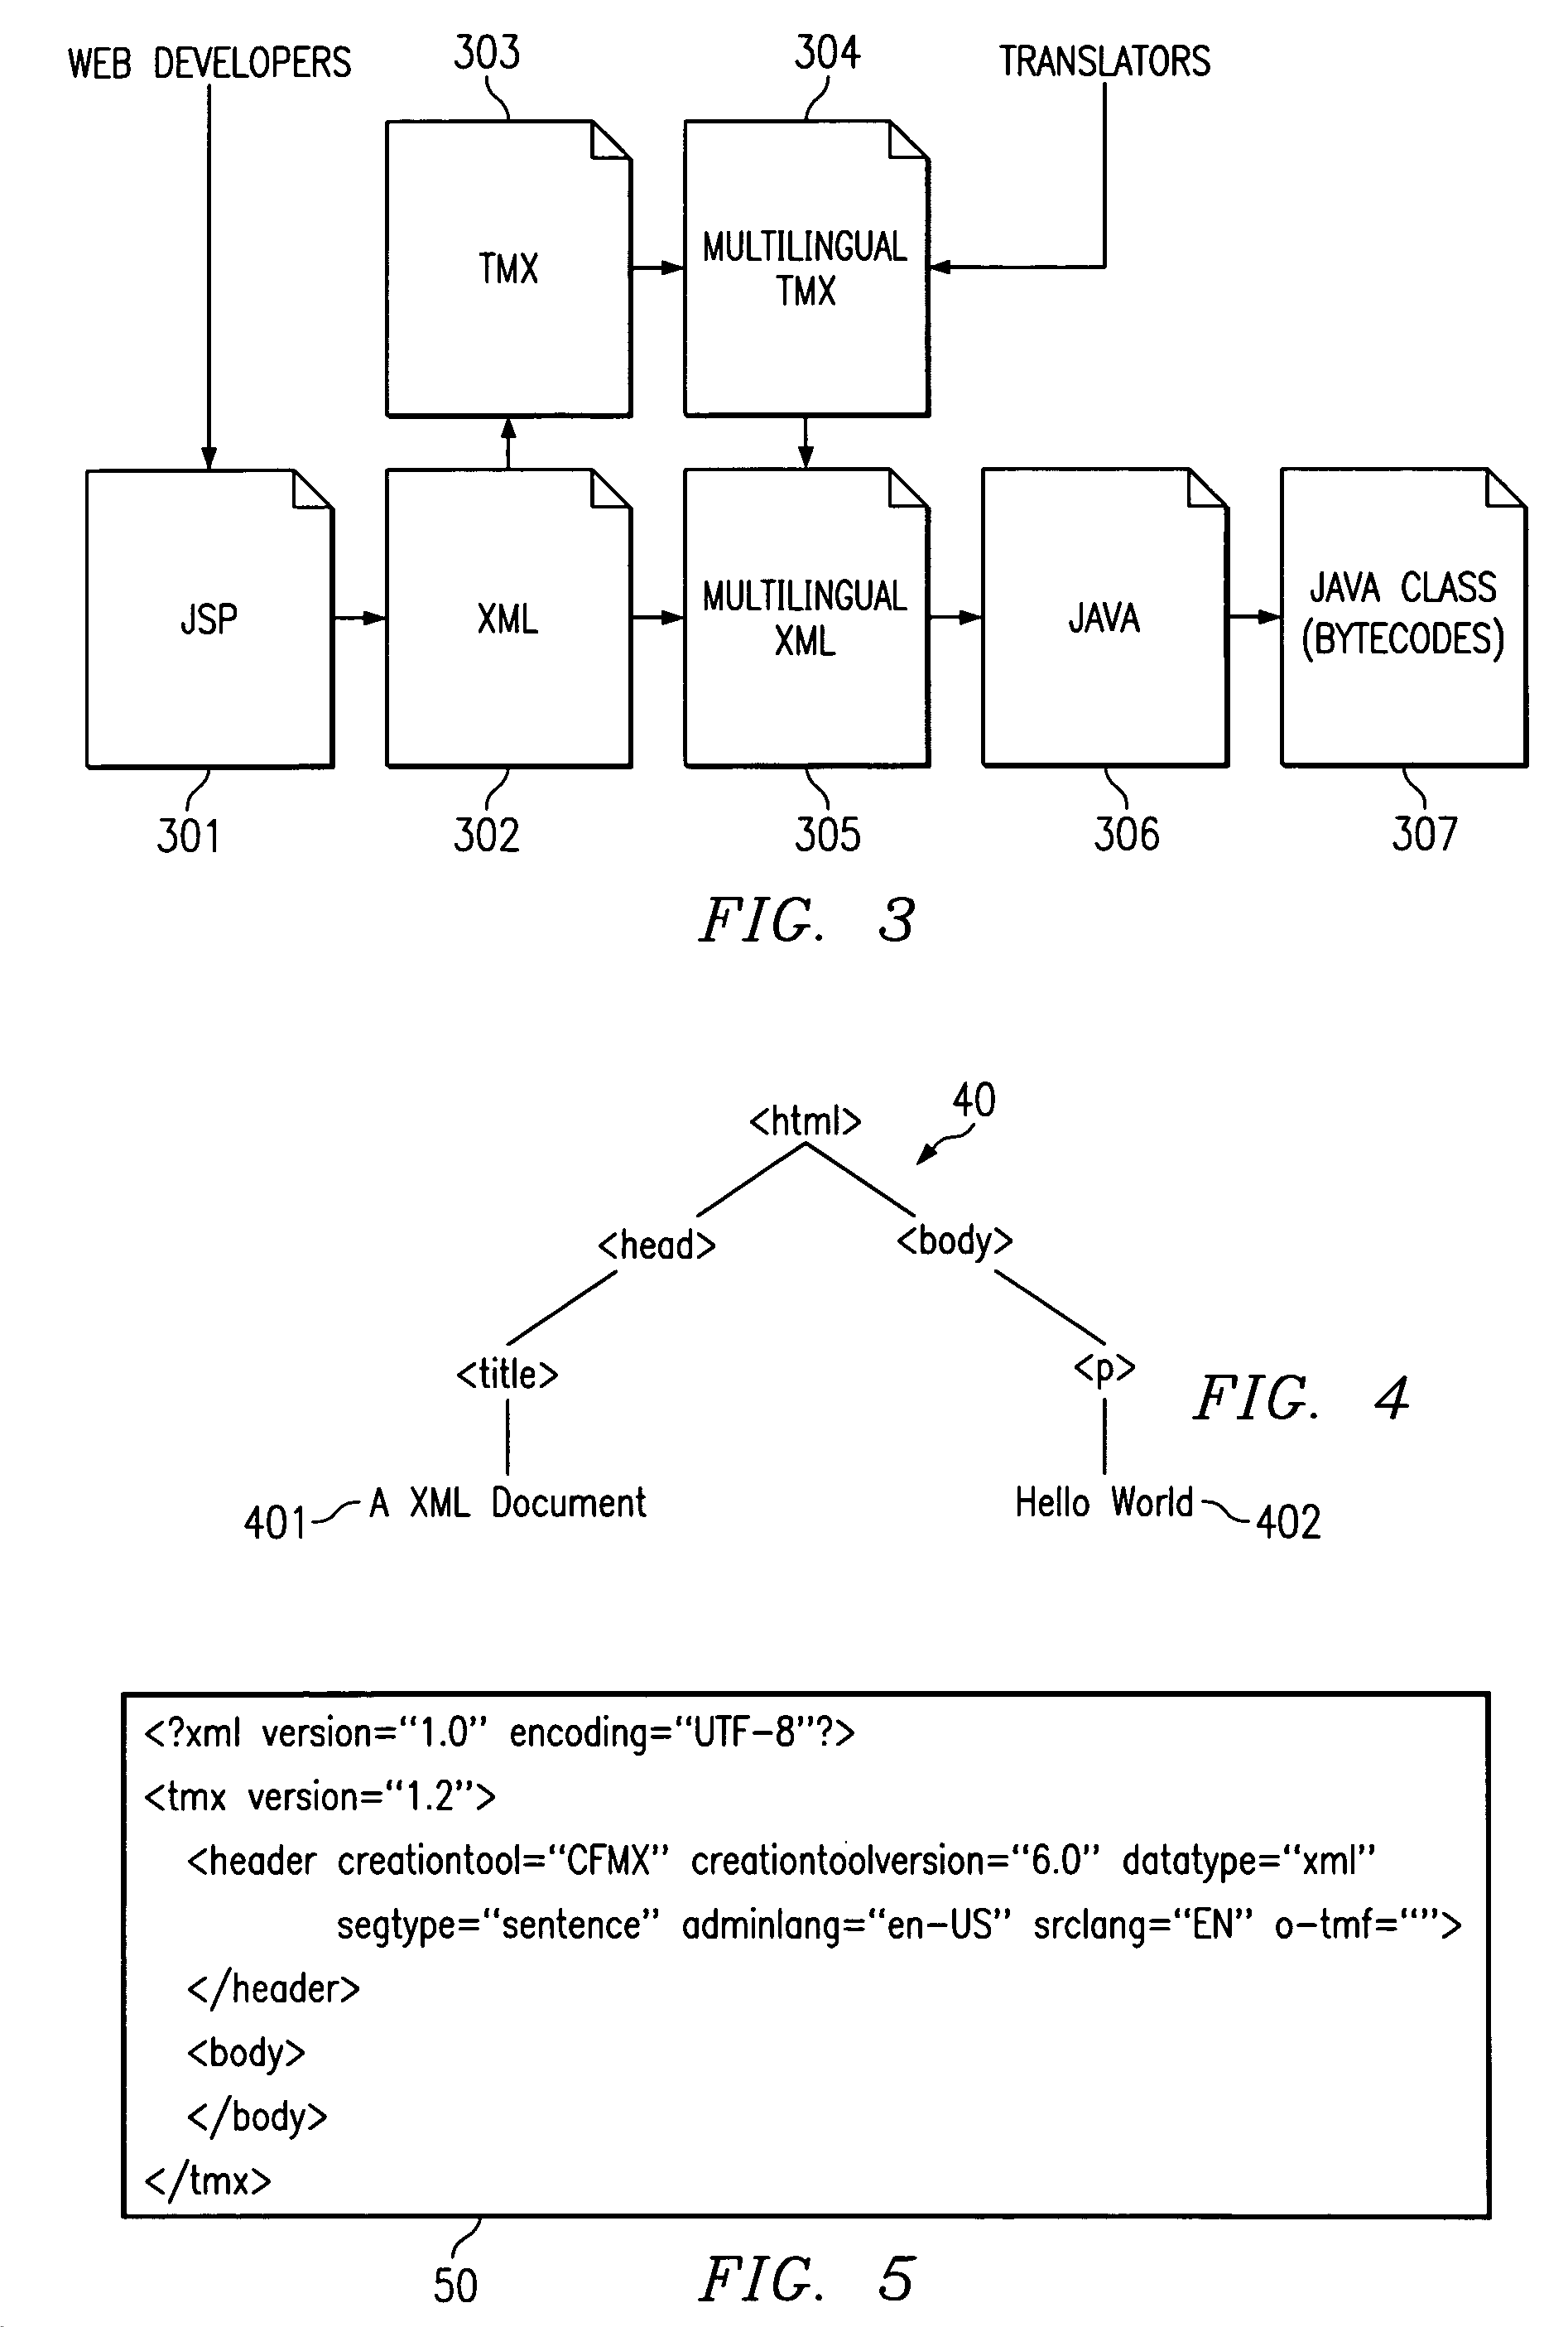
A system and method is described for internationalization of web pages by extracting translatable content from extensible mark-up language (XML), or similar data-centric meta-language representations of web pages or data used to build web pages. The extracted translatable content is stored in a translation task repository (TTR) accessible by the web developer and the translator. The XML representation is then modified to include selection control logic to select the appropriate translations for insertion into the final web page. The translator accesses the TTR to translate the appropriate content and saves the translations back to the TTR associated with the original translatable data. The translations are obtained from the TTR as selection cases for the selection control logic of the XML representation. As the XML is converted into the web source code, the selection logic and translations are embedded therein facilitating building the web site in multiple different languages.
Owner:ADOBE INC
Language model prompt authoring and execution in a database system
ActiveUS20250005299A1Natural language translationDatabase management systemsCommunication interfaceWeb application
A database system may include one or more relational databases storing information for a plurality of tenants in accordance with database object definitions. The database system may also include a communication interface providing the plurality of tenants with access to web applications through which to access the information and configured to receive an indication of one or more of the database object definitions from a tenant. The database system may also include a storage device storing a prompt template specific to the tenant and that includes one or more natural language instructions for generating text and a reference to the one or more database object definitions. The database system may also include a processor configured to retrieve a database record associated with the tenant and corresponding to the one or more database object definitions and to determine a text generation prompt based on the database record and the prompt template.

Owner:SALESFORCE INC
Determining critical logs for network applications
Techniques are described for a computing system configured to obtain a plurality of candidate logs for a plurality of layers of a computing infrastructure. The computing system may, for each candidate log of the plurality of candidate logs, map the candidate log to a log template of a plurality of log templates, wherein each log template to which a candidate log is mapped is a mapped log template. The computing system may rank mapped log templates based on properties of the mapped log templates. The computing system may select, based on the ranking, one or more candidate logs as critical logs. The computing system may output at least one of (1) an indication of the critical logs to determine a potential root cause associated with a performance issue of a network application or (2) an indication of the potential root cause associated with the performance issue of the network application.

Owner:JUNIPER NETWORKS INC
Creative thinking support generative AI system
This invention provides a web application system that allows instructors to effectively use generative AI in classes to match learning tasks, reducing the risk of students asking questions that are inappropriate for the task or trusting false information from the generative AI, and encouraging students' creative thinking through dialogue using generative AI, with the aim of supporting creative activities. SOLUTION: The web application system of this invention creates prompts by integrating questions from learners with prompts preset by the instructor, and provides automatically generated answers through API connection. The app is built using HTML code with a website creation tool, so it can be managed without specialized knowledge. Prompts are edited using three items: Theme, Conditions, and Additional Instructions, to control the answers of the generating AI. In addition, restrictions on questions outside the topic can be set to prevent misuse.

Owner:向田 識弘
Intelligent natural language queries via large language model and user interface element metadata
PendingUS20250190470A1Natural language translationSpecial data processing applicationsWeb applicationLinguistic model
Natural language queries can be answered by using a large language model to find an appropriate user interface element appearing in an application. User interface element metadata can be incorporated when choosing the user interface element. Browser automation can then navigate to a page in the application on which the interface element appears, extract answer data, and then present the answer data as an answer to the natural language query. Input values can be supported, and a large language model can select a matching input value based on semantic matching, even if the natural language query does not have an exactly matching input value. Additional features such as pre-calculating embeddings, pre-determining candidate input values, and the like can be supported. The technologies can provide natural language access to web applications that can result in immediate access for new users and faster query execution by experienced users.

Owner:SAP SE
AI protection engine construction method and system based on Web application
The invention relates to the technical field of AI protection, and discloses an AI protection engine construction method and system based on Web application. The method comprises the steps of obtaining a Web application HTTP request and performing semantic analysis to obtain request feature data; performing multi-dimensional threat feature extraction to obtain a Web request threat feature set; performing mode matching on the Web request threat feature set and a preset attack mode library to obtain a threat type judgment result and attack intention information; performing time sequence behavior analysis to obtain a Web behavior abnormal index; comprehensive decision making is carried out through a multi-agent collaborative decision making system, and a defense decision making scheme is obtained; according to the defense decision scheme, a corresponding defense component is selected through a defense execution engine for safety protection, and a Web request processing result is obtained. According to the method, corresponding protection measures can be taken aiming at requests of different risk levels, so that logic vulnerability attacks which are difficult to detect by a traditional system are effectively identified and defended.

Owner:SHAOGUAN COLLEGE
System and method for large language model based automated test input generation for web applications
Existing techniques for automated generation of test data for testing web applications need detailed requirement documents. The present disclosure receives a plurality of textual documents to extract context. Rephrasing the extracted context by implementing a plurality of rules and passing extracted context along with a first set of prompts to Large Language Model (LLM). Generating program, validator and first set of constraints for extracted context and generating test data by running the generated program. Assigning ranking to test data and selecting the test data with highest ranking. Statically refining the generated program by calling a mathematical library function on the highest ranked test data to generate structural information and modifying language of the second set of prompts passed to the LLM. Dynamically refining the generated program by passing feedback generated by executing the highest ranked test data on a web application and refining the response obtained.


Owner:TATA CONSULTANCY SERVICES LTD
Web application fuzzy testing method based on multi-modal large model assisted web crawler
The invention provides a Web application fuzzy testing method based on a multi-modal large model assisted web crawler, which comprises the following steps of: collecting page information of a Web application program by using an LLM (Logical Link Model), extracting associated information among Web pages, and constructing a state machine according to the associated information among the Web pages to guide a sequence of crawling the Web pages; performing screenshot on the Web page by using the MLLM, obtaining HTML (Hypertext Markup Language) content of the Web page, and generating a natural language description of a task so as to describe the task needing to be completed by a user on the page and an operation required for completing the task; and sequentially converting the natural language description into test codes by using LLM, judging whether the test codes successfully complete a task or not according to the state change of the Web page before and after execution, and if the test codes successfully complete the task, generating corresponding form content and an operation sequence to generate an effective HTTP request. The method has the advantages of simple implementation method, low cost, high test efficiency, high coverage rate and the like.

Owner:NAT UNIV OF DEFENSE TECH
Tree component optimization method based on React framework and fusing virtualization rendering and increment rendering
ActiveCN119668568AReduce stepsImprove loading speedSoftware designWebsite content managementVirtualizationCycle control
The invention belongs to the technical field of front-end development, and particularly relates to a React framework-based tree component optimization method fusing virtualization rendering and increment rendering. Comprising the steps of S1, data preprocessing; S2, dynamic virtualization rendering: dynamically calculating a node index range in a visible area according to a real-time scrolling position of a user viewport, only rendering nodes in the range, and realizing seamless lazy loading of data through scrolling event monitoring; s3, intelligent incremental updating: identifying changed nodes through a state change comparison algorithm, and executing local re-rendering only for the changed nodes based on a component life cycle control mechanism of a React framework; and S4, lazy loading cooperative control. The method aims at solving the problems in the aspects of performance, memory management, user experience and the like when a tree component in a React ecological system processes large-scale data, and is widely applied to various Web application program development scenes needing to display and operate a large-scale tree data structure.

Owner:HANGZHOU ARTECH
Automated attack mitigation
A distributed denial of service attack is detected. In response to detection of the attack, application layer properties of network traffic associated with a web application under attack are analyzed. Changes to distributions of the application layer properties are identified. A signature is generated based, at least in part, on identifying a combination of application layer properties whose distributions have changed, and which identifies traffic increased since onset of the attack. A mitigation rule is generated based, at least in part, on the signature.

Owner:AMAZON TECH INC
Web vulnerability scanning method, system and device and medium
The invention discloses a Web vulnerability scanning method, system and device and a medium, and the method comprises the steps: data collection: obtaining a source code and a configuration file of a target Web application, and data and historical vulnerability information of the application during operation; feature extraction: analyzing source codes to extract key function calling, parameter passing and control flow information, and constructing semantic representation of codes; analyzing runtime data, and constructing a comprehensive feature vector in combination with a static code analysis result; model training: matching the extracted features with known vulnerability tags to form a training set and a test set; a deep learning model is selected for training according to problem characteristics, and hyper-parameters are adjusted to optimize model performance; vulnerability detection: executing automatic scanning on the Web application to be detected, and judging whether vulnerabilities exist or not according to the features extracted in real time; and generating a report. According to the method, a comprehensive automatic process from data collection to vulnerability report generation is realized, the scanning efficiency and accuracy are remarkably improved, and the security risk is effectively reduced.

Owner:HENAN ZHONGYUAN CONSUMER FINANCE CO LTD
Model-based confidence ranking of web application vulnerabilities
ActiveUS20250005167A1Platform integrity maintainanceMachine learningWeb applicationGraphical user interface
Various embodiments include systems and methods of implementing a machine learning model for calculating confidence scores associated with potential security vulnerabilities. The machine learning model is trained using vulnerability data associated with a set of previously identified vulnerabilities, where the vulnerability data indicates whether a previously identified vulnerability is a true positive or a false positive. In some embodiments, scan traffic data may be obtained. The scan traffic data may be associated with potential security vulnerabilities detected via scan engine(s) that implement application security testing. The machine learning model may be used to determine respective confidence scores for each potential security vulnerability. According to some embodiments, responsive to a request for scan findings associated with a particular application, the respective confidence scores may be displayed via a vulnerability analysis graphical user interface.

Owner:RAPID7 INC
Artificial intelligence-aided classification system for alzheimer's disease screening from retinal photographs
The subject invention pertains to an artificial intelligence-aided classification system for Alzheimer's disease (AD) screening from retinal photographs, which includes a three-in-one deep learning (DL)-based pre-diagnosis module for image assessment and a DL-based AD classification module with additional heatmaps for visualization. For the AD classification module, three kinds of DL models predict the AD-dementia / non-demented probabilities from three directions with both eyes' four images (Direction-1), both eyes' four images combing demographical information (Direction-2), and a single eye's two images (Direction-3), respectively. For the pre-diagnosis image assessment, embodiments provide one pre-processing model, with three additional models for each of the three classification tasks, including image-quality (e.g., gradable or ungradable), field-of-view (e.g., macula-centered or optic nerve head-centered), and laterality-of-the-eye (e.g., right or left eye). Also included is a cloud-based web application that can output the pre-diagnosis image assessment and a simple binary AD-dementia / non-demented classification based on retinal photographs.

Owner:THE CHINESE UNIVERSITY OF HONG KONG
Method and system to provide individualized interventions based on a wellness model
PendingUS20250135287A1Medical simulationPhysical therapies and activitiesPersonalizationPhysical medicine and rehabilitation
Embodiments described herein relate to systems and methods for an individualized intervention to generate and provide wellness pattern aware interventions. The system generates digital instructions and output for an online web application, device hosted application, smart device, or similar system. In one embodiment, the system provides the individualized intervention that matches device capacity, user context, and the best intervention type for a multi feel state longitudinal journey over a multi-day duration.

Owner:LULULEMON ATHLETICA CANADA INC
Tree structure data dynamic management method based on node hierarchical attributes and recursive updating
The invention relates to the field of Web application, in particular to a tree structure data dynamic management method based on node hierarchical attributes and recursive updating. Comprising the following steps: S1, constructing a tree structure data system, and endowing each node with a hierarchical attribute which is used for identifying position information of the node in a tree structure; s2, receiving an operation instruction of a user for the tree structure data, wherein the operation instruction comprises node adding, node batch deleting, node moving, data exporting and importing, node querying and node quantity counting; and S3, according to different operation instructions, executing corresponding processing logic: based on node hierarchy attributes, applying a recursive update mechanism to realize dynamic management of tree structure data, and ensuring data consistency and accuracy.

Owner:HANGZHOU ARTECH
Distributed denial of service protection management
Methods and systems for distributed denial of service (DDoS) protection management are described. The system may aggregate, from a web application firewall (WAF) bridge service that interfaces with one or more WAF services, one or more DDoS event records associated with one or more DDoS events. The system may analyze the one or more DDoS event records via an analysis of one or more headers and one or more payloads of the one or more DDoS event records, logging information, and a threat intelligence feed. The system may generate a security configuration that indicates one or more parameters of the one or more WAF services to be set. The system may validate the security configuration and may transmit the security configuration to the one or more WAF services based at least in part on the validation.

Owner:SALESFORCE INC
User plane optimizations using network data analytics
A user equipment “UE” may be configured with a client application for data collection, contact information pertaining to a network Application Function “AF,” and data collection information such as parameters, whereby the UE collects data that is specific to the UE and sends it to the AF over a user plane. The data collection parameters may include one or more of a type of data the UE should collect, data associated with one or more analytics IDs and application IDs, a data collection frequency, and a reporting frequency. The data collection information may include a processing requirement, an expiration time for the collected data, a timestamp of the data collection, and / or a correlation identifier that associates the collected data with the UE.

Owner:INTERDIGITAL PATENT HOLDINGS INC
Language model prompt authoring and execution in a database system
PCT designated stage expiredWO2025006247A1Natural language translationDigital data information retrievalCommunication interfaceLinguistic model
A database system may include one or more relational databases storing information for a plurality of tenants in accordance with database object definitions. The database system may also include a communication interface providing the plurality of tenants with access to web applications through which to access the information and configured to receive an indication of one or more of the database object definitions from a tenant. The database system may also include a storage device storing a prompt template specific to the tenant and that includes one or more natural language instructions for generating text and a reference to the one or more database object definitions. The database system may also include a processor configured to retrieve a database record associated with the tenant and corresponding to the one or more database object definitions and to determine a text generation prompt based on the database record and the prompt template.

Owner:SALESFORCE INC
Systems and methods for detecting malicious webassembly modules under source code obfuscation
Systems, methods, and frameworks for detecting malicious WebAssembly (Wasm) modules under source code obfuscation are provided. The system is configured to accurately identify malicious behavior in Wasm modules irrespective of the specific malicious functionality and in the presence of source code obfuscation techniques. The detection process leverages a Vision Transformer (ViT) model to classify a Wasm module as benign or malicious, enabling robust identification of threats across diverse attack patterns. The system operates with substantially low runtime overhead on computing resources, making it suitable for integration into real-time web application environments.

Owner:FLORIDA INTERNATIONAL UNIVERSITY
File uploading attack interception method based on semantic entropy enhancement
The invention provides a file uploading attack interception method based on semantic entropy enhancement, and aims at overcoming the defects of an existing file uploading security protection technology in the face of complex attacks. The method specifically comprises the steps that S1, file format analysis and content extraction are conducted, hidden scripts are mined through nested content recognition, and intermediate representation is generated through grammar cleaning and coding specifications; s2, constructing an abstract syntax tree and semantic entropy calculation, tracking a pollution chain, analyzing a high-risk function, identifying a high-entropy character string, modeling and controlling flow complexity, and generating a semantic entropy vector; s3, dynamic scoring and decision making are carried out, and accurate judgment is carried out in combination with white list perception, feature comparison, multi-modal model scoring, adaptive threshold and sandbox observation; and S4, carrying out real-time interception and feature synchronization, blocking malicious file landing, generating an attack log and synchronizing an attack fingerprint. The method takes the semantic entropy vector as a core, breaks through the limitation of static features, remarkably improves the recognition rate of complex attacks, reduces missed judgment, and guarantees the safety of Web applications.

Owner:CHINA LIFE INSURANCE CO LTD
Front end and rear end separated data processing method and device
ActiveCN119449487Aaccurate conversionUser identity/authority verificationNetwork socketCommunication link
According to the front-end and rear-end separated data processing method and device provided by the embodiment of the invention, the protocol recognition engine is realized by constructing the interface platform service framework and adopting the type script language, so that unified interface management is realized. Class attributes and class method definition instructions are innovatively designed, and identity token verification and data formatting functions are integrated. The system ensures data security through identity label matching and authority verification, establishes a reliable data communication link by using a network socket, and realizes accurate conversion of front-end and rear-end data through a data formatting unit. According to the method, the limitation of a traditional front-end and back-end framework is broken through, and an efficient and safe data processing solution is provided for modern web application.

Owner:KAIYUN LIANCHUANG (BEIJING) TECH CO LTD
Web application firewall security defense method and system
ActiveCN120074950APlatform integrity maintainanceSecuring communicationModel managementInternet traffic
The invention discloses a Web application firewall security defense method and system, and belongs to the technical field of network security, and the method specifically comprises the steps: collecting and preprocessing network flow data in real time, constructing standardized data input, and training a multi-modal deep neural network attack detection model to recognize attack behaviors in a network; in the real-time detection process, the model outputs an attack type and a probability, and when an attack is detected, the firewall automatically generates an attack behavior graph, triggers a multi-level depth defense mechanism and feeds back a result to the model management module; and the model management module updates model parameters in real time through online learning, realizes version management, and performs model optimization in combination with a rapid rollback mode, thereby improving the network security protection capability.

Owner:NANJING TORTOISE & HARE RACE SOFTWARE RES INST CO LTD +1
Remote server isolation utilizing zero trust architecture
A zero trust cloud environment provides access to a secure network, and secure network applications. The zero trust cloud environment performs authentication of a user account, and upon successful completion initiates a secure network application, such as an SSH session to a server in a secure network. The server is instructed to generate an isolated network namespace through which a virtual network interface is bridged to the default network namespace. A firewall of the default network namespace does not permit network traffic from the virtual network interface to pass if it is directed to an address of the secure network.

Owner:HEWLETT PACKARD ENTERPRISE DEV LP
User interface navigation for web applications with retrieval-augmented generation
An offline collection system comprises a pipeline for storing metadata of user interface (UI) elements at web pages of a web application. The pipeline comprises crawling uniform resource locators (URLs) of web pages of the web application for content and rendering screenshots of the web pages. The pipeline then prompts a multimodal large language model (LLM) to generate database entries for the web pages comprising UI element metadata derived from the crawled content and rendered screenshots. A response system receives user queries to navigate the web application and augments prompts to an LLM to respond to the user queries with metadata of UI elements relevant to the user queries stored by the offline collection system.

Owner:PALO ALTO NETWORKS INC
Techniques for managing cookies through a secure web gateway
A system and method for facilitating communication between a user device and a web application through a zero trust network providing a secure web gateway using authentication cookies. The method includes receiving network traffic from a user device including an altered authentication cookie, the network traffic directed at a web application; retrieving an original authentication cookie based on the altered authentication cookie; generating a new network traffic based on: the received network traffic, and the original authentication cookie; and sending the new network traffic from the zero trust network environment to the web application.

Owner:HEWLETT PACKARD ENTERPRISE DEV LP
Digital twin WEB application air gesture interaction method and system
ActiveCN119723653AInput/output for user-computer interactionCharacter and pattern recognitionPersonalizationWeb application
The invention belongs to the technical field of human-computer interaction, and discloses a digital twin WEB application air gesture interaction method and system. Comprising the following steps: collecting a real-time video stream of a camera of user side equipment, and preprocessing the real-time video stream; x hand region frames are obtained; inputting the X hand region frames into a preset hand key point detection model based on a generative adversarial network to obtain hand key point coordinate data; acquiring a hand skeleton model based on the hand key point coordinate data; acquiring a joint angle and a hand motion track according to the hand skeleton model; mapping the hand skeleton model into a digital twin virtual scene, presetting n gesture instruction modes in the digital twin virtual scene, and matching the hand skeleton model, the joint angle and the hand motion track with the gesture instruction modes; personalized and extensible gesture interaction capability is provided, and man-machine interaction modes are enriched.

Owner:JIANGSU I FRONT SCI & TECH CO LTD
System for advanced network traffic analysis in a computing environment
Systems, computer program products, and methods are described herein for advanced network traffic analysis in a computing environment. The present disclosure is configured to retrieve, from a traffic data log of a Web Application Firewall (WAF), information associated with a blocked traffic instance; implement, using a code analysis subsystem, a security testing protocol on a host application associated with the blocked traffic instance; determine an exposure associated with the host application based on at least implementing the security testing protocol; generate a notification comprising information associated with the exposure; and transmit a signal configured to cause a computing device associated with the host application to display the notification.

Owner:BANK OF AMERICA CORP
Real-time bidirectional communication between robotic process automation (RPA) robots and a web application
To performing real-time bidirectional communication between robotic process automation (RPA) robots and a web application, a robot initiates execution of a primary workflow when a request is received from a web application. The robot then listens for one or more triggers from the web application to start execution of a secondary workflow, and executes the secondary workflow when the one or more triggers are detected. The robot also returns a result of the execution of the secondary workflow to the web application.

Owner:UIPATH INC
Cloud-based web application and API protection from untrusted users and devices
ActiveUS12238070B2Specific access rightsKey distribution for secure communicationComputer networkWeb application
Systems and methods include, responsive to determining a user can access an application via a cloud-based system, wherein the application is in one of a public cloud, a private cloud, and an enterprise network, and wherein the user is remote over the Internet, obtaining a predetermined inspection profile for the user with the inspection profile including a plurality of rules evaluated in an order; performing inspection of the access using the plurality of rules in the order; and responsive to results of any of the plurality of rules, one or more of monitoring, allowing, blocking, and redirecting the access, via the cloud-based system.

Owner:ZSCALER INC
Mobile data management system
ActiveUS12211596B2Data processing applicationsHealth-index calculationWeb applicationMobile data management
A data management arrangement that comprises system(s) enabling monitoring and interconnectivity system resources and configuration parameters to be dynamically adapted to ensure re-defined data prioritization and associated essential minimal data interconnectivity is maintained during high-dependence or critical data applications with arrangement includes the capability to combine and adapt / adjust online network application services connectivity parameters and configurations, mobile or remote monitoring and / or information and communication technology in accordance to required monitoring criteria, monitoring and interconnectivity conditions, status of monitored individual or object, and / or available resources and conditions associated with said NAS connectivity and / or mobile or remote monitoring and / or ICT systems, in accordance to the application and applicable risk mitigation and high-dependence connectivity monitoring aspect and associated requirements, and the capability to combine mobile monitoring or computing location details with current and / or forecast and / or normal conditions in order to determine travel, health, and other alerts, advice and recommendations.

Owner:BURTON DAVID