
Tunnel connection request distribution method and device
A connection request and tunnel connection technology, applied in the field of data communication, can solve the problems of incompatibility with standard methods and unfavorable large-scale commercial applications
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2013-02-06
Smart Images
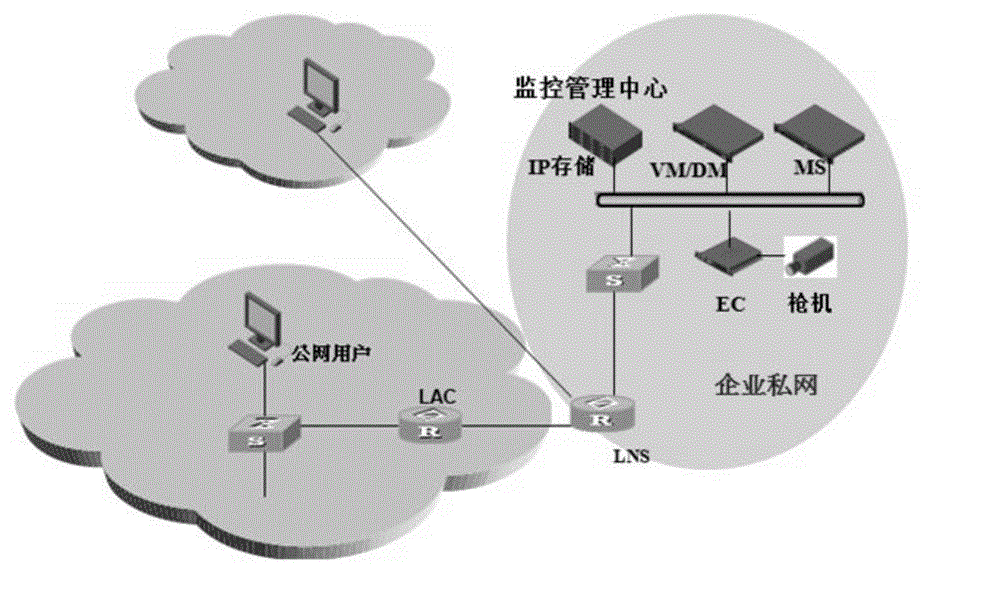
Figure 1 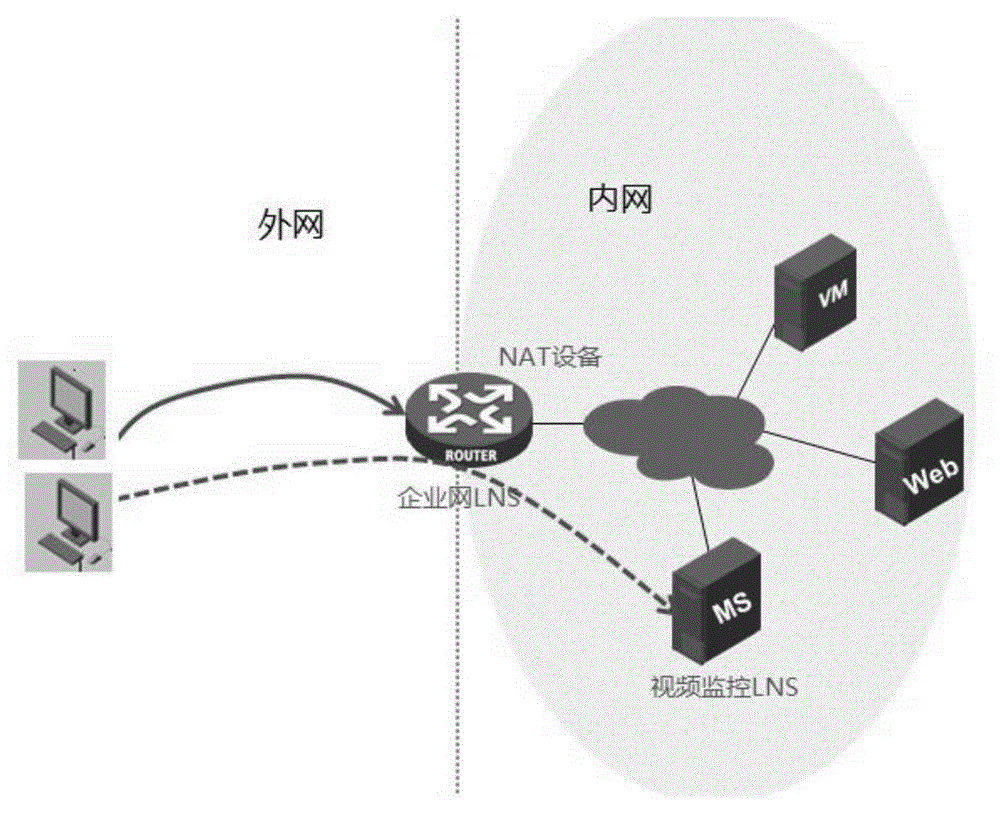
Figure 2 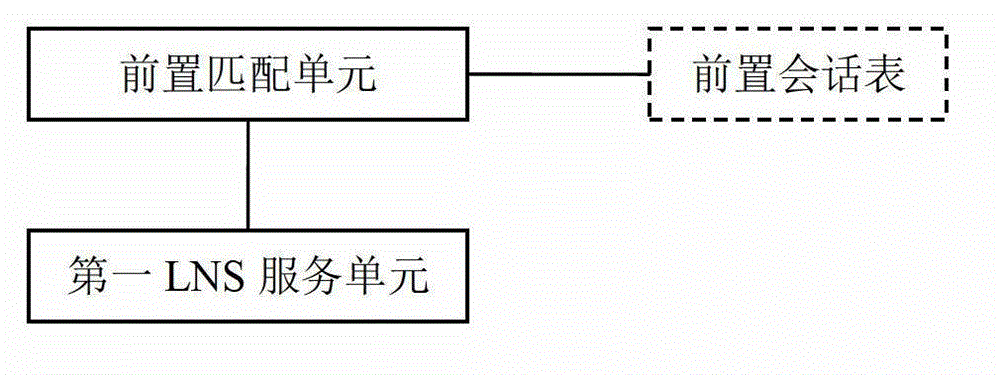
Figure 3
Abstract
Description
technical field
[0001] The invention relates to the field of data communication, in particular to a method and device for distributing tunnel connection requests in an enterprise network environment. Background technique
[0002] With the continuous development of standardized and easily expandable network technology, especially IP technology, intelligent video surveillance technology based on IP network has developed rapidly, and IP surveillance has become the mainstream of current surveillance. For security and cost reasons, most surveillance networks are deployed in private networks. Many mobile users or public network users use the decoding client (such as VC) to access the monitoring resources in the private network (such as the live resources on the encoder EC). private network access, figure 1 It is such a typical application scenario. For related technologies of using tunnels to traverse the monitoring network NAT, reference may be made to related patent applicatio...
Examples
Embodiment Construction
[0017] The present invention performs special processing in the authentication stage of the L2TP connection request, and under the premise of basically guaranteeing the user experience, intelligently identifies the user's L2TP connection request, and distributes the user's L2TP connection request to different service network front-end LNS servers for processing . The detailed implementation in the preferred embodiments of the present invention will be described below in conjunction with the accompanying drawings.
[0018] Please refer to figure 2 , image 3 as well as Figure 4 , The present invention provides a device for distributing tunnel connection requests. In a preferred embodiment, the present invention is realized by using a computer program, the device runs on the NAT gateway, and includes a pre-matching unit and an LNS service unit. The following describes the processing flow of the device running on the NAT gateway and cooperating with the existing functions o...