
Effective realization method for credible OpenSSH
An implementation method, a trusted technology, applied in electrical components, user identity/authority verification, transmission systems, etc., can solve problems such as security, functional compatibility, performance, and rapid deployment without considering and solving
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Patents(China)
- Current Assignee / Owner
- Publication Date
- 2013-10-30
- Estimated Expiration
- Not applicable · inactive patent
Smart Images
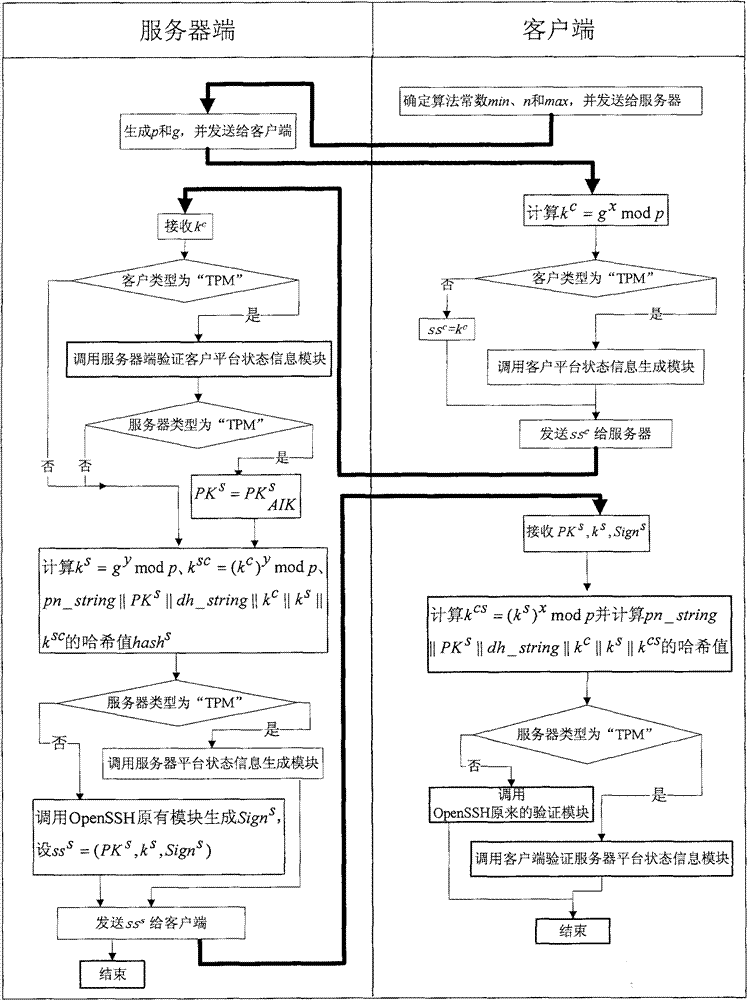
Figure 1 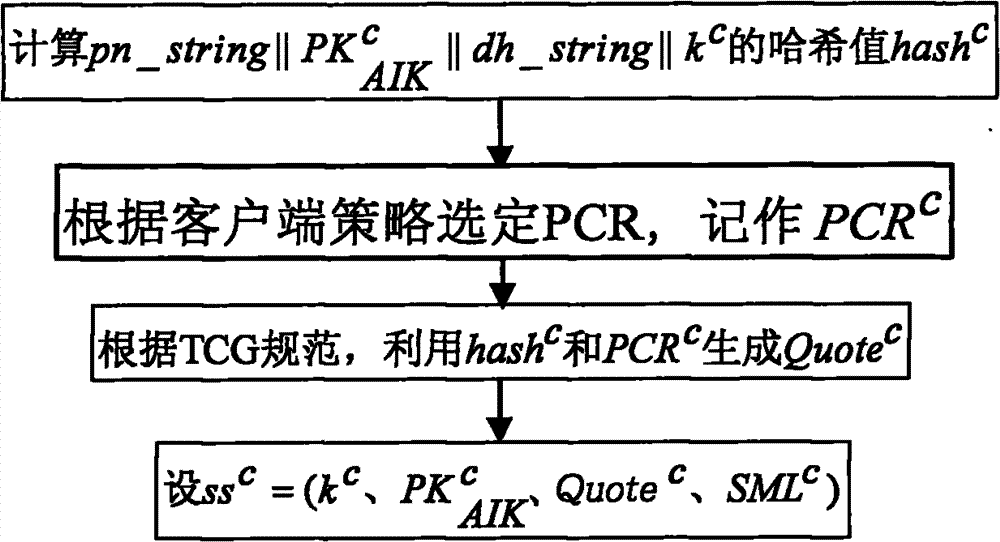
Figure 2 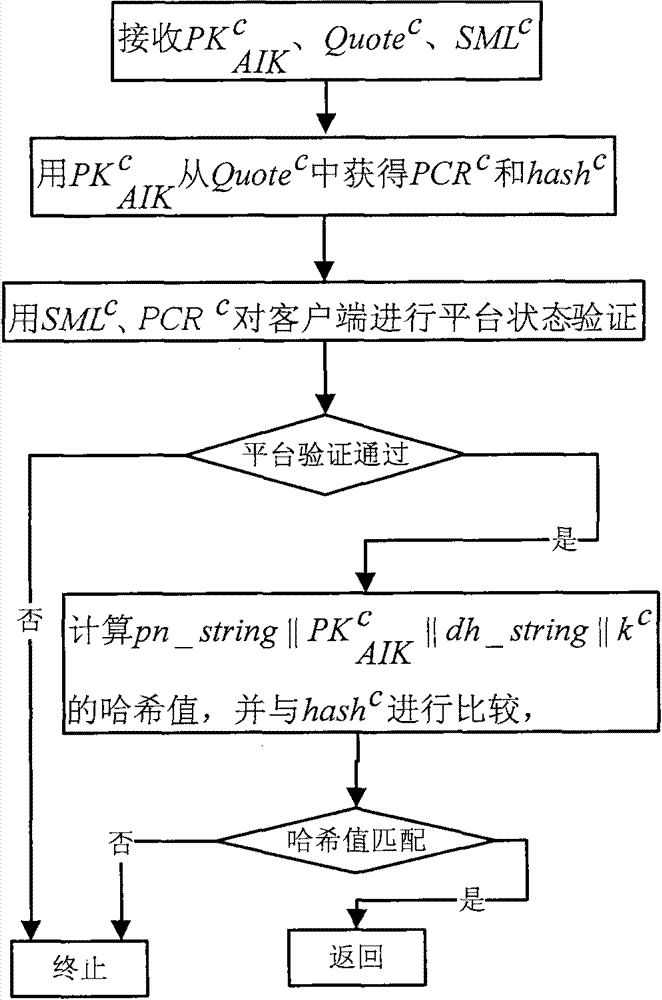
Figure 3
Abstract
Description
Technical field
[0001] The invention relates to an effective method for implementing trusted OpenSSH, which belongs to the field of computer information security. Background technique
[0002] The SSH (Secure Shell) protocol is a security protocol developed by the IETF's network working group to protect the data transmitted between the client and the server. The SSH protocol adopts a hierarchical structure design, including four sub-protocols: SSH transport layer sub-protocol, user authentication sub-protocol, connection sub-protocol and file transfer sub-protocol. When the client and the server communicate using the SSH protocol, the first implementation is the SSH transport layer sub-protocol, which is responsible for establishing a secure channel between the server and the client. The sub-protocol includes protocol version exchange and parameter negotiation (parameter negotiation content includes key The three processes of exchange method, identity authentication algorithm, h...
Examples
Embodiment Construction
[0032] The method provided by the present invention assumes that the server and the client are equipped with a trusted security chip TPM on the hardware, and the BIOS of the server and the client both support TPM; on the software, it is assumed that the server and the client are installed with an operating system trusted boot manager, A trusted operating system that supports hardware TPM and trusted measurement modules is installed. In addition, the server and client are installed with TPM software protocol stack (TrouSers) software. The specific implementation steps of the method provided by the present invention in version 4.7 and above of the open source OpenSSH software are as follows:
[0033] Step 1. Modify the formation process of the identity authentication algorithm negotiation string: add three candidates, which are represented by the variables ssh-TPM-TPM, ssh-TPM-option, and ssh-option-TPM; trusted client and available The server side constructs an identity authentica...