
Online formal verification of executable models
A propositional formula and statement technology, applied in the field of online formal verification of executable models, which can solve problems such as time-consuming, error-prone test cases, etc.
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Patents(China)
- Current Assignee / Owner
- Publication Date
- 2015-02-25
Smart Images
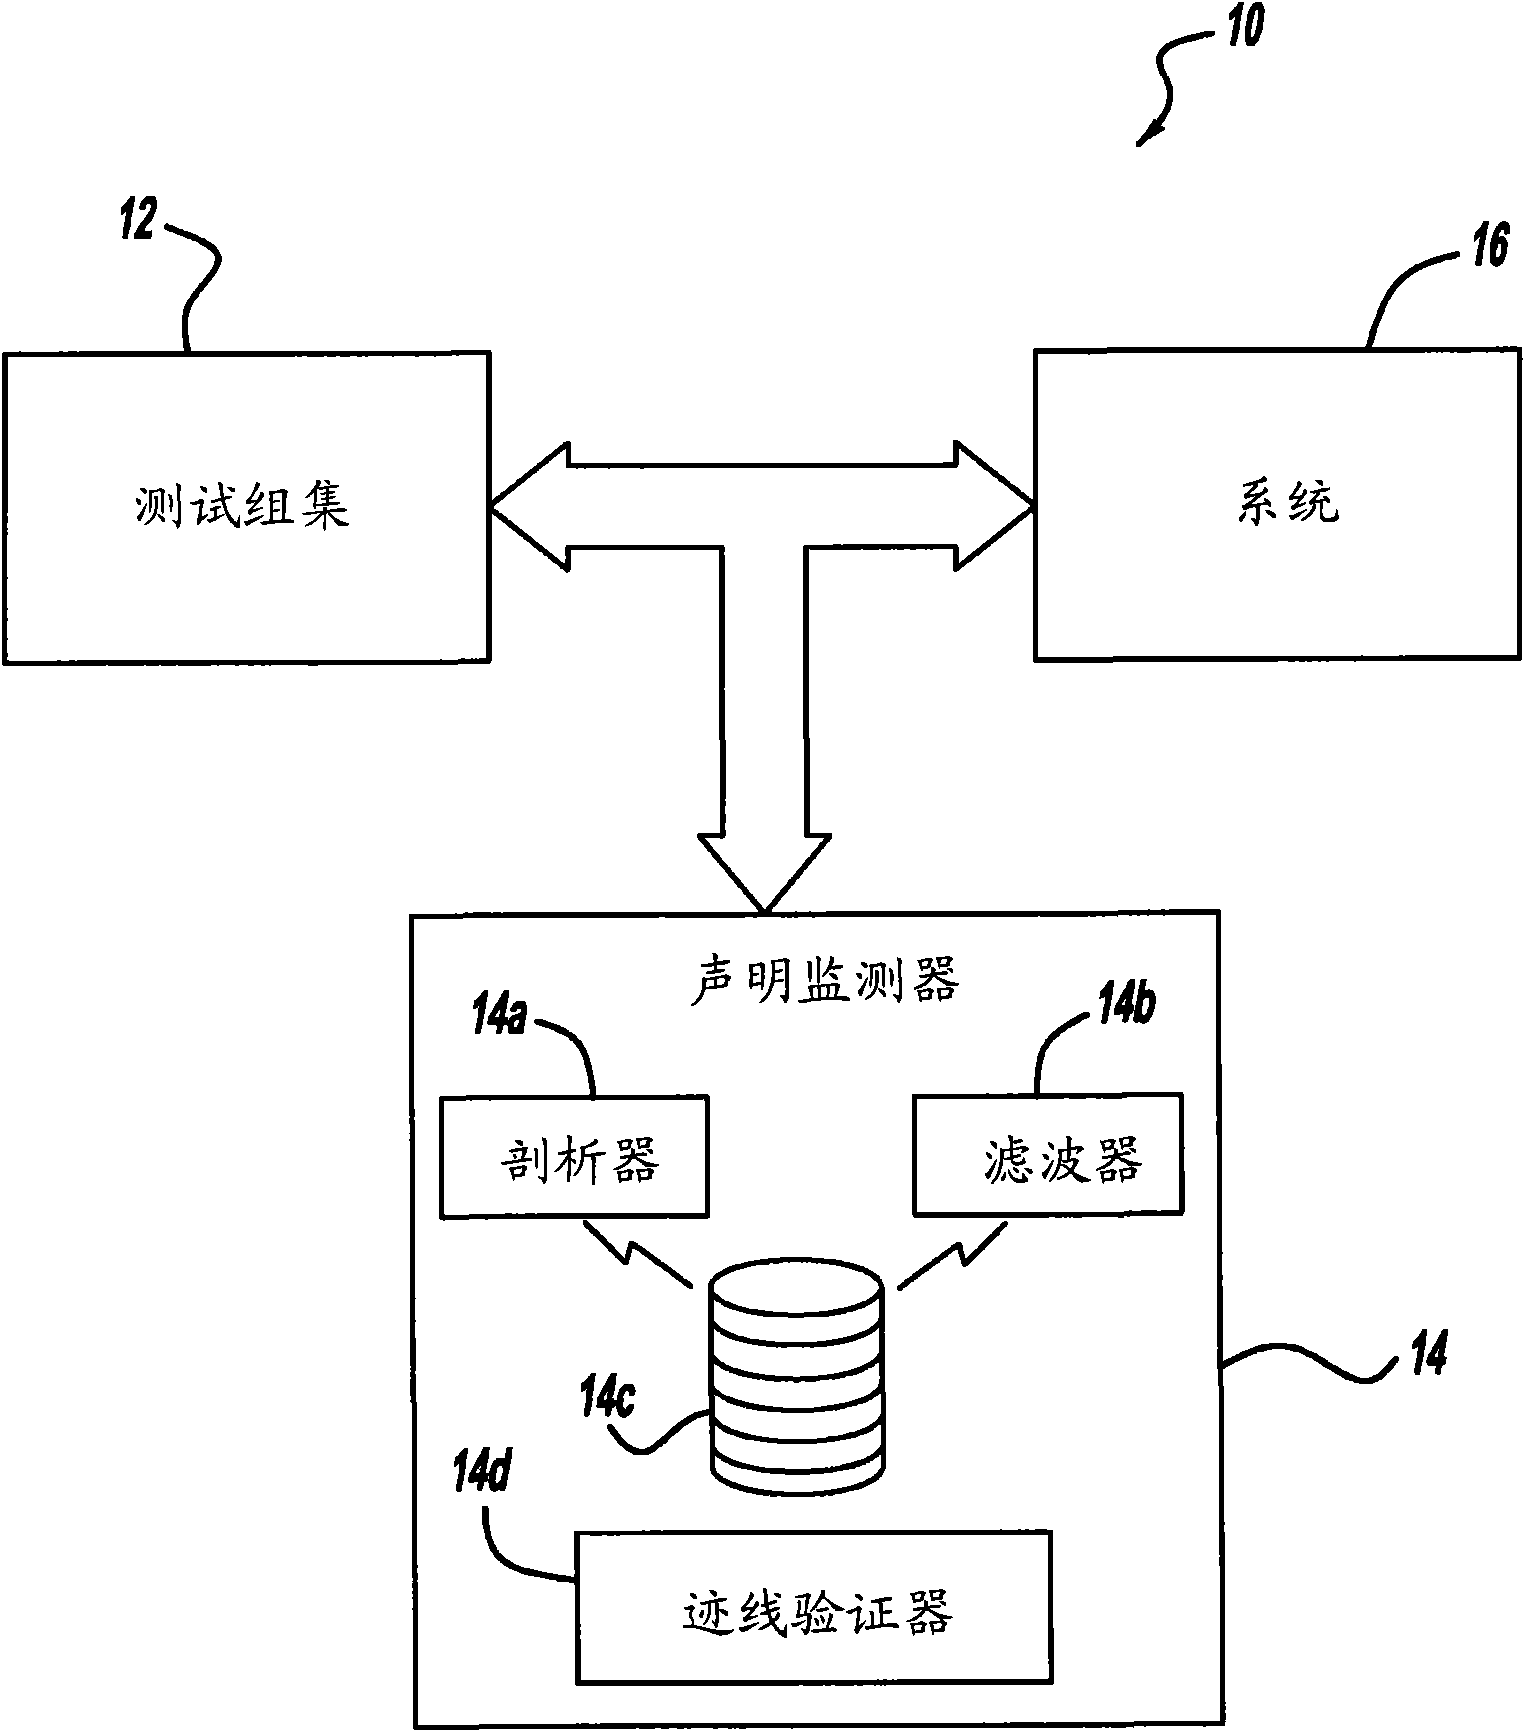
Figure 1 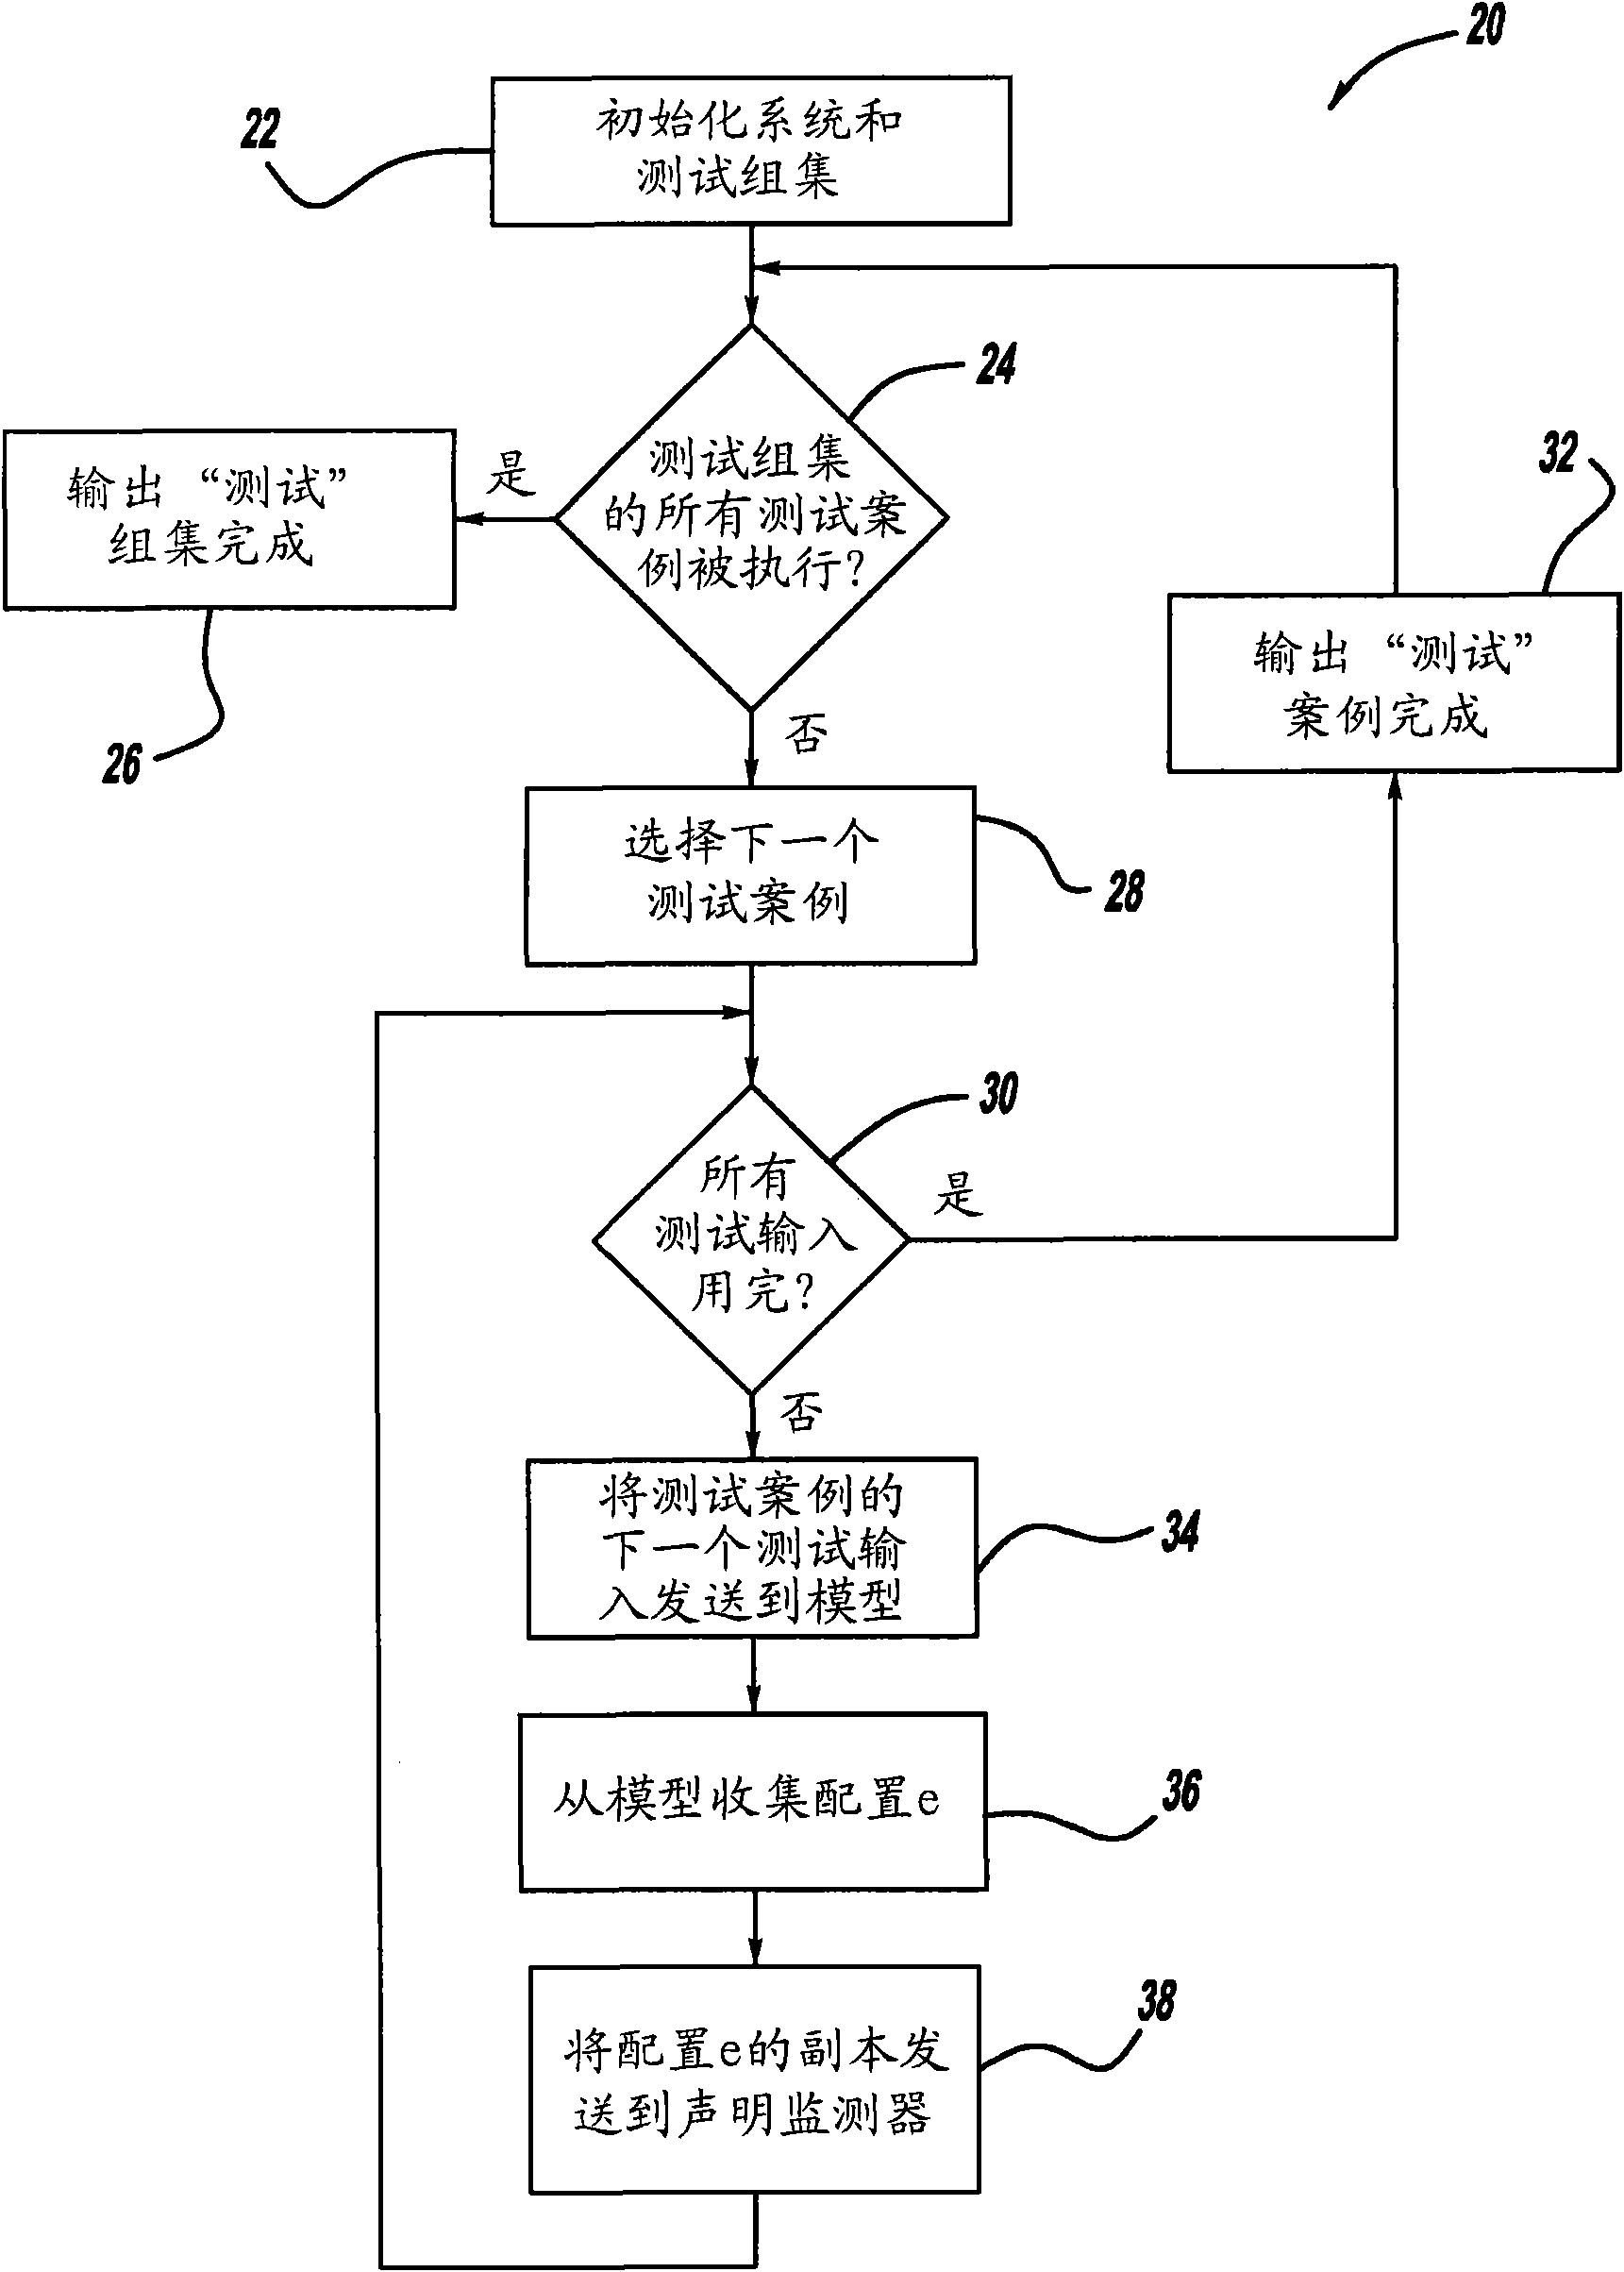
Figure 2 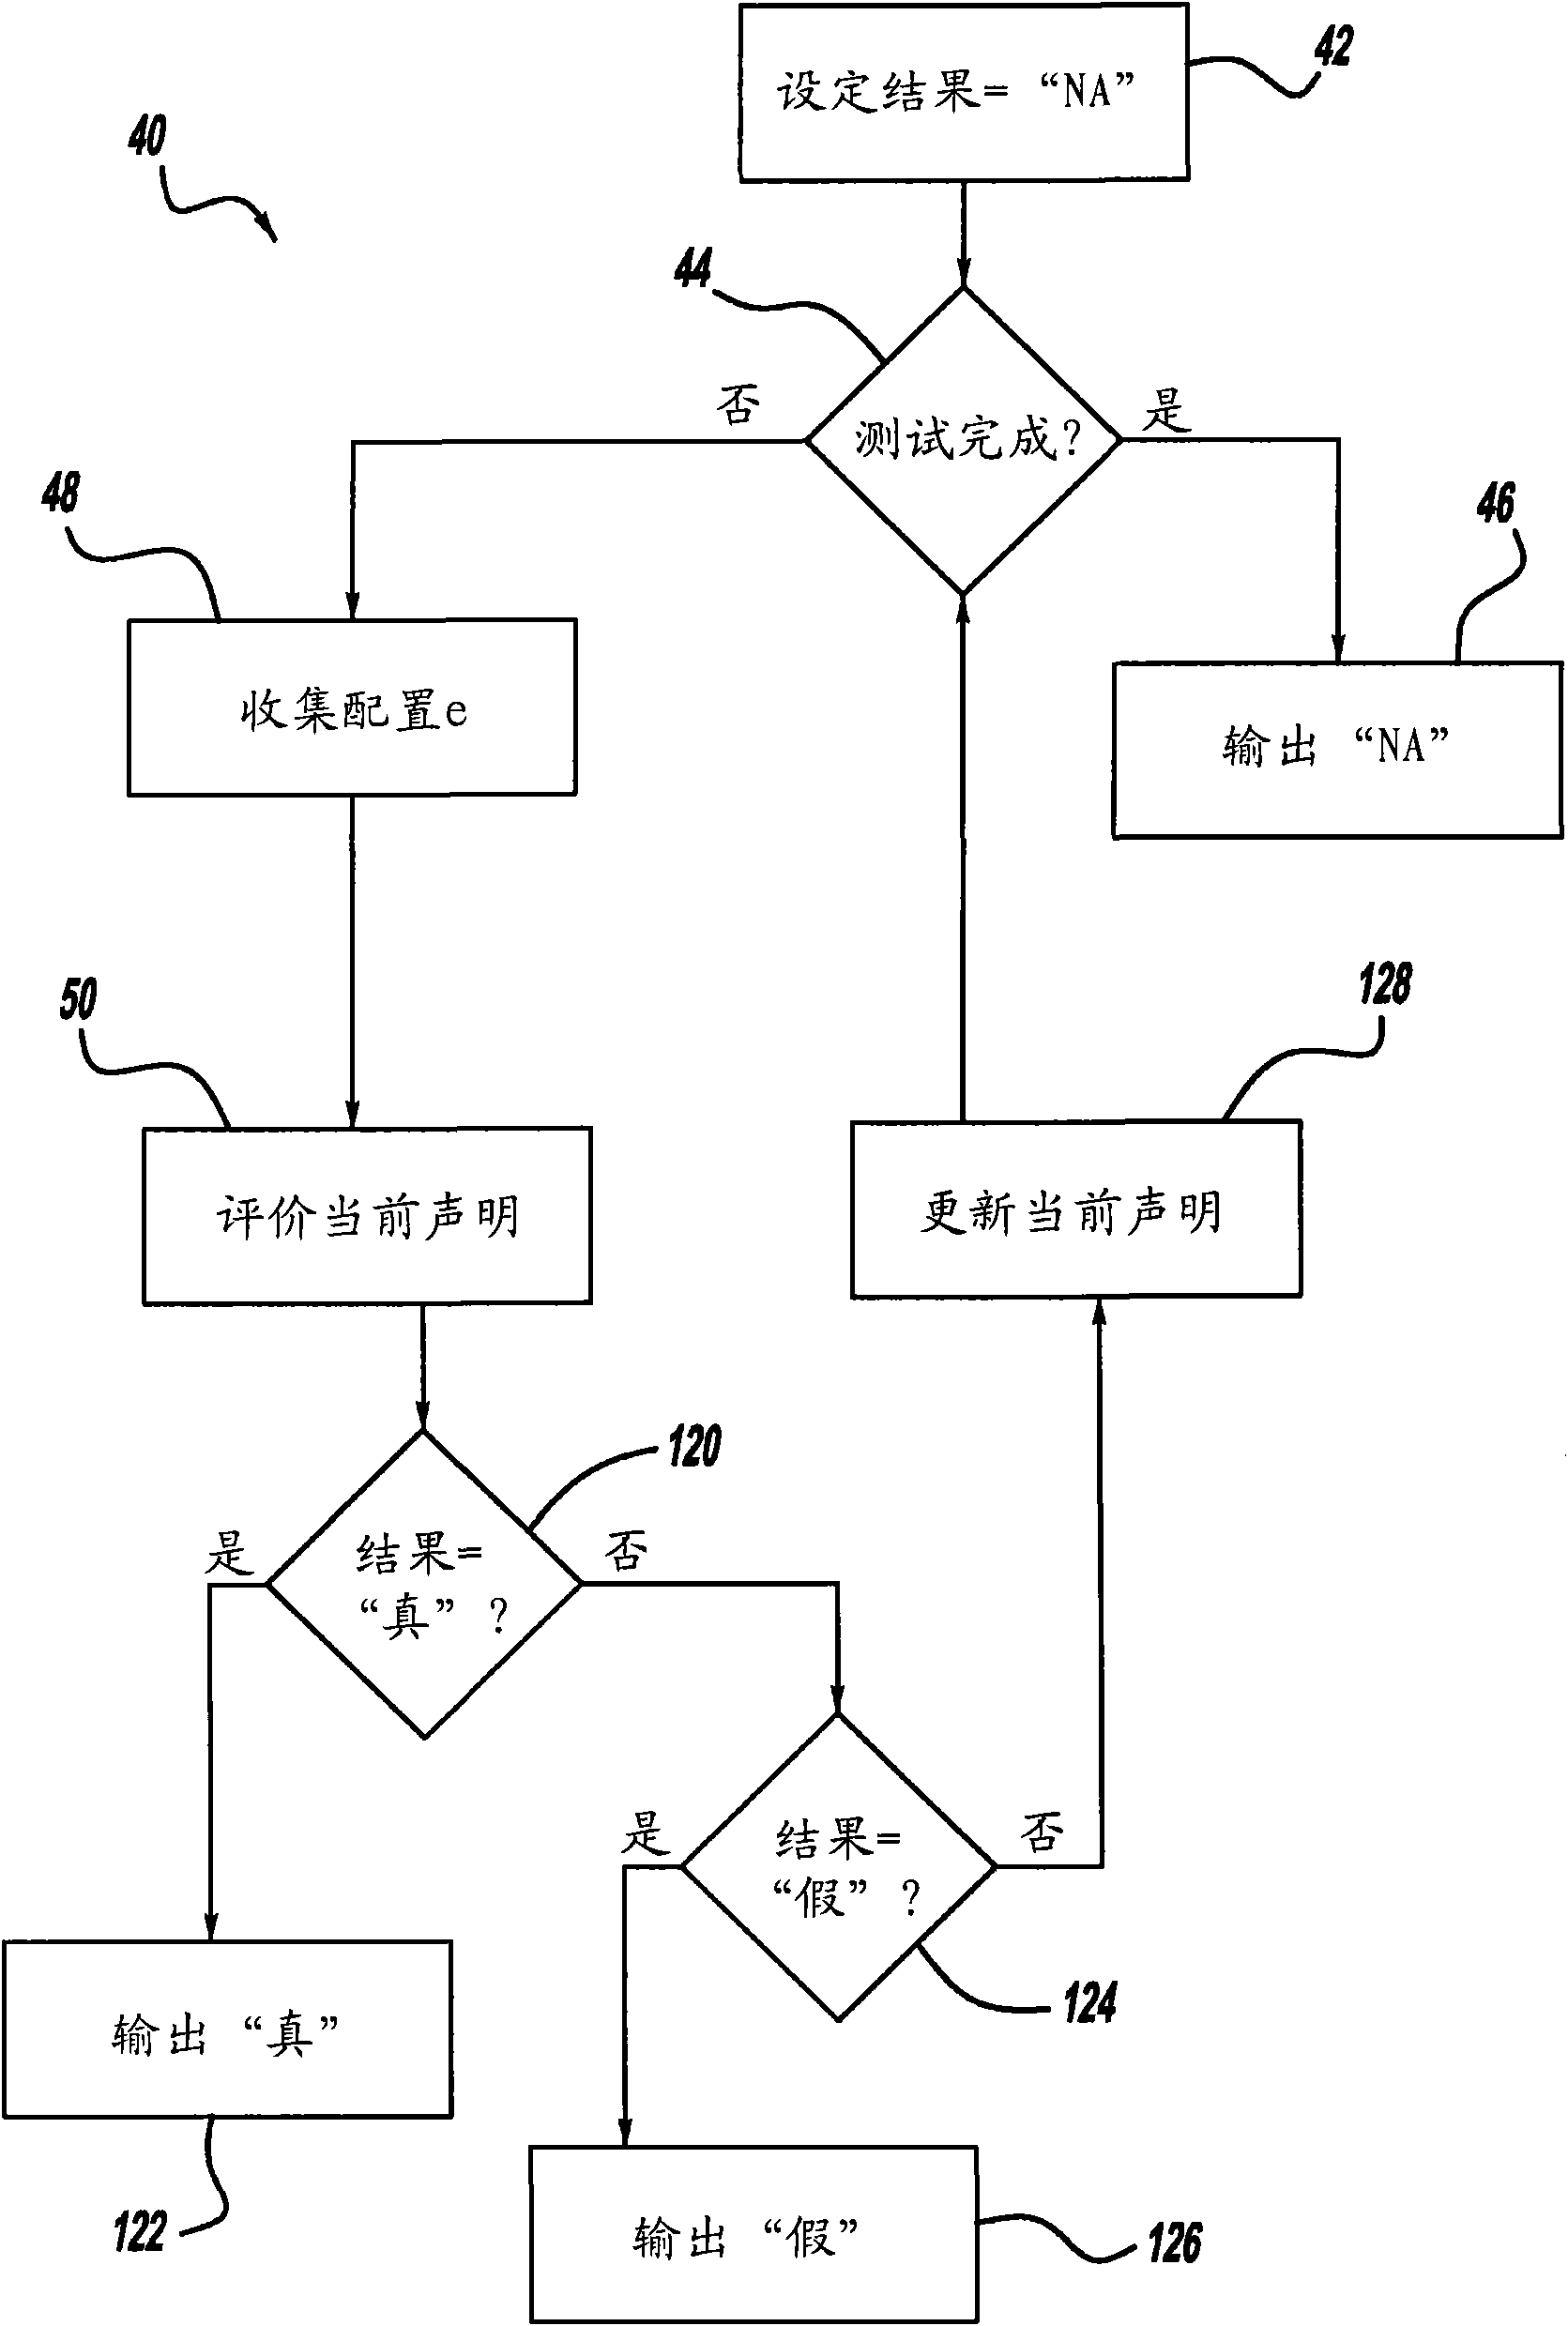
Figure 3
Abstract
Description
Background technique
[0001] Overall, the system development process includes a requirements development phase, a design and development phase, and a verification phase. Requirements can be characterized as documented needs for how a particular product or service should be implemented. More specifically, requirements may refer to statements that identify necessary functions, attributes, capabilities, characteristics, or qualities of a system. Requirements in the form of a requirements specification are used as input in the design phase of the system development process to design what elements and functions are necessary for a particular system.
[0002] Requirements specifications can be expressed in multiple languages. These languages may be graphical or textual in nature, and may include, but are not limited to, transition systems (eg, state machines), event sequence diagrams (eg, situation or sequence diagrams), and structured English language. Systems are implemented u...
Examples
Embodiment Construction
[0049]Embodiments described herein relate generally to systems and methods for formal verification of executable systems, and more particularly to systems and methods for automated formal verification of executable systems against specified portions of a specification. The systems and methods employ a claims-based authentication process that is scalable to any size system and configured to operate with or without direct access to the system (ie, online or offline, respectively).
[0050] An online method using a formal verification system to generate a suite of test cases to verify specific claims from a specification. Typically, a statement is a true-false statement used to verify some property of a variable contained in a specification. Test cases are simulated by the system and the results are sent to the claim monitor for evaluation and verification of claims.
[0051] Using an offline method of formal verification systems, a set of traces representing the sequence of sys...