

Malicious sample identification method and device, computing equipment and medium
A malicious and sample technology, applied in the computer field, can solve the problems of low recognition efficiency, single recognition method, and low recognition accuracy, and achieve the effect of improving recognition efficiency and recognition accuracy
Patent Information
- Authority / Receiving Office
- CN · China
- Current Assignee / Owner
- Publication Date
- 2021-01-12
Smart Images
Figure 1 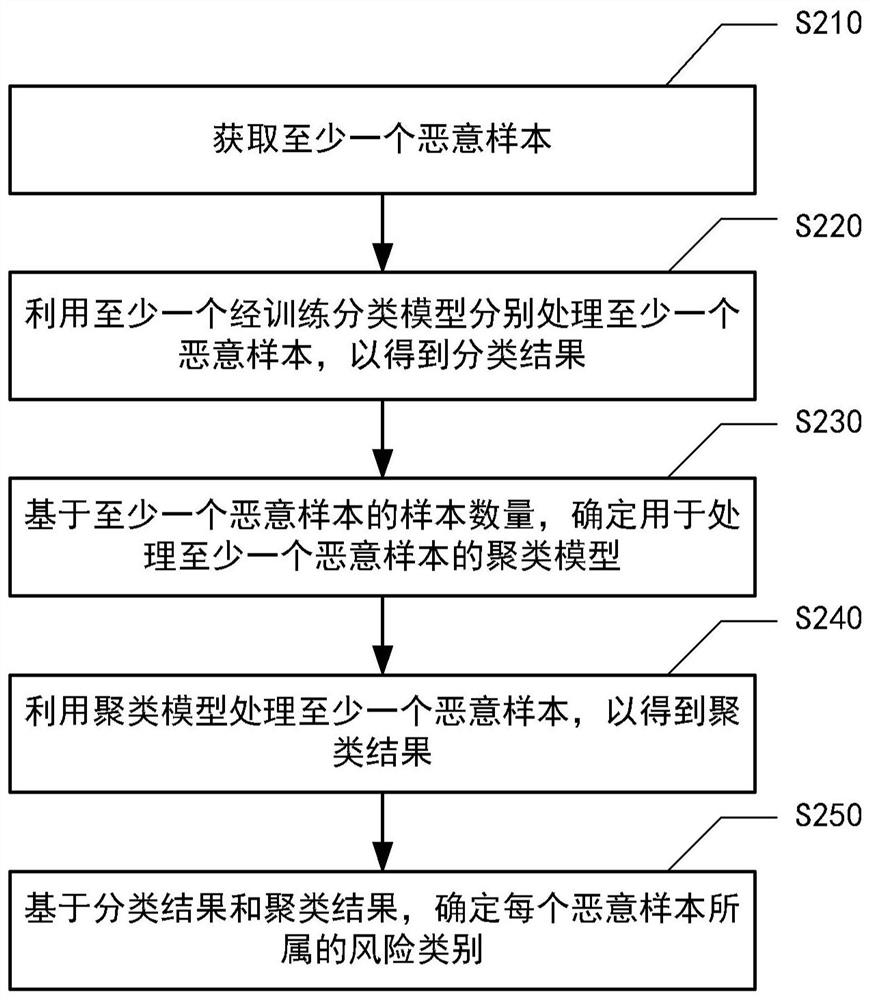
Figure 2 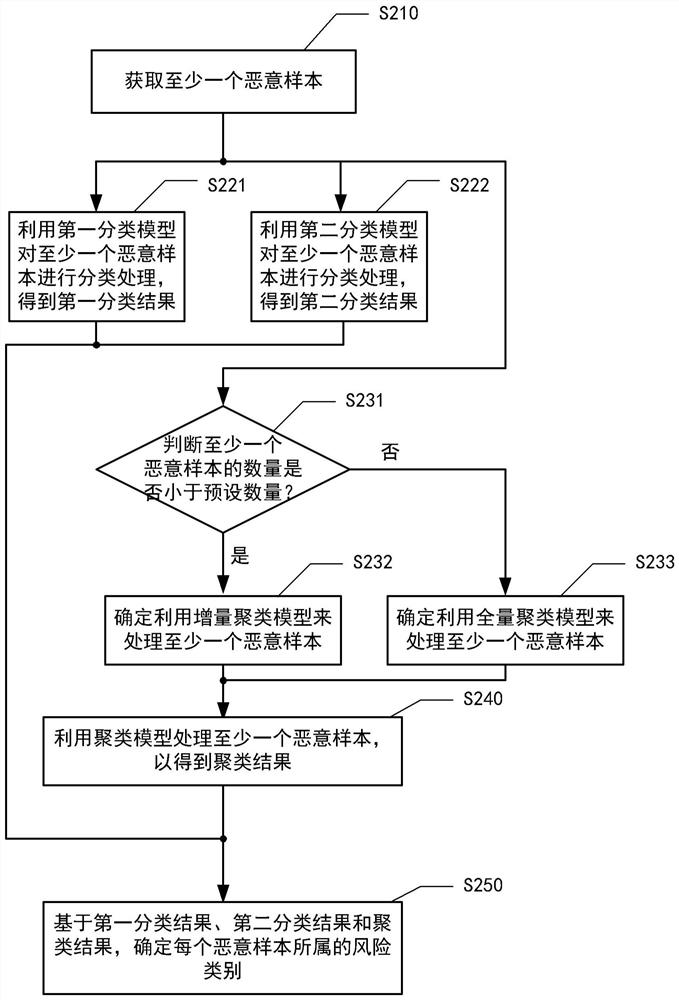
Figure 3
Abstract
Description
technical field
[0001] The present disclosure relates to the field of computer technology, and more specifically, to a malicious sample identification method, a malicious sample identification device, a computing device, and a computer-readable storage medium. Background technique
[0002] In order to improve system security, it is usually necessary to identify whether the samples accessing the system are risky, such as identifying the malicious family or attack group to which the malicious sample belongs. However, in order to avoid security detection, the important features of malicious samples are usually hidden and difficult to find. Related technologies usually use a single identification method to identify malicious samples, resulting in low identification efficiency when identifying the malicious family or attack group to which the malicious sample belongs. , The recognition accuracy is low. Contents of the invention
[0003] In view of this, the present disclosure ...
Examples
Embodiment Construction
[0029] Hereinafter, embodiments of the present disclosure will be described with reference to the drawings. It should be understood, however, that these descriptions are exemplary only, and are not intended to limit the scope of the present disclosure. In the following detailed description, for purposes of explanation, numerous specific details are set forth in order to provide a thorough understanding of the embodiments of the present disclosure. It may be evident, however, that one or more embodiments may be practiced without these specific details. Also, in the following description, descriptions of well-known structures and techniques are omitted to avoid unnecessarily obscuring the concept of the present disclosure.
[0030] The terminology used herein is for the purpose of describing particular embodiments only, and is not intended to be limiting of the present disclosure. The terms "comprising", "comprising", etc. used herein indicate the presence of stated features, ...