
Network port security-based micro-isolation system
A technology for isolating systems and network ports, applied in the field of micro-isolation systems, it can solve the problems of inconsistent hardware firewall functions, difficult upgrades, and increased procurement and maintenance costs, so as to solve the security management of east-west traffic and avoid the spread of attack risks.
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2022-02-18
Smart Images
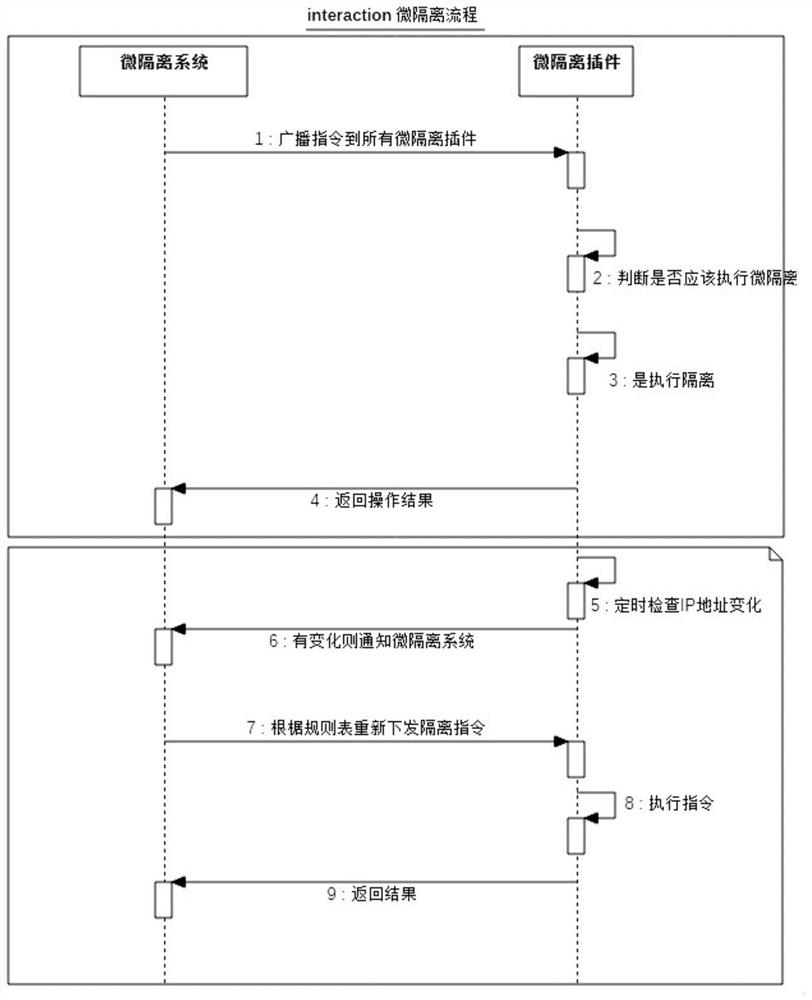
Figure 1 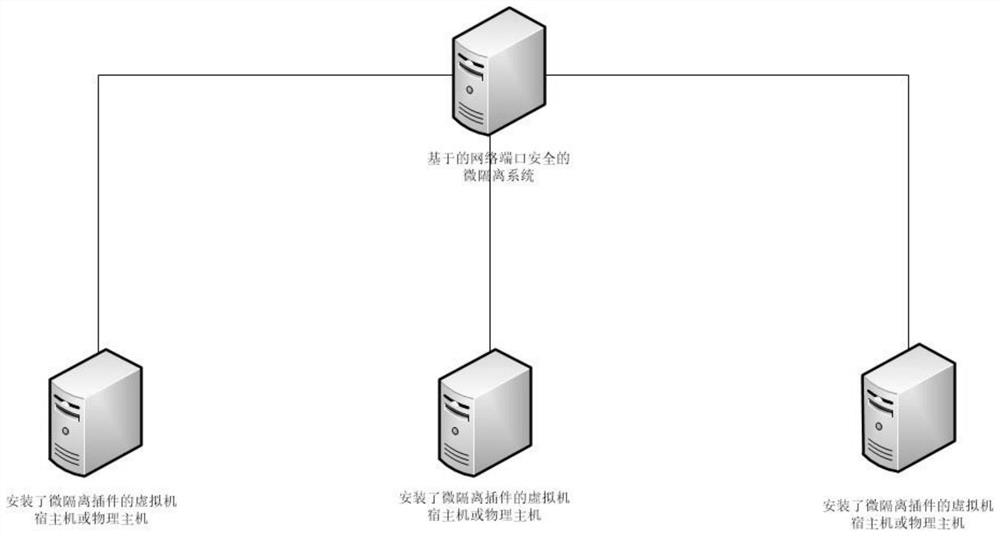
Figure 2 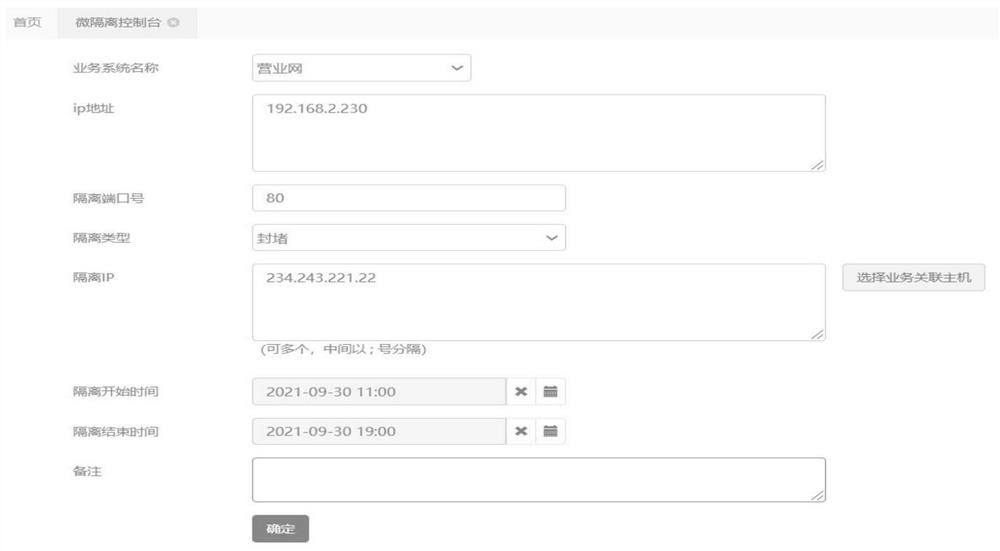
Figure 3
Abstract
Description
technical field
[0001] The invention relates to the field of network security, in particular to a micro-isolation system based on network port security. Background technique
[0002] With the rapid development of cloud computing and virtualization technologies, more and more enterprises are migrating data and services to multiple data center environments spanning physical machines, public clouds, private clouds, and hybrid clouds. When the attacker has the opportunity to get a springboard machine on the intranet, it turns out that the intranet network is basically unimpeded. Traditional firewalls, WAFs, IPS and other endpoint security and network security methods are stretched in the cloud environment.
[0003] Network-oriented micro-isolation control, through comprehensive and detailed visual analysis of network internal traffic, monitoring network port activities, and based on fine-grained security access policies, it helps users quickly and easily realize isolation of dif...
Examples
Embodiment
[0040] Example: The specific micro-isolation implementation process is as follows:
[0041] S1. Through the micro-isolation system, issue isolation instructions to the micro-isolation plug-in of the host (such as image 3 shown);
[0042] S2. The micro-isolation plug-in receives the instruction, executes the isolation, and returns the result (such as Figure 4 shown); specifically, through the following steps:
[0043] S21. Install the micro-isolation plug-in on each host computer, and broadcast instructions from the micro-isolation system to all micro-isolation plug-ins;
[0044] S22, the micro-isolation plug-in, compares whether the server IP address in the instruction is consistent with the external IP address of the server local machine and the internal virtual machine, thereby judging whether the isolation instruction should be executed at the local firewall;
[0045] S23. After it is determined that it needs to be executed, execute the isolation instruction;
[0046]...