
Network safety guarded distributing invading detection and internal net monitoring system and method thereof
A technology for network security and intrusion detection, applied in transmission systems, digital transmission systems, data exchange networks, etc., can solve problems affecting data flow speed, lack of internal network monitoring, poor scalability, etc., to improve fault tolerance and reliability, The effect of standardizing the behavior of internal operators and blocking external intrusion
Patent Information
- Authority / Receiving Office
- CN · China
- Current Assignee / Owner
- Publication Date
- 2005-01-12
- Estimated Expiration
- Not applicable · inactive patent
Smart Images
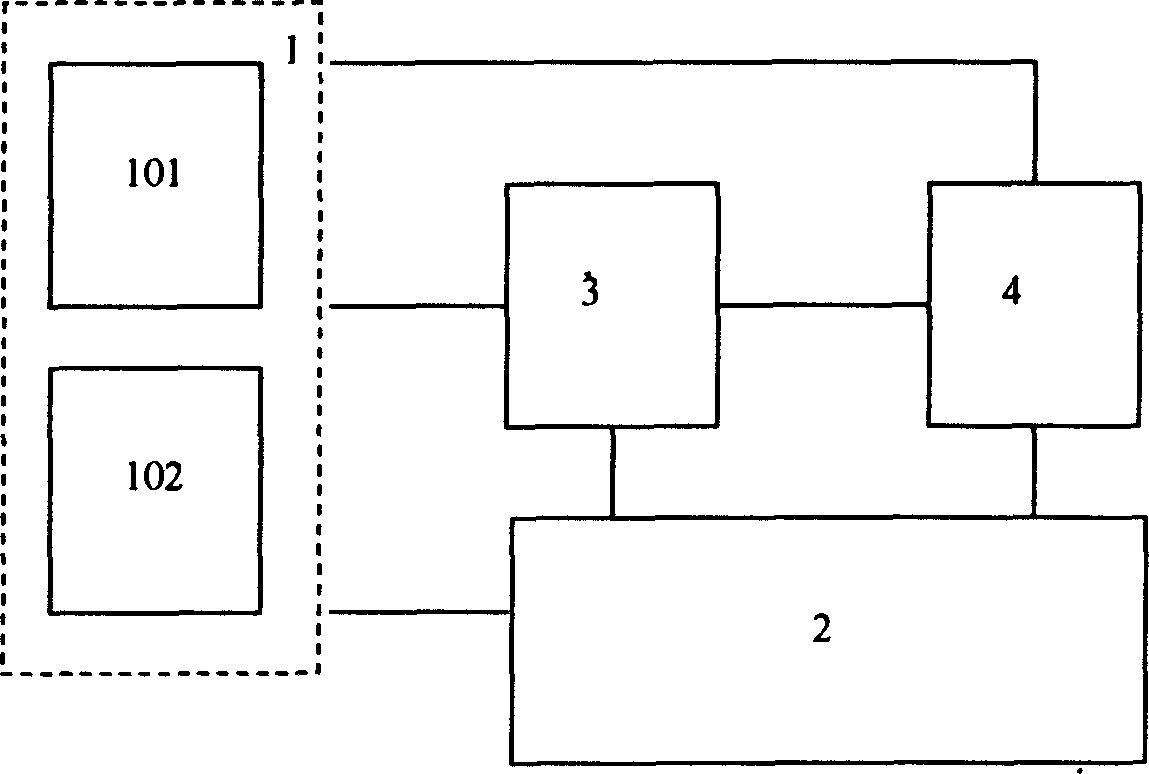
Figure 1 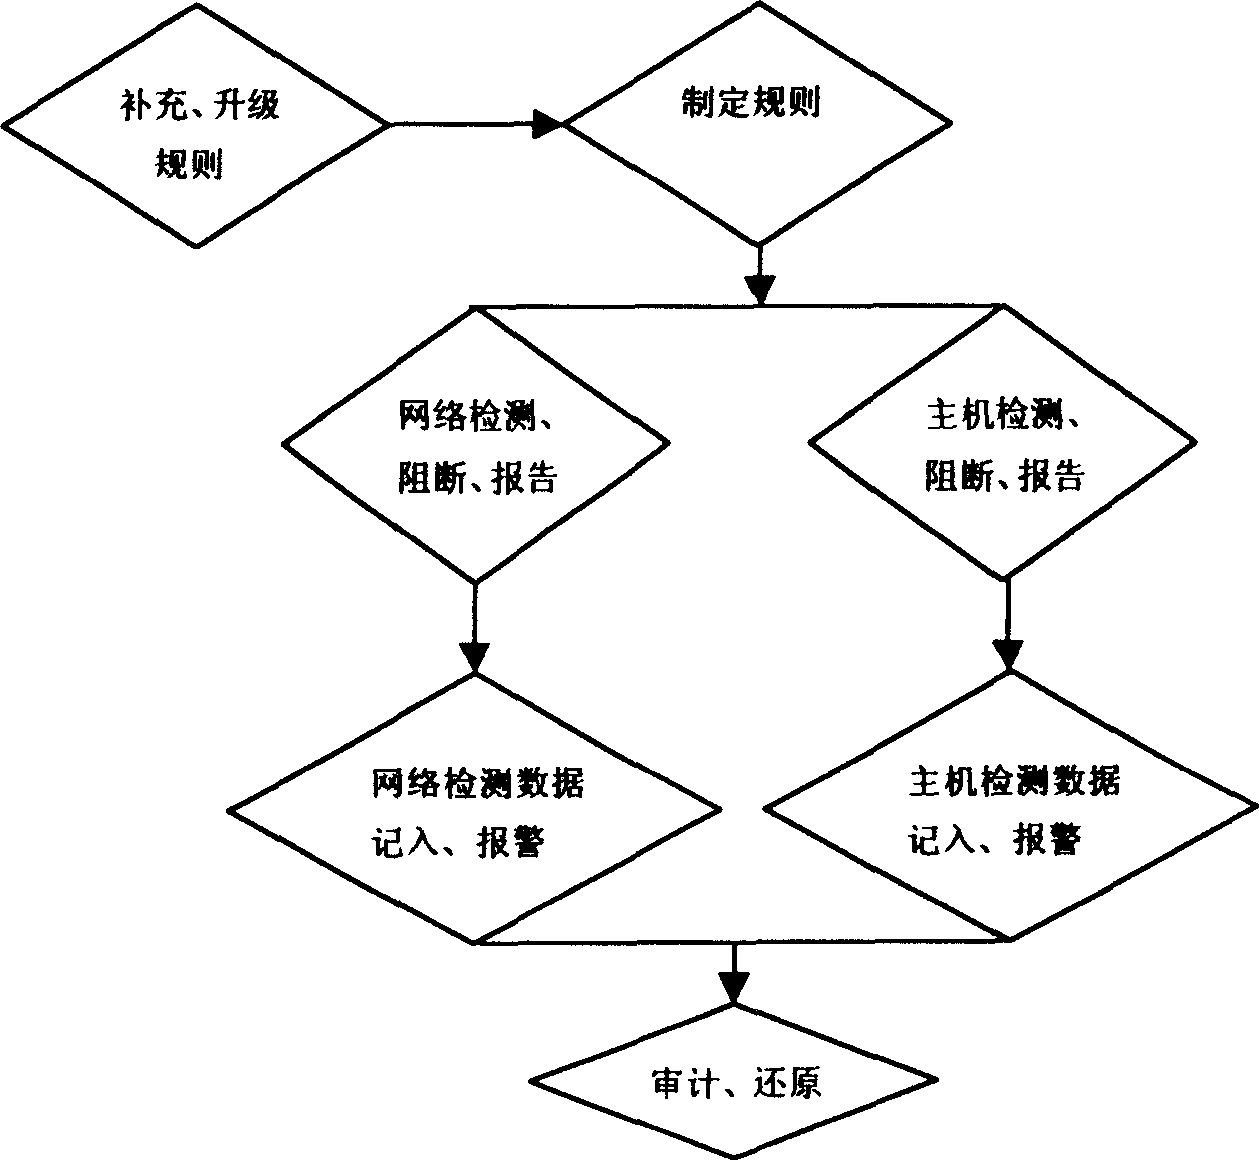
Figure 2 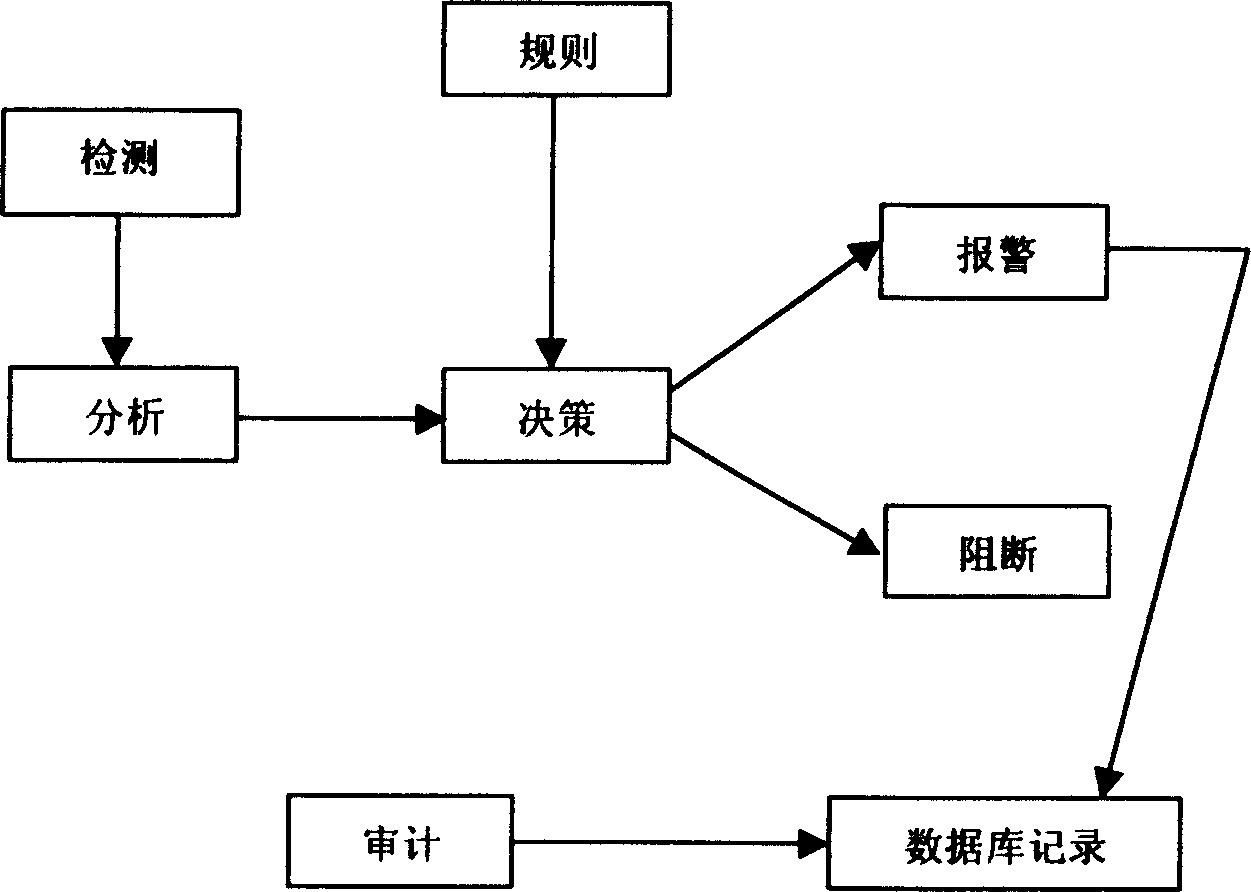
Figure 3
Abstract
Description
technical field
[0001] The invention relates to a system and method for network security protection, in particular to a distributed intrusion detection and intranet monitoring system and method for network security protection. The system and method can provide network security guarantees for internal LAN and network users connected to the Internet. It is suitable for secret-related networks with strict requirements on network security, as well as financial, insurance, electric power, tobacco, education, securities, etc. Large and medium-sized networks with large networks, complex network conditions, and centralized management of network security. Background technique
[0002] With the wide application of the Internet and the rapid development of e-commerce, higher and higher requirements are put forward for network security technology, and network security has become an important issue of concern to governments and enterprises all over the world. At present, anti-virus soft...
Examples
Embodiment Construction
[0022] For an embodiment of the network security protection system of the present invention, see figure 1 . The distributed intrusion detection and intranet monitoring system for network security protection has a three-layer distributed structure, including a detector 1, a central controller 2, a management monitoring center 3 and a background database 4. The detector 1 includes a network detector 101 and a host detector 102 . The network detector 101 and the host detector 102 are connected with the central processing unit 2 , the management monitoring center 3 and the background database 4 .
[0023] Embodiment Network detector 102 is distributed in sensitive parts of the network, based on advanced network message capture technology, monitors the data flow of the network in real time, analyzes the data flow in real time according to the security rules formulated by the management and monitoring center 3, and finds network attacks or network attacks. In the case of violation...