
Semi-supervised intrusion detection method combining improved Grey Wolf algorithm
An intrusion detection and semi-supervised technology, applied in the field of network information security, can solve the problems of low solution accuracy, difficulty in coordinating the exploration and development capabilities of the wolf algorithm, and achieve the effect of high detection accuracy and guaranteed detection accuracy.
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2018-09-11
Smart Images
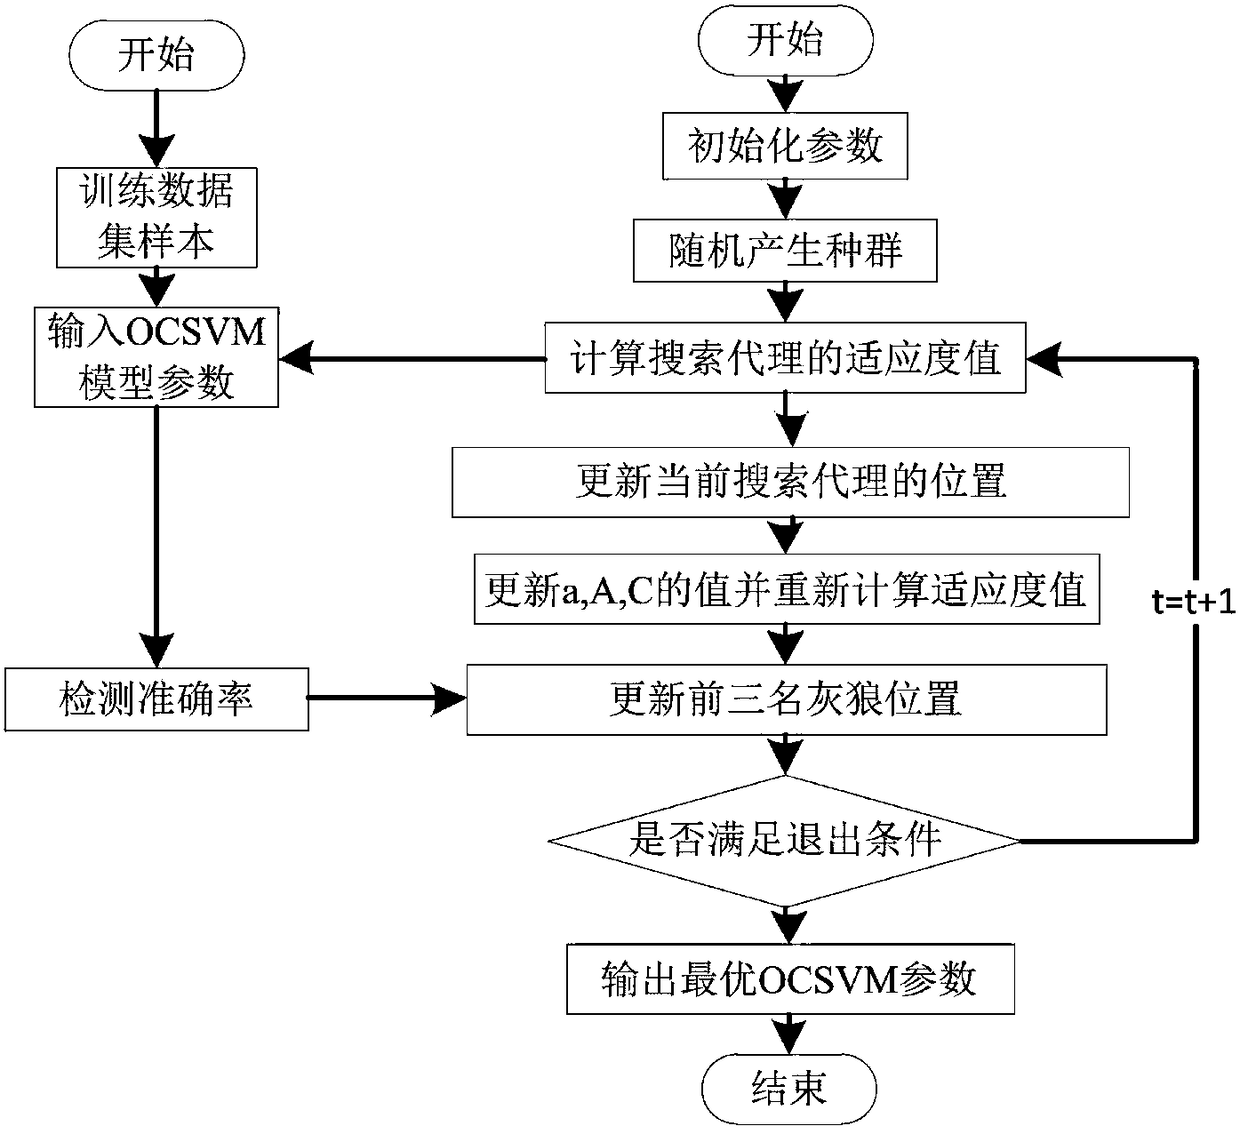
Figure 1 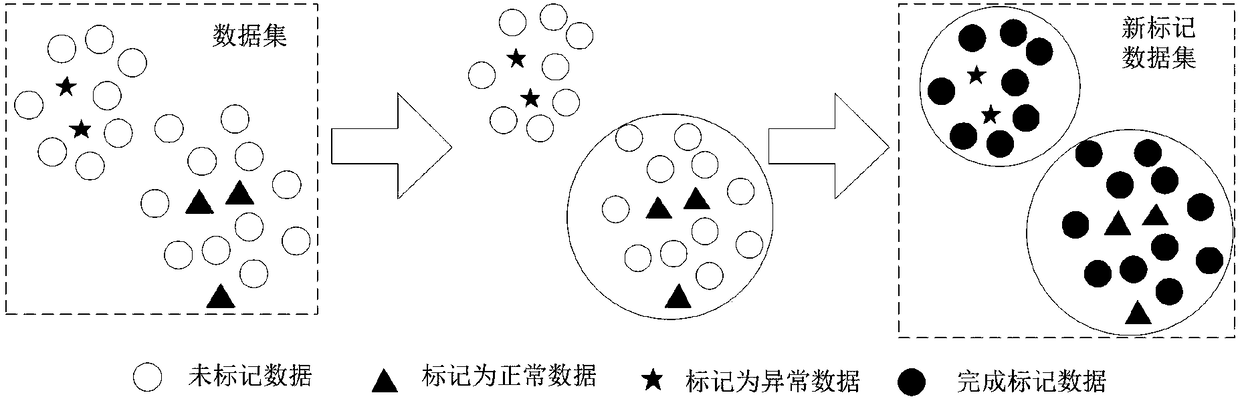
Figure 2 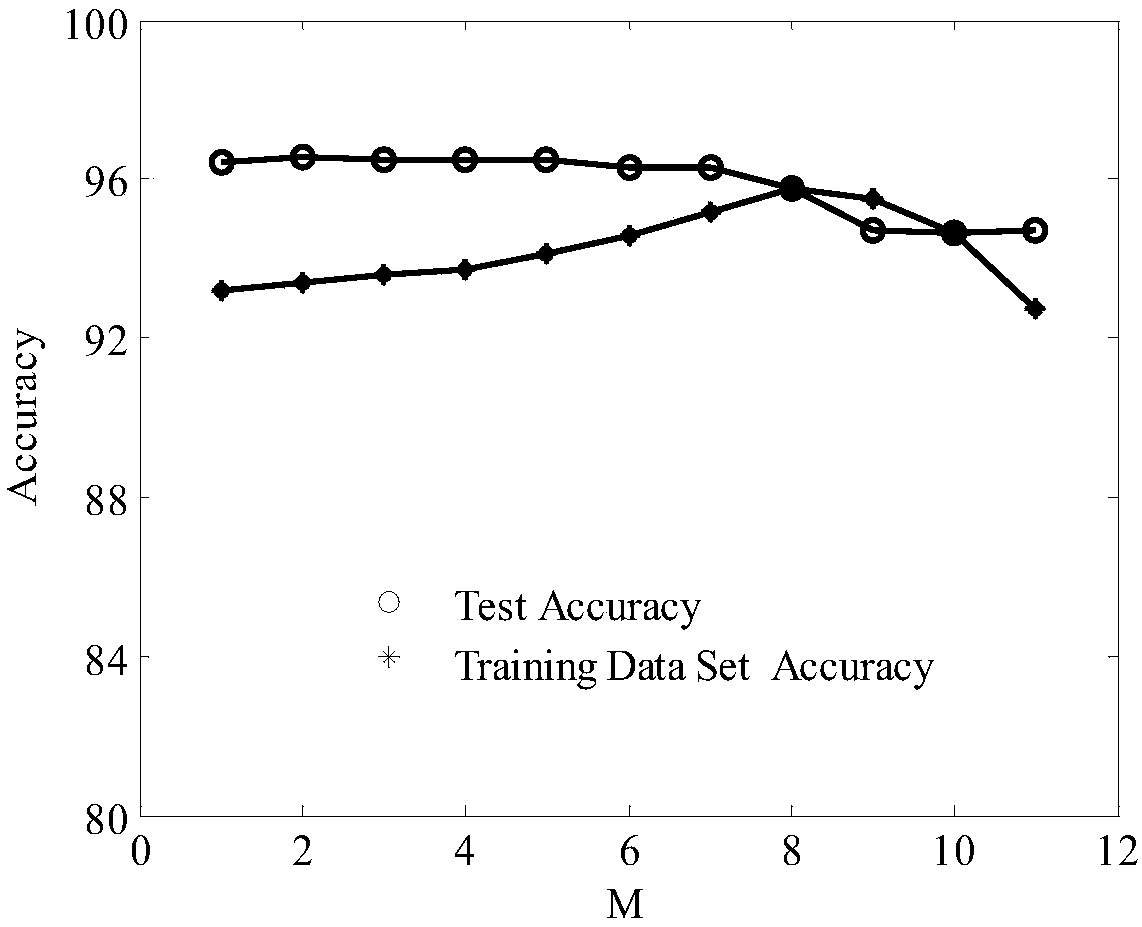
Figure 3
Abstract
Description
technical field
[0001] The invention relates to a semi-supervised intrusion detection method of an improved wolf algorithm, which belongs to the technical field of network information security. Background technique
[0002] With the rapid development of Industry 4.0 and related technologies, however, there are inevitable loopholes in the existing industrial communication protocols, which make the industrial control network vulnerable to malicious attacks by attackers. In 2010, the attackers used the Stuxnet virus to destroy Iran’s nuclear facilities, causing A serious accident occurred, which sounded the alarm for the safety of industrial control systems.
[0003] Industrial control network intrusion detection can be divided into two categories: misuse detection and anomaly detection. For anomaly detection, it can be divided into three categories: statistics-based methods, knowledge-based methods and machine learning-based methods. Commonly used industrial control network i...
Examples
Embodiment Construction
[0034] In order to solve the difficulty in adaptively selecting the characteristics of unknown attack traffic in the industrial control network, and the time-consuming and labor-intensive training data sets of a large number of accurately marked, the present invention adopts the cloud gray wolf algorithm to optimize the semi-supervised learning method of the K-means clustering center, using a small amount of Correctly mark the samples to generate a large-scale training data set, and then use the cloud gray wolf algorithm to optimize the parameters of the single-class support vector machine to more efficiently detect unknown attacks.
[0035] The present invention will be described in further detail below in conjunction with the accompanying drawings.
[0036] Step 1: Combine the basic GWO algorithm with the cloud model algorithm, optimize the control parameters of the GWO algorithm, and obtain the cloud GWO algorithm, so that it can obtain a larger search area and increase its ...