
Hybrid encryption-based network transmission data security processing method
A technology for network transmission and data security, applied in key distribution, to achieve the effect of ingenious design, guaranteed security, and unique method
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2019-01-04
- Estimated Expiration
- Not applicable · inactive patent
Smart Images
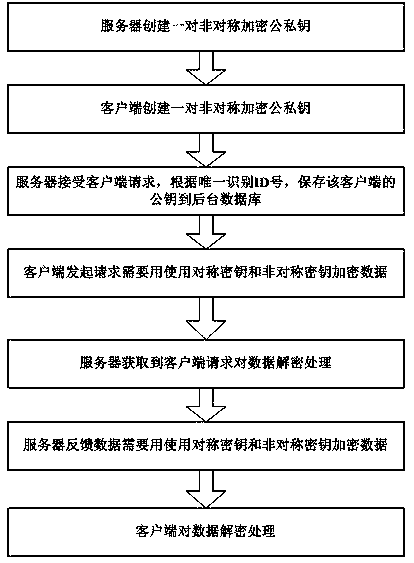
Figure 1 
Figure 2 
Figure 3
Abstract
Description
technical field
[0001] The invention relates to the technical field of network security evaluation, in particular to a method for safely processing network transmission data based on hybrid encryption. Background technique
[0002] The Internet is an open system for the public. At the beginning of its design, the security of the information transmitted on the network was not fully considered. With the rapid development of network technology, the network security problems caused by it are becoming more and more serious. How to protect the information transmitted on the network, that is, the security of data transmitted on the network, is becoming more and more important.
[0003] All related theories and technologies related to the confidentiality, authenticity, availability, integrity and controllability of network information belong to the research field of network information security. Information security technology mainly includes encryption, detection, authentication, m...
Examples
Embodiment Construction
[0034] The present invention will be further described below in conjunction with the accompanying drawings.
[0035] Such as figure 1 As shown, the network transmission data security processing method based on hybrid encryption of the present invention includes the following steps,
[0036] Step (A), the server creates a pair of asymmetric encrypted public and private keys, including A-PublicKey and A-PrivateKey, the server stores the private key A-PrivateKey, and the public key A-PublicKey is open to all clients, and the client needs to save the public key ;
[0037] Step (B), the client creates a pair of asymmetric encrypted public-private keys B-PublicKey and B-PrivateKey, the client creates and saves the private key B-PrivateKey locally, initiates an upload request to upload the public key B-PublicKey to the server, and uploads the The unique identification ID number of the client, the unique identification ID number of the client is UDID, and the UDID is the unique devi...