
Role-Based Menu Authorization Method
一种菜单、角色的技术,应用在基于角色的菜单授权领域,能够解决操作频繁、难记住角色权限差别、效率低等问题,达到提高授权效率的效果
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Patents(China)
- Current Assignee / Owner
- Publication Date
- 2021-04-06
Smart Images
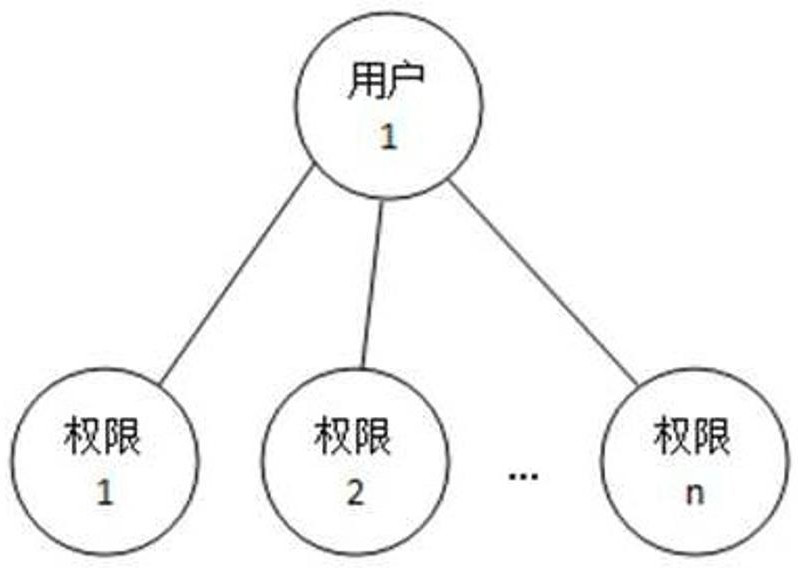
Figure 1 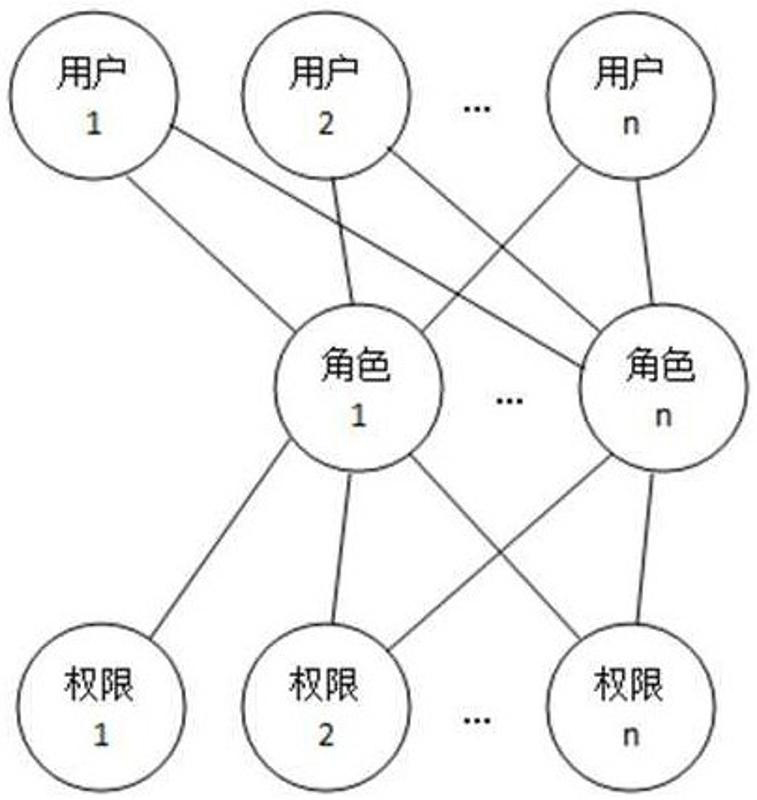
Figure 2 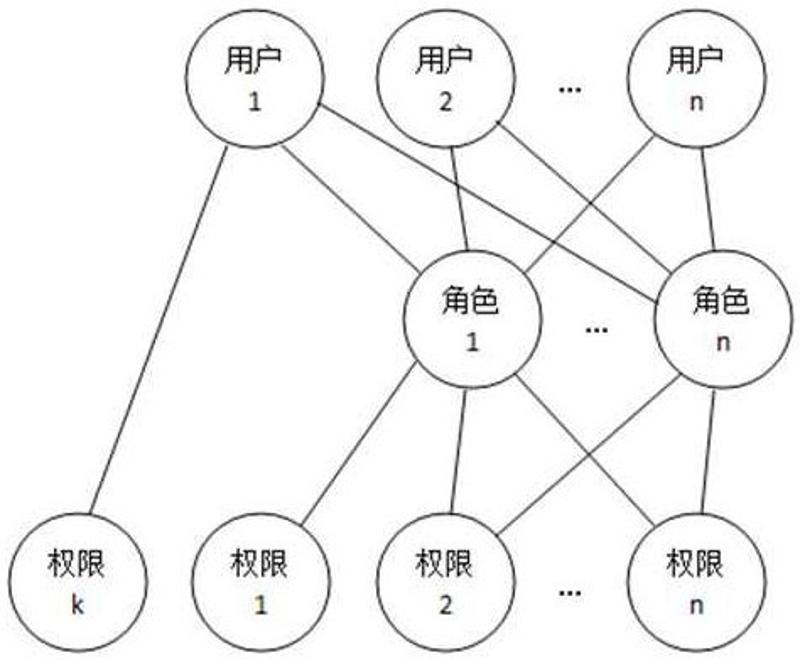
Figure 3
Abstract
Description
technical field
[0001] The invention relates to a form authorization method of management software systems such as ERP, in particular to a role-based menu authorization method. Background technique
[0002] Role-based access control (RBAC) is the most researched and thoughtful database permission management mechanism in recent years. It is considered to be an ideal candidate to replace traditional mandatory access control (MAC) and discretionary access control (DAC). The basic idea of role-based access control (RBAC) is to divide different roles according to different functional positions in the enterprise organization view, encapsulate the access rights of database resources in roles, and users can indirectly access database resources by being assigned different roles.
[0003] There are often a large number of tables and views in large-scale application systems, which makes the management and authorization of database resources very complicated. It is very difficult for...
Examples
Embodiment 2
[0056] [Embodiment 2] A role-based menu authorization method, including: Select authorized objects: select one or more roles as authorized objects, each role is an independent individual, not a group / category, and one role can only Associate a unique user, and a user is associated with one or more roles; perform menu authorization on authorized objects: display the permission candidate menu, select an existing role or a created template as the authorization template, and use the existing role in the permission candidate menu The menu that has been selected and saved before the role or created template is automatically selected, select the corresponding menu from the permission candidate menu (select the menu that is not selected but needs to be selected, or the menu that is selected but does not need to be selected) to deselect); as in Figure 7As shown, clerk 1 (Zhang San) is the authorized object, and in the permission candidate menu, the menu that has been selected and save...