

Patents
Literature
9341 results about "Third party" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
System and method to notify a person of a traveler's estimated time of arrival
InactiveUS20050114014A1Instruments for road network navigationRoad vehicles traffic controlTime of arrivalThird party
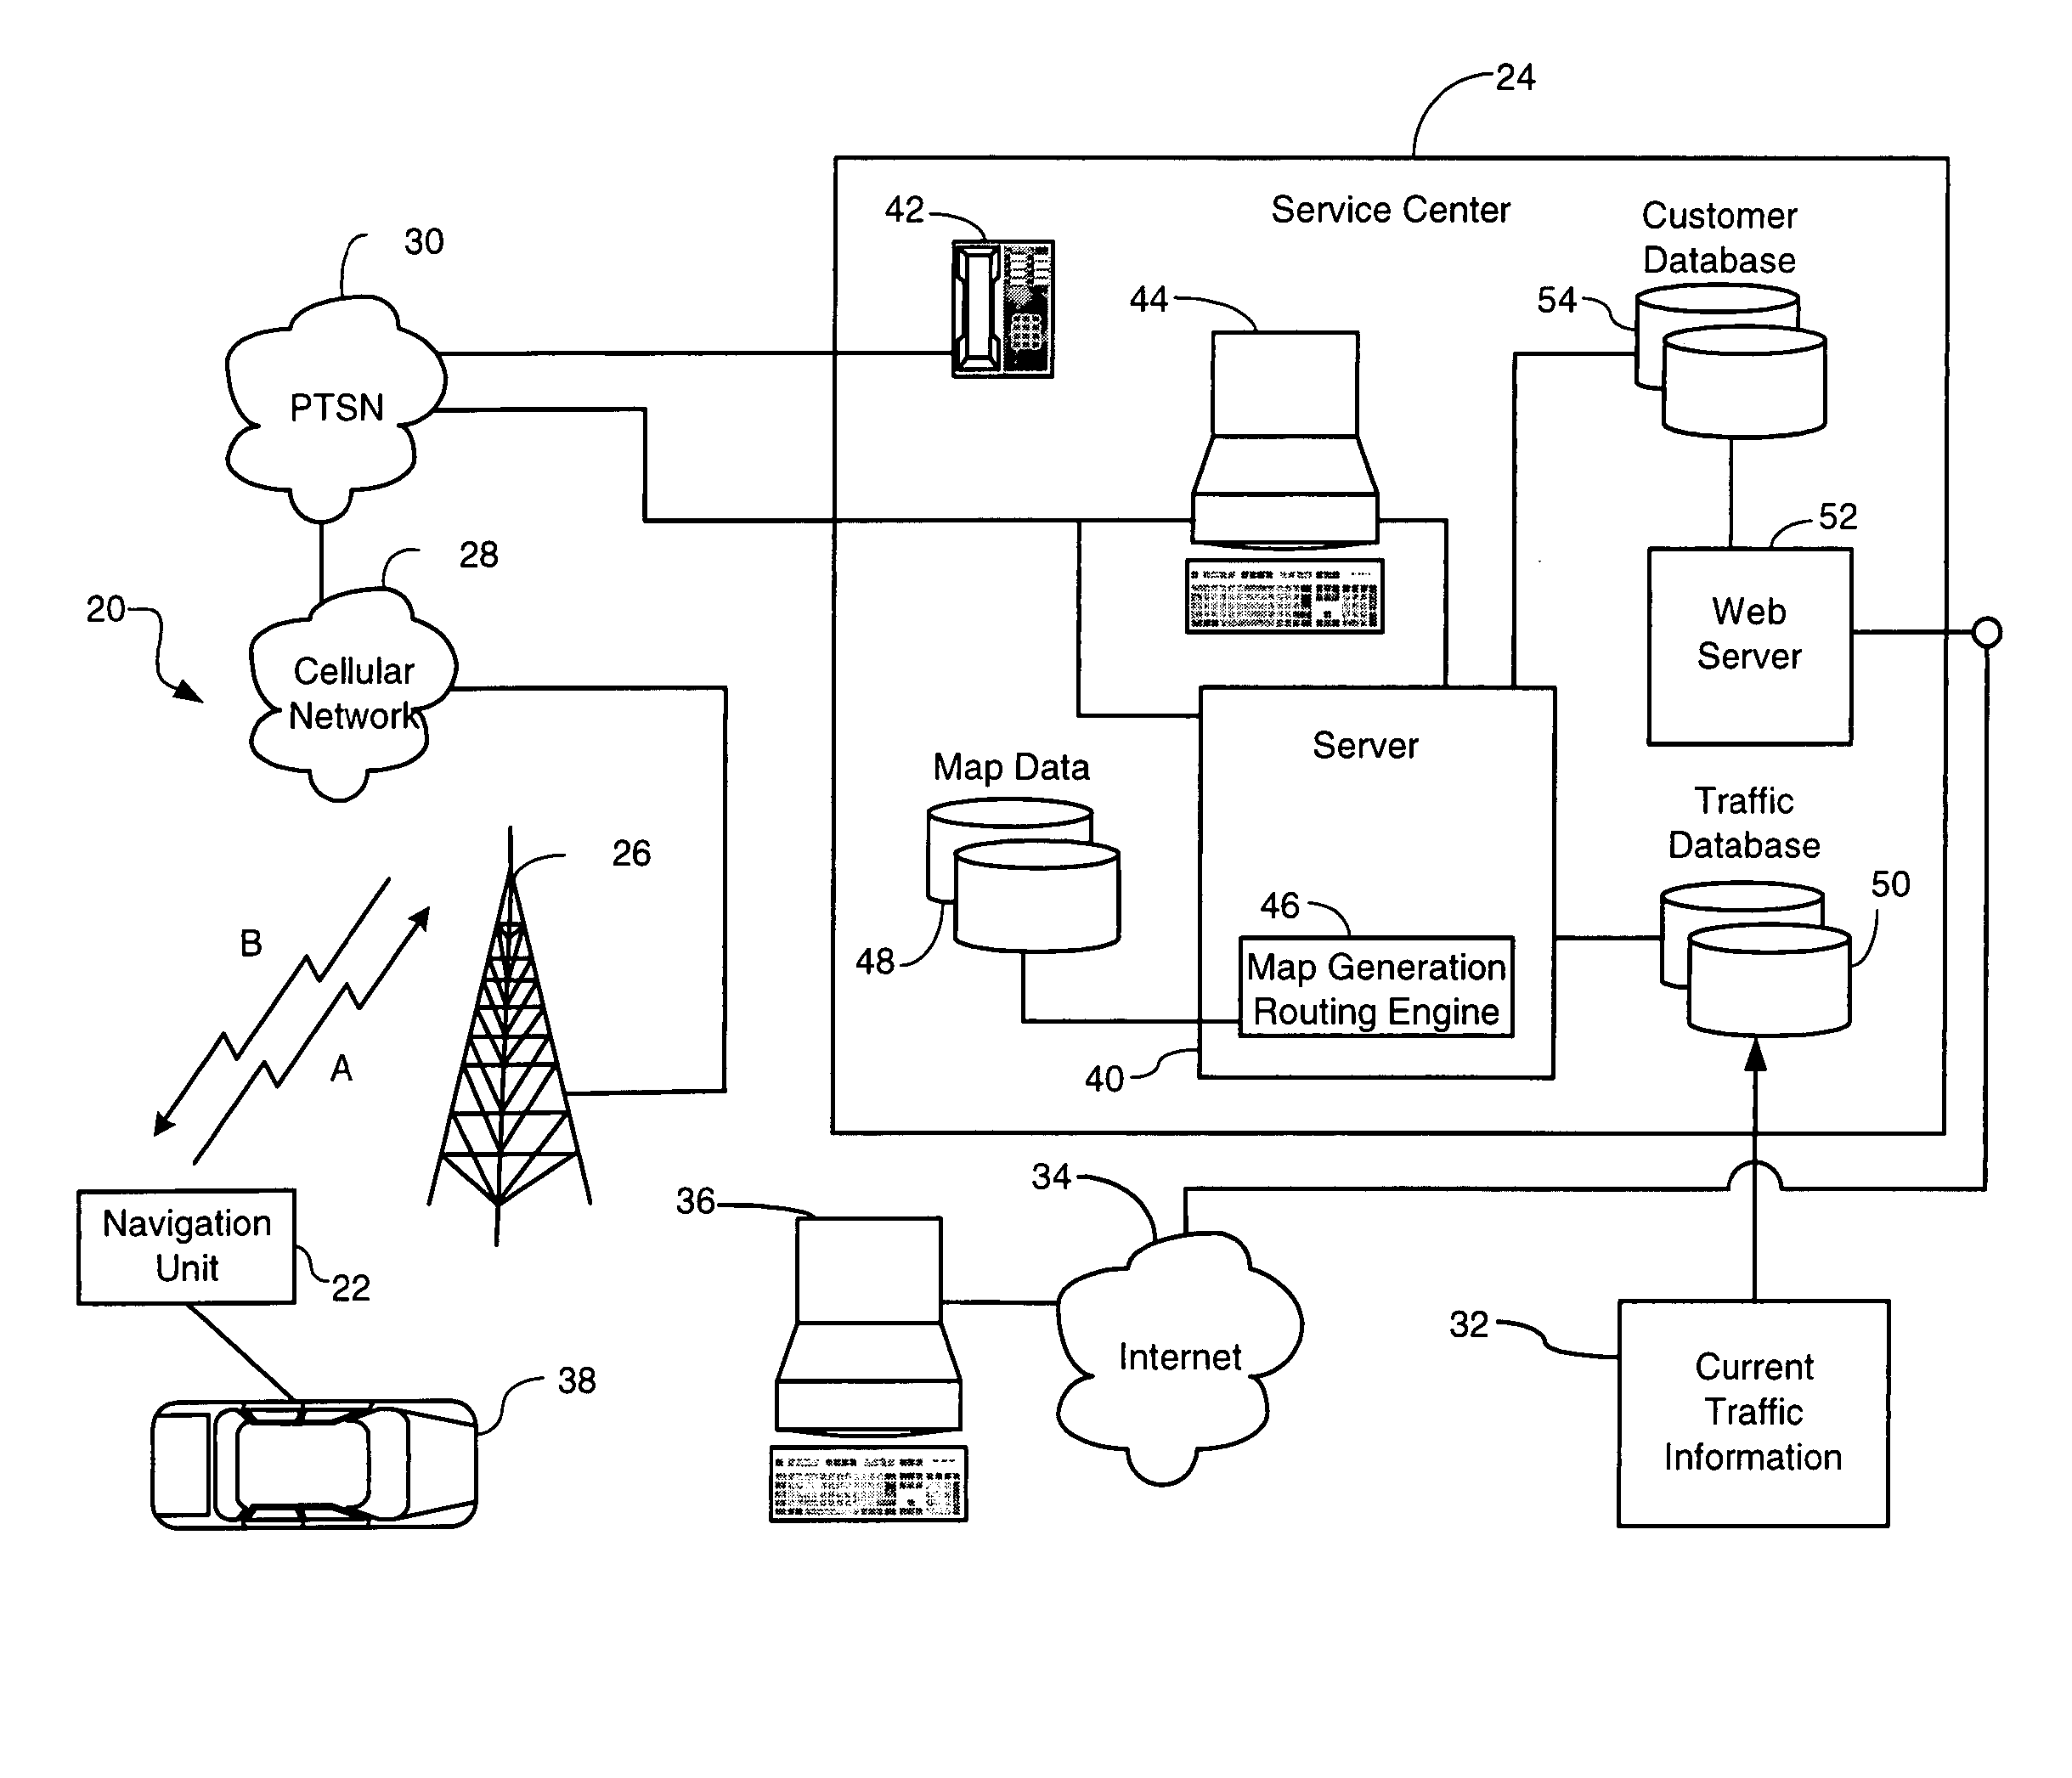
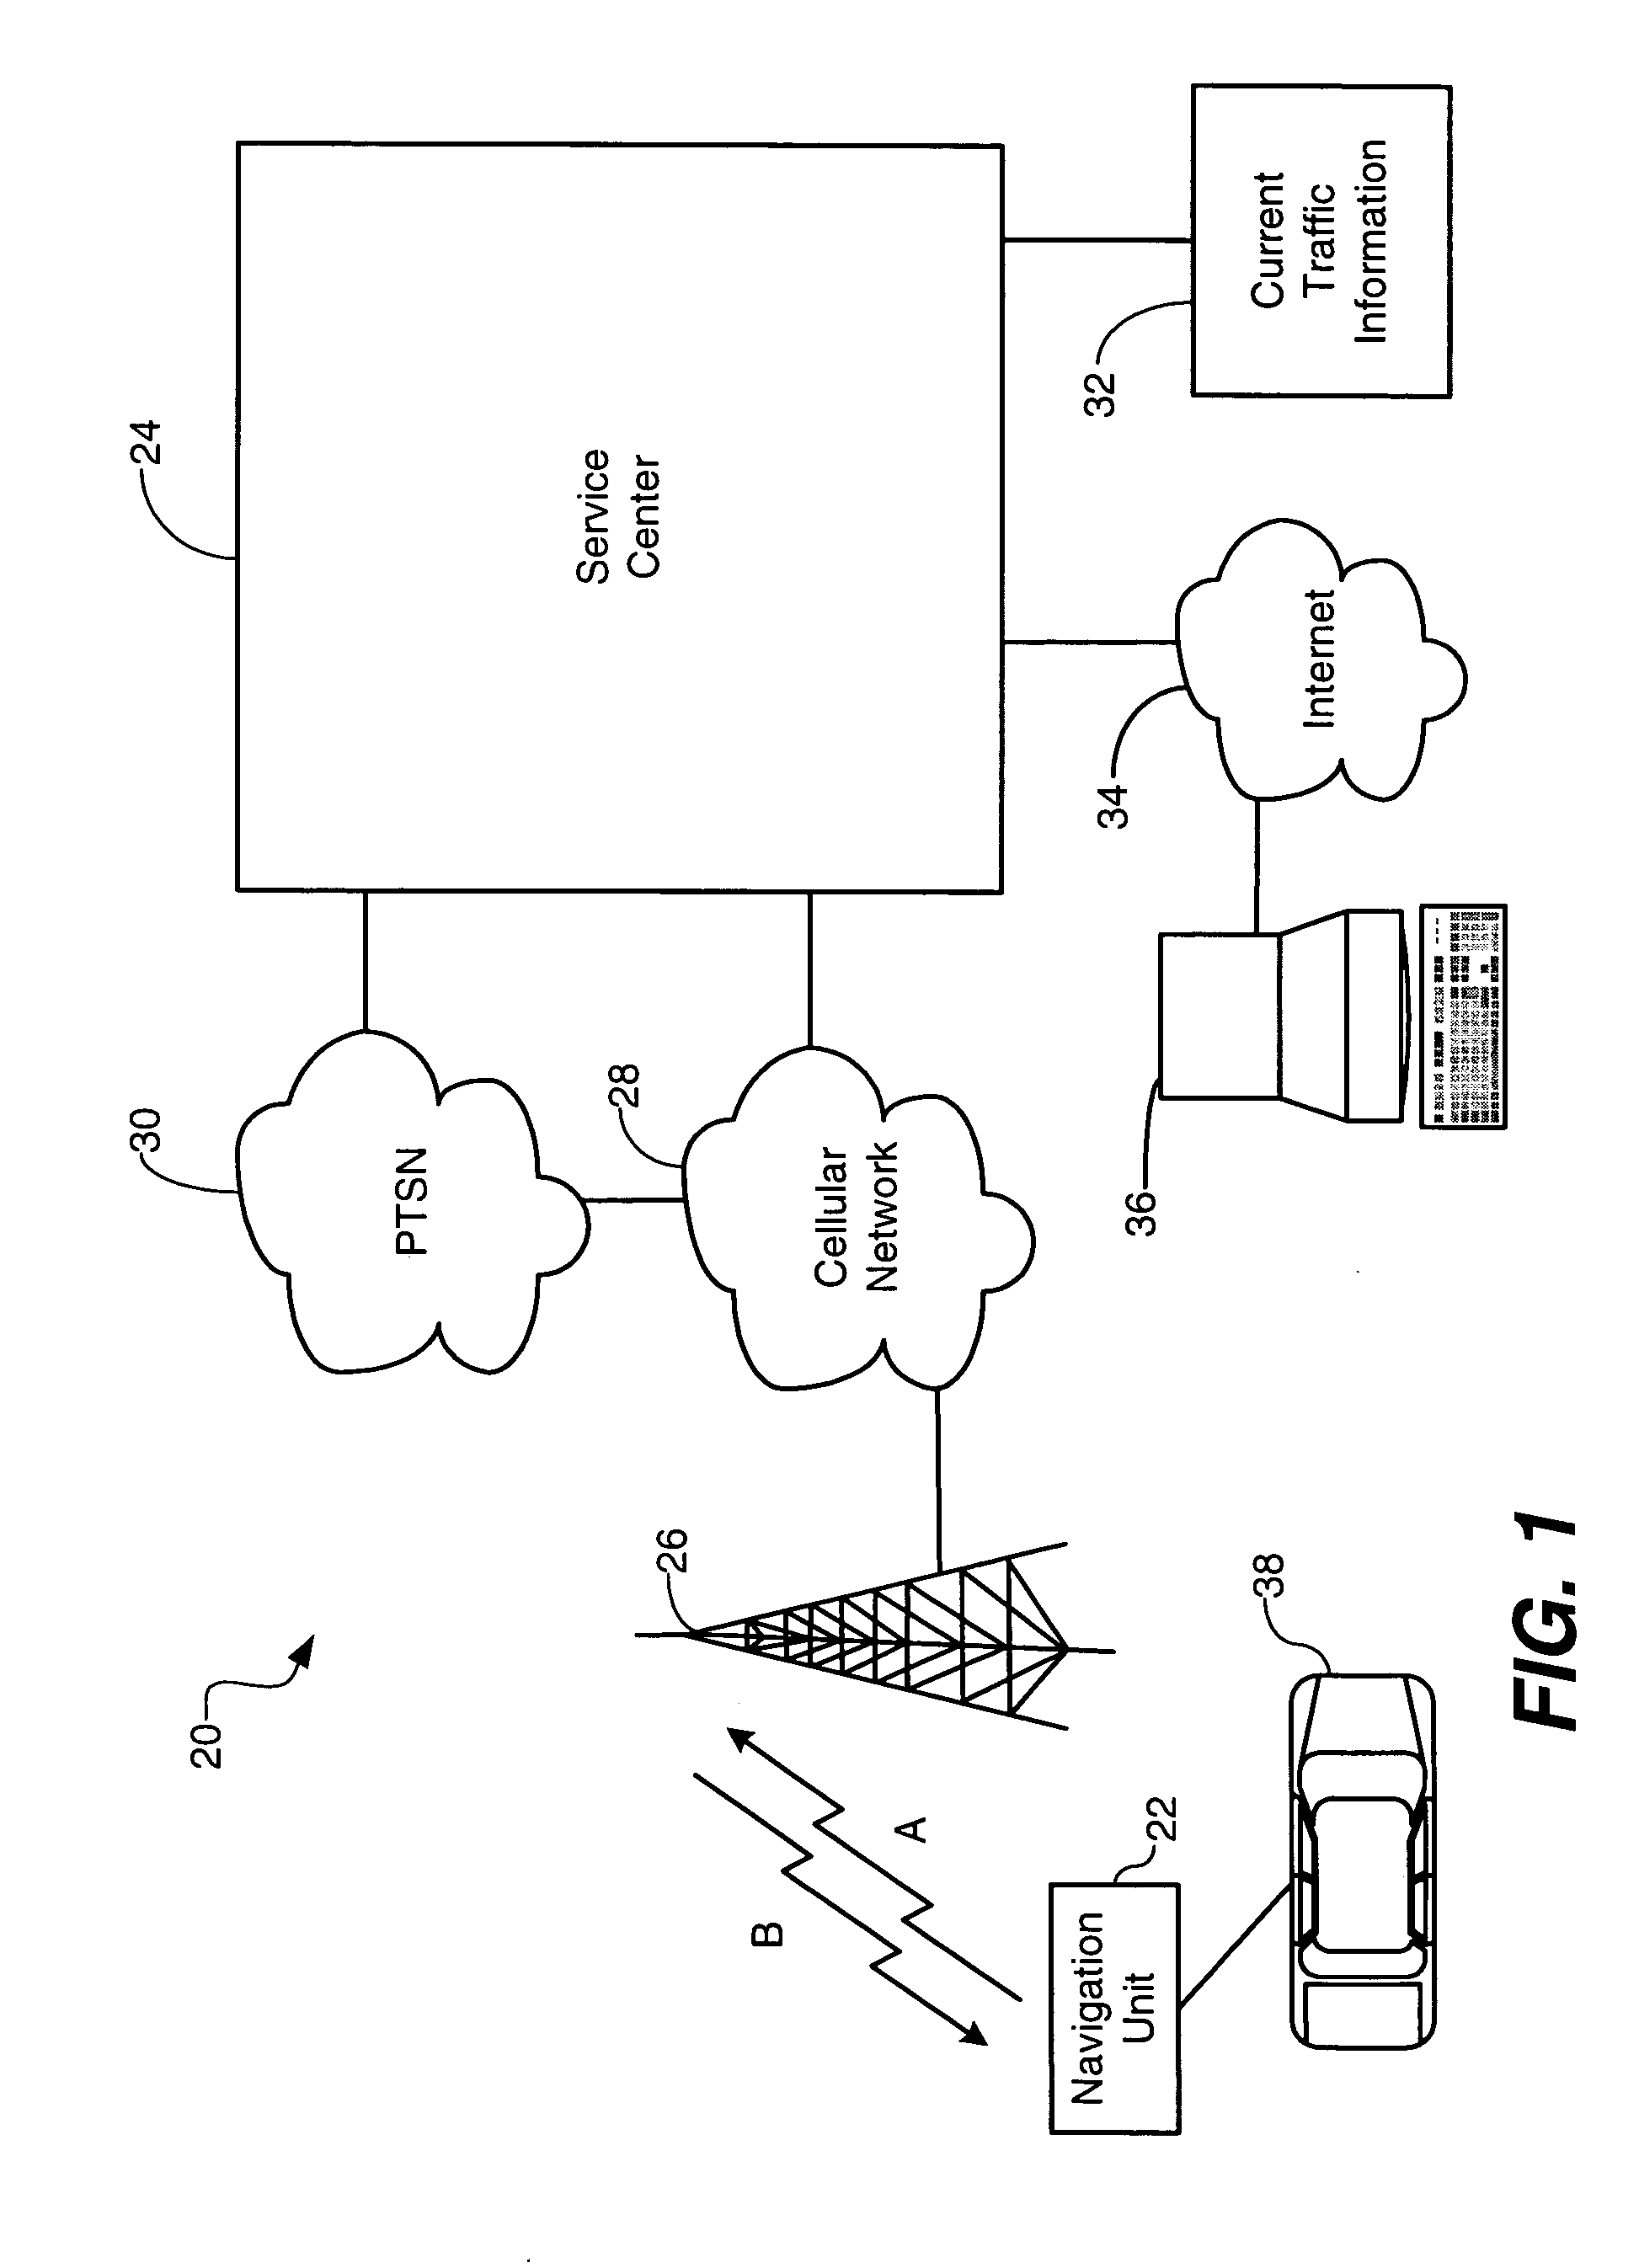
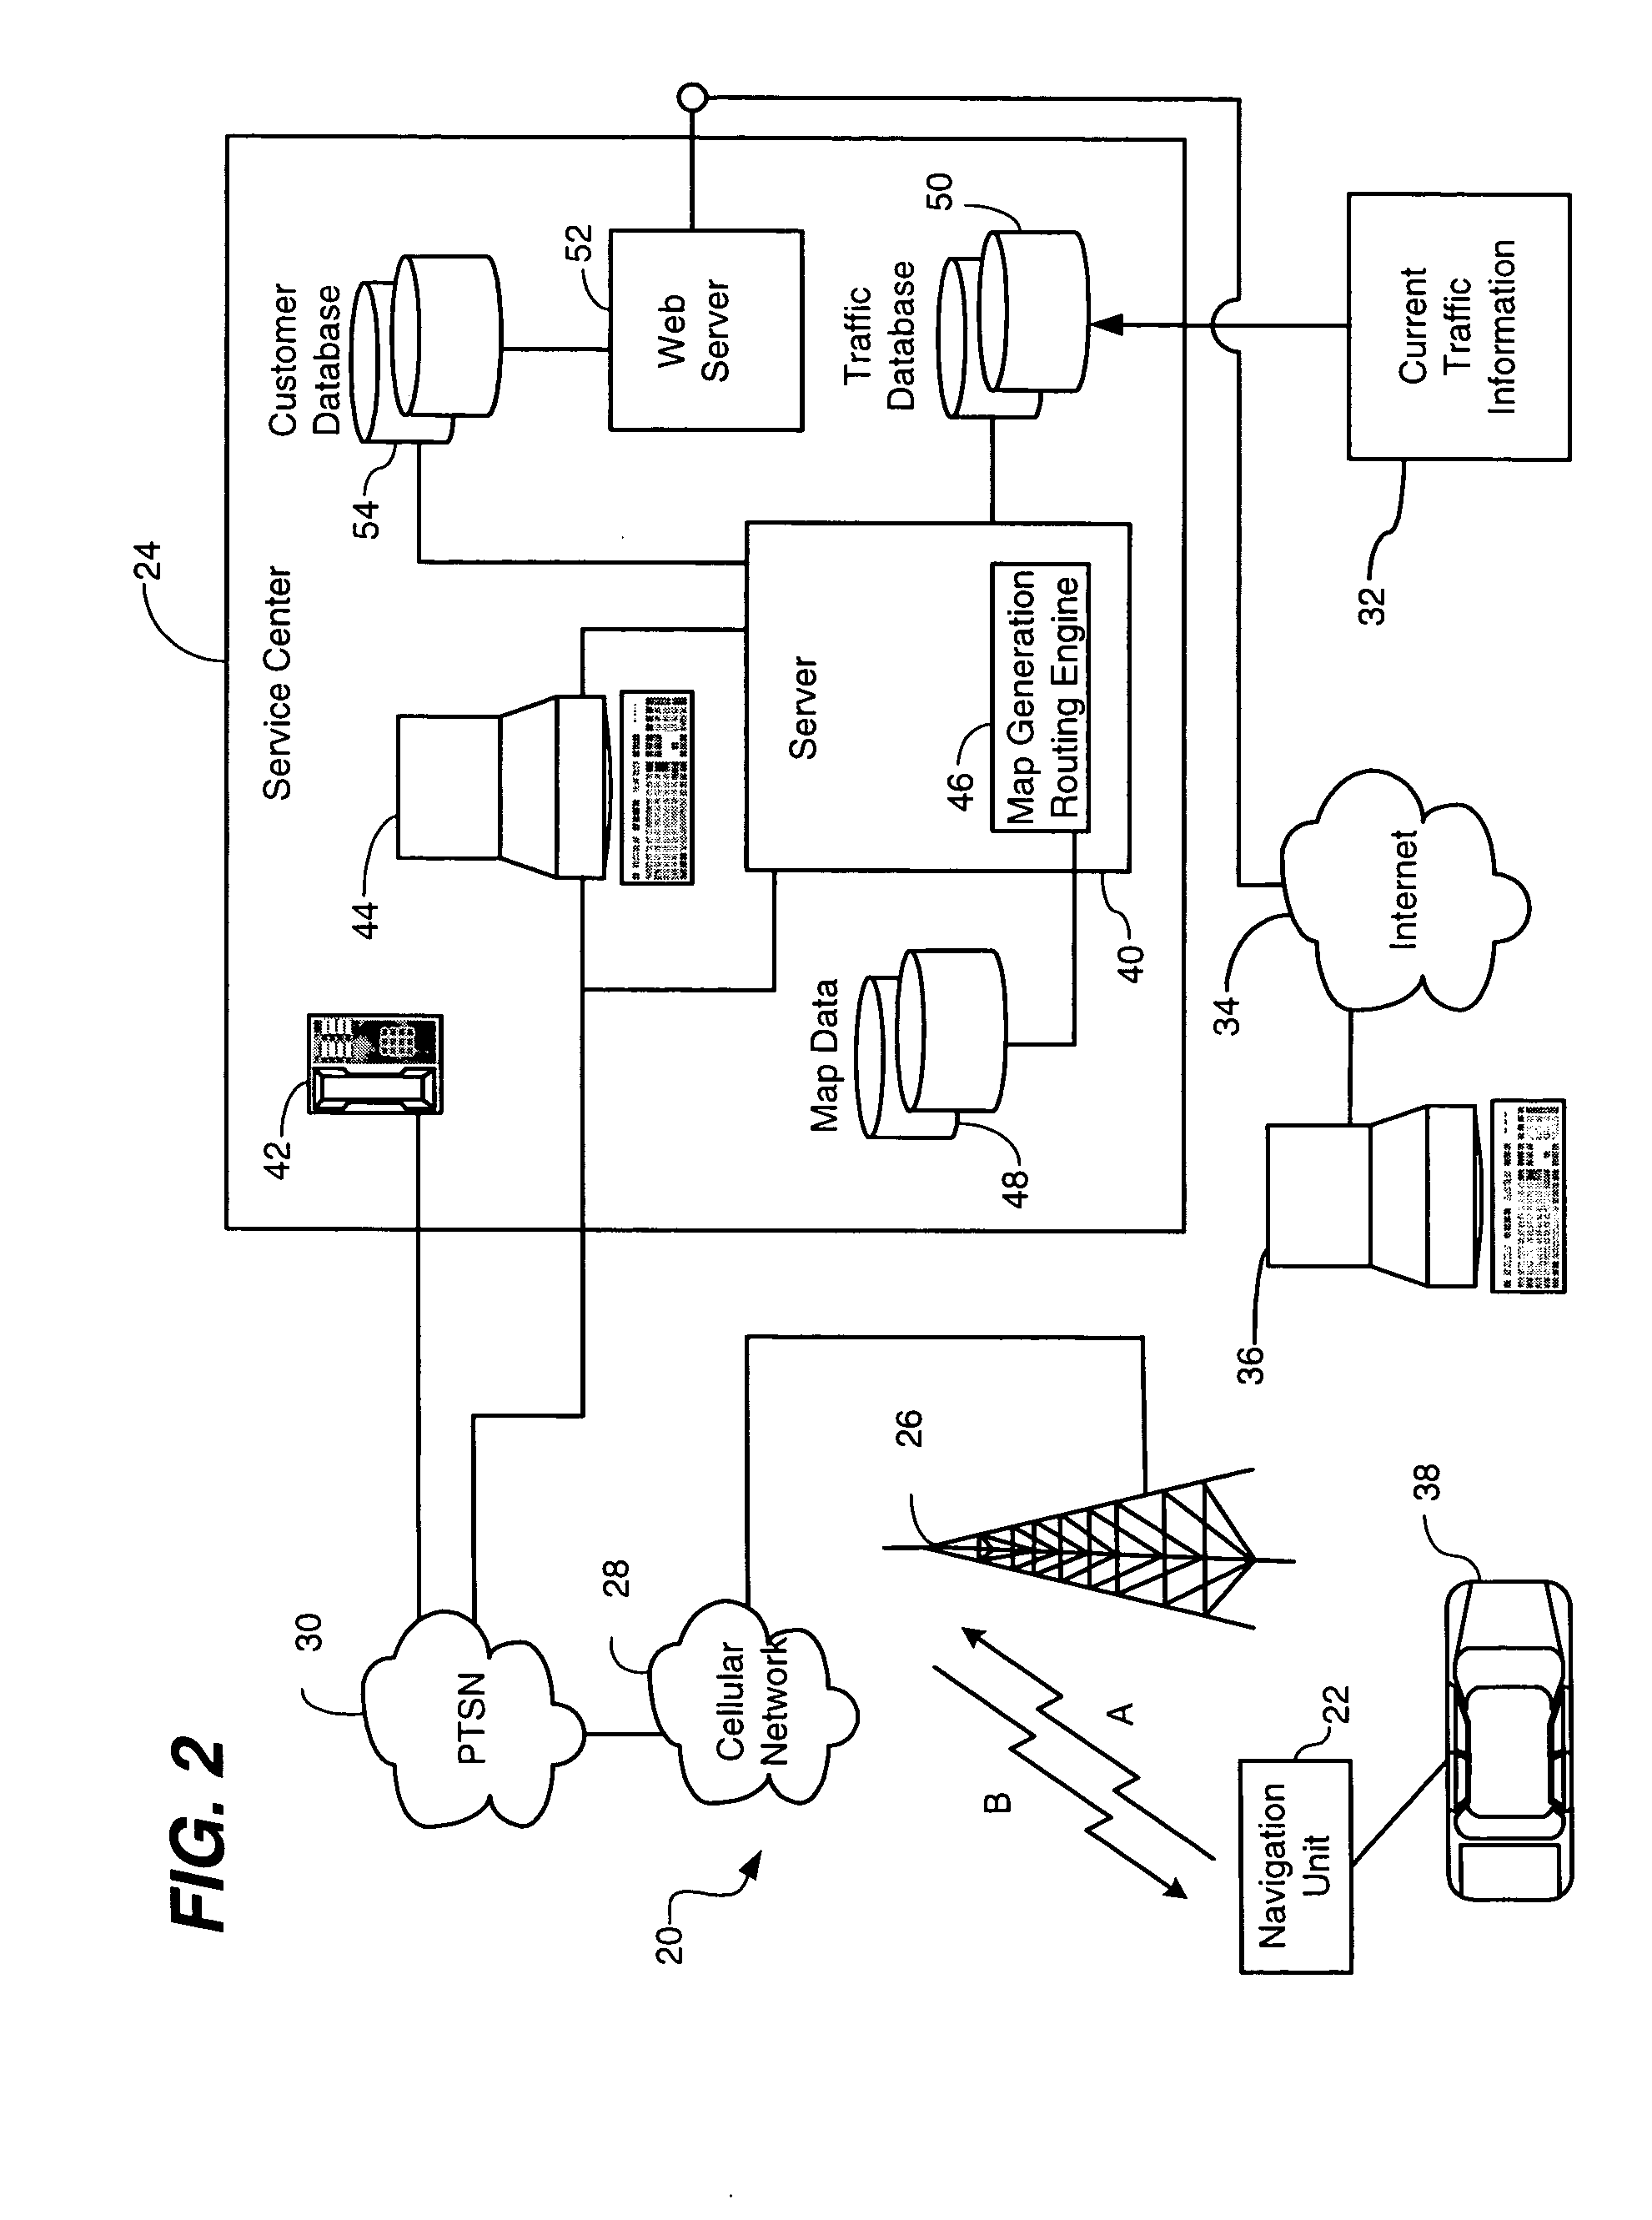
A system and method of calculating an estimated time of arrival for a traveler is provided, along with a notification of this estimated time that is sent to a third party. The traveler is equipped with a navigation unit having a global positioning sensor and a wireless communications device. The navigation unit communicates with a service center equipped with a server capable of generating a preferred navigational route for the traveler. The service center also includes a traffic database for maintaining current traffic information. Once the traveler has selected a predetermined time and frequency of notifications based upon a selected criterion, the navigation unit transmits the traveler's position and velocity to the service center. The service center then calculates the estimated time of arrival based upon the traveler's position, velocity, distance to be traveled and traffic and weather conditions. Once this time is calculated, the service center sends a notification to the third party.
Owner:MOTOROLA INC
Medical data security sharing method and system based on block chain
The invention discloses a medical data security sharing method and system based on a block chain, and relates to the field of data security, and the method comprises the steps: constructing a medical data sharing block chain system; encrypting the medical data of the user by adopting a fully homomorphic encryption algorithm; organizing the encrypted medical data by adopting a Merkle tree structure, encrypting and storing the medical data in the Merkle tree through an IPFS distributed storage system provided by a third-party service node, and storing the root hash of the Merkle tree and the encrypted IPFS address of the medical data as index information of the medical data in a block chain through a medical data uplink smart contract; calling a privacy protection smart contract to verify the identity and authority of the requester by using a zero-knowledge proof method; according to index information of the request data, obtaining corresponding Merkle tree root hash and an encrypted IPFS address of the medical data, and returning the Merkle tree root hash and the encrypted IPFS address to the requester; in view of insufficient privacy protection in a medical data sharing process in the prior art, the security of privacy data is improved.

Owner:TIANJIN ANXUNDA TECHNOLOGY CO LTD
Intelligent operation and maintenance management and control system for information communication network
The invention discloses an intelligent operation and maintenance management and control system for an information communication network, and belongs to the technical field of communication. The system comprises the following modules: an intelligent sensing and data acquisition module which is responsible for real-time acquisition of multi-source network data, dynamic monitoring of cross-domain equipment states and conversion of heterogeneous data into a unified standard; the network intelligent analysis module integrates network performance prediction, fault risk assessment, abnormal behavior identification and security threat monitoring, and provides comprehensive network operation and maintenance insight; the intelligent resource scheduling module is used for realizing dynamic allocation of cross-domain network resources and ensuring efficient and safe utilization of the resources through multi-dimensional optimization and a real-time load balancing strategy; the intelligent decision support module is used for continuously optimizing an operation and maintenance strategy based on machine learning, analyzing a long-term operation trend and providing suggestions for management decisions; and the open integration and collaboration module provides integration of an open API interface and a third-party system, supports cross-domain collaboration management, and improves the flexibility and expansibility of the system.

Owner:东莞市大朗镇政务服务中心
Cross-industry data security sharing method and system based on data desensitization and medium
The invention discloses a cross-industry data security sharing method and system based on data desensitization and a medium, and relates to the related field of privacy computing, and the method comprises the following steps: carrying out dynamic desensitization processing on original data, generating a shared data set for real-time recording, constructing an access behavior characteristic spectrum to configure a dynamic access strategy, and establishing a third-party security data sharing platform, storing the shared data set in a trusted execution environment in a fragmented manner, obtaining fragmented encrypted data, executing a dynamic access strategy, performing conjoint analysis on the fragmented encrypted data through a security multi-party computing protocol, and generating a data security sharing suggestion. The technical problems that in cross-industry data sharing, the privacy leakage risk is high, the static desensitization rule is rigid, and the multi-party calculation efficiency is low are solved, and the technical effects of breaking data islands and constructing safe and mutual-trust data circulation ecology through fusion of dynamic hierarchical desensitization and a trusted execution environment are achieved.


Owner:LINGSHU TECH CO LTD
Systems, devices, and methods for applications for communication with ketone sensors
A software library for providing a uniform framework for various applications or third-party applications access to sensor data. The system further includes a sensor control module and a remote management module. The sensor control module includes logic for communicating with the sensors and receiving sensor data and to communicate that sensor data to the remote management module or various applications. The sensor control module may include a user interface that may display a banner containing numerous components. The content of the banner may differ depending on the host application. The system may further include a host application that incorporates the banner.

Owner:LINGO SENSING TECH UNLIMITED CO
Third-party registration processing method based on IP multimedia subsystem network
InactiveCN101110833AAvoid data inconsistenciesHandle exceptions efficientlyTransmissionRegistration statusThird party
The present invention discloses a third party registration processing method based on the IMS network, which comprises that a UE completes the registration on a S-CSCF entity; the S-CSCF entity starts a waiting timer; the UE and a P-CSCF entity initiate and complete a registration status subscribing respectively to the S-CSCF entity; the S-CSCF entity initiate a third party registration to an AS when the waiting time of the waiting timer is enough. Through the present invention, the S-CSCF entity performs a waiting after the UE is successfully registered, to make the subscribing success of the registration status of the P-CSCF and the UE take precedence over the third party registration and avoid the situation of conflicting data of the UE, the P-CSCF, the S-CSCF and an HSS, to make the UE, the P-CSCF and the S-CSCF effectively process the abnormal circumstance occurred when the third party registration fails.


Owner:ZTE CORP
Systems and methods for verification and validation of cyber resilience
Systems, methods, and computer-readable storage media for compliance verification and validation of cyber resilience in a distributed entity or third-party network (DETPN). Some methods can include generating or identifying, by one or more processing circuits, one or more compliance parameters for a plurality of entities or third-parties on the DETPN. Some methods can include determining, by the one or more processing circuits, at least one compliance level. Some methods can include receiving or identifying, by the one or more processing circuits, environmental data of the DETPN. Some methods can include determining, by the one or more processing circuits at a second timing phase, an updated at least one compliance level for at least one of the plurality of entities or third-parties based at least on the environmental data. In some implementations, some methods can include generating and storing, by the one or more processing circuits, one or more tokens.

Owner:AS0001 INC
Personal loan-lending system and methods thereof
This disclosure relates to a lending system comprising a processor, a memory, and at least one network interface controller configured to enable data exchange with external systems. The memory includes lending management logic configured to execute a personal loan-lending system wherein one or more loans are generated by collecting and preprocessing borrower data from multiple sources, conducting risk assessment and scoring, generating one or more scores based on the conducted risk assessment, and approving loans based on the generated scores. The system leverages machine learning processes to refine scoring accuracy and dynamically adapt to borrower profiles and external conditions. The system may integrate with third-party data sources for enhanced verification and incorporate compliance logic to ensure adherence to regulatory standards. By employing automated, data-driven processes, the system improves efficiency, accuracy, and security in loan origination, servicing, and compliance while enabling dynamic risk management and tailored loan product offerings.

Owner:LOANDEPOT COM LLC
NFT-based sports player scouting records
A subscriber establishes or acquires an NFT token concerning a specific sports player. The subscriber can be a player, a coach, a fan, a sports writer, advertiser, or the like. The player history is updated on the NET token by different data sources. An NFT engine mints NFT tokens and processes and secures transactions. The NFT token can be accessed by a third party to review and use embedded data for player scouting, advertising, promotion and other purposes.

Owner:DATACURVE INC
Software supply chain risk detection protection method and system
The invention provides a software supply chain risk detection protection method and system, and the method comprises the steps: obtaining a third-party component from a software supply chain, and analyzing the multi-level dynamic behaviors of the third-party component; predicting a risk behavior pattern by using a Bayesian network algorithm, and constructing a behavior pattern library; monitoring a behavior of the third-party component during operation, and recording a behavior data stream; identifying an abnormal behavior deviating from a normal behavior mode by applying a time sequence anomaly detection algorithm of deep learning; evaluating risk levels of the abnormal behaviors by using a graph neural network, and generating an abnormal behavior list in combination with relevance and propagation paths among the behaviors; according to the list, a response strategy in the safety control measure library is dynamically adjusted through an adaptive strategy selection algorithm, and safety control measures are formulated for the third-party component. According to the invention, the identification and prediction capabilities of potential risk behaviors are improved.

Owner:HUAQING WEIYANG (BEIJING) TECHNOLOGY CO LTD
Personal data cross-border circulation method based on block chain
ActiveCN120090874AUser identity/authority verificationDigital data protectionData authenticityPrivacy protection
The invention discloses a personal data cross-border circulation method based on a block chain. The method comprises the steps of data acquisition and local storage, third-party neutral institution witness and data fingerprint chaining, data transmission and use authorization declaration, fingerprint verification and data verification on a receiver chain, and full-link tracing and dynamic auditing. Aiming at the problems that trust guarantee of personal data cross-border circulation depends on a single technical means such as centralized institution authentication or encrypted transmission or a static legal protocol, a trust transfer chain is lengthy, and cross-national legal mutual recognition is fragile, a data fingerprint anchoring system constructed based on a block chain is designed; aiming at the problems that traditional data cross-border authorization depends on a manual signing protocol or static strategy configuration, response lag exists, rule execution deviation exists, privacy protection and compliance auditing are difficult to consider and the like, a data use rule is dynamically constrained through an intelligent contract; a user defines a data use range, timeliness and an operation white list through a declarative intelligent contract, and contract codes are automatically executed after being subjected to consensus verification of nodes on a chain.

Owner:National Information Center (National E-Government Extranet Management Center)
Universal AI Based Autonomous Pet Management Platform
The present invention introduces a universal AI-powered pet management platform that establishes an entirely new category of technology, transcending conventional pet training systems. This comprehensive system integrates a modular wearable pet device with interchangeable sensors, sophisticated AI processing capabilities, and diverse output modules to create a unified ecosystem for holistic pet care. Unlike traditional training devices focused solely on behavior modification, this platform simultaneously manages multiple domains including real-time health monitoring, environmental safety assessment, emotional well-being analysis, autonomous training, emergency response, and seamless integration with external systems. The platform's universal architecture enables dynamic adaptation across diverse applications from companion animals to service animals, wildlife monitoring, and specialized deployments. By leveraging advanced artificial intelligence models, multimodal communication pathways, and a universal API for third-party integration, the system creates an interconnected technological framework that fundamentally transforms the relationship between pets, technology, and human interaction, rendering isolated pet devices obsolete.

Owner:TORRES TERRY LEE
Systems and methods for zero-knowledge proof (ZKP) modeling
Systems, methods, and / or computer readable storage media for protecting data. A system can include one or more processing circuits configured to receive or identify at least one token including cyber resilience data of at least one entity and corresponding with at least one posture or compliance parameter of at least one third party The one or more processing circuits can perform a zero-knowledge proof (ZKP) on the cyber resilience data, determine at least one posture or compliance parameter of the at least one third party is satisfied based on the cyber resilience data, and / or generate at least one ZKP including at least one cryptographic commitment obfuscating the cyber resilience data. The one or more processing circuits can provide, to at least one third party computing system of the at least one third party, the at least one ZKP or indication of performance of the at least one ZKP.

Owner:AS0001 INC
Dynamic real time avatar-based ai communication system
A novel avatar-based conversational AI platform that integrates large language models (LLMs) with realistic avatar visualization is disclosed. The platform employs advanced AI technologies to create lifelike avatars capable of personalized and emotionally responsive communication with users. avatar creation tools enable users to generate unique avatar configurations, while animation machine learning subsystems automatically generate the avatar's speech, movements, and emotional responses in real-time. personality machine learning subsystems direct the avatar's voice, personality, and emotions, enhancing the realism of the interaction. The platform supports integration with third-party applications and provides comprehensive deployment and asset management tools. A two-way messaging architecture enables real-time interactions between avatars and users. Authorization and licensing controls protect intellectual property rights, while the avatar's personality dynamically evolves based on user interactions. By integrating LLMs, real-time animation, and emotional intelligence, the platform offers a groundbreaking solution for creating immersive and personalized conversational experiences across various applications.

Owner:SAGEN AI CORP
Attribute-level access control for federated queries
Various embodiments of the present disclosure provide access control for data provided by a federated query system based on attributes of a federated query. The techniques include determining a user identifier associated with a federated query, determining a set of access controls for a plurality of third-party data sources based on the user identifier, and generating an execution plan for resolving the federated query via one or more executable tasks with respect to the plurality of third-party data sources. The techniques also include generating, using a first portion of the execution plan, a result set that comprises information aggregated from the plurality of third-party data sources in accordance with the federated query. The techniques also include generating, using a second portion of the execution plan, a user result set that masks a portion of the information for the result set in accordance with the set of access controls.

Owner:OPTUM INC
Multi-node carbon emission intelligent contract verification method based on block chain
ActiveCN120238313AKey distribution for secure communicationUser identity/authority verificationNode clusteringSource Data Verification
The invention relates to the technical field of data processing, provides a multi-node carbon emission intelligent contract verification method based on a block chain, and aims to solve the problems that data verification in an existing carbon asset transaction system is non-transparent, high in trust cost and difficult to adapt to policy changes. Distributed storage and dynamic verification of data are realized by constructing a hierarchical block chain architecture, the data are collected by using edge computing nodes, and third-party verification data are obtained through an oracle machine node cluster. The dynamic rule engine monitors data changes in real time, triggers a multi-stage verification process, and improves the data accuracy. And meanwhile, an improved Byzantine fault-tolerant mechanism is adopted to reach a consensus, and the system has the functions of strategy dynamic updating and security enhancement, so that the flexibility and security of the system are improved. According to the method, multi-party consensus and real-time verification of the carbon emission data are realized, trust cost of cooperation among enterprises is reduced, and healthy development of a carbon emission permit trading market is promoted.

Owner:LONGYUAN (BEIJING) CARBON ASSET MANAGEMENT TECH CO LTD
Methods and systems for facilitating collection of road user charges using a digital currency based on a distributed ledger technology
PendingUS20250378436A1Transportation facility accessCryptography processingDigital currencyThird party
A system and method for facilitating collection of Road User Charges (RUC) using a digital currency within a Distributed Ledger Technology (DLT) network are disclosed. The system generates secure digital wallets for Road Users and Facility Owners, receives trip, position, distance, and cost data from vehicles, sensors, and facility systems, and encodes settlement logic into smart contracts. These contracts automatically execute jurisdiction-specific disbursements across blockchain, directed acyclic graph (DAG), or hashgraph frameworks, ensuring scalability and auditability without reliance on centralized tolling infrastructure. An AI Activity Module processes multi-source telemetry—including vehicle sensors, GNSS / PNT data, roadside infrastructure, and third-party traffic feeds—to detect congestion, forecast conditions, optimize routing, and dynamically adjust segment-level RUC pricing in real time. The integration of AI-driven adaptive pricing with distributed ledger settlement provides a decentralized, infrastructure-agnostic framework for secure, transparent, and verifiable road use fee collection across multiple jurisdictions, distinct from conventional tolling systems.

Owner:LOCHRANE TAYLOR WILLIAM PAUL
Communication network security situation prediction method and system based on big data
The invention relates to the technical field of digital information transmission, and provides a communication network security situation prediction method and system based on big data, which break through the limitation of single data in the aspect of data fusion, integrate four large classes and 12 subclasses of multi-source heterogeneous data, and combine a dynamic weighting mechanism to make feature extraction more comprehensive and accurate; on the aspect of model architecture, CNN-Bi-LSTM-Attention three-level fusion and PSO optimization are adopted, spatial and temporal features are effectively captured, the convergence speed is increased, the prediction accuracy is high, and the false alarm rate is low; in the risk assessment aspect, a layered assessment system is constructed, and early warning is realized in combination with a dynamic threshold value and Monte Carlo simulation; the model training module innovatively adopts a federated learning mode, and the model generalization ability is improved while data privacy is guaranteed; the prediction analysis module deploys an optimization hybrid model, supports high-concurrency prediction and is short in response time; the visual decision-making module provides three-dimensional visualization and geographical drilling functions, and output data can be seamlessly connected with a third-party platform.

Owner:XINJIANG RUISHU YUNDING INFORMATION TECH CO LTD
Compensation for a service associated with a humanoid robot with advanced kinematics
Various systems and methods are described for obtaining compensation for tasks performed by a humanoid robot, where the humanoid robot is associated with a first party. The method includes a first party providing a humanoid robot for use in an operating location. The humanoid robot engaged in performing a plurality of tasks at the operating location. A third party compensates the first party with a specified amount of currency for a pre-determined time interval during which said humanoid robot has engaged in performing the plurality of tasks at the operating location.


Owner:FIGURE AI INC
Text classification method, device and system based on large language model, storage medium and product
ActiveCN119647408AStrong text comprehension skillslow costNatural language data processingThird partyText categorization
The invention discloses a text classification method, device and system based on a large language model, a storage medium and a product, and relates to the technical field of text classification, the method comprises the following steps: receiving a to-be-classified text and a classification label input or selected by a user through a user interaction interface of the text classification system; and according to the to-be-classified text and the classification label, constructing prompt words, and calling a pre-trained large language model to perform different-level classification on the to-be-classified text to generate a classification result. According to the technical scheme, the low-cost and low-use-threshold text classification method is provided based on the large language model, classification of different levels can be achieved, in addition, due to the fact that the text classification result is in a light-weight and convenient-to-analyze JSON format, the system can visually display the classification result to a user and can also provide an interface for a third-party application to call, and the user experience is improved. And the application scene of text classification is expanded.

Owner:CHINA MERCHANTS BANK
Federal learning system based on multi-key homomorphic encryption and adaptive differential privacy
PendingCN120811569AKey distribution for secure communicationMultiple keys/algorithms usagePrivacy protectionKey generation
The invention relates to a federated learning system based on multi-key homomorphic encryption and adaptive differential privacy, and belongs to the technical field of privacy computing. According to the system, on the premise that no trusted third party exists, a multi-client collaborative key generation and threshold decryption mechanism is achieved, it is ensured that model parameters are always in an encrypted state in the aggregation process, and leakage of a single node is prevented. By introducing a parameter sensitivity analysis and selective encryption strategy, the system only encrypts high-risk parameters, and the encryption burden is effectively reduced. Meanwhile, in combination with an adaptive privacy budget allocation mechanism, the system dynamically adjusts noise intensity according to a model training state, and model performance and convergence speed are maintained while privacy protection capability is improved. According to the method, high robustness and collusion resistance are realized, stable operation under the condition that part of clients are offline is supported, and the method is suitable for application scenes such as medical treatment and finance with high data sensitivity and strict performance requirements.

Owner:FUZHOU UNIV
Scenic area passenger flow trend prediction analysis method based on AI big language model
ActiveCN119398214ACollaborative workunderstand intuitiveForecastingMachine learningEngineeringTrend prediction
The invention belongs to the technical field of artificial intelligence and big data analysis, and particularly relates to a scenic spot passenger flow trend prediction analysis method based on an AI big language model. According to the method, big data and artificial intelligence technologies are utilized, LBS data, scenic spot data, holiday and festival information, third-party maps, weather data and other multi-source data are comprehensively applied, a comprehensive multi-dimensional knowledge base is constructed, and meanwhile, the knowledge search and generation capability is improved by utilizing an RAG technology; through model pre-training and fine tuning, the universal model capability is developed, and a multi-agent system is further constructed; based on the natural language processing capability of the AI large language model, the LLM can intelligently analyze the text input of the scenic region administrator, drive the cooperative work among multiple agents, and achieve the intelligent prediction and analysis of the scenic region passenger flow trend. The method can more accurately predict the passenger flow trend of the scenic area.

Owner:GUANGZHOU HANTELE COMM CO LTD
Misconfiguration Detection and Prevention in a Data Fabric
PendingUS20250373647A1Computer security arrangementsSecuring communicationData streamSoftware engineering
The present disclosure describes systems and methods for detecting and preventing data misconfigurations within a security-focused data fabric platform. The system integrates an advanced script migration engine designed to streamline the translation of security rules and scripts across different scripting languages while ensuring alignment with the fabric's unified schema. The method involves receiving inputs from data sources, mapping these inputs to entities of a target schema, monitoring real-time data changes, and simulating impacts on operational dependencies to detect misconfigurations proactively. Leveraging AI-driven mechanisms, including Large Language Models (LLMs), the system dynamically identifies breaking changes in third-party data streams, issues alerts, and provides suggested fixes. The script migration engine further enhances the platform's functionality by automating cross-platform script translations and enabling faster onboarding of security tools. Together, these innovations ensure scalable, accurate, and resilient integration and management of security data across heterogeneous sources, strengthening operational integrity and minimizing security risks.

Owner:AVALOR TECH LTD
Method for constructing feature knowledge base of mapping behavior based on deep learning
The disclosure belongs to the technical field of network security, and provides a method for constructing a feature knowledge base of mapping behavior based on deep learning, which includes: data acquisition and preprocessing: extracting five-tuple information and behavior features from network traffic. The disclosure automatically extracts the spatio-temporal features through the deep learning model, and enhances the sensitivity to abnormal behaviors by combining the attention mechanism, thus significantly improving the detection accuracy. The explanatory AI technology is used to automatically generate detection rules, the maintenance cost of manual rules is greatly reduced and the efficiency of rule generation is significantly improved. The feature knowledge base supports dynamic updating, may integrate third-party threat information in real time, and ensures the continuous defense ability against new attacks and variant detection means.

Owner:HUANENG INFORMATION TECH CO LTD
Automatic contract text auditing method and system based on term unified modeling
ActiveCN119476938Ahigh transparencyAchieve traceabilityFinanceNatural language data processingThird partyRisk Control
The invention discloses an automatic contract text auditing method and system based on clause unified modeling, and belongs to the technical field of contract auditing, and the auditing method comprises the following specific steps: I, accessing a third-party credit investigation mechanism or a credit rating platform to extract the credit information of both parties of a contract, and carrying out the credit investigation and auditing of the both parties of the contract; iI, establishing an initial contract template classified according to economic businesses, and extracting contract key information through an NLP technology; the optimal rule can be quickly identified and selected in a large number of detection rules, the auditing efficiency is remarkably improved, the time required by manual intervention is shortened, the auditing process is more flexible, the method can adapt to specific requirements of different contracts, potential risks in the contracts can be comprehensively identified, auditing personnel can be helped to find high-risk terms in time, and the contract auditing efficiency is improved. The law risk in contract fulfillment is reduced, the benefits of colleges and universities are protected, more stable risk control and compliance guarantee are provided for the colleges and universities, the contract fulfillment condition is monitored through integration with an accounting system, the compliance and the executive force of the contract are ensured, and the transparency and the traceability of contract management are improved.

Owner:HEFEI UNIV OF TECH
System and method for source code transformation
There is disclosed herein a method of providing protected access to a third-party generative artificial intelligence (GAI) for software development including transforming a source code input (a transformed source code) via a one-way transform, wherein an enterprise has a proprietary interest in the source code input, and wherein the one-way transform is not internally reversible; providing the transformed source code to the third-party GAI, in association with a query for the third-party GAI, wherein the third-party GAI is controlled by a party other than the enterprise; receiving from the third-party GAI a response to the query; and presenting the response to a human user via a human interface device (HID).

Owner:MCAFEE LLC
Spatio-temporal key encryption for authentication and encryption of communication and information systems
ActiveEP4485843A1Key distribution for secure communicationMultiple keys/algorithms usageThird partyThreat level
A third-party authentication and encryption method, known as spatio-temporal encryption, is used to protect sensitive information by guaranteeing the origin and integrity of its content for recording or transmission purposes. This method is based on hidden characteristics associated with the message's location and creation date, derived from GNSS signal processing. Without requiring additional dedicated security infrastructure, the method allows for the protection and authentication of any data entered into the information system, anytime and anywhere, and enables the assessment of associated security risks at any system level. Leveraging the various levels of access protection for GNSS signal services, the solution offers different levels of robustness, with complexity and security that can be tailored to the threat level, while minimizing the impact on communication network performance.

Owner:TILT-GNSS SAS
Systems and methods for secure digital identity verification and access to disparate data sources
PendingUS20240427868A1Interprogram communicationDigital data authenticationDigital identityThird party
The present disclosure provides a method for secure verification of identities. The method includes obtaining personal identifying information from an individual using a remote device and transmitting the information to an application service. The application service accesses multiple disparate data sources via an API, including public entity data sources, third party data sources, and services sources. The API normalizes data received from the disparate data sources. The personal identifying information is verified against the normalized data. Biometric identifying information is obtained from the individual using the remote device and transmitted to the application service. The biometric identifying information is compared with normalized biometric data from the disparate data sources. Based on the comparison, a determination is made whether to issue a digital identification credential to the individual. An authentication result is transmitted to the remote device.

Owner:COLORADO DEPARTMENT OF LAW
Identifying unauthorized entities from network traffic
Systems, methods, and devices to detect unauthorized third-party connections within a network infrastructure, such as by analyzing network traffic data using fuzzy matching and machine learning techniques. One aspect includes receiving network traffic data comprising records of communication events involving network identifiers, determining communication relationships between network entities identified by the network identifiers, accessing entity identifiers associated with known third-party systems, and determining associations between the network identifiers and the entity identifiers using a fuzzy matching process. Other aspects include identifying communication relationships involving the third-party systems based on the associations and detecting unregistered or unknown third-party connections within the network infrastructure. Further aspects include normalizing identifiers, computing string similarity metrics, assigning confidence scores, incorporating external data sources, building network association patterns, comparing current patterns to baseline patterns to detect anomalies, and updating security policies or firewall rules in response to detected anomalies. Additional aspects are provided.

Owner:HSBC GRP MANAGEMENT SERVICES LTD
Commercial and trade circulation supply chain optimization method based on multi-modal data fusion
The invention discloses a commerce and trade circulation supply chain optimization method based on multi-modal data fusion, and the method comprises the following steps: 1, multi-modal data collection: collecting the multi-modal data of the whole supply chain in real time through an Internet of Things device, an enterprise ERP system, a logistics tracking system and a third-party platform, the multi-modal data comprises text data, image data, voice data, time sequence data and spatial data. When the scheme is implemented, multi-source heterogeneous data of the Internet of Things, ERP and the like are integrated, so that the problem of an information island in a traditional supply chain is effectively solved; position coding and a cross-modal attention mechanism are introduced into the multi-modal fusion model, so that the data alignment precision is remarkably improved, for example, when'emergency order adding 'in a voice communication record is associated with a corresponding order image, the weight distribution accuracy is improved; the application of the block chain technology ensures the transparency and traceability of the supply chain decision.

Owner:BEIJING HAIZHIYAN ADVERTISEMENT CO LTD