

Cloud protection method and device based on tunnel mode
A tunnel mode and tunnel technology, applied in the field of network security, can solve problems such as increased operation and maintenance costs, complicated access, and inability to use high-defense Alibaba Cloud high-defense services for Windows servers outside the cloud, so as to reduce operation and maintenance costs and access way simple effect
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2018-05-04
Smart Images
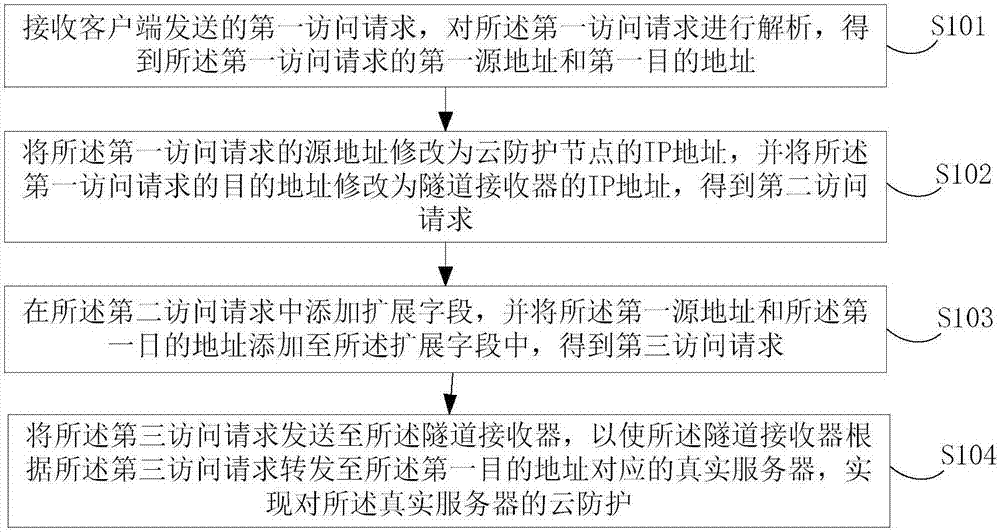
Figure 1 
Figure 2 
Figure 3
Abstract
Description
technical field
[0001] The embodiments of the present invention relate to the technical field of network security, and in particular to a tunnel mode-based cloud protection method and device. Background technique
[0002] Anti-DDoS Pro cloud protection service needs to resolve the domain name to Anti-DDoS Pro IP (for web services, the domain name resolution points to Anti-Defense IP, and for non-web services, the business IP is replaced with Anti-Defense IP), and at the same time, forwarding rules are set on Anti-DDoS Pro IP. All public network traffic will first pass through the high-defense cleaning cloud node, and the access traffic will be forwarded to the source station IP through the high-defense IP through port protocol forwarding. Return to the IP of the source site, so as to ensure the protection service of stable access to the IP of the source site.
[0003] In the existing technology of Alibaba Cloud Anti-Defense, if the host outside the cloud wants to use the An...
Examples
Embodiment Construction
[0039] The specific embodiments of the present invention will be further described below in conjunction with the accompanying drawings. The following examples are only used to illustrate the technical solution of the present invention more clearly, but not to limit the protection scope of the present invention.
[0040] figure 1 It shows a schematic flowchart of a tunnel mode-based cloud protection method provided in this embodiment, including:
[0041] S101. Receive a first access request sent by a client, parse the first access request, and obtain a first source address and a first destination address of the first access request.
[0042] Wherein, the first access request is a request that the client expects to send to the real server to access data of the real server.
[0043] The first source address is the IP address of the client, and the first destination address is the IP address of the real server.
[0044] Specifically, the cloud protection node receives the first...