
Network safety log template extraction method and device
A network security and log technology, applied in the field of information security, can solve the problems that analysts are difficult to extract log templates, log format changes, etc., achieve high accuracy, reduce system load, and improve computing efficiency
Patent Information
- Authority / Receiving Office
- CN · China
- Current Assignee / Owner
- Publication Date
- 2015-11-11
Smart Images
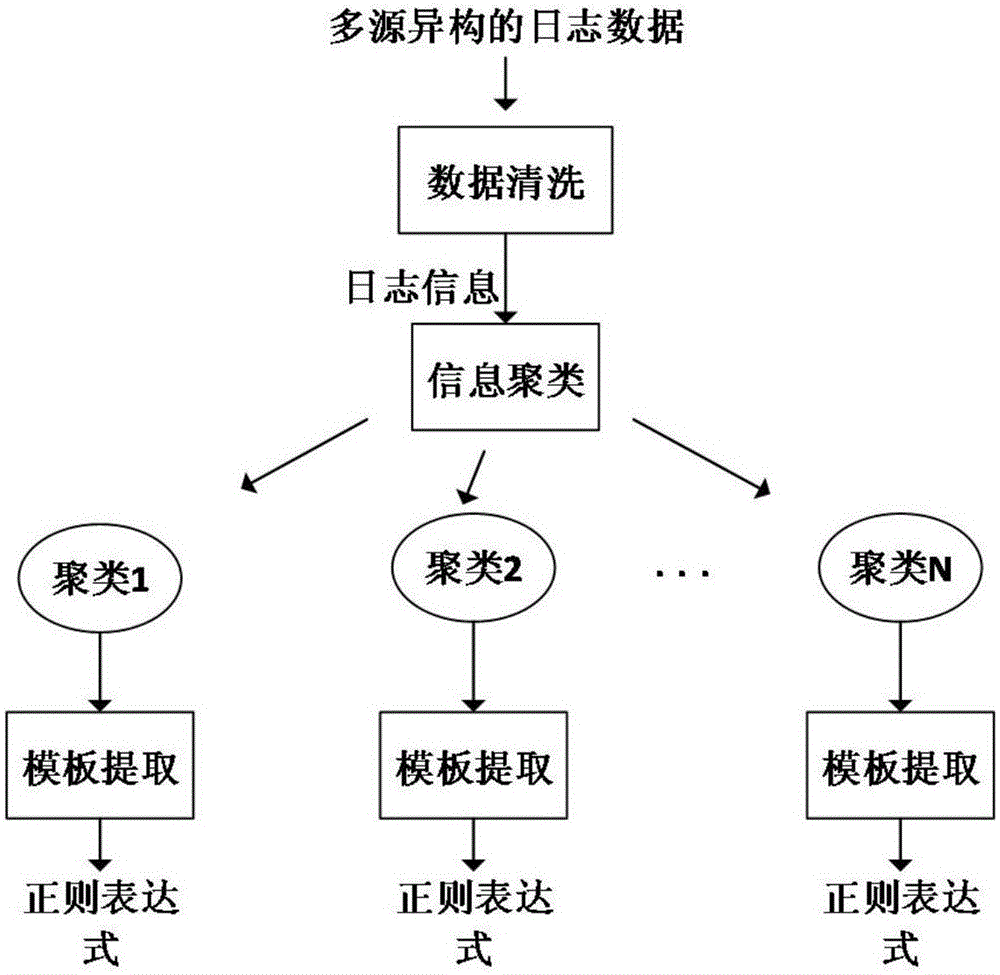
Figure 1 
Figure 2 
Figure 3
Abstract
Description
technical field
[0001] The invention relates to the field of information security, in particular to a method and device for extracting a network security log template. The solution does not depend on any prior knowledge and can automatically extract a template describing an unknown network security log format. Background technique
[0002] Network security logs, including system logs generated by the operating system and alarm logs generated by network security devices, record various security events in the network environment and provide important clues for network abnormal diagnosis and network attack threat discovery. In the network security log analysis system, log format parsing is an essential step. Therefore, extracting network security log templates is of great significance for log analysis. At present, in some relatively mature network security log analysis products, such as OSSIM, Snort, OSSEC, etc., log parsing methods based on regular expressions are usually col...
Examples
Embodiment Construction
[0032] In order to make the above objects, features and advantages of the present invention more obvious and understandable, the present invention will be further described below through specific embodiments and accompanying drawings.
[0033] The network security log template extraction method provided by the present invention, its main steps include data cleaning, information clustering and template extraction, such as figure 1 shown. Among them, data cleaning is to first filter the fields with specific formats in the log data, including date, IP address, etc.; information clustering is to use clustering algorithm to divide the logs with similar formats into one category after cleaning. Medium; template extraction is to extract the template words describing the format in the log for each log in the class, and only keep the template words in the original log to obtain the log format.
[0034] 1. Data cleaning
[0035] The data cleaning in this method is mainly to filter out...