
A WeChat forensics method and system based on data collision
A technology of data collision and WeChat, applied in the direction of digital transmission system, transmission system, digital data protection, etc., can solve the problems of unrecognizable, unable to obtain and analyze UID, unable to analyze and collect evidence of WeChat data, etc., to achieve high security and convenient decryption Effect
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Patents(China)
- Current Assignee / Owner
- Publication Date
- 2020-05-19
Smart Images
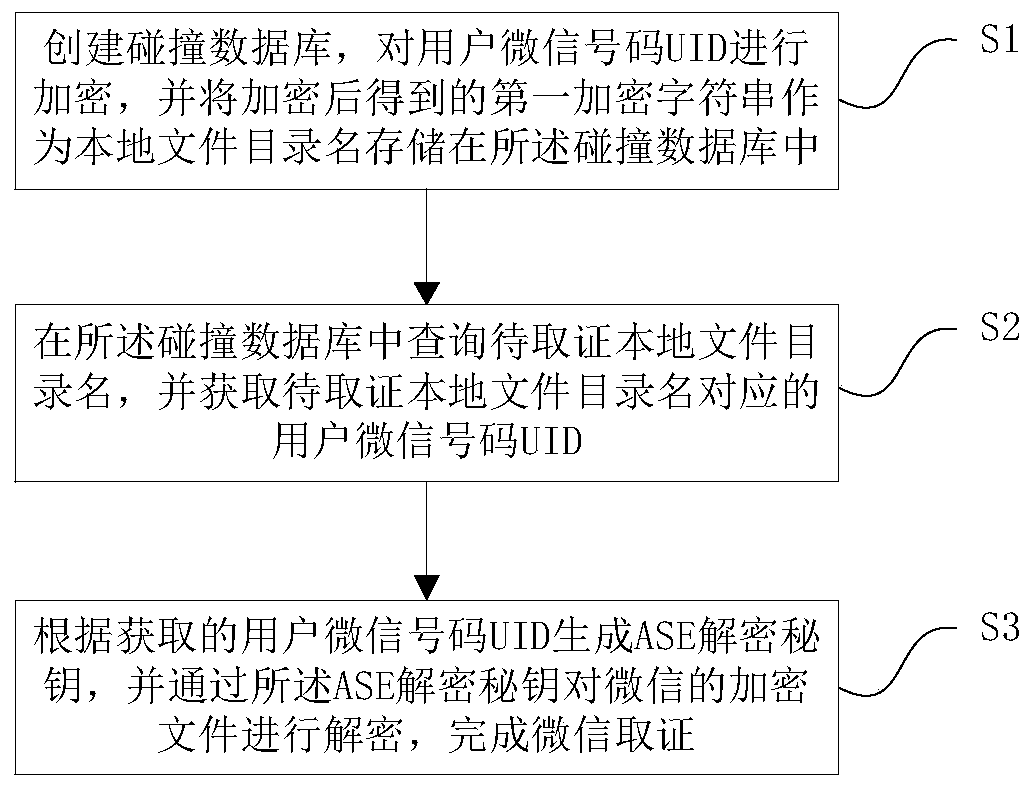
Figure 1 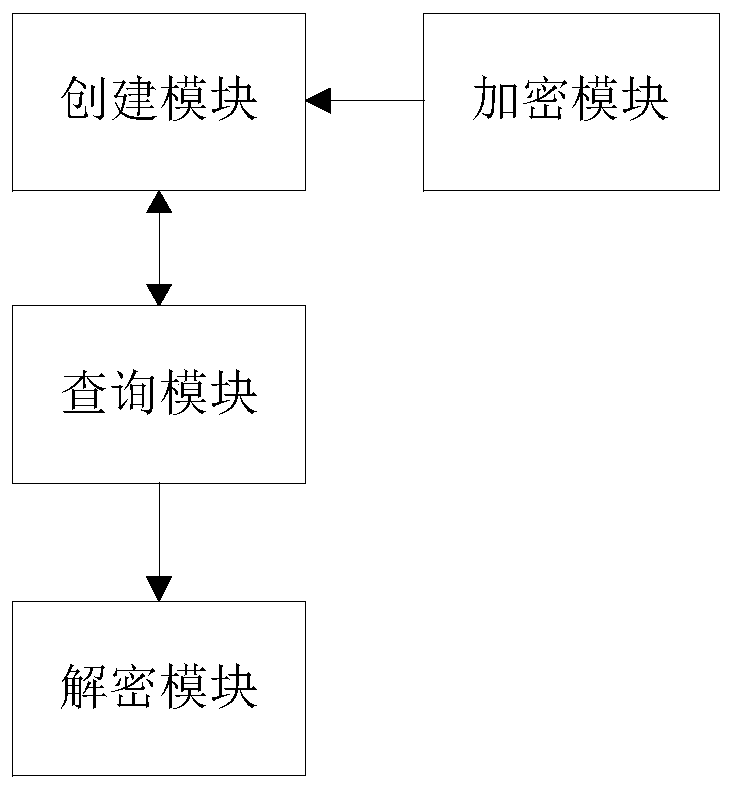
Figure 2 
Figure 3
Abstract
Description
technical field
[0001] The present invention relates to the technical field of data encryption and decryption, in particular to a WeChat evidence collection method and system based on data collision. Background technique
[0002] The traditional mobile phone forensic analysis system decrypts the extracted WeChat local files, obtains the WeChat user UID by analyzing the fields of the cached files, and then transforms the UID to obtain the decryption key to achieve decryption. However, when the user UID is not known or the same mobile phone logs in multiple WeChat accounts, the UID cannot be obtained and analyzed, or the WeChat user UID corresponding to the local file cannot be identified, and thus the WeChat data cannot be analyzed and collected. In order to overcome the above-mentioned technical defects, it is necessary to establish a mapping relationship between the user's local data and the user data information in the server database, so as to facilitate the completion of...
Examples
Embodiment 1
[0015] Embodiment 1. A WeChat forensics method based on data collision. The following will combine figure 1 A WeChat forensics method based on data collision in this embodiment is introduced in detail.
[0016] like figure 1 As shown, a WeChat forensics method based on data collision includes the following steps:
[0017] Step 1: Create a collision database, encrypt the UID of the user's WeChat ID, and store the first encrypted character string obtained after encryption as a local file directory name in the collision database;
[0018] Step 2: Query the directory name of the local file to be evidenced in the collision database, and obtain the UID corresponding to the directory name of the local file to be evidenced;
[0019] Step 3: Generate an AES decryption key according to the obtained user's WeChat code UID, and use the AES decryption key to decrypt the encrypted file of WeChat to complete WeChat evidence collection.
[0020] In this embodiment, in the step 1, the spec...
Embodiment 2
[0042] Embodiment 2. A WeChat forensics system based on data collision. The following will combine figure 2 A WeChat forensics system based on data collision in this embodiment is introduced in detail.
[0043] like figure 2 As shown, a WeChat forensics system based on data collision includes a creation module, an encryption module, a query module and a decryption module. The creation module is used to create a collision database; the encryption module is used for user micro-signal code UID to encrypt, and the first encrypted character string obtained after encryption is stored in the collision database as a local file directory name; the query The module is used to inquire about the local file directory name to be obtained in the collision database, and obtains the user micro-signal code UID corresponding to the local file directory name to be obtained; the decryption module is used to generate an AES decryption key according to the obtained user micro-signal code UID , ...