A sandbox shelling method and system based on an android virtual machine
What is AI technical title?
AI technical title is built by Patsnap AI team. It summarizes the technical point description of the patent document.
A virtual machine and sandbox technology, applied in the field of information security, can solve the problems of mobile phone sensitive information theft, system crash, security risks, etc., and achieve the effect of ensuring the security of the device environment, simple use and high efficiency
Active Publication Date: 2022-06-21
WUHAN ANTIY MOBILE SECURITY
View PDF4 Cites 0 Cited by
Summary
Abstract
Description
Claims
Application Information
AI Technical Summary
This helps you quickly interpret patents by identifying the three key elements:
Problems solved by technology
Method used
Benefits of technology
Problems solved by technology
At the same time, other malicious programs can also obtain root privileges, resulting in the tampering of the system, or the theft of sensitive information in the mobile phone, resulting in security risks
Secondly, the hook technology uses the replacement of key functions in the system layer to achieve the goal of obtaining memory. Improper handling may lead to system crashes
Method used
the structure of the environmentally friendly knitted fabric provided by the present invention; figure 2 Flow chart of the yarn wrapping machine for environmentally friendly knitted fabrics and storage devices; image 3 Is the parameter map of the yarn covering machine
View more
Image
Smart Image Click on the blue labels to locate them in the text.
Viewing Examples
Smart Image
Click on the blue label to locate the original text in one second.
Reading with bidirectional positioning of images and text.
Smart Image
Examples
Experimental program
Comparison scheme
Effect test
specific Embodiment 1
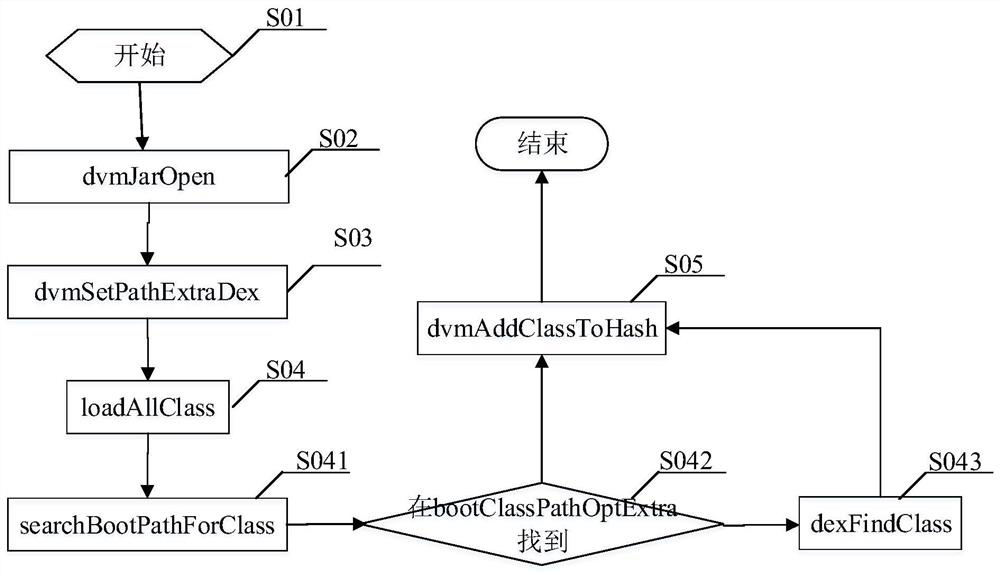
[0097] combine image 3 As shown, the present invention provides a function of modifying the Android system framework code based on the Android system principle. The steps of this function are as follows:
[0099] S02, using the system dvmJarOpen to load the custom Android virtual machine code package of the present invention to obtain a DexFile object.
[0100] S03, calling dvmSetBootPathExtraDex to store the above DexFile object in bootClassPathOptExtra.
[0101] S04, call loadAllClass, and loop to find the classes in the above DexFile, so all of them are added to the hashTable for subsequent use.
[0102] S041, classloader and DvmDex are not provided here for class search, use dvmFindSystemClassNoInit to search from bootclass.
[0103] S042, use dexFindClass to search directly from bootClassPathOptExtra, and return if found, otherwise go to the next step.
[0104] S043, use dexFi...
specific Embodiment 2
[0106] This system refers to the operating principle of the Android system, and implements the interfaces from Activity, Application to ActivityThread, etc., which are directly called by applications. It also implements classes related to environment and resources such as ApplicationInfo, LoadedApk, Context, etc. Since many system principles are involved, this embodiment only describes the reference steps.
[0107] S01, the control module starts the dalvik virtual machine.
[0108] S02, the control module uses the function of Embodiment 1 to load the jar package of the system framework.
[0109] S03, pass in the target application app path, and parse to obtain the Application name and the main Activity name.
[0110] S04, use the Jni interface FindClass to find the target Application class, and call Initialize the function and call NewObject to generate an object.
[0111] S05, use the Jni interface FindClass to find the ActivityThread. At this time, the ActivityThread i...
the structure of the environmentally friendly knitted fabric provided by the present invention; figure 2 Flow chart of the yarn wrapping machine for environmentally friendly knitted fabrics and storage devices; image 3 Is the parameter map of the yarn covering machine
Login to View More
PUM
Login to View More
Abstract
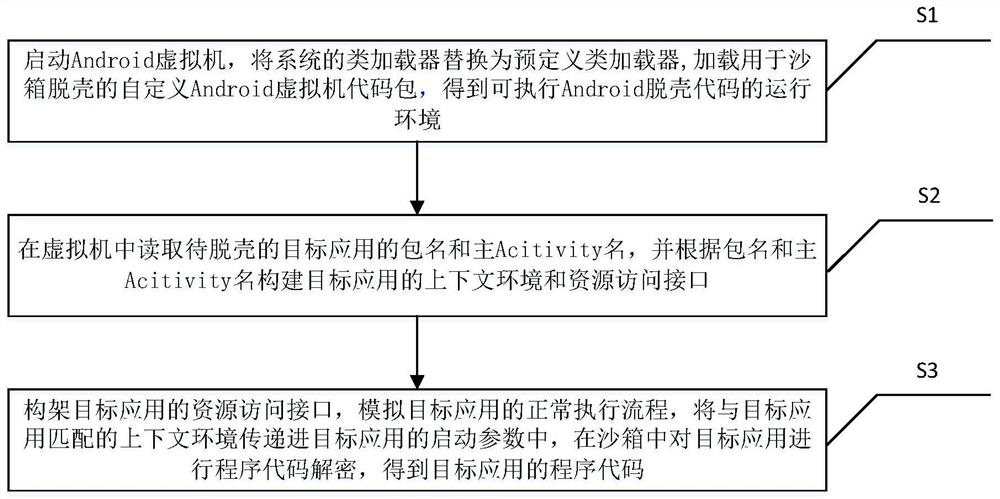
The invention discloses a sandbox unpacking method and system based on an Android virtual machine. The method includes the following steps: starting the Android virtual machine, replacing the class loader of the system with a predefined class loader, and loading the unpacking method for sandbox unpacking. Customize the Android virtual machine code package of the shell to obtain the operating environment that can execute the Android unpacking code; read the package name and main activity name of the target application to be unpacked in the virtual machine, and build the target application according to the package name and main activity name The context environment and resource access interface of the target application; the resource access interface of the target application is constructed, the normal execution process of the target application is simulated, the context environment matching the target application is passed into the startup parameters of the target application, and the target application is programmed in the sandbox The code is decrypted to obtain the program code of the target application. The execution environment of the present invention does not need to provide the highest access authority, which ensures the security of the user's equipment environment; and is simple to use and high in execution efficiency.
Description
technical field [0001] The invention relates to the technical field of information security, in particular to a method and system for unpacking a sandbox based on an Android virtual machine. Background technique [0002] Android devices are developing rapidly, extending from mobile phones to tablets, smart TVs, etc., and there are more and more risky and malicious applications on the devices. The general malicious detection methods are mostly based on feature detection, which is basically ineffective for the malicious behavior of hardened samples. Therefore, there is an urgent need for a solution that can provide a fast detection function in user scenarios. [0003] The general unpacking technology on the user side requires the use of hook (hook) technology, and involves system root (obtaining the highest authority), which is equivalent to opening a door to the mobile system and causing security risks. The system root is based on a linux-like account authority mechanism. T...
Claims
the structure of the environmentally friendly knitted fabric provided by the present invention; figure 2 Flow chart of the yarn wrapping machine for environmentally friendly knitted fabrics and storage devices; image 3 Is the parameter map of the yarn covering machine
Login to View More
Application Information
Patent Timeline
Application Date:The date an application was filed.
Publication Date:The date a patent or application was officially published.
First Publication Date:The earliest publication date of a patent with the same application number.
Issue Date:Publication date of the patent grant document.
PCT Entry Date:The Entry date of PCT National Phase.
Estimated Expiry Date:The statutory expiry date of a patent right according to the Patent Law, and it is the longest term of protection that the patent right can achieve without the termination of the patent right due to other reasons(Term extension factor has been taken into account ).
Invalid Date:Actual expiry date is based on effective date or publication date of legal transaction data of invalid patent.

 Login to View More
 Login to View More