
A program anomaly analysis method based on dynamic taint propagation
A technology of program exception and analysis method, which is applied in the field of network security, can solve problems such as staying on the surface, insufficient analysis depth, inability to deal with packing confusion, anti-debugging ability target software, etc., and achieve the effect of improving analysis efficiency
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Patents(China)
- Current Assignee / Owner
- Publication Date
- 2021-04-27
Smart Images
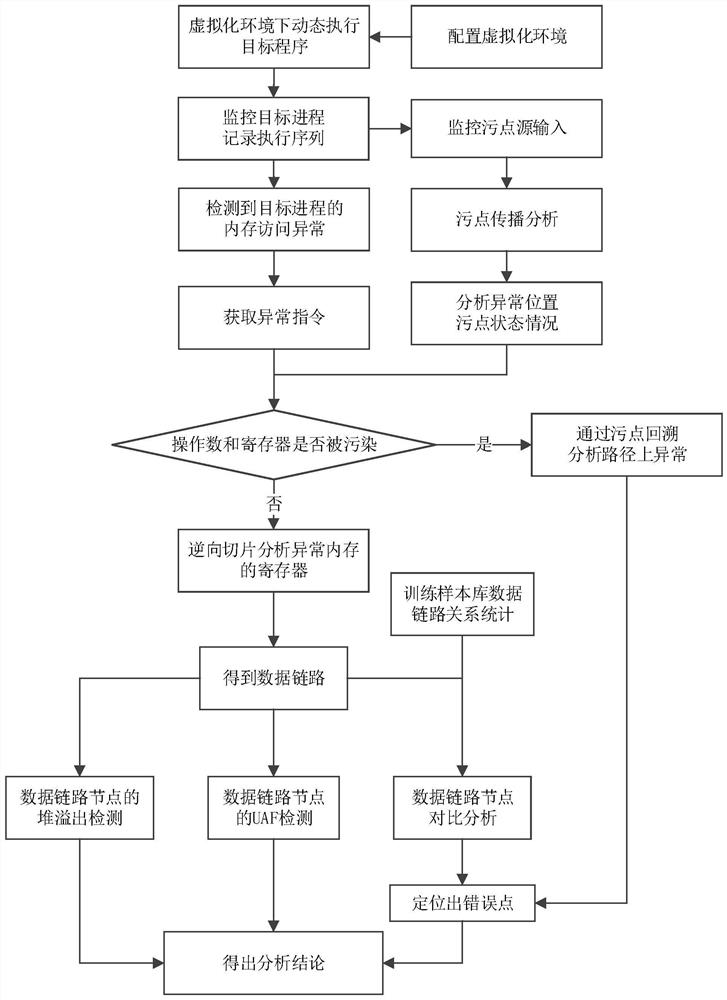
Figure 1 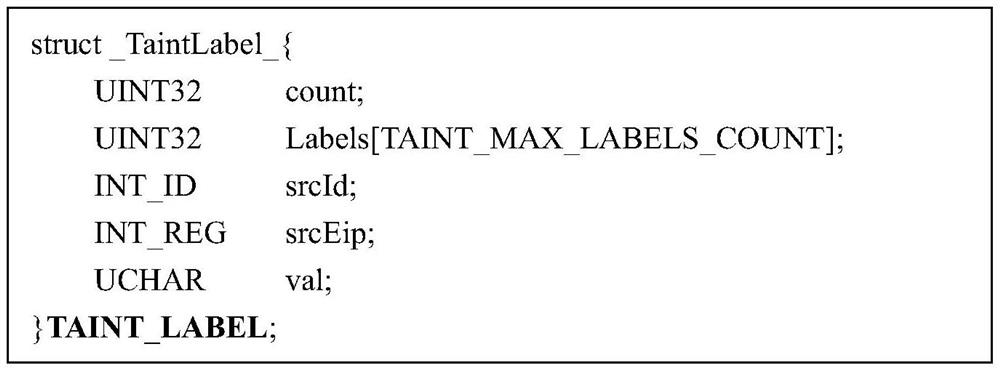
Figure 2
Abstract
Description
technical field
[0001] The invention belongs to the technical field of network security, and specifically relates to a method for analyzing abnormalities or loopholes of binary programs and locating error points on a virtualization platform based on data flow analysis of dynamic stain propagation. Background technique
[0002] With the continuous improvement of program functions, scale, and complexity and the intensification of update iteration speed, as well as the lack of security awareness of software developers, software vulnerabilities have seriously threatened the security of cyberspace, and the damage caused by them has become increasingly serious. The harm of the vulnerability is initially manifested in the crash and exception of the program, and most of these crashes and exceptions are caused by memory access exceptions. Currently, memory access exceptions include memory read exceptions, write exceptions, and execution exceptions. Common causes include null pointer ...
Examples
Embodiment Construction
[0033] In order to make the object, technical solution and advantages of the present invention clearer, the present invention will be described in further detail below in conjunction with specific embodiments and with reference to the accompanying drawings.
[0034] like figure 1 As shown, a program anomaly analysis method based on dynamic taint propagation, including steps:
[0035] 1. Configure the virtualization environment
[0036] The present invention adopts the dynamic virtualization technology. Firstly, it is necessary to install the virtual machine operating system for running the target program, install and deploy the target program in the virtual machine operating system, import the input data files that cause abnormalities, and configure the required software and hardware environment for operation. network environment and other conditions.
[0037] 2. Dynamically run the target program
[0038] The present invention adopts a dynamic analysis method, uses a virtu...