
Method and system for realizing secure interaction between systems
A system and security technology, applied in the computer field, to achieve the effect of improving scalability
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2018-11-02
Smart Images
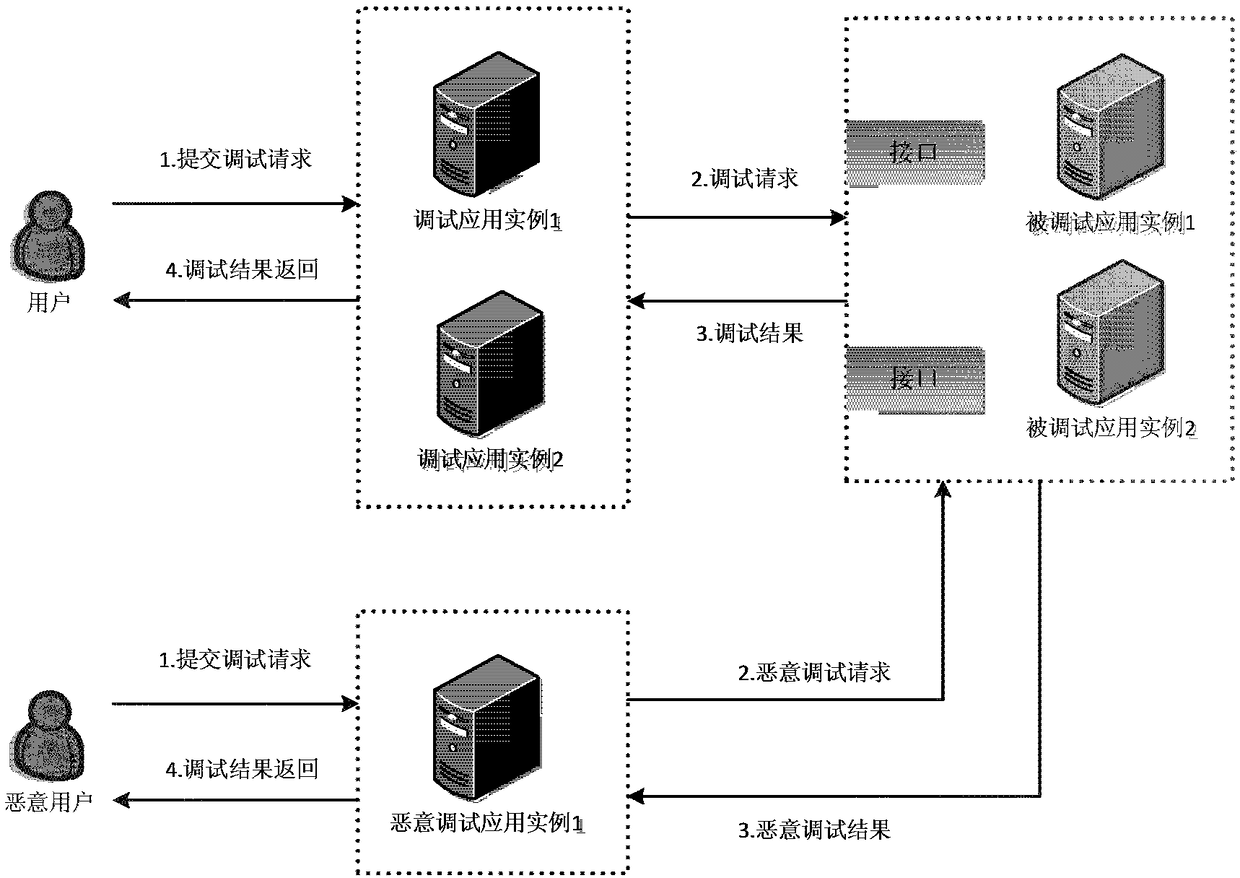
Figure 1 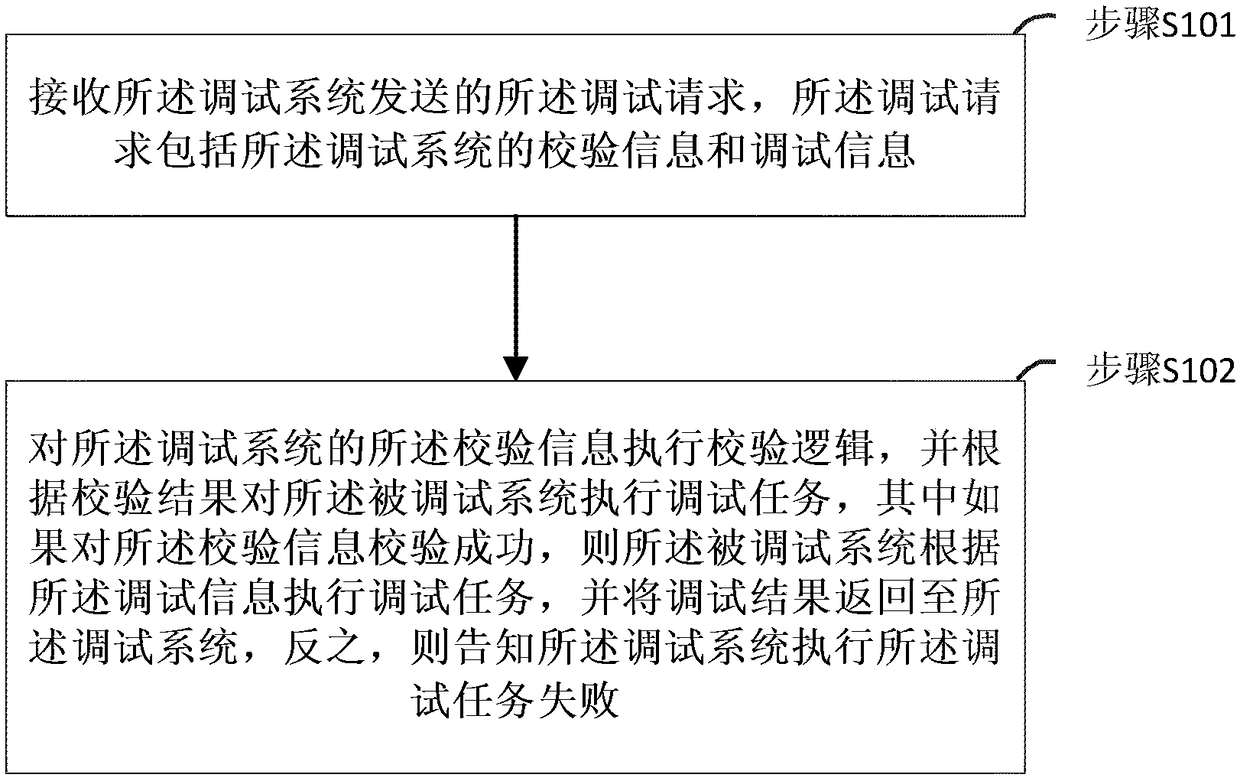
Figure 2 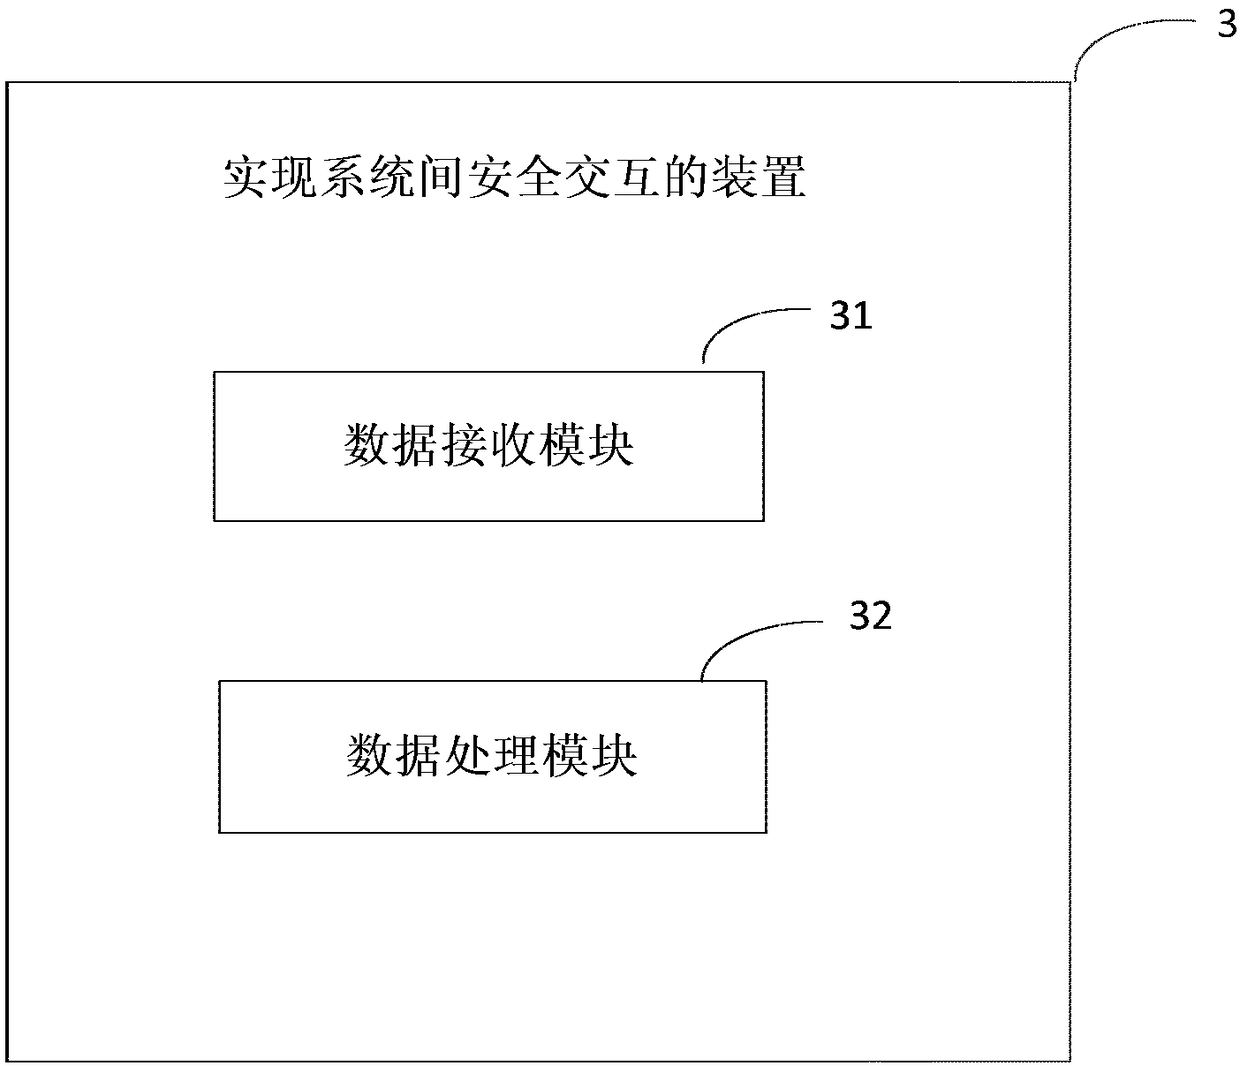
Figure 3
Abstract
Description
technical field
[0001] The invention relates to the field of computer technology, in particular to a method and device for realizing safe interaction between systems. Background technique
[0002] Existing Internet systems are generally divided into test environment, production environment, etc., and the production environment is the environment accessed by users, so the production environment cannot be changed or modified by developers at will. Many companies will strictly control the online process to ensure the stability of system services in the production environment. However, there are still some anomalies in the system in the production environment, and since they cannot be reproduced in the test environment, it is difficult for developers to find anomalies. When an abnormal situation occurs, it will inevitably lead to an extension of the exception processing time, which will affect the user's access.
[0003] In view of the above situation, the user can enter the d...
Examples
Embodiment
[0059] The present invention will be specifically described below in conjunction with a specific embodiment, but it should be noted that this specific embodiment is only for better describing the present invention, and does not constitute an improper limitation of the present invention.
[0060] Step S201: the user initiates a debugging request, and the debugging system receives the debugging request from the user;
[0061] Step S202: The debugging system acquires the Token value of the debugged system from the local cache, if it does not exist in the local cache, then execute step S203; if it exists, then execute step S204;
[0062] Step S203: The monitoring system obtains the Token value list of the debugged system, finds the Token value of the currently called system, and stores the Token value in the local cache, and then executes Step S204;
[0063] Step S204: Set the acquired Token value of the debugged system into the set in the request header of the debug request, and...