
Server network behavior description method
A server and network technology, applied in the direction of data exchange network, digital transmission system, electrical components, etc., can solve the problems of many differences, poor new attack or intrusion detection effect, high false positive rate, etc., to achieve intuitive and reliable results, The effect of reducing the false negative rate and high accuracy
Patent Information
- Authority / Receiving Office
- CN · China
- Patent Type
- Applications(China)
- Current Assignee / Owner
- Publication Date
- 2015-11-18
Smart Images
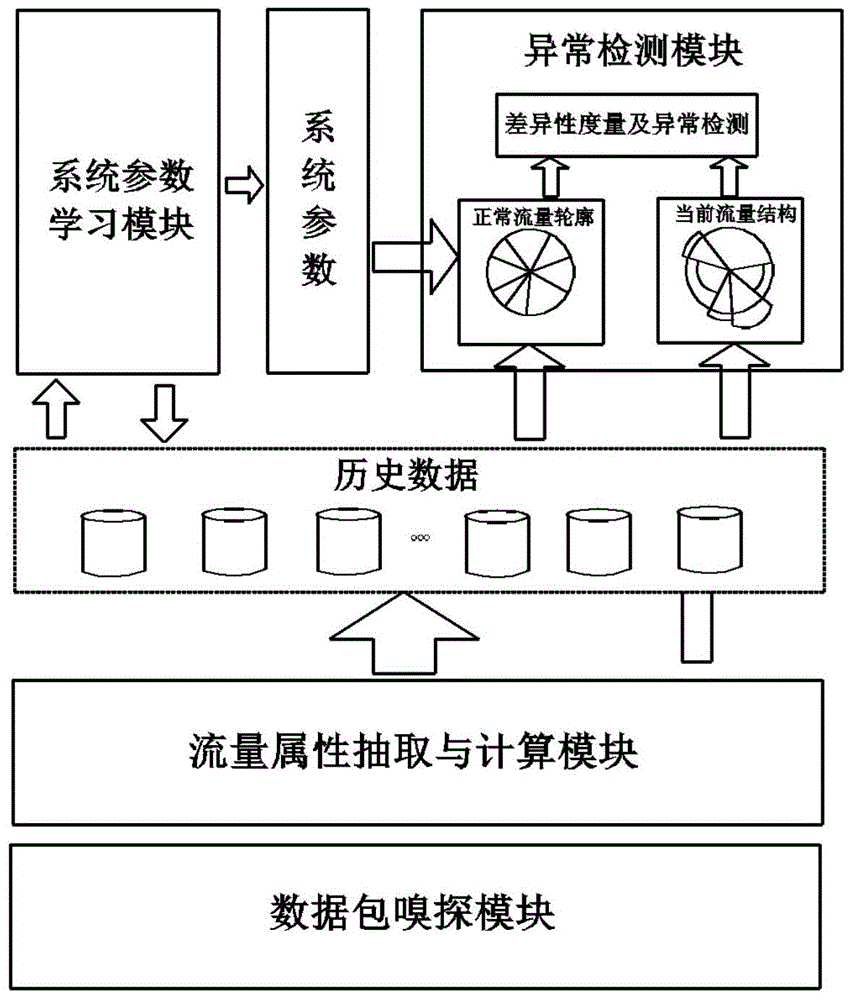
Figure 1 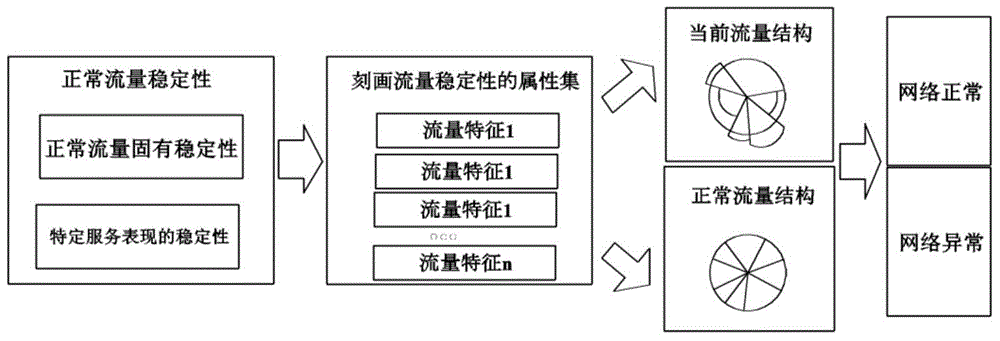
Figure 2 
Figure 3
Abstract
Description
technical field
[0001] The invention relates to a behavior description method for network abnormal traffic detection, in particular to a server network behavior description method based on traffic structure stability. Background technique
[0002] The server is usually used as the core equipment in the IT system to provide network services, so the security protection of the server is particularly important; for the security protection of the server network, according to the characteristics of the protection means, it can be mainly divided into the following three categories: (1) Deploying intrusion detection based on the network boundary System, firewall and other protective equipment; (2) Correlation analysis and mining based on server logs; (3) Traffic analysis on servers.
[0003] At present, the main means of server security protection is to deploy border devices such as IDS, IPS, and firewalls on the network border to detect and filter the traffic entering and leaving t...
Examples
Embodiment Construction
[0049] The present invention will be further described below in conjunction with the accompanying drawings and specific embodiments.
[0050] A server network behavior description method, comprising the following steps:
[0051] (1) Obtain the flow information of entering and exiting the server through the data packet sniffing module;
[0052] (2) Extract the flow information according to the flow attributes through the flow attribute extraction and calculation module, and make statistics on the flow corresponding to each flow attribute according to the time window to form historical data;
[0053] (3) Calculate the acquired historical data through the system parameter learning module that interacts with the historical data in real time, and obtain the system parameters based on the stability of the traffic structure;
[0054] (4) Construct a dynamic normal flow profile according to system parameters and historical data;
[0055] (5) Construct the current traffic structure a...