
Secure memory card with life cycle phases
a technology of memory cards and life cycle phases, applied in the field of memory cards and encryption, can solve the problems of difficult access to testing mechanisms, encryption keys, encrypted content, and inability to access encrypted keys, and achieve the effect of solving problems such as scalability
Patent Information
- Authority / Receiving Office
- US · United States
- Patent Type
- Patents(United States)
- Current Assignee / Owner
- Publication Date
- 2012-11-27
- Estimated Expiration
- Not applicable · inactive patent
Smart Images
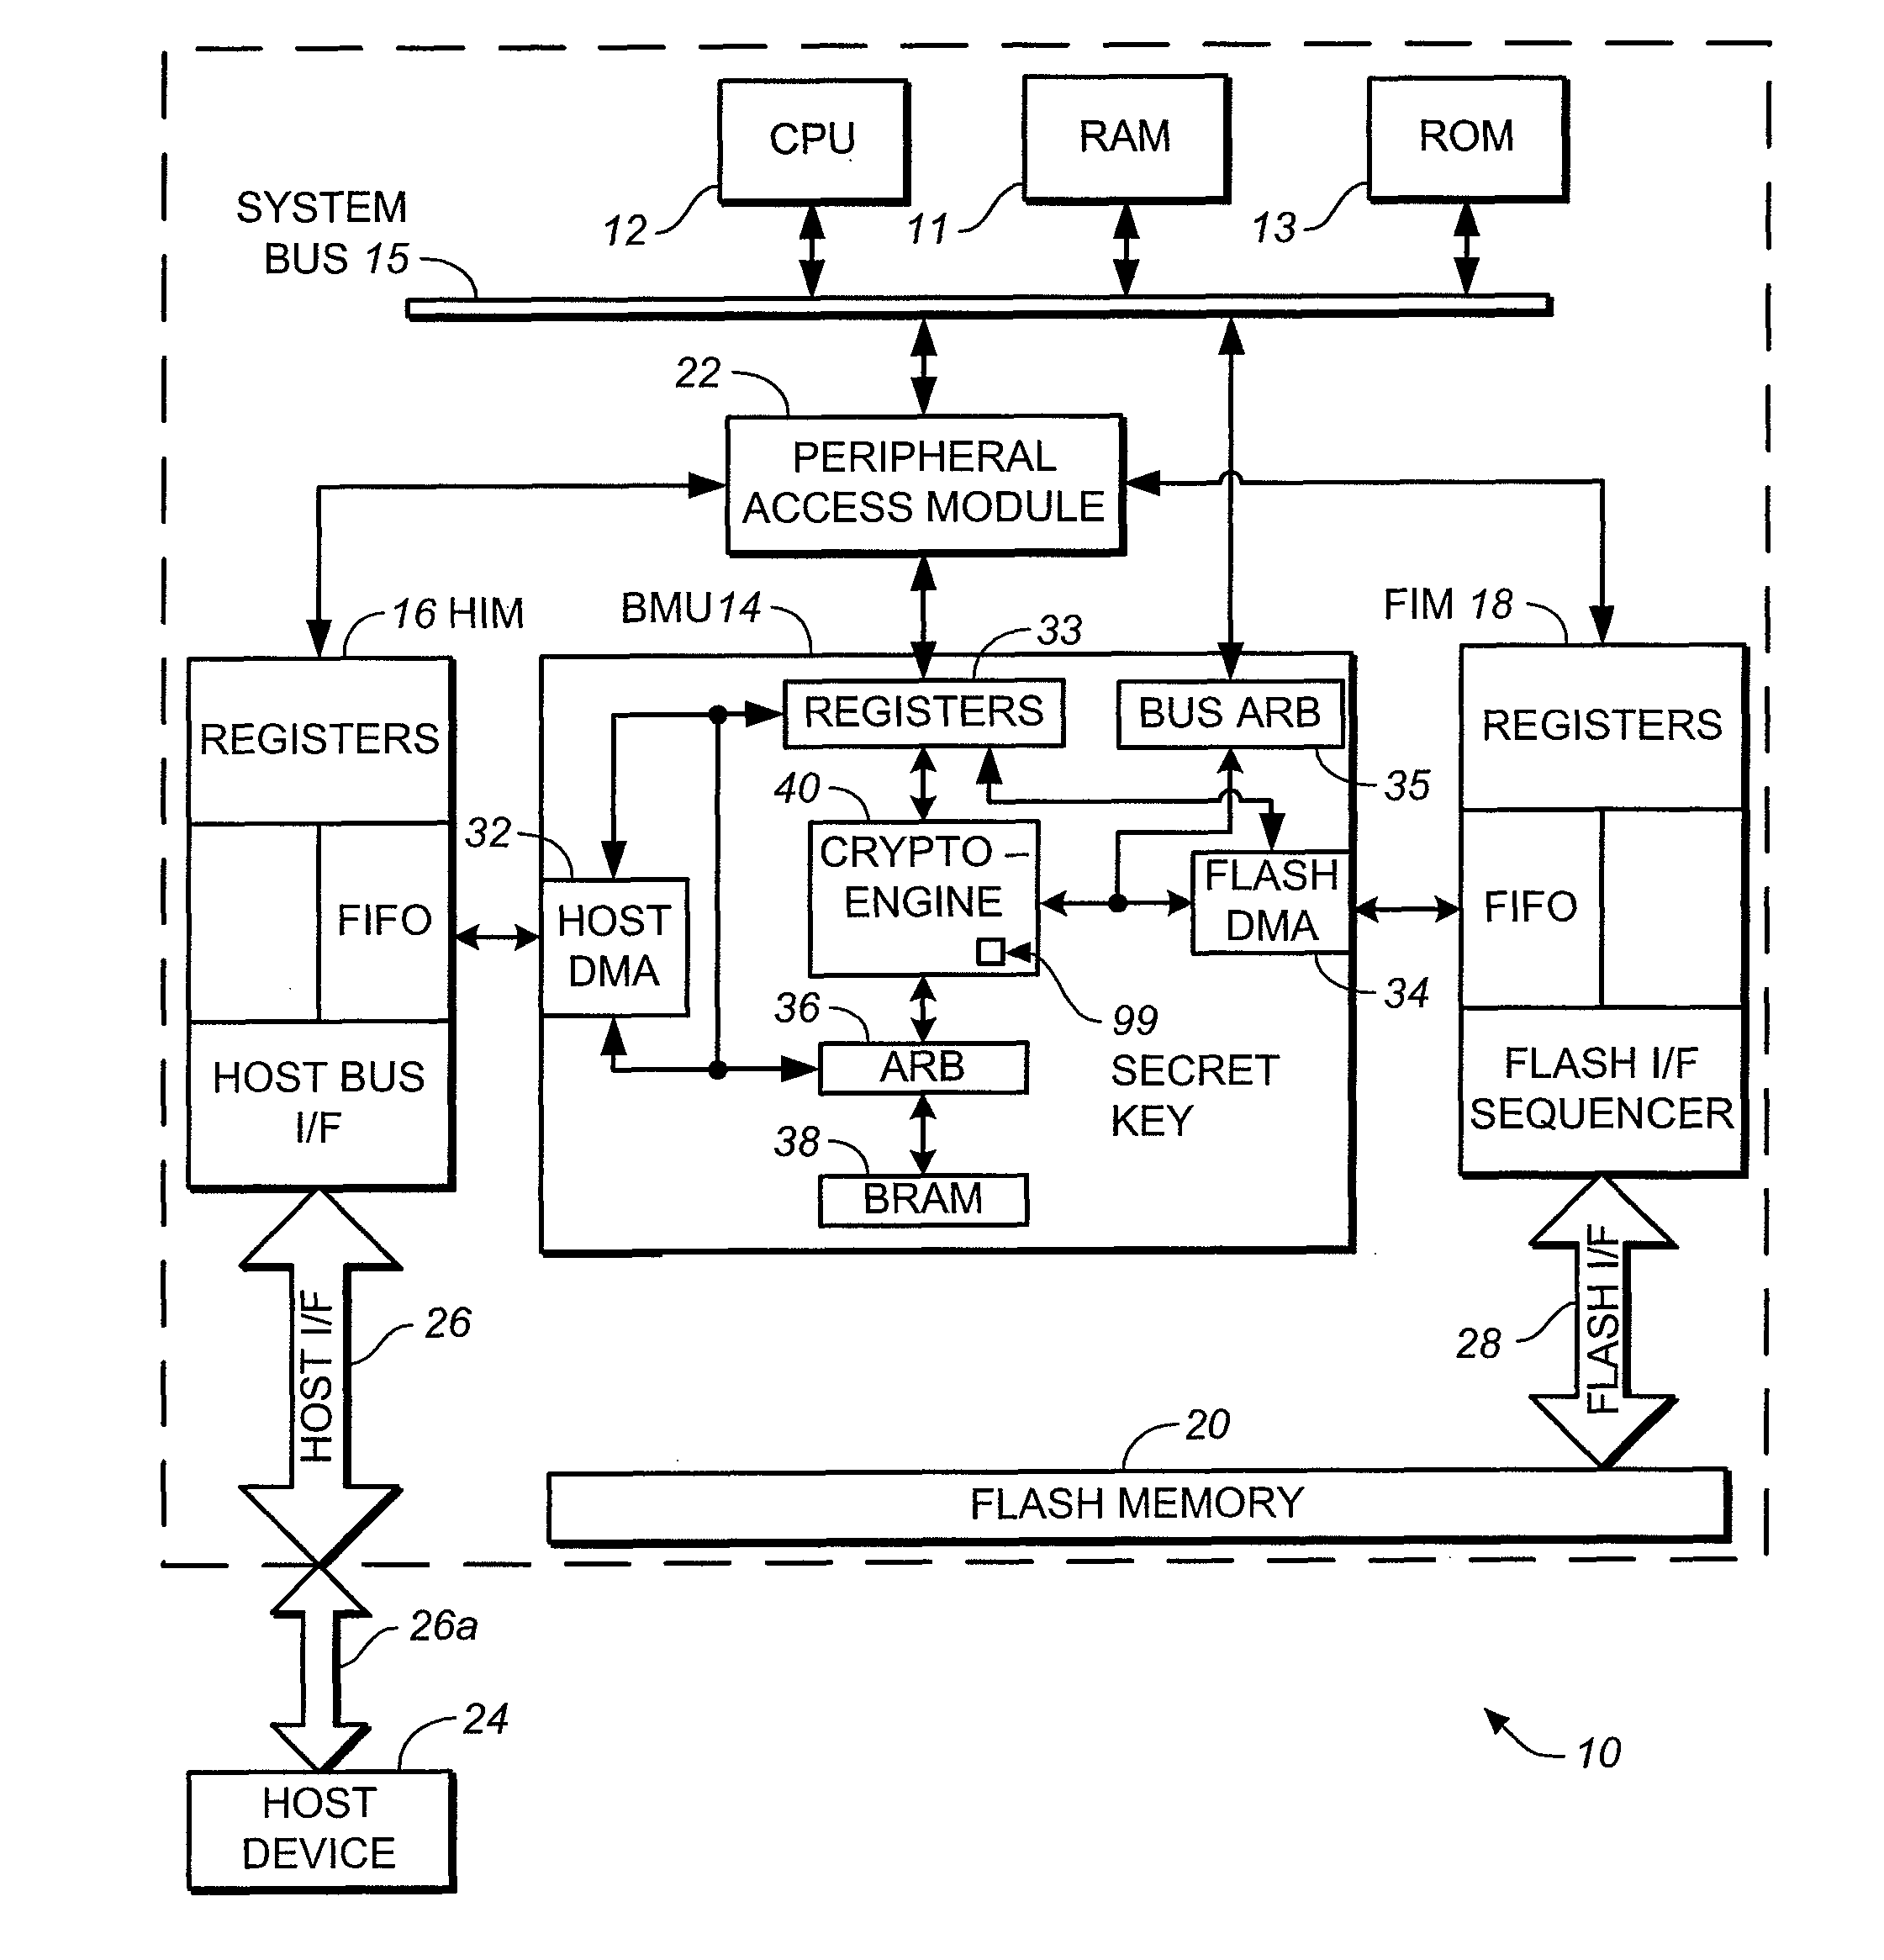
Figure 1 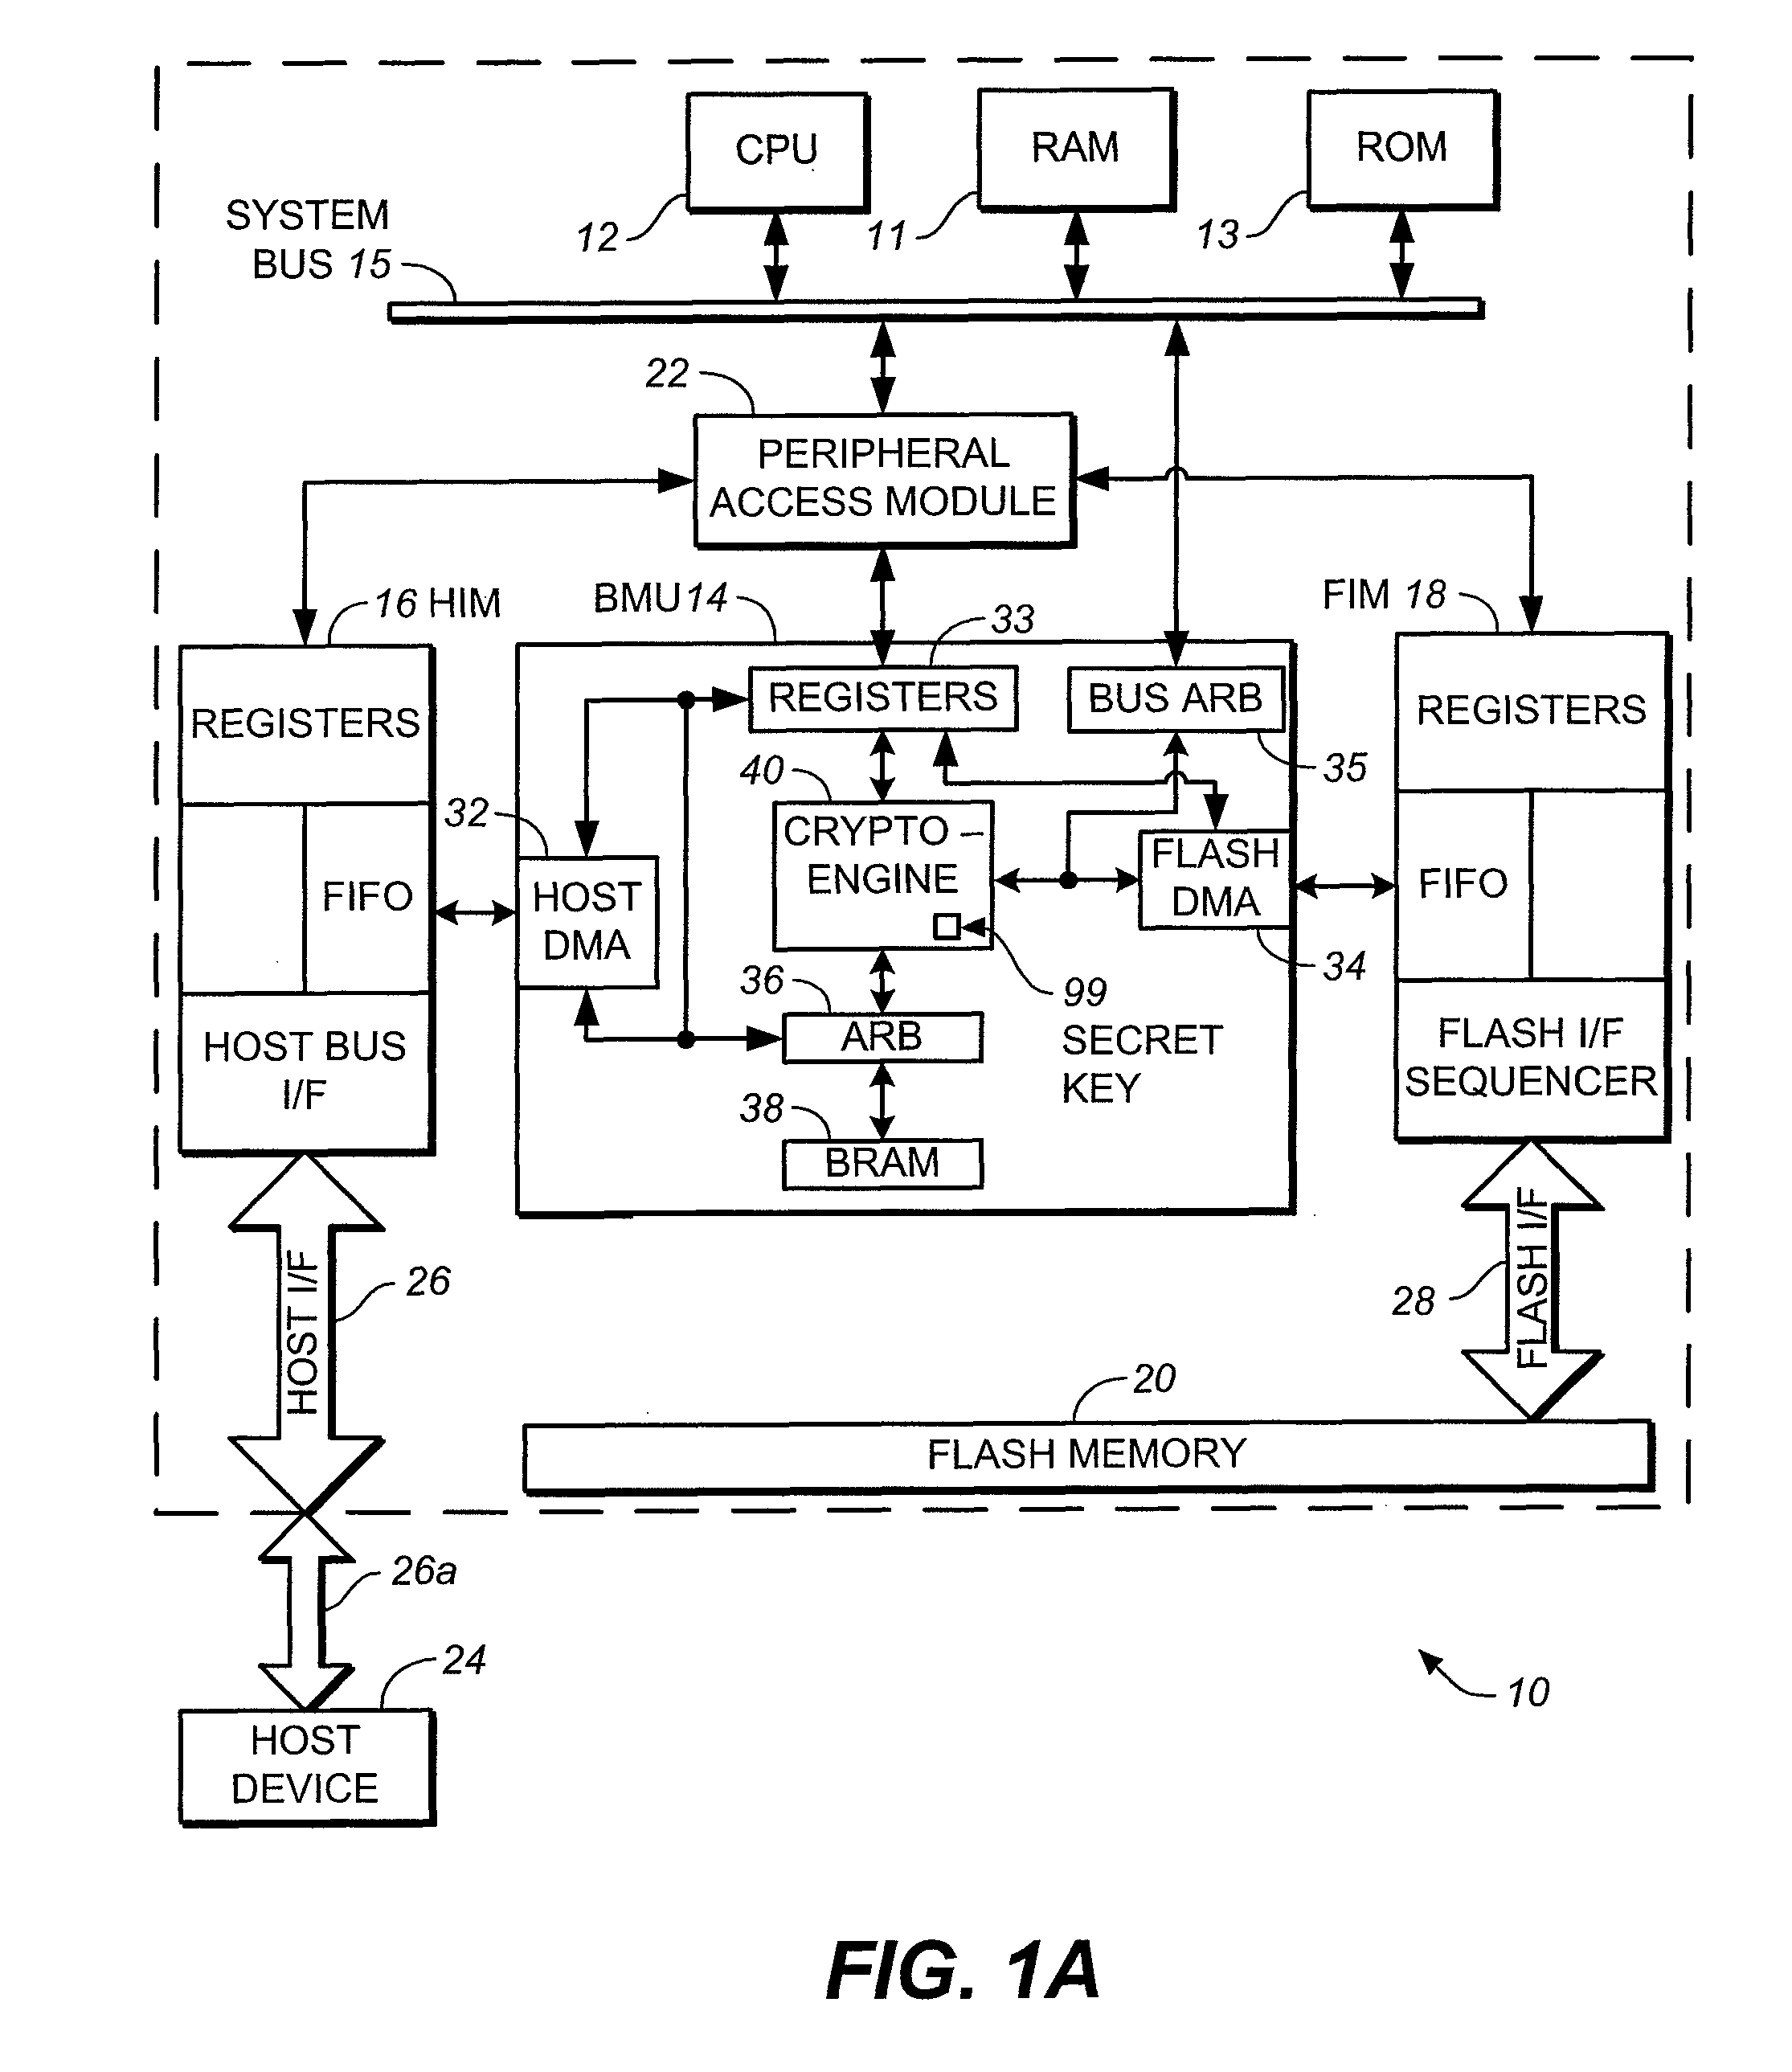
Figure 2 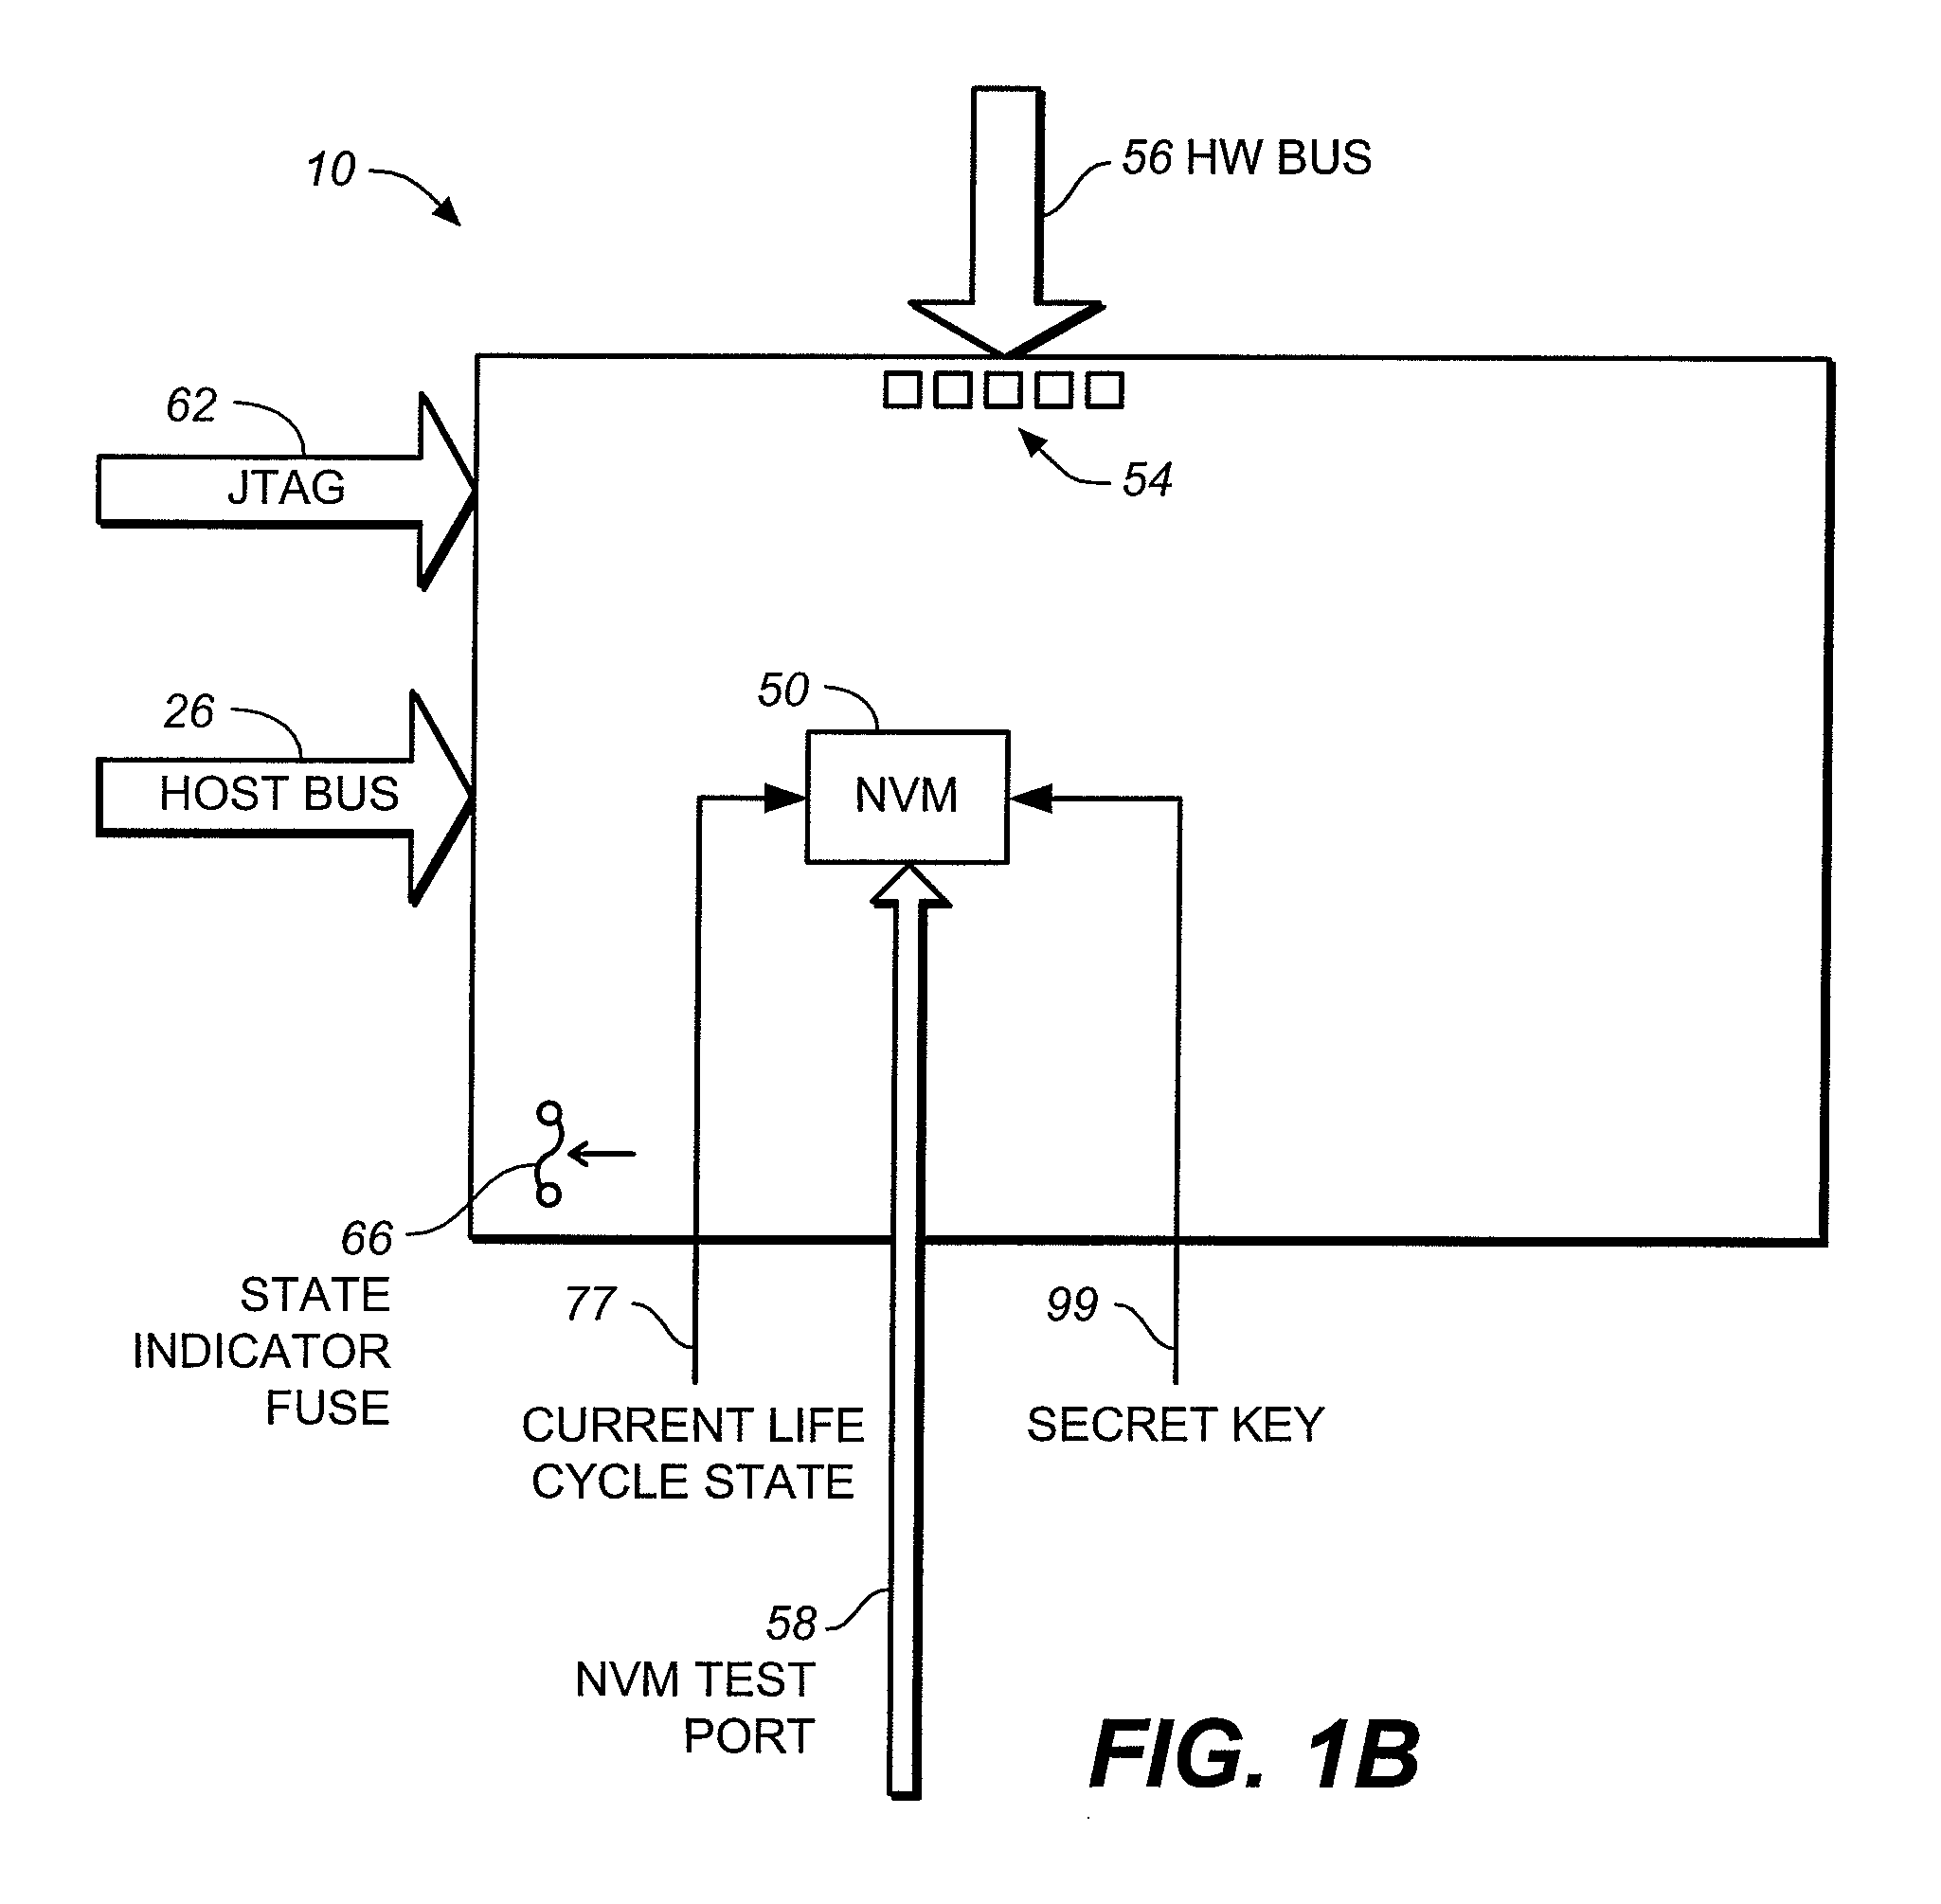
Figure 3
Abstract
Description
CROSS REFERENCE TO RELATED APPLICATIONS
[0001] This application claims priority to provisional Application No. 60 / 651,128, filed Feb. 7, 2005, to Micky Holtzman et al. entitled “Secure Memory Card With Life Cycle Phases.”
[0002] This application is related to the following applications, each of which is hereby incorporated by this reference in its entirety: “Methods Used in a Secure Memory Card With Life Cycle Phases” to Micky Holtzman et al. filed herewith, “Method of Hardware Driver Integrity Check Of Memory Card Controller Firmware” to Micky Holtzman et al., application Ser. No. 11 / 284,623, “Hardware Driver Integrity Check Of Memory Card Controller Firmware” to Micky Holtzman et al., application Ser. No. 11 / 285,600, “Methods Used in a Secure Yet Flexible System Architecture for Secure Devices With Flash Mass Storage Memory” filed herewith to Micky Holtzman et al., and Secure Yet Flexible System Architecture for Secure Devices With Flash Mass Storage Memory” filed herewith to Micky Ho...
Examples
Embodiment Construction
Memory System Architecture
[0019]An example memory system in which the various aspects of the present invention may be implemented is illustrated by the block diagram of FIG. 1A. As shown in FIG. 1A, the memory system 10 includes a central processing unit (CPU) or controller 12, a buffer management unit (BMU) 14, a host interface module (HIM) 16, flash interface module (FIM) 18, a flash memory 20 and a peripheral access module 22. Memory system 10 communicates with a host device 24 through a host interface bus 26 and port 26a. The flash memory 20, which may be of the NAND type, provides data storage for the host device 24. The software code for CPU 12 may also be stored in flash memory 20. FIM 18 connects to the flash memory 20 through a flash interface bus 28 and in some instances a port, which is not shown, if the flash memory 20 is a removable component. HIM 16 is suitable for connection to a host system like a digital camera, personal computer, personal digital assistant (PDA) an...