

Patents
Literature
51 results about "Vulnerability factor" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
Definition of Vulnerability factor. Vulnerability factor means an individual is a child under the age of six or meets the definition of an elderly or disabled person.
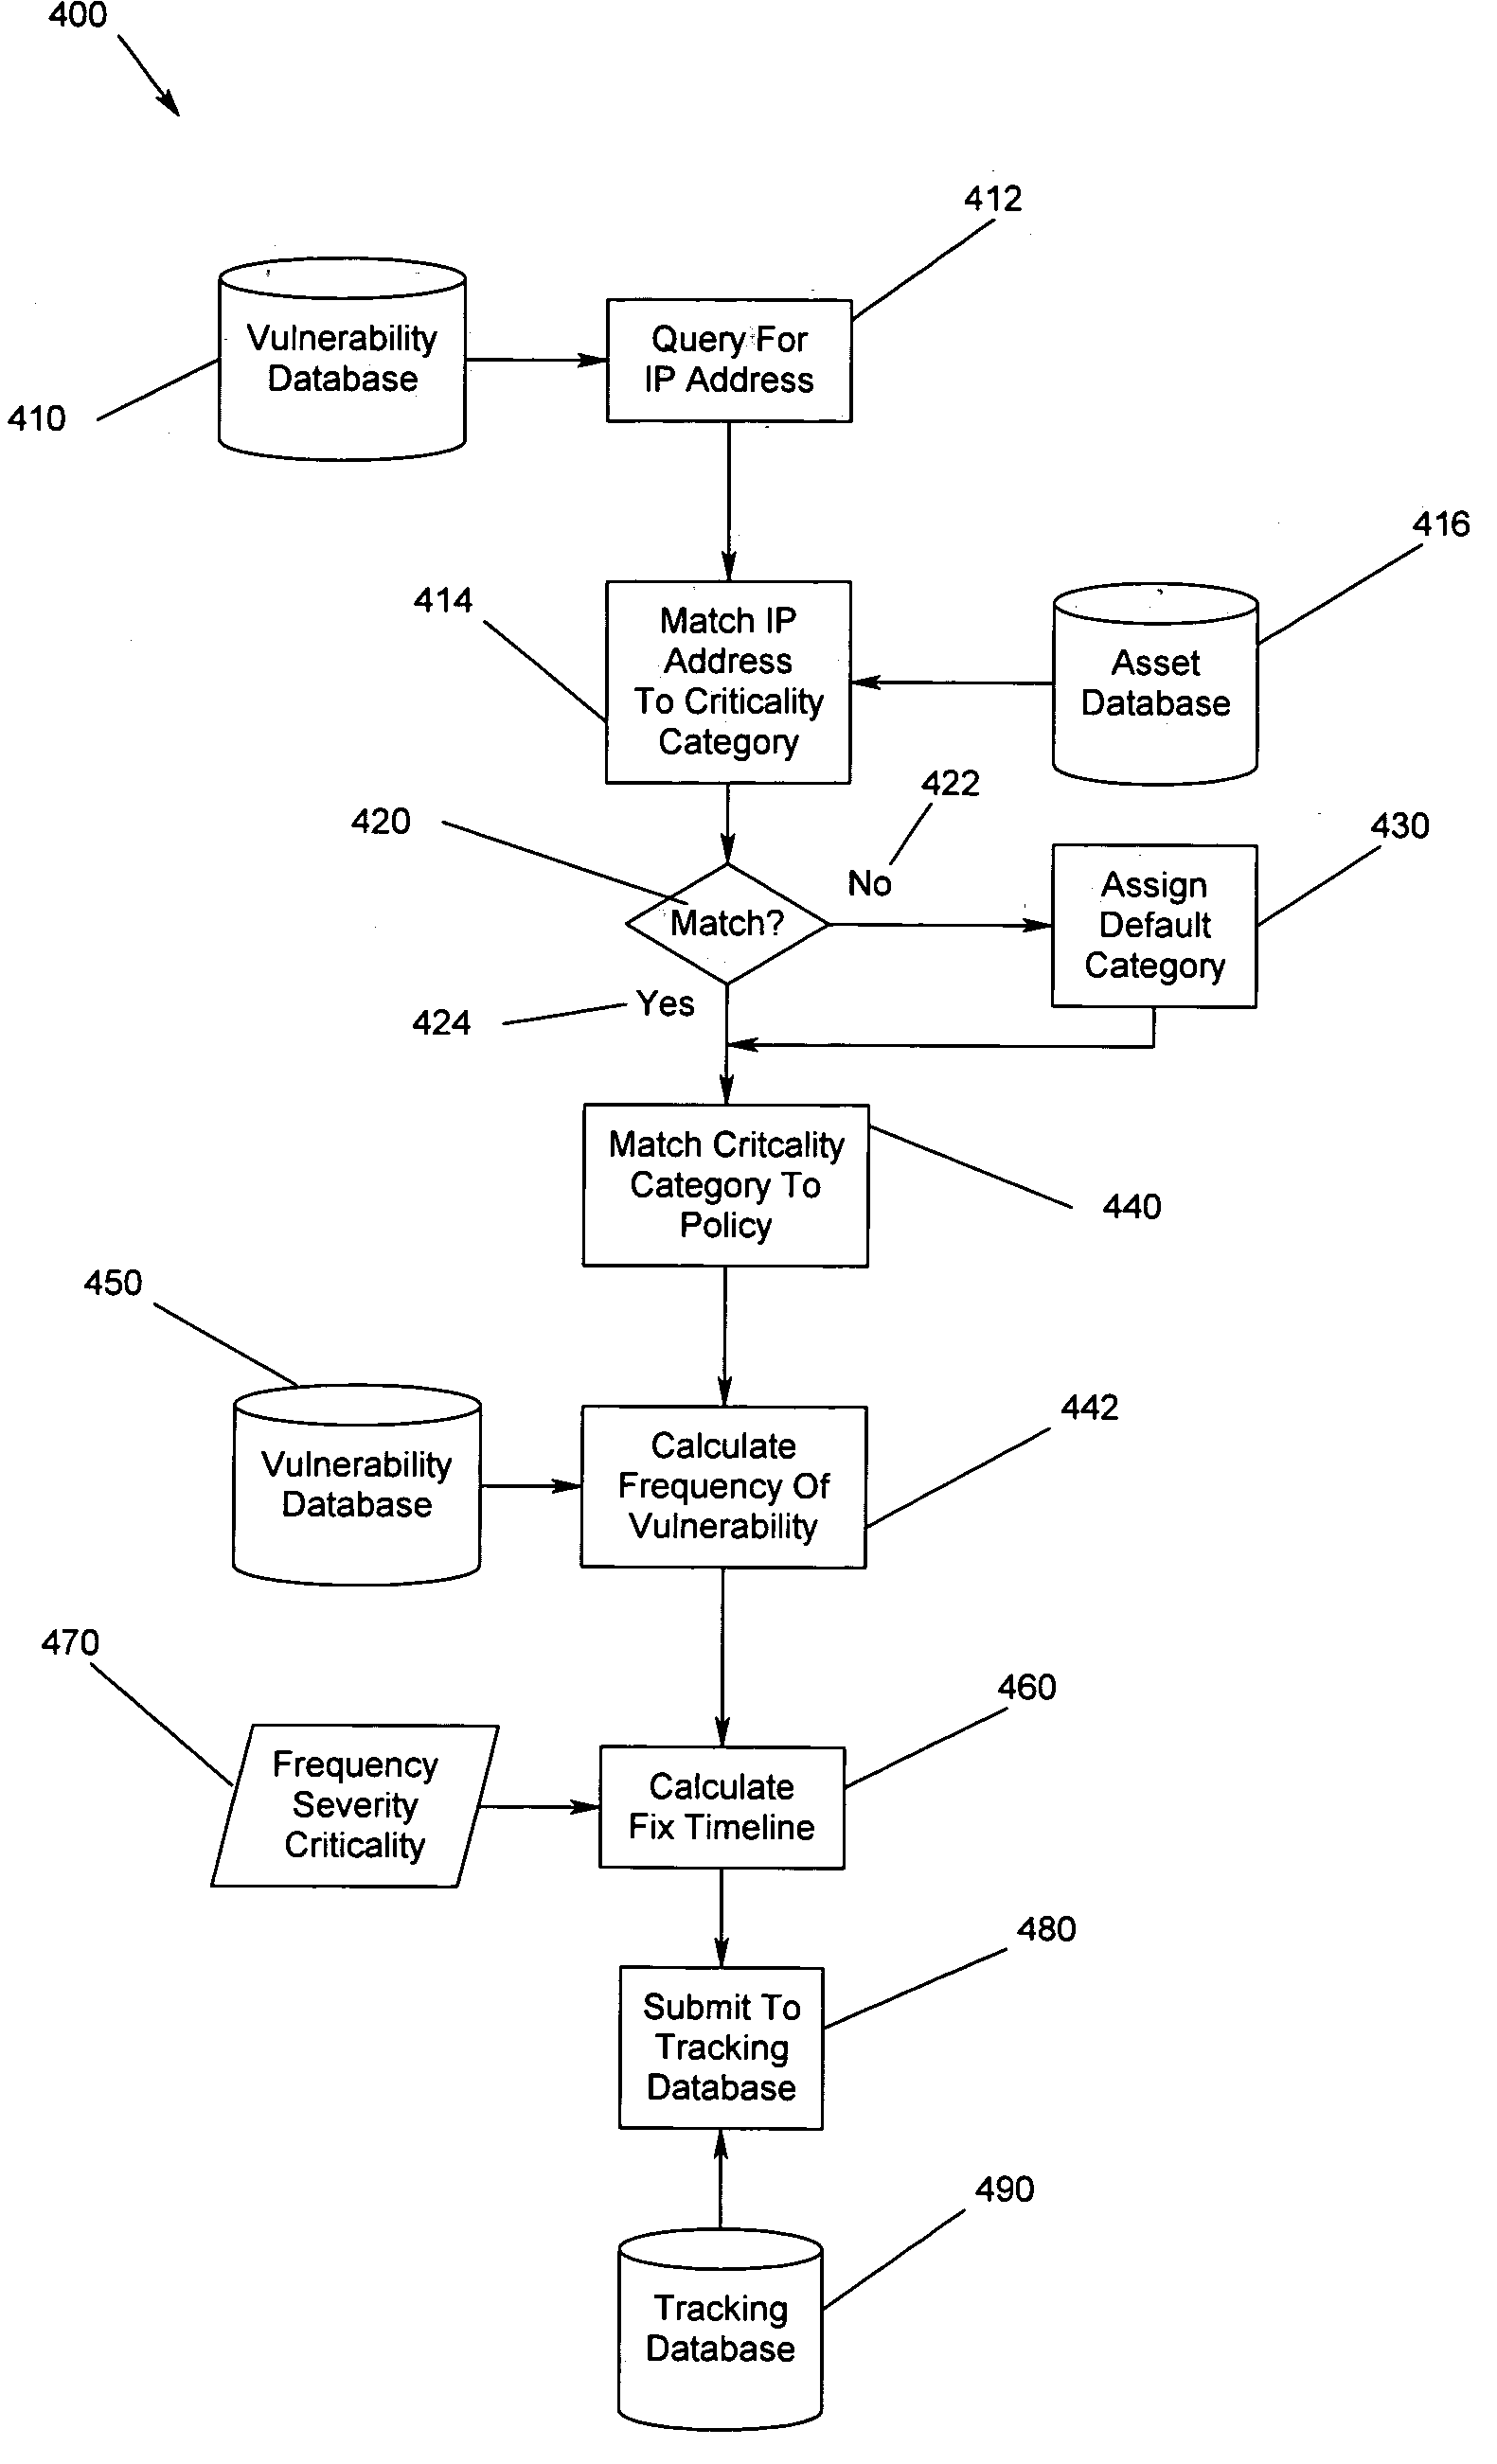
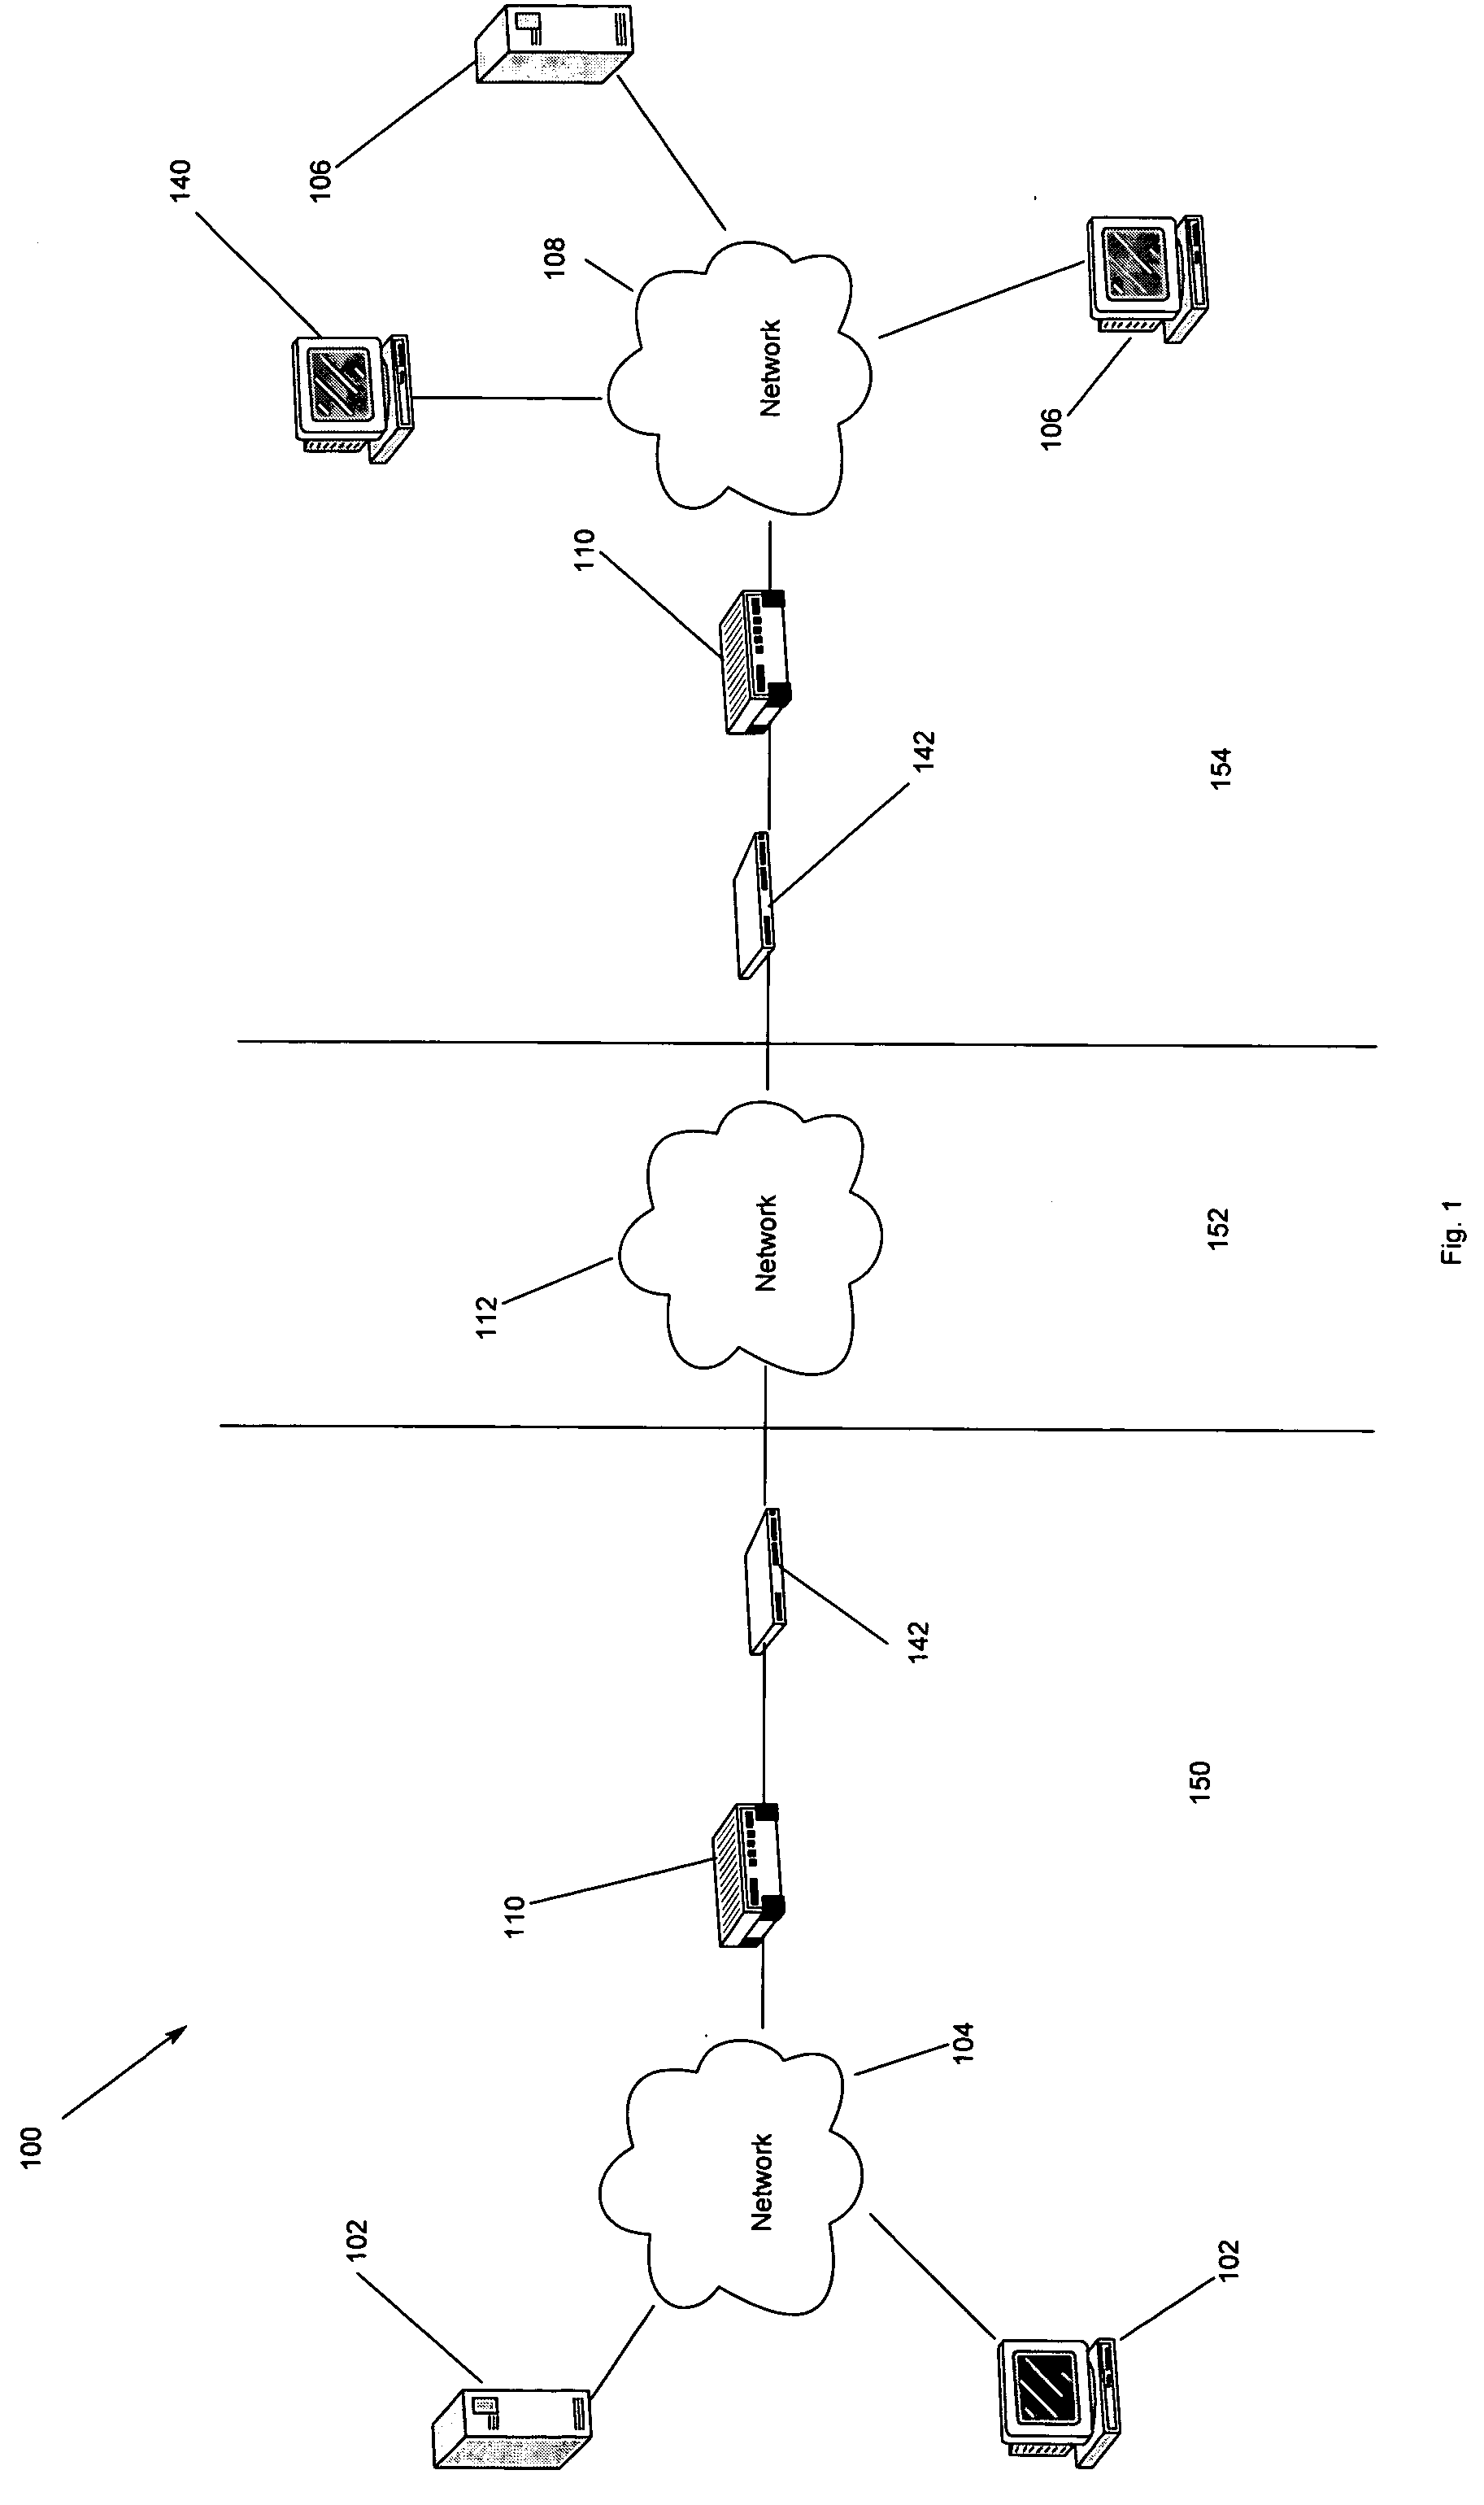
Method, apparatus and program storage device for providing automated tracking of security vulnerabilities
InactiveUS20050160480A1Memory loss protectionUnauthorized memory use protectionVulnerability factorOperating system
A method, apparatus and program storage device for providing automated tracking of security vulnerabilities is disclosed. Security problems are reported, aged and tracked. A time to fix the vulnerability identified by the vulnerability assessment of the system is based on the determined vulnerability score. The vulnerability factor is based upon consideration of a plurality of identified parameters.
Owner:IBM CORP
Electric power system vulnerability assessment method
InactiveCN104156769ACatastrophe preventionFully determinedData processing applicationsAc network circuit arrangementsStructural vulnerabilityEngineering
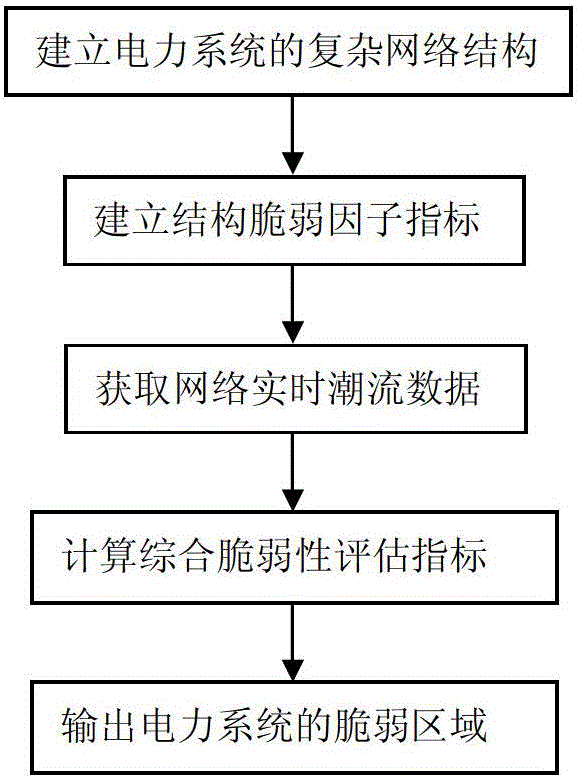
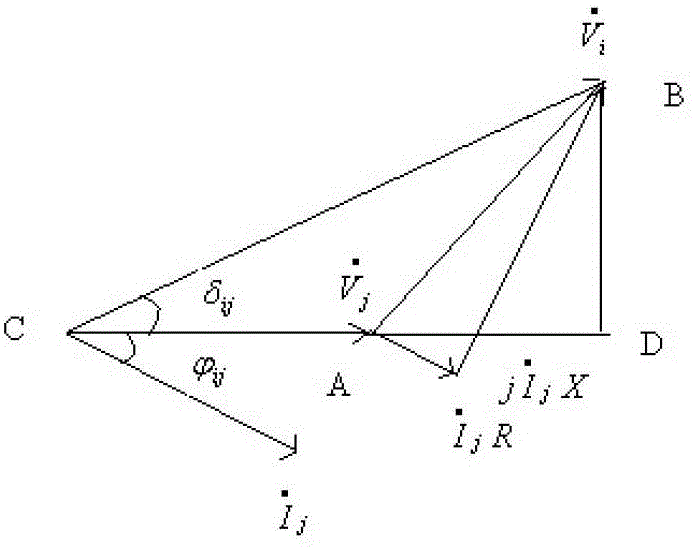
The invention discloses an electric power system vulnerability assessment method, and relates to the field of a power network safety analysis technology. The electric power system frangibility assessment method comprises the following steps: (1), establishing a complex network structure of an electric power system; (2), establishing a structure vulnerability factor indicator through electrical betweenness in the complex networks structure; (3), obtaining network real-time trend data through a static energy function method; (4), calculating a state vulnerability factor, and calculating to obtain an integrated vulnerability assessment indicator through combination with a structural vulnerability factor in step (2); and (5), outputting a vulnerable area of the electric power system. According to the invention, since the electric power system vulnerability assessment method analyzes vulnerable links which may exist in the electric power system from a global perspective, the vulnerable area in the operation of the electric power system can be comprehensively, accurately and effectively determined, the defects of a conventional single one-sided electric power system vulnerability assessment method and the like can be made up for, emphases are provided for prevention and control of safe operation of the electric power system, and collapse of the electric power system, caused by disturbance or accidents, is effectively prevented.
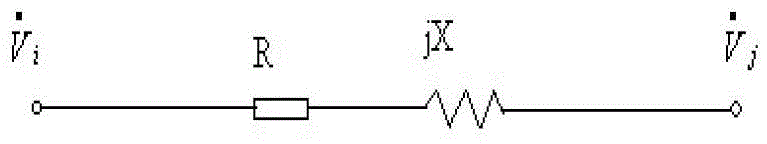
Owner:ELECTRIC POWER SCHEDULING CONTROL CENT OF GUIZHOU POWER GRID CO LTD +1
System and method for assessing risk to a collection of information resources
InactiveUS8020210B2Improve securityMemory loss protectionError detection/correctionInformation resourceVulnerability factor
A system and method for assessing the risk to information resources that may include the generation and / or use of a security risk index. The security risk index may represent the security of information resources. The security risk index may be based on at least one factor. The at least one factor may be individually quantified. The at least one factor may include a threat factor associated with a rate or frequency of security events that threaten the security of the information resources, a vulnerability factor associated with a likelihood of a security event breaching the security of the information resources, an impact factor associated with an expected cost of a breach of the security of the information resources, or another type of factor. The security risk index of a subset of information resources including at least one resource may enable various comparisons and observations with respect to the security of the subset of information resources. The security risk index may be updated for a variety of reasons, such as, to be kept current, or for another reason.


Owner:VERIZON PATENT & LICENSING INC
Multi-dimensional comprehensive index-based power grid vulnerability evaluation method
ActiveCN107193274AGuaranteed uptimeHigh riskProgramme controlElectric testing/monitoringElectric power systemControl system
The present invention relates to a multi-dimensional comprehensive index-based power grid vulnerability evaluation method and belongs to the power system intelligent analysis and control technical field. The multi-dimensional comprehensive index-based power grid vulnerability evaluation method is characterized in that multi-dimensional comprehensive indexes for power grid vulnerability evaluation are built; and power grid vulnerability is evaluated from three aspects, namely, equipment vulnerability evaluation, network vulnerability evaluation and operation vulnerability evaluation. Adjustment and control operation personnel can realize the key monitoring of power grid vulnerable equipment or power grid vulnerable weak links through the visualized power flow diagram of a local dispatching control system, and therefore, the adjustment and control operation personnel can be facilitated to timely process vulnerability factors that may affect the safety of a power grid.


Owner:POWER DISPATCHING CONTROL CENT OF GUANGDONG POWER GRID CO LTD +1
Power communication network vulnerability evaluation and routing optimization method
ActiveCN106789190AImprove accuracyComprehensive performance of the size of the vulnerabilityData switching networksVulnerability factorVulnerability evaluation
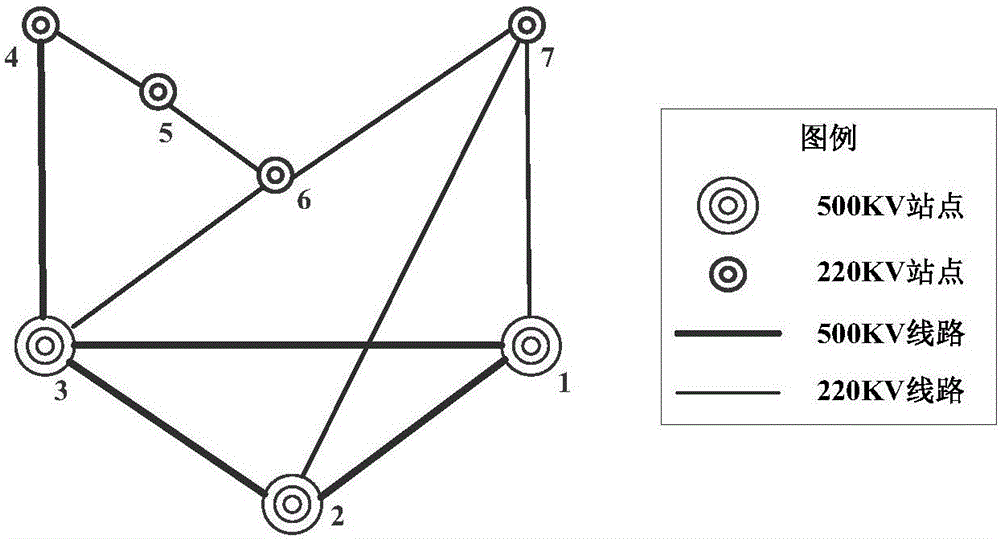
The invention relates to a power communication network vulnerability evaluation and routing optimization method, and belongs to the technical field of power communications. The method comprises the following steps: modeling a network topology of a power communication network, and defining the power communication network as a weighted undirected network; establishing a vulnerability evaluation model of a node and a side according to a topology vulnerability factor, a business vulnerability factor and an equipment vulnerability influencing the vulnerability of the node and the side, and evaluating the vulnerability of the power communication network according to the vulnerability evaluation model. The factors influencing the vulnerability of the node and the side are summarized as three factors of topology vulnerability, the business vulnerability and the equipment vulnerability, and a comprehensive vulnerability index is obtained according to the relation of above mentioned three factors, thereby comprehensively displaying the vulnerability size of the node and the side, and improving the vulnerability evaluation accuracy of the power communication network.
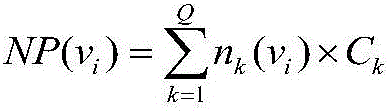
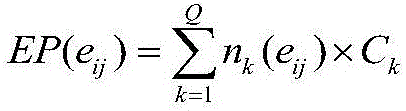
Owner:STATE GRID HENAN INFORMATION & TELECOMM CO +1
Method, apparatus and program storage device for providing automated tracking of security vulnerabilities
InactiveUS8136163B2Memory loss protectionUnauthorized memory use protectionVulnerability factorOperating system
A method, apparatus and program storage device for providing automated tracking of security vulnerabilities is disclosed. Security problems are reported, aged and tracked. A time to fix the vulnerability identified by the vulnerability assessment of the system is based on the determined vulnerability score. The vulnerability factor is based upon consideration of a plurality of identified parameters.


Owner:INT BUSINESS MASCH CORP
Reducing data loss in a computing storage environment
InactiveUS20140258658A1Reduce data lossInput/output to record carriersError detection/correctionVulnerability factorData loss
For reducing data loss by a processor device in a computing storage environment, data blocks are prioritized for creating an N number of additional secondary copies of data using a vulnerability factor for identifying those of the data blocks having a probability of failure. The data blocks include at least a primary copy and a secondary copy of the data.


Owner:IBM CORP
SCADA system information security risk assessment method and system
ActiveCN108833416AAccurate risk assessment resultsResourcesData switching networksSCADAVulnerability factor
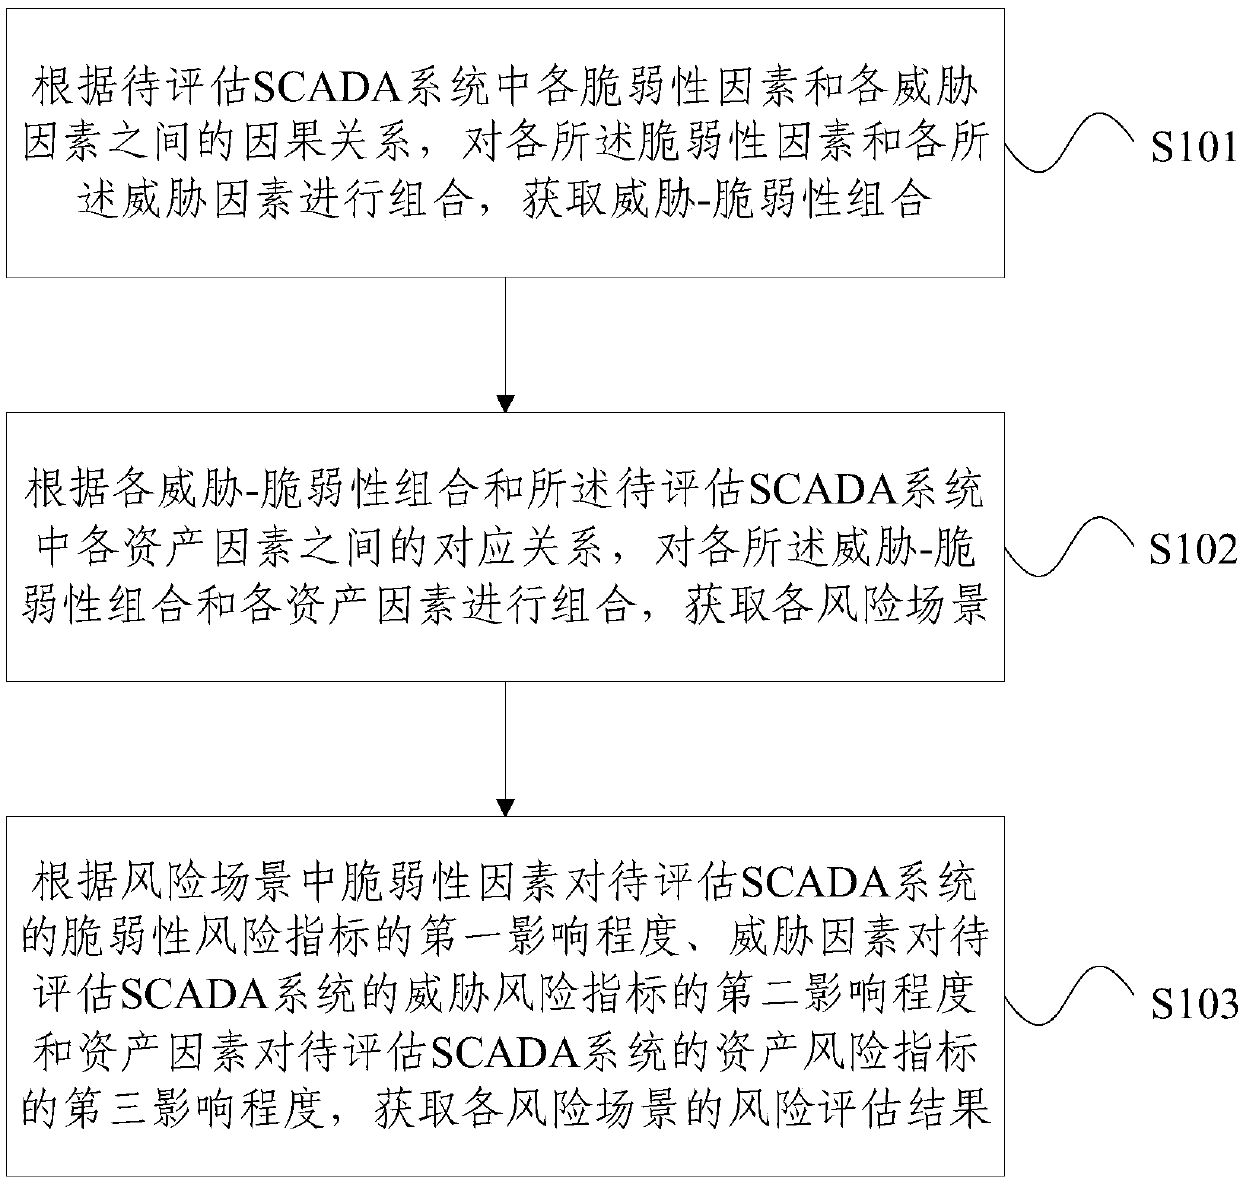
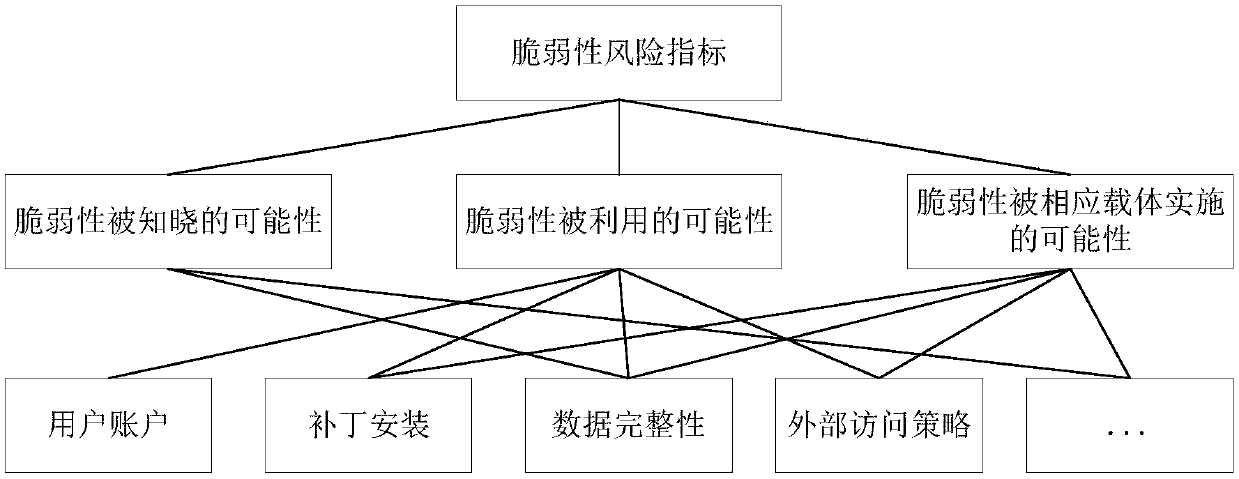
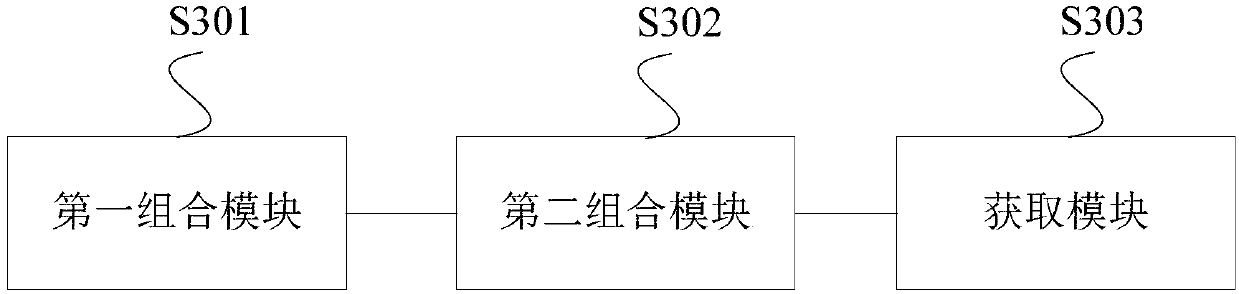
The invention provides an SCADA system information security risk assessment method and system. The method includes the following steps: according to a causal relationship between each vulnerability factor and each threat factor in an SCADA system to be assessed, combining each vulnerability factor and each threat factor to obtain threat-vulnerability combinations; according to a corresponding relationship between each threat-vulnerability combination and each asset factor in the SCADA system to be evaluated, combining each threat-vulnerability combination and each asset factor to obtain each risk scenario; and according to the first influence degree of the vulnerability factors on a vulnerability risk indicator of the SCADA system to be assessed in each risk scenario, the second influencedegree of the threat factors on a threat risk indicator, and the third influence degree of the asset factors on an asset risk indicator, obtaining risk assessment results of the risk scenarios. According to the scheme of the invention, the risk assessment results can be quantitatively obtained, and thus the risk assessment results can be more accurate.
Owner:BEIJING MUNICIPAL INST OF LABOUR PROTECTION
DDoS attack situation early warning method based on dynamic threshold and server
ActiveCN110474878AReal-time warningAccurate identificationNeural architecturesTransmissionNetwork packetData mining
The embodiment of the invention provides a DDoS attack situation early warning method based on a dynamic threshold and a server, and relates to the technical field of DDoS attack detection. The methodcomprises the following steps: generating an IP data packet statistical characteristic time sequence, and modeling the IP data packet statistical characteristic time sequence by using an LSTM neuralnetwork prediction model to obtain an LSTM prediction model; predicting the to-be-tested network flow of the target area by adopting an LSTM prediction model, calculating a threshold value and a threshold value tolerance of the target area according to a prediction result and the network security vulnerability factor, and dividing a plurality of early warning levels; and for the network traffic ofthe target area at the target moment, generating a target IP data packet statistical feature, and then identifying a DDoS attack and determining an early warning level of the to-be-tested network traffic. The DDoS attack early warning method and the device can improve the DDoS attack early warning accuracy.


Owner:HAINAN UNIVERSITY
Network security assessment method and system
InactiveCN109245944ATroubleshoot technical issues with poor securityData switching networksAssessment methodsVulnerability factor
The present invention discloses a network security assessment method. The method includes the steps: obtaining network security risk factors, wherein the risk factors include an asset factor, a vulnerability factor, and a threat factor; establishing a network security assessment model according to the risk factors via a first preset rule; utilizing the network security assessment model to obtain evaluation values of the risk factors; obtaining credibility degrees of the risk factors according to a second preset rule; obtaining a network security evaluation value according to the evaluation values of the risk factors and the credibility degrees of the risk factors, wherein the network security assessment values are obtained by multiplying the evaluation values of the risk factors by the reliability degrees of the risk factors. The invention also provides a network security assessment system implementing the above method. The method and system solve the technical problem that the security defense technology in the related art has poor network security because the action is taken after an event and a possible network attack event cannot be predicted.
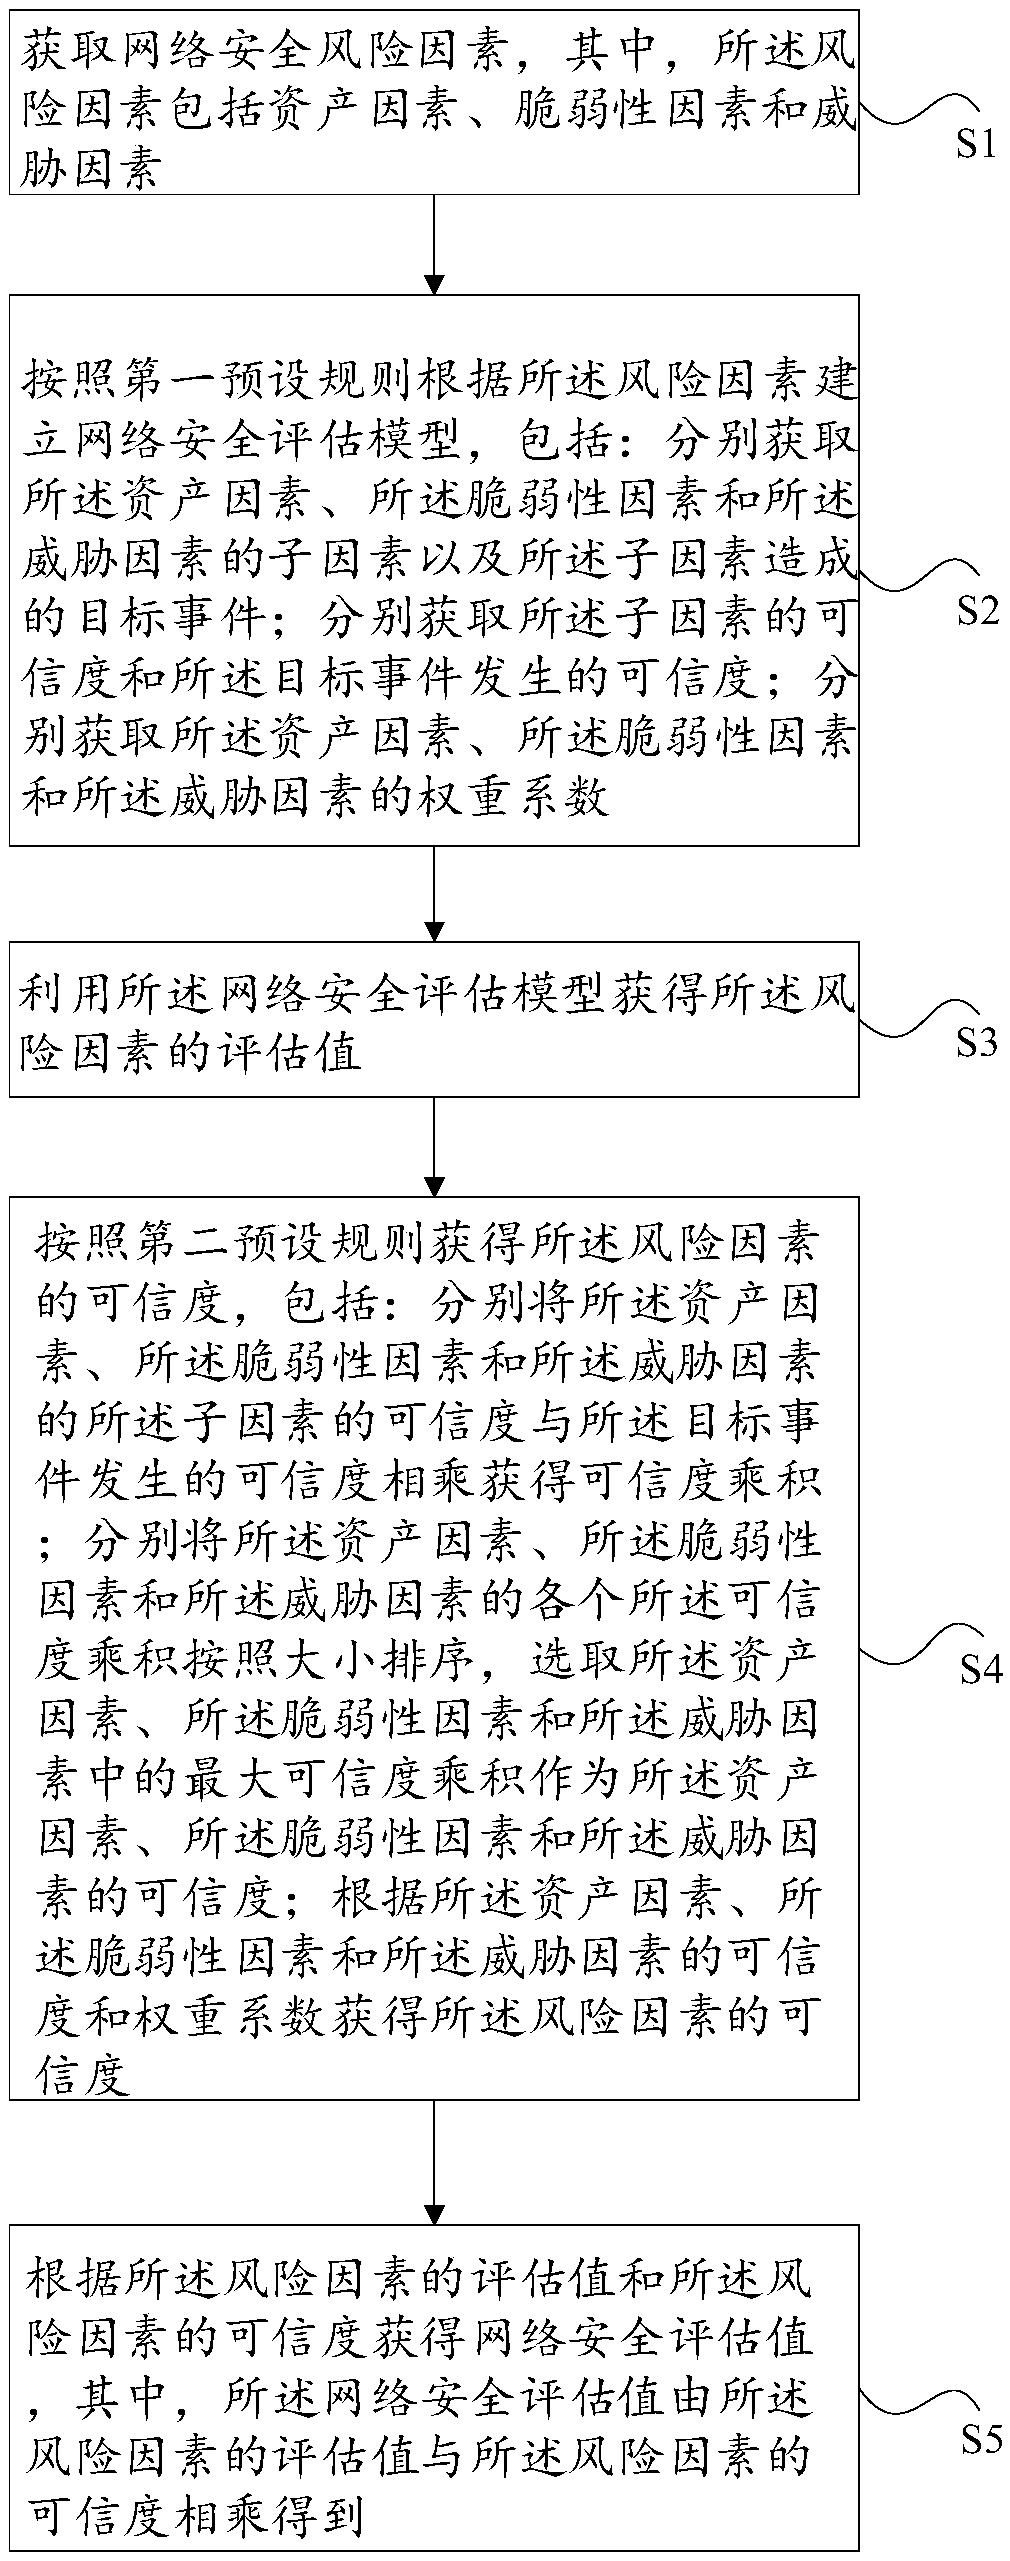
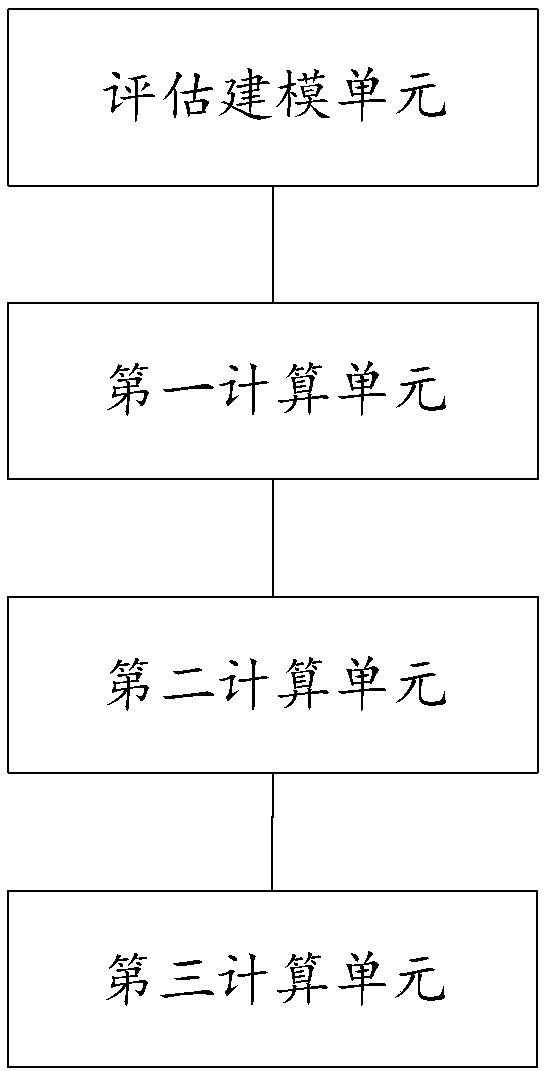
Owner:SOUTHWEST PETROLEUM UNIV
Method for identifying and optimizing fragile line of electric-gas coupling system
ActiveCN110096764AQuantitative determination of vulnerability impactsEasy to monitorDesign optimisation/simulationSpecial data processing applicationsElectricityPower flow
The invention discloses a method for identifying and optimizing a fragile line of an electric-gas coupling system. The method includes inputting original data, establishing an electric-gas coupling system optimization model, and processing to obtain initial operation state of coupling system; turning off the output power of each gas source of the natural gas network, calculating the gas source vulnerability, and carrying out weight processing to obtain a line coupling vulnerability factor; extracting a topological structure of the electric network and processing to obtain a line topological vulnerability factor; respectively disconnecting each power grid line to obtain a power flow distribution entropy so as to obtain a line operation vulnerability factor; comprehensively obtaining the comprehensive vulnerability of the lines, sorting according to the descending order, and the lines larger than a set threshold value are the fragile lines; and after the fragile line is identified, the transmission capacity of the fragile lines is improved through the thickened wire. According to invention, fragile line in electricity-gas coupling system can be rapidly identified, monitoring and protection of fragile line are enhanced, and probability of large-area power failure of power system can be effectively prevented.


Owner:ZHEJIANG UNIV
Service routing addressing method for service operation of power communication network
ActiveCN110971525AThe effect of optimizing addressingImprove addressing efficiencyMultiplex system selection arrangementsData switching networksGenetics algorithmsPhysical layer
The invention discloses a service routing addressing method for service operation of a power communication network. Firstly, modeling is carried out on a power communication network; a chromosome coding mode based on priority is adopted; the service running state of the communication network is encoded; decoding is carried out by using a decoding mode corresponding to the code to obtain a servicepath set, then joint analysis is carried out on vulnerability factors of nodes and links in a physical layer, a network topology layer and a service organization layer to obtain a comprehensive vulnerability evaluation index of the power communication network, and an objective function and constraint conditions are set according to the comprehensive vulnerability evaluation index of the power communication network; and finally, the set target function is taken as a target optimization function of a genetic algorithm, the service route is optimized by adopting the genetic algorithm according tothe constraint condition, and the service route meeting the condition is selected from the service route set. According to the invention, the addressing efficiency can be improved, and the addressingeffect is improved.


Owner:WUHAN UNIV +4
Method for accelerating soft error resistance test of multi-core CPUs (central processing units)
InactiveCN102541738APromote generationGenerate flexibleSoftware testing/debuggingCode synthesisTested time
The invention discloses a method for accelerating soft error resistance test of multi-core CPUs (central processing units), which includes steps: acquiring a parsing program of a CPU, using the parsing program to analyze a standard test case of the multi-core CPU to obtain a basic parameter of the standard test case, analyzing the basic parameter to set up the corresponding relation between the basic parameter and an architectural vulnerability factor of the multi-core CPU, compiling a code synthesis program which uses the basic parameter as input according to the corresponding relation between the basic parameter and the architectural vulnerability factor of the multi-core CPU, running the code synthesis program, and adjusting the basic parameter to obtain a parallel output program which is used as the test case of the soft error resistance test of multi-core CPUs. The method for accelerating soft error resistance test of multi-core CPUs has the advantages of quickness in the test process and short test time, so that test cost is greatly reduced.


Owner:HUAZHONG UNIV OF SCI & TECH
Urban lifeline pipeline operation risk assessment method and device and electronic equipment
PendingCN113807655AAvoid wastingAccurate assessmentPipeline systemsResourcesRisk levelConstruction engineering
The invention provides an urban lifeline pipeline operation risk assessment method and device and electronic equipment. The method comprises the steps of carrying out the analysis based on the own attribute of each lifeline pipeline in a lifeline system, the external disaster interference of the lifeline system, and the coupling relation between the pipelines in the lifeline system, and obtaining the failure possibility of the lifeline pipelines; carrying out vulnerability analysis on a disaster-bearing body based on the vulnerability factors related to the disaster-bearing body to obtain the vulnerability of the disaster-bearing body; analyzing early-stage prevention preparation, monitoring and rescue treatment of the urban emergency management department on emergencies, and obtaining the emergency management level of the urban emergency management department; based on the lifeline pipeline failure possibility, the disaster-bearing body vulnerability and the emergency management level, comprehensively calculating an analysis result; and based on the analysis result, dividing risk levels, and proposing lifeline pipeline protection measure suggestions. According to the invention, the risk of the lifeline pipelines can be systematically analyzed, a manager can make a protection strategy for risk pipelines, and the waste of public security resources is avoided.


Owner:BEIJING INSTITUTE OF TECHNOLOGYGY
Method for detecting and locating vulnerable links in power communication networks
The invention discloses a method for detecting and locating vulnerable links in power communication networks. According to the invention, a structural vulnerability factor and a service vulnerabilityfactor are analyzed respectively according to structural characteristics of a power communication network and characteristics of a power service; the two vulnerability factors are combined; the network is analyzed and evaluated by considering the vulnerability of a node itself and the vulnerability of multi-level neighbor nodes; in a power service importance assessment, a damping coefficient is set to correct the evaluation value of the end-to-end service importance, that is to say, in the end-to-end service, if multiple services of the same type exist, the importance of each service is improved; the impact of the internal instability of the network on the vulnerability and the impact of the network traffic transmission on the vulnerability are analyzed by using a triangular module operator integrated network structure and the vulnerability assessment of the service; the vulnerability of the node itself and the contribution of the neighbor node vulnerability are considered. According to the invention, the problem that most of the current algorithms are considered from a single aspect is solved.


Owner:SICHUAN UNIV
Method and system for reducing dynamic redundant multithreading performance and power consumption overhead
ActiveCN103699458AImprove forecast accuracyReduce running timeRedundant operation error correctionProcessor registerParallel computing


Owner:INST OF COMPUTING TECH CHINESE ACAD OF SCI
Performance-aware and reliability-aware data placement for n-level heterogeneous memory systems
Techniques for selecting one of a plurality of heterogeneous memory units for placement of blocks of data (e.g., memory pages), based on both reliability and performance, are disclosed. A “cost” for each data block / memory unit combination is determined, based on the frequency of access of the data block, the latency of the memory unit, and, optionally, an architectural vulnerability factor (which represents the level of exposure of a particular memory data value to memory faults such as bit flips). A memory unit is selected for the data block for which the determined cost is the lowest, out of all memory units considered, and the data block is placed into that memory unit.


Owner:ADVANCED MICRO DEVICES INC
Method and system for predicting loss of rainstorm disaster and medium
The invention discloses a rainstorm disaster loss prediction method and system and a medium, and belongs to the technical field of natural disaster loss prediction. Comprising the following steps: acquiring disaster-inducing factors causing rainstorm disasters, disaster-pregnancy environmental factors breeding the rainstorm disasters and factors reflecting exposure and vulnerability of disaster-bearing bodies in the rainstorm disasters; through Min-Max standardization, scale differences of disaster-inducing factors, disaster-pregnancy environment factors and exposure and vulnerability factors are eliminated; adjusting the sequence of the disaster-inducing factors, the disaster-pregnancy environment factors and the exposure and vulnerability factors by using a random sampling mode; integrating a plurality of machine learning algorithms after hyper-parameter combination optimization, and constructing a multi-model rainstorm disaster loss prediction system; inputting the processed disaster-inducing factors, disaster-pregnancy environment factors and exposure and vulnerability factors into a multi-model prediction system, and outputting economic loss of the rainstorm disaster; according to the method, the economic loss of the rainstorm disaster is effectively predicted.

Owner:HANGZHOU NORMAL UNIVERSITY
Password enhancement method based on vulnerability factor analysis
ActiveCN108470124AOvercoming the disadvantages of generative constraintsAccurate portrayalDigital data authenticationFeature vectorPassword
The invention discloses a password enhancement method based on vulnerability factor analysis. The method comprises the steps of composing vulnerability feature vectors through a characteristic description, a characteristic matching algorithm and a characteristic modification strategy set, and combining the plurality of vulnerability feature vectors to form a password vulnerability feature library;when registering or changing a password in a service or a website, acquiring a password text and matching the password text with the vulnerability feature vectors of the password vulnerability feature library, and analyzing all possible vulnerability factors in the password to generate a vulnerability factor set; and solving an optimal modification position set of the password based on the vulnerability factor set, traversing all positions in the optimal modification position set, and randomly selecting a modification strategy in the modification strategy set at each position for execution tofinally complete password enhancement. The password enhancement method based on vulnerability factor analysis has the characteristics of initiativity for password enhancement, plug and play of the vulnerability feature library, automation of unloading and the like and can effectively defend against various password guess attacks including conventional attack methods.

Owner:EAST CHINA NORMAL UNIVERSITY
Fire optimal escape route planning method and system based on multi-modal fusion algorithm
InactiveCN120108096ANavigational calculation instrumentsSignalling system detailsAlgorithmArtificial intelligence
The invention relates to the technical field of route optimization, in particular to a fire optimal escape route planning method and system based on a multi-modal fusion algorithm, and the method comprises the following steps: obtaining temperature, smoke and oxygen sensor readings and building information data, calculating the multi-source fusion criticality of each position and each moment of a building, obtaining a position time sequence fusion hazard value, and calculating the position time sequence fusion hazard value; and based on the position time sequence fusion hazard value, integrating numerical values of different time points, and establishing a time-varying hazard probability distribution diagram. According to the invention, through real-time acquisition and fusion of temperature, smoke and oxygen sensor readings and building information data, hazard degree dynamic evaluation of each position in a building is realized, a position time sequence fusion hazard value is constructed, and space hazard identification accuracy is effectively improved; thermal damage analysis and long-term fragility factor calculation of beams and columns in the building structure are further combined, and the bearing performance change of the building structure under the thermal action is comprehensively evaluated, so that the risk evaluation is more comprehensive.

Owner:WUXI UNIV
A Single Event Soft Error Vulnerability Identification Method Applicable to Processor System
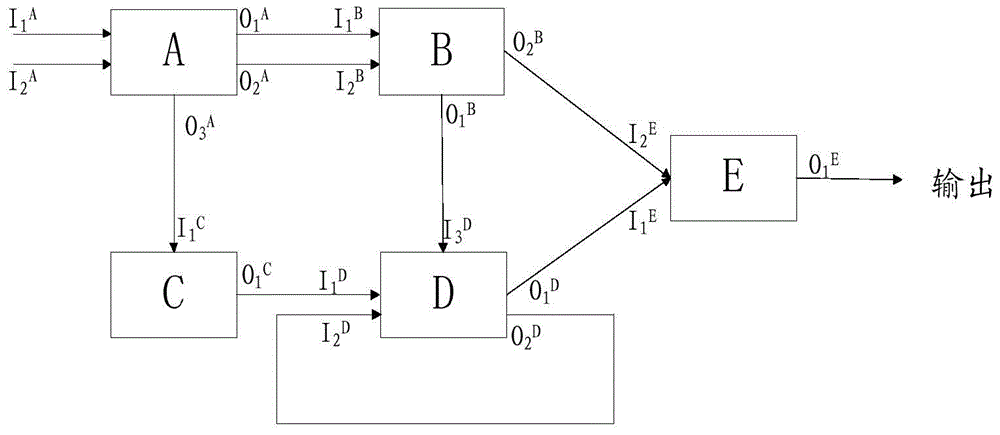
A method applied to recognizing vulnerabilities of single-event soft errors in processor systems includes: based on influences of single-event soft error protective design upon system performance and resources, establishing an importance function module for vulnerability recognition model analytic protection; according to an operating principle of compilation instructions, dividing an element circuit node (a specific function / subfunction module used for pre-compiling codes or instruction sequences) from code level of design, extracting vulnerability factors of the element circuit node from instruction level by compile mapping relation, and performing grade domain division; finally, subjecting uncertainty intervals (gray level intervals) of vulnerability factor grading for the element circuit node to credibility evaluation according to a gray level system theory, and acquiring computation results according to grade credibility sorting. The method has the advantages that the simple vulnerability analysis method for processor systems is provided, system cost and performance loss are reduced on the premise of implementing reliability, and system protection effect is improved.
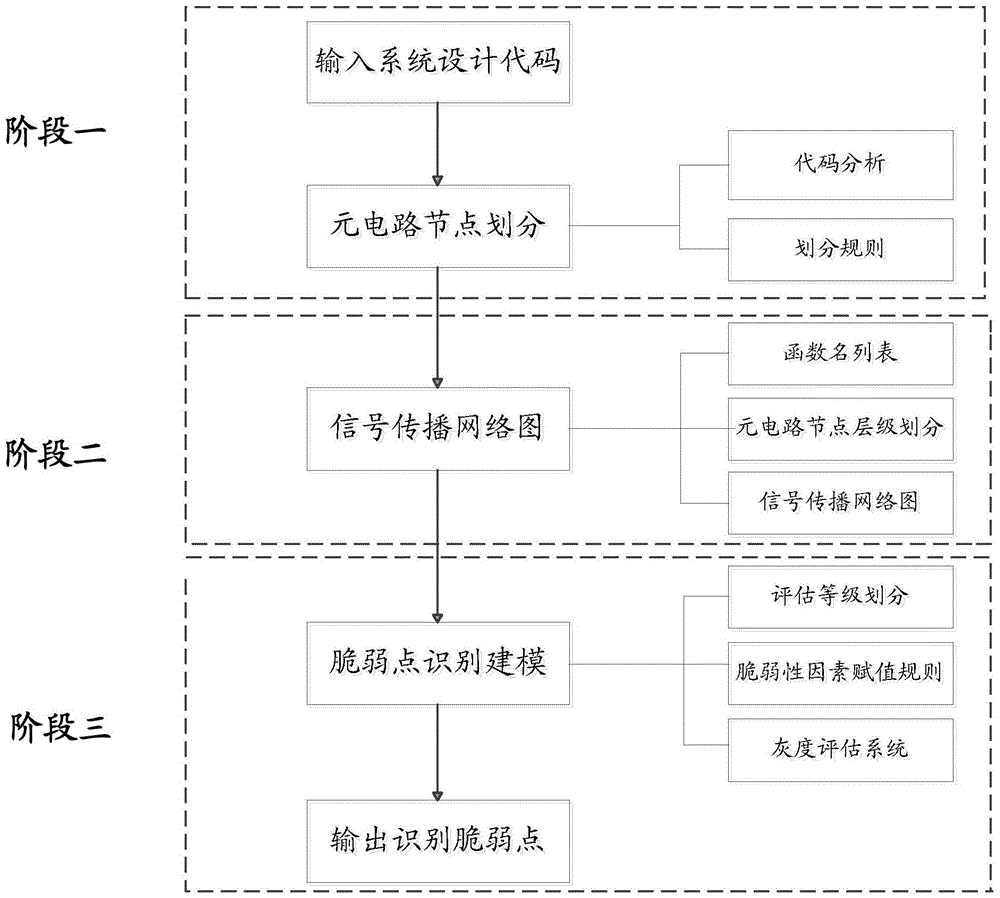
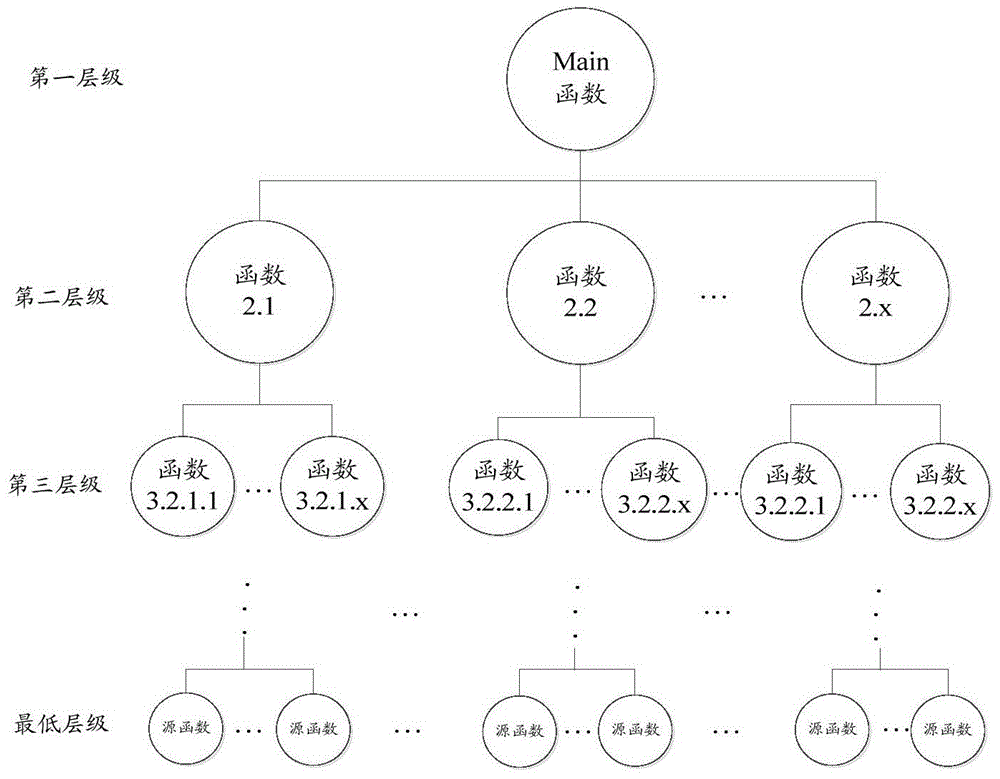
Owner:XIAN INSTITUE OF SPACE RADIO TECH
A graph-based power CPS vulnerability assessment method and system
ActiveCN119130152BData processing applicationsKnowledge representationGraph theoreticDegree (graph theory)
The present application relates to the field of power system application technology, and specifically to a graph-theory-based power CPS vulnerability assessment method and system, the method comprising: constructing an unweighted network topology model of a power CPS network, obtaining each node of the power CPS network, the edges between nodes, and the load voltage data of each node; obtaining the load anomaly of each node of the power CPS network; obtaining the voltage recovery responsiveness of each node of the power CPS network; obtaining the operation robustness of each node of the power CPS network; obtaining each community in the power CPS network and the associated communities of each community; obtaining the voltage mutation time sequence of each node in the power CPS network; obtaining the degree of cascading failure of each community in the power CPS network; obtaining the cascading criticality of each community in the power CPS network; obtaining the power CPS network vulnerability factor, and evaluating the power CPS vulnerability. The present application reduces the risk of damage to the safety of the power system.

Owner:国网黑龙江省电力有限公司绥化供电公司
Method for accelerating soft error resistance test of multi-core CPUs (central processing units)
InactiveCN102541738BPromote generationGenerate flexibleSoftware testing/debuggingCode synthesisTested time
The invention discloses a method for accelerating soft error resistance test of multi-core CPUs (central processing units), which includes steps: acquiring a parsing program of a CPU, using the parsing program to analyze a standard test case of the multi-core CPU to obtain a basic parameter of the standard test case, analyzing the basic parameter to set up the corresponding relation between the basic parameter and an architectural vulnerability factor of the multi-core CPU, compiling a code synthesis program which uses the basic parameter as input according to the corresponding relation between the basic parameter and the architectural vulnerability factor of the multi-core CPU, running the code synthesis program, and adjusting the basic parameter to obtain a parallel output program which is used as the test case of the soft error resistance test of multi-core CPUs. The method for accelerating soft error resistance test of multi-core CPUs has the advantages of quickness in the test process and short test time, so that test cost is greatly reduced.


Owner:HUAZHONG UNIV OF SCI & TECH
Novel power distribution system vulnerability assessment method and system based on dynamic weight
The invention discloses a novel power distribution system vulnerability assessment method and system based on a dynamic weight. The method comprises the following steps: establishing a power distribution system vulnerability assessment index system, and determining an initial weight through an analytic hierarchy process (MSDM-AHP) based on a Muslim diagram; collecting safety monitoring data in real time; updating the weight of each index through a dynamic weight adjustment mechanism based on real-time data: calculating the current threat level of each index, dynamically adjusting the weight when the current threat level exceeds a trigger threshold value, and performing normalization processing; and finally, calculating a comprehensive vulnerability factor through a TOPSIS algorithm by using the obtained dynamic weight, and then calculating a comprehensive risk value based on the vulnerability factor, the asset value and the influence consequence to quantify a network security evaluation result of the novel power distribution system. According to the method, the defects of lag and stiffness of a traditional static evaluation model are overcome, and real-time, self-adaptive and accurate evaluation of the network security state of the novel power distribution system is realized.

Owner:NARI INFORMATION & COMM TECH +4
Detection and location method of vulnerable links in electric power communication network
The invention discloses a method for detecting and locating vulnerable links in a power communication network. According to the structural characteristics of the power communication network and the characteristics of power services, the structural vulnerability factor and the business vulnerability factor are respectively analyzed, and the two vulnerability factors are combined. By considering the node's own vulnerability and multi-level Neighboring node vulnerability is analyzed and evaluated on the network; the damping coefficient is used to modify the evaluation value of the end-to-end business importance in the evaluation of the power business importance, which is equivalent to the end-to-end, if there are multiple services of the same type, The importance of each business has been increased; using the triangular model operator to synthesize the network structure and the vulnerability assessment of the business, it analyzes the impact of the instability within the network on the vulnerability and the impact of the network service transmission on the vulnerability; Considering the vulnerability of the node itself and the contribution of the vulnerability of neighboring nodes; it solves the problem that most current algorithms consider from a single aspect.


Owner:SICHUAN UNIV
Cross-domain cascading failure risk assessment method, system and equipment for power distribution network information physical system and storage medium
The invention discloses a power distribution network cyber-physical system cross-domain cascading failure risk assessment method, system and device and a storage medium, and the method comprises the steps: obtaining a power distribution network cyber-physical system cross-domain cascading failure propagation path, and tracing a fault source from a communication network level in combination with the behavior characteristics of an attacker; establishing a directed attack path model based on the complete evolution chain of the multi-space coupling fault; based on an attack profit-and-loss evaluation criterion, calculating an attack profit-and-loss value of each directed attack path, evaluating a priority sequence of different cross-space cascading failures under an attacker perspective, and establishing a cross-space cascading failure probability prediction model; and calculating a vulnerability factor of each node of the directed attack path model based on an improved attack graph algorithm, traversing a network attack path and synthesizing an accumulated value of the vulnerability factor of each node to obtain a path comprehensive risk coefficient so as to generate a risk level judgment result of the cross-space cascading failure. And an important technical support is provided for improving the network security and the operation toughness of the power system.

Owner:GUIZHOU POWER GRID CO LTD
Chaos testing prioritization using vulnerability factors
Architectures and techniques are described that can determine a vulnerability factor (VF) for a microservice (or another suitable executable instruction unit) of a microservice platform (or another suitable software system or platform). The VF can be indicative of an aggregate vulnerability score of the microservice. The VF can combine an engineering risk score, a code complexity score, and / or a historical record score, each of which can be configurably weighted. A list of the microservices ranked or ordered according to the VF can be used to prioritize chaos testing procedures.


Owner:DELL PROD LP
A method and system for evaluating comprehensive vulnerability of power grid under natural disasters
ActiveCN118799122Bguide runImprove disaster resilienceData processing applicationsNatural disasterPower grid
The present application relates to the field of power grid security technology, and provides a method and system for evaluating the comprehensive vulnerability of power grids under natural disasters. In the method, according to the node failure occurrence probability, node operation state value, node emergency response value, node failure trigger threshold, node vulnerability correction coefficient and their corresponding weight thresholds of each node of the power grid system under the influence of natural disasters, the system failure occurrence probability #imgabs0#, system operation state value #imgabs1#, system emergency response value #imgabs2#, system failure trigger threshold #imgabs3# and system vulnerability correction coefficient #imgabs4# of the power grid system under the influence of natural disasters are determined; then, based on the pre-constructed comprehensive power grid vulnerability assessment model, the comprehensive vulnerability value #imgabs5# of the power grid system under the influence of natural disasters is determined, and combined with the vulnerability adjustment factor #imgabs6# of the power grid system under the influence of natural disasters determined by the vulnerability factors of the power grid system under the influence of natural disasters in advance, the comprehensive vulnerability of the power grid system under the influence of natural disasters is dynamically adjusted.

Owner:CHINA UNIV OF MINING & TECH (BEIJING)
Obstacle removing scheme generation method for removing branches beside overhead electrified line
The invention provides a method for generating an obstacle clearing scheme for clearing branches beside an overhead electrified line, which comprises the following steps of: determining line tree contradiction points on a plurality of electrified lines and a plurality of vulnerability factors corresponding to the line tree contradiction points, and calculating the vulnerability T of each line tree contradiction point according to the vulnerability factors; and constructing an objective function and setting constraint conditions according to the vulnerability T of each line tree contradiction point, and determining the to-be-maintained line tree contradiction point based on the solution of the objective function to generate an obstacle clearing scheme. According to the method, the obstacle clearing scheme comprising the line tree contradictory points of the plurality of electrified lines can be formulated by taking the minimum load loss and obstacle clearing cost as targets, the utilization efficiency of obstacle clearing resources can be effectively improved, and the load loss of the electrified lines is reduced.


Owner:STATE GRID TIANJIN ELECTRIC POWER COMPANY +1
A Method for Identification and Optimization of Vulnerable Lines in Electrical-Pneumatic Coupling System
ActiveCN110096764BQuantitative determination of vulnerability impactsEasy to monitorGeometric CADCAD network environmentThermodynamicsPower flow
The invention discloses a method for identifying and optimizing vulnerable lines of an electric-pneumatic coupling system. Input the original data, establish an optimization model of the electric-pneumatic coupling system, and process to obtain the initial operating state of the coupling system; respectively turn off the output power of each gas source in the natural gas network, calculate the vulnerability of the gas source and perform weight processing to obtain the line coupling vulnerability factor; extract the power The network topology structure processing obtains the line topology vulnerability factor; disconnects each power grid line separately, obtains the power flow distribution entropy, and thus obtains the line operation vulnerability factor; comprehensively obtains the comprehensive vulnerability of the line, and sorts it in order from large to small, greater than The line with the set threshold is the fragile line; after the vulnerable line is identified, the transmission capacity of the vulnerable line can be increased by thickening the wire. The invention can quickly identify the fragile lines in the electric-pneumatic coupling system, strengthen the monitoring and protection of the fragile lines, and can effectively prevent the probability of large-scale power outages in the power system.


Owner:ZHEJIANG UNIV