

Patents
Literature
83 results about "Handover authentication" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
Method and system for handover authentication
ActiveUS20100046467A1Unauthorised/fraudulent call preventionEavesdropping prevention circuitsClient-sideNetwork service
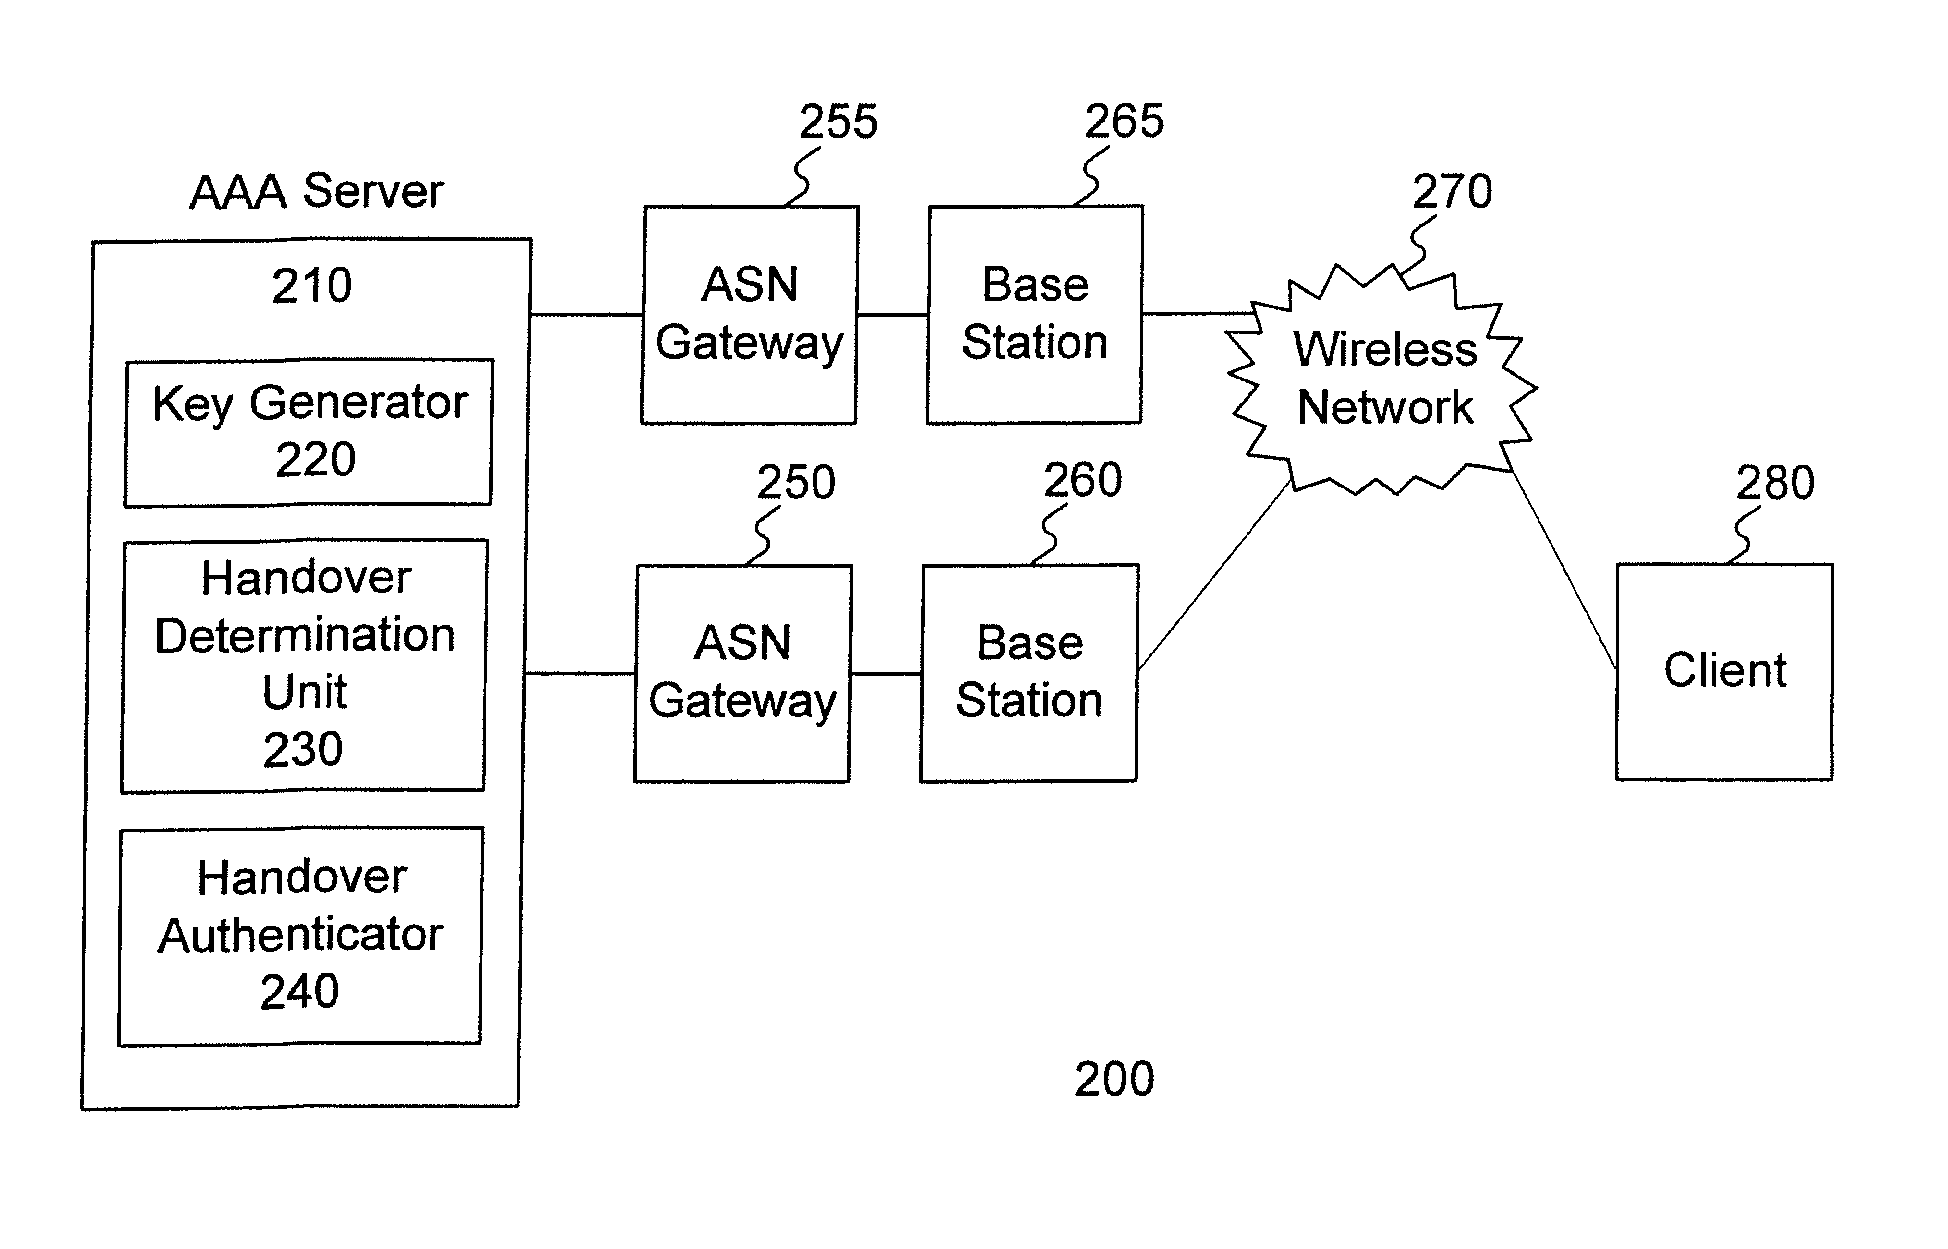
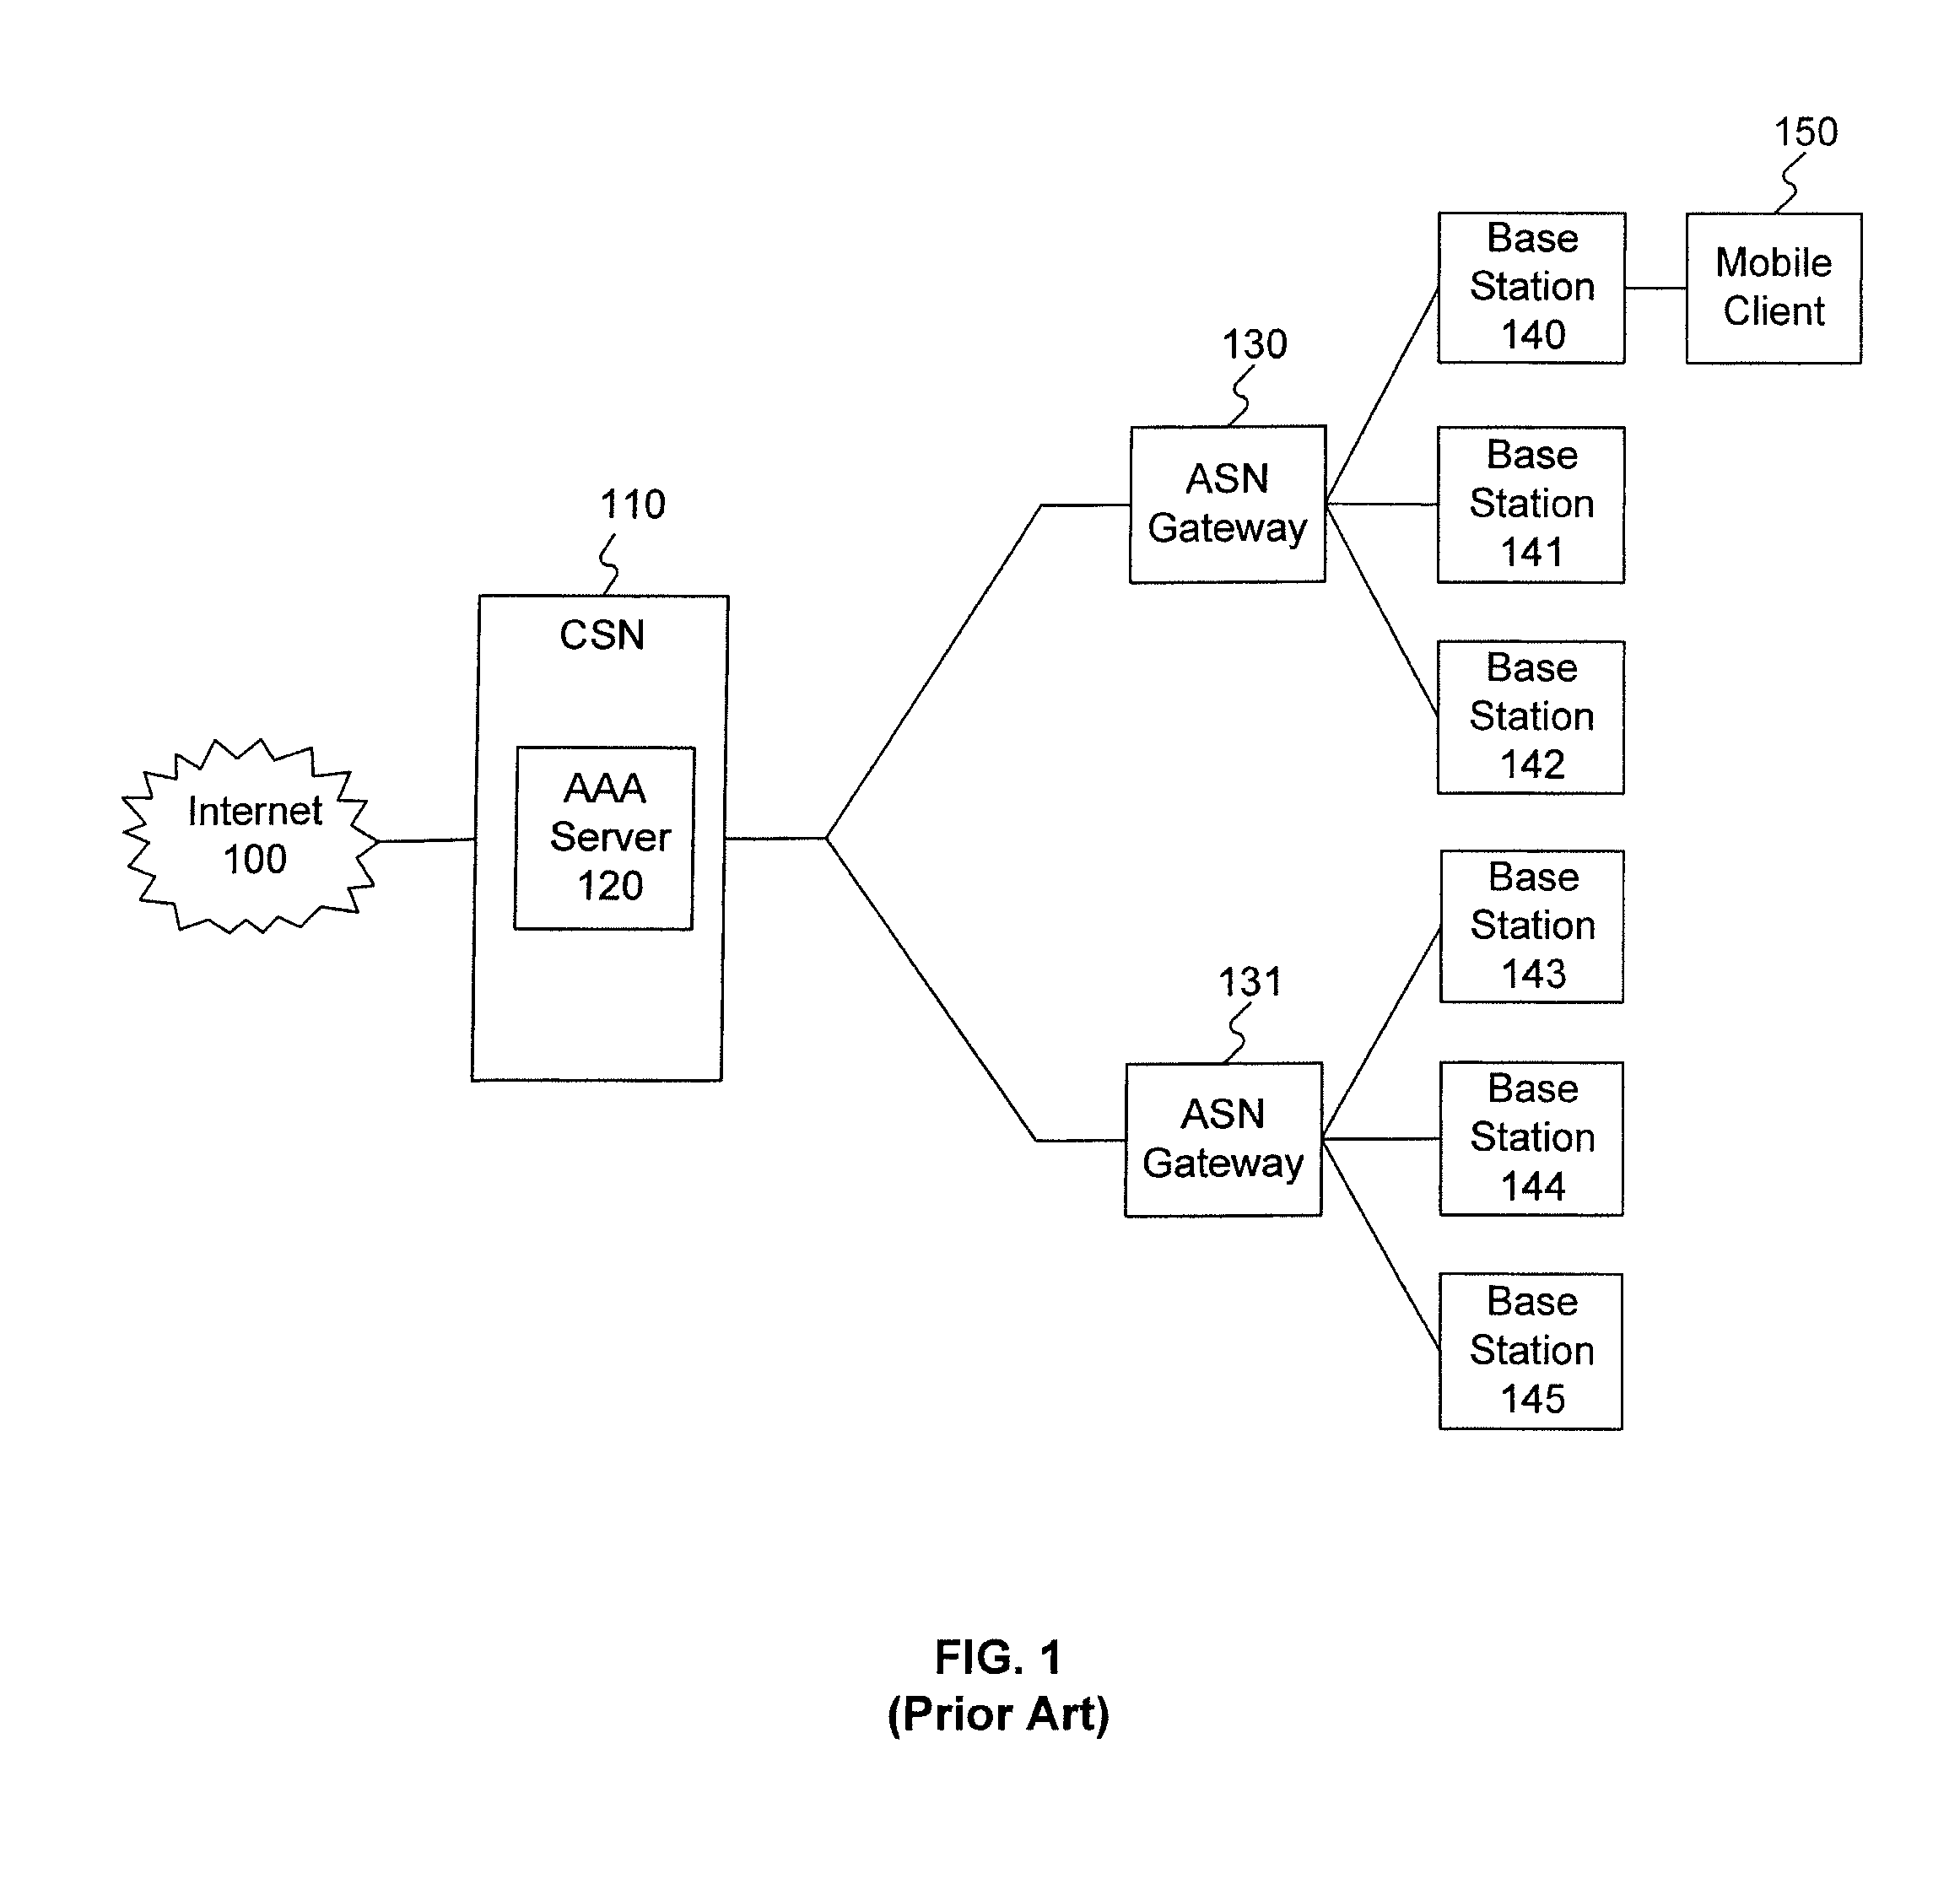
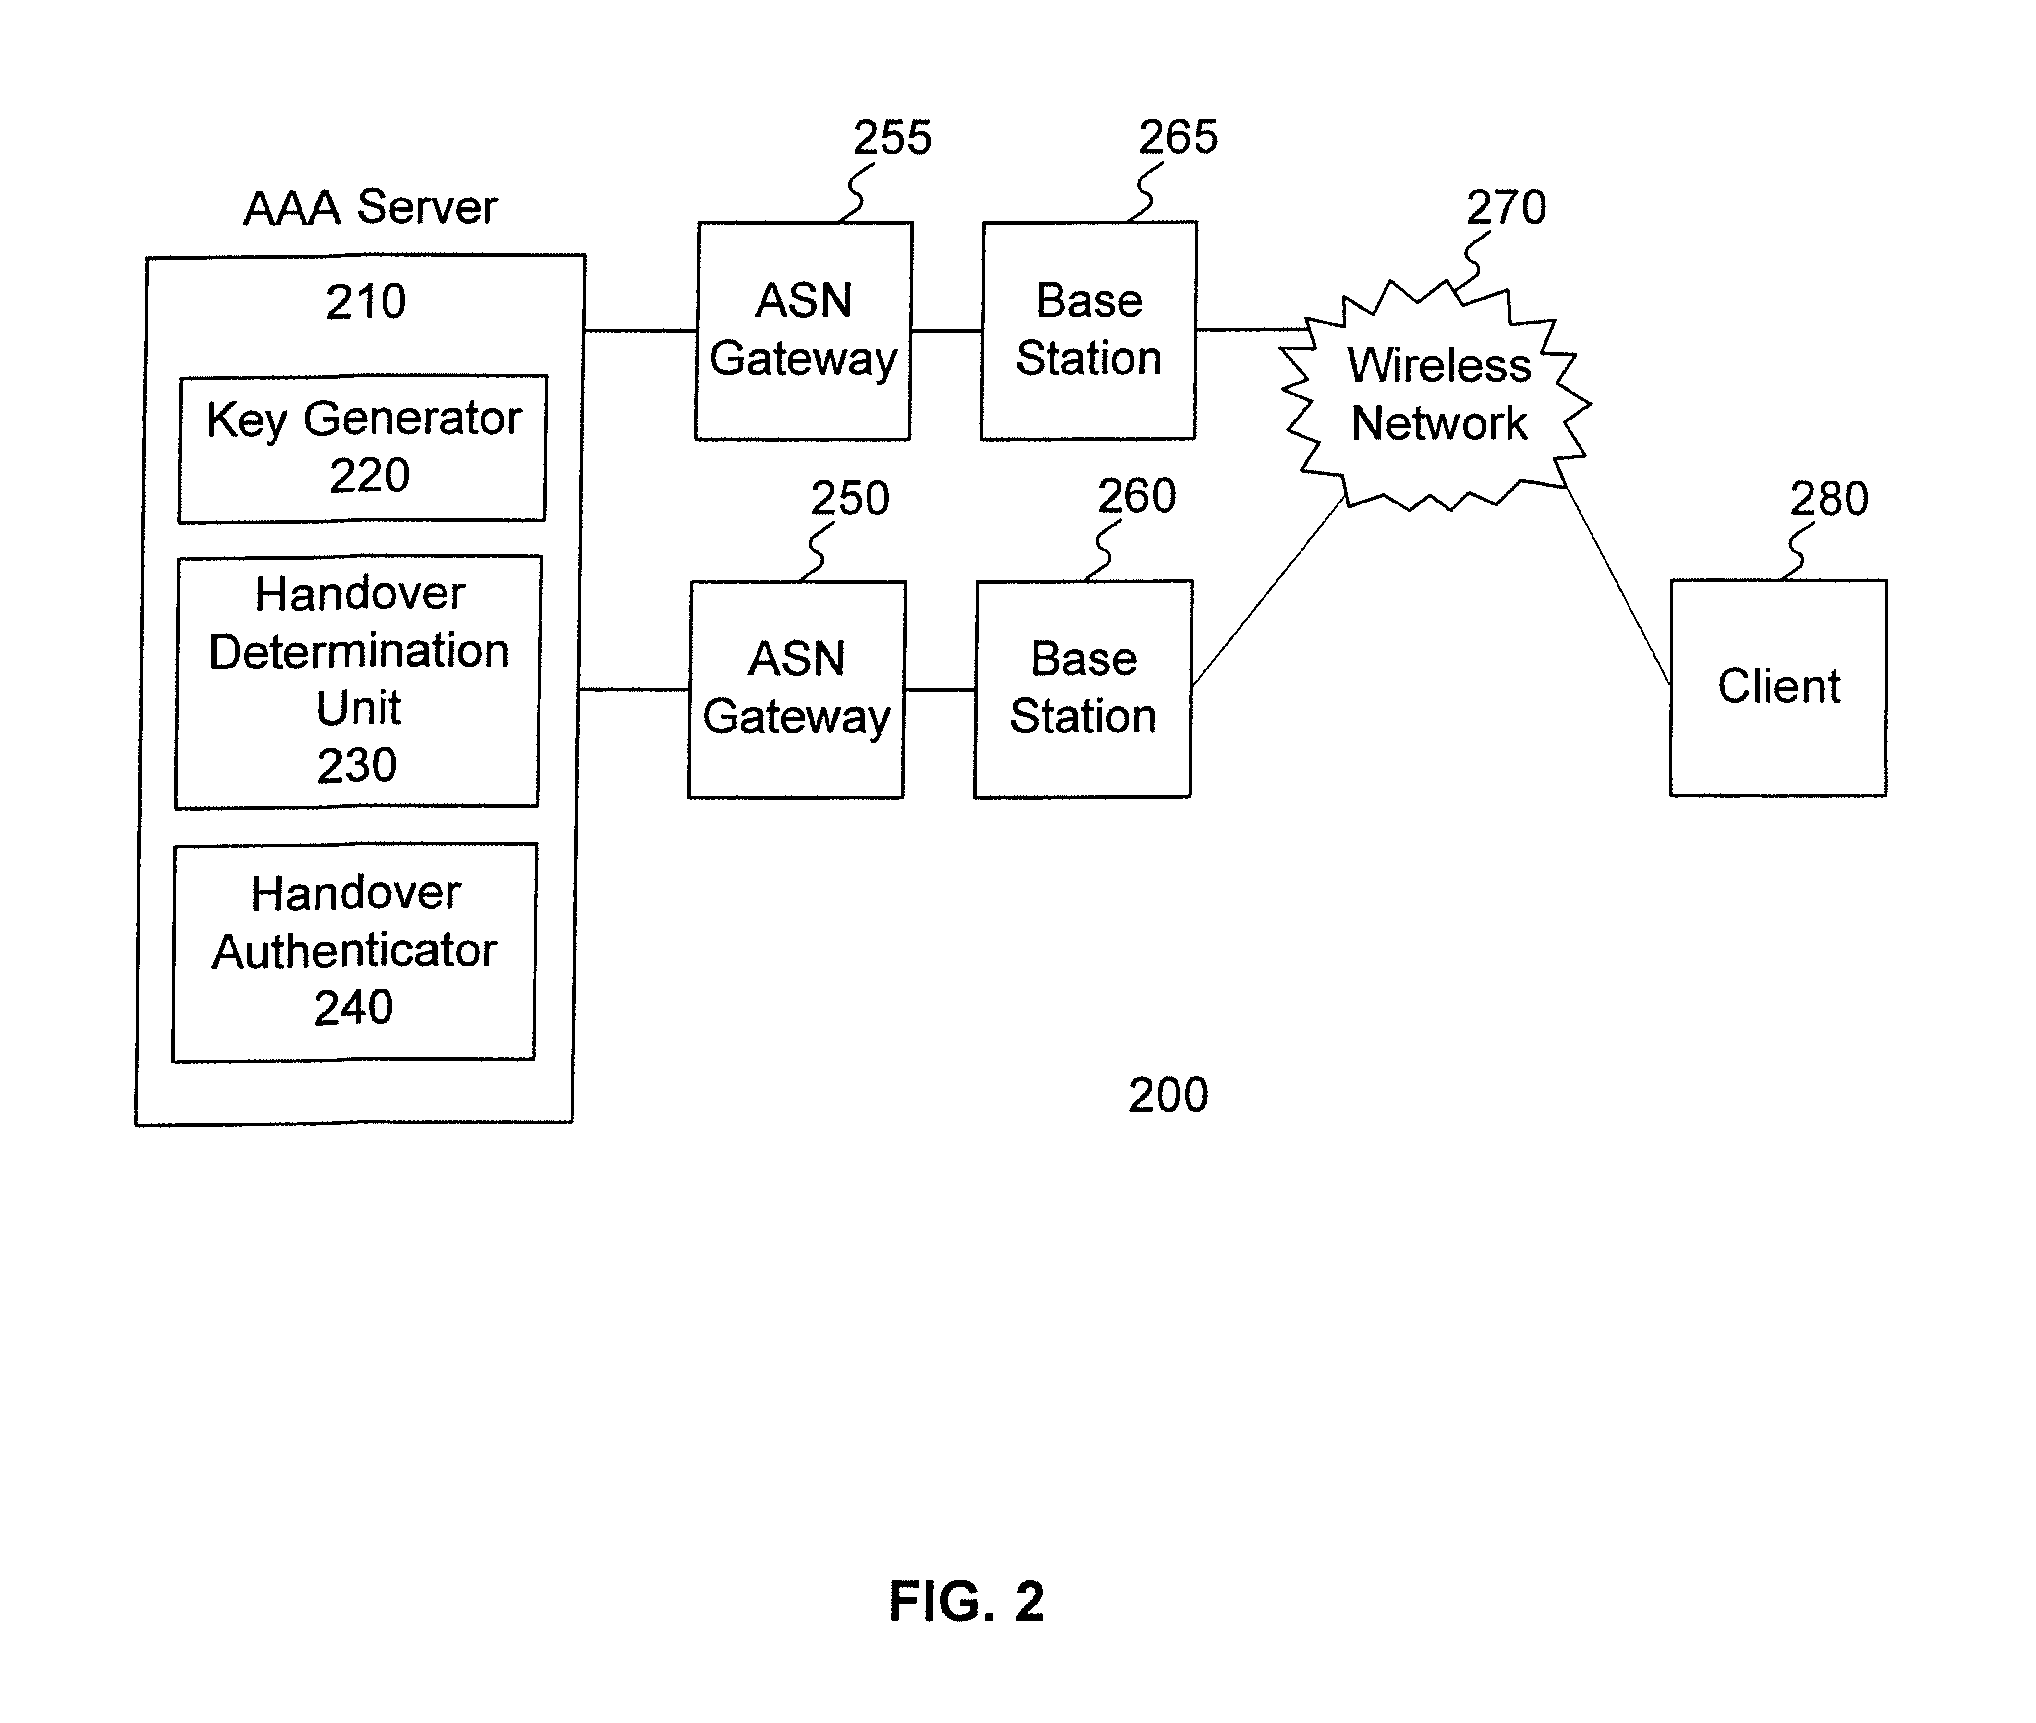
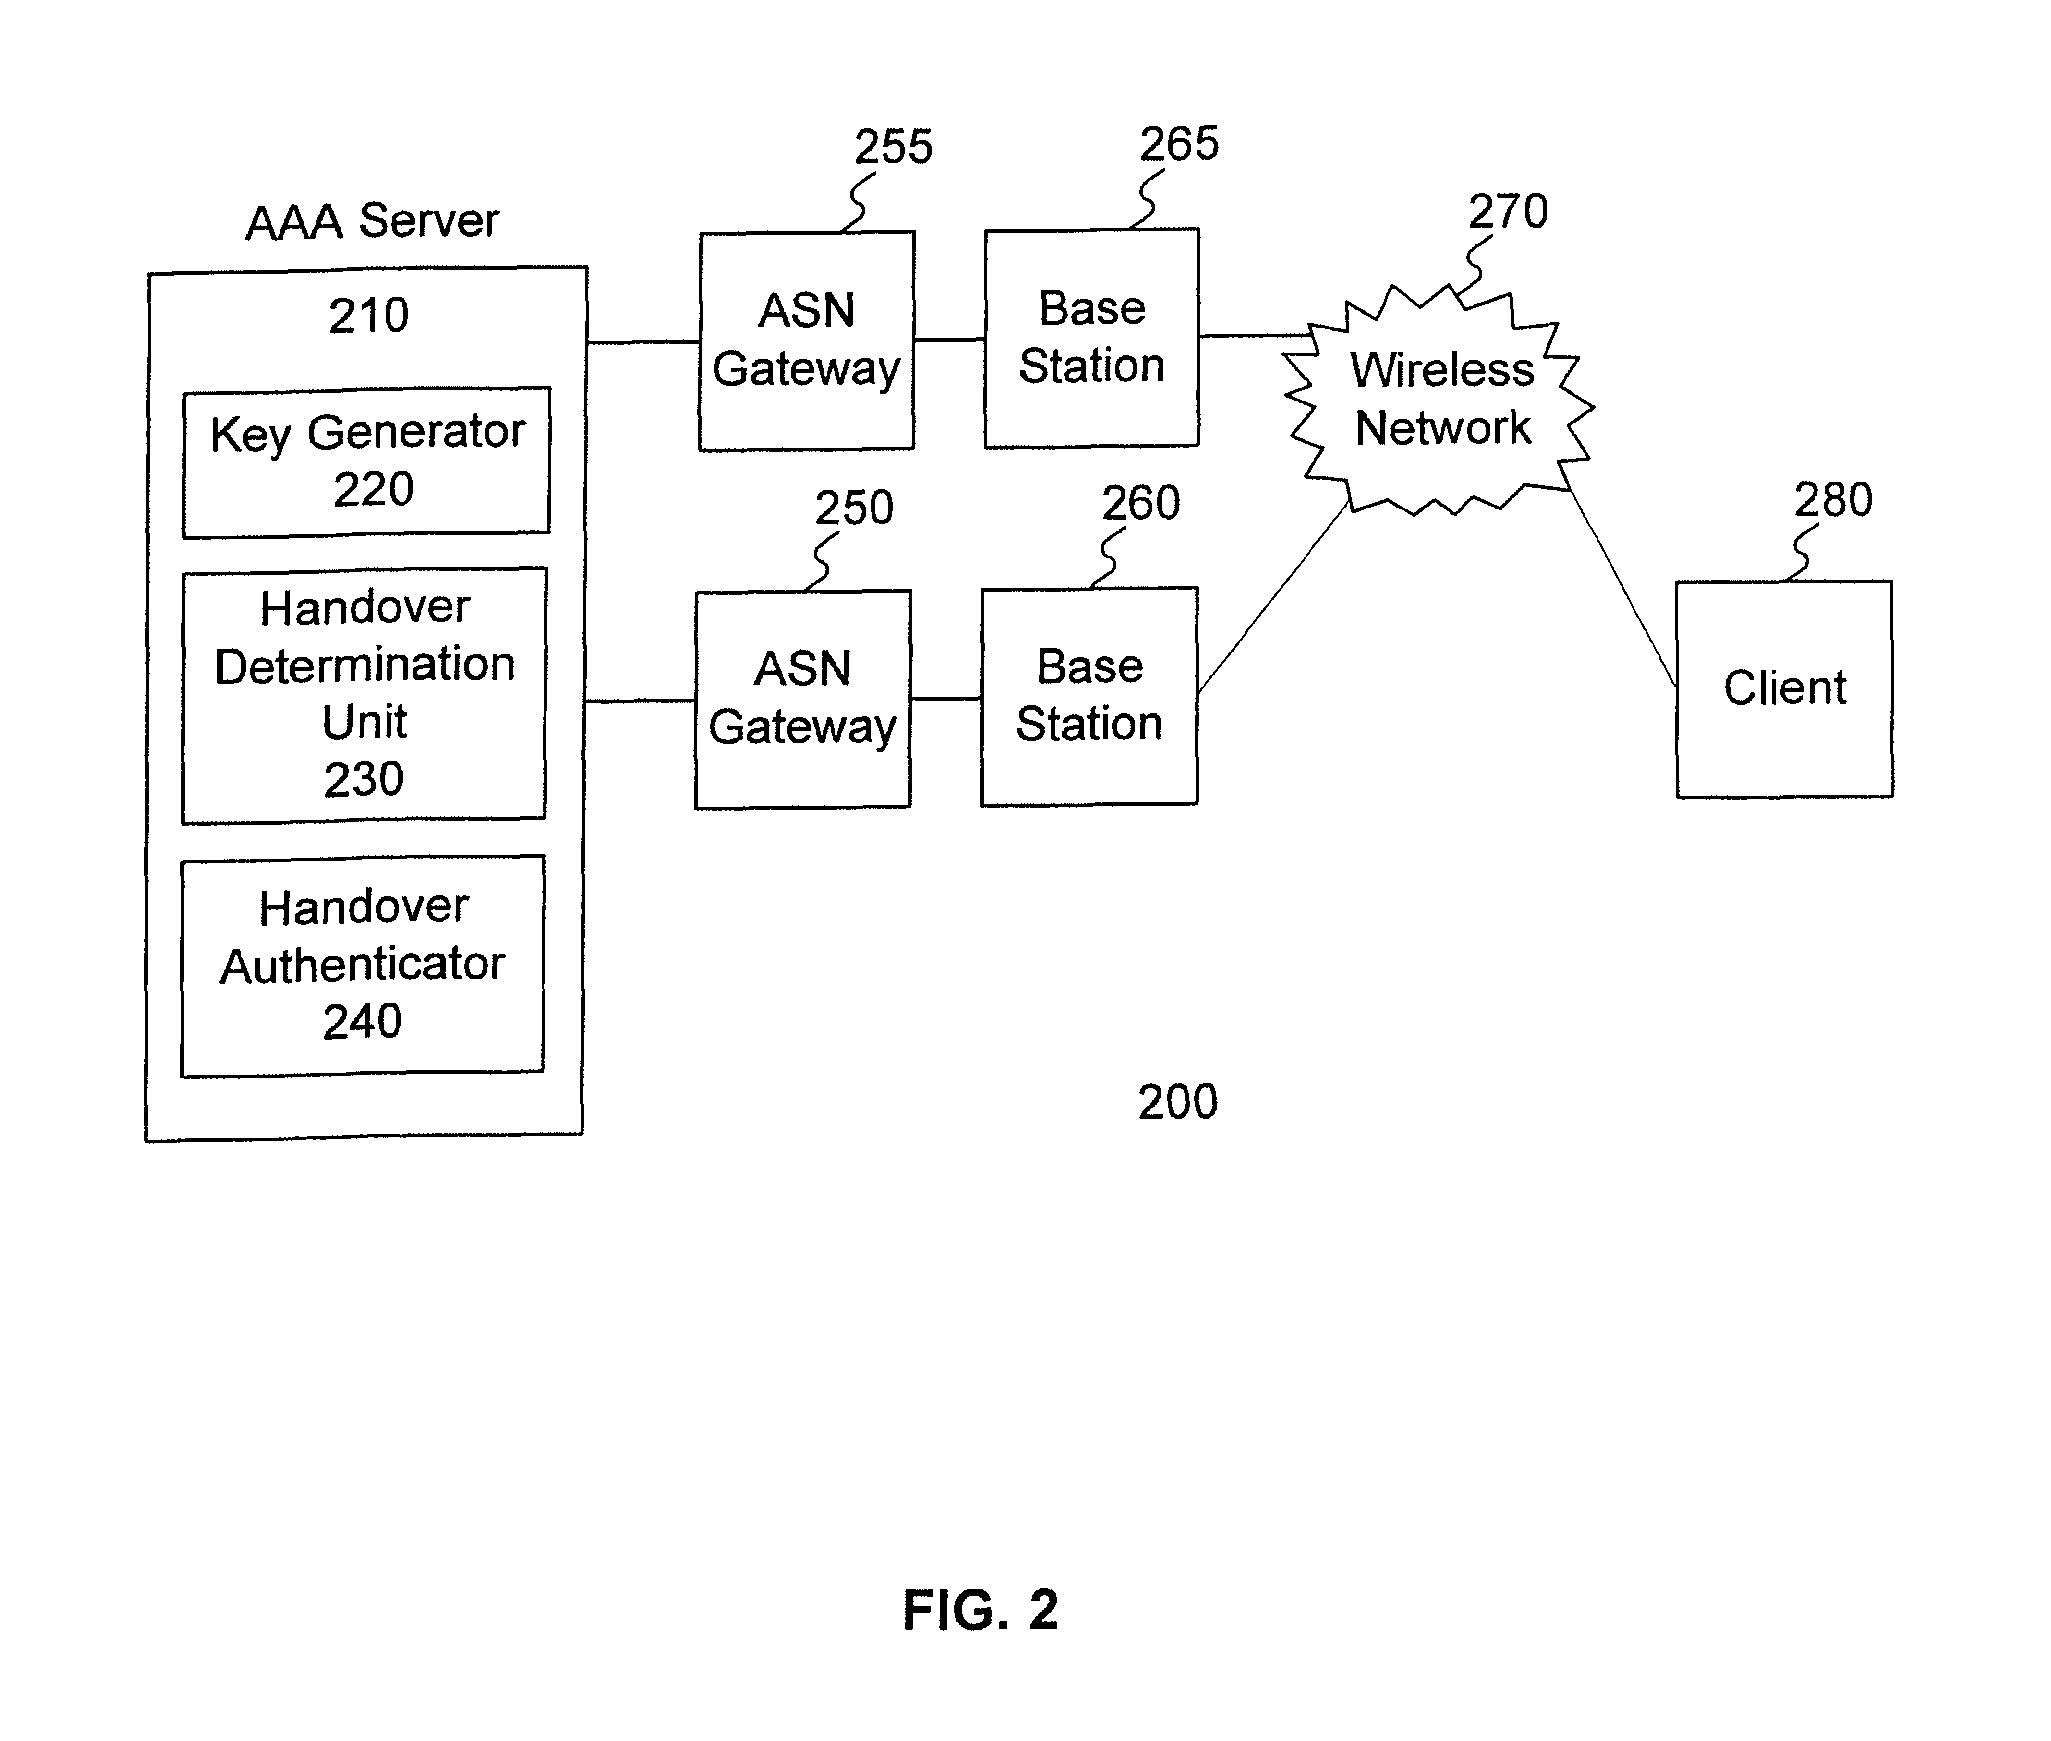
A handover authentication method includes performing, by a wireless network server, a first authentication between a client and the wireless network server via a first network gateway; obtaining first authentication keys for the wireless network server and the client based on the first authentication; determining, by the wireless network server, a need to handover the client from the first network gateway to a second network gateway; deriving, by the wireless network server and from the first authentication keys, a handover authentication key shared by the client and the wireless network server; obtaining, by the wireless network server, second authentication keys for the network server and the client; and serving, by the wireless network server, the client via the second network gateway.
Owner:IND TECH RES INST
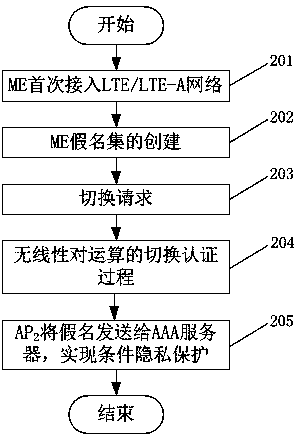
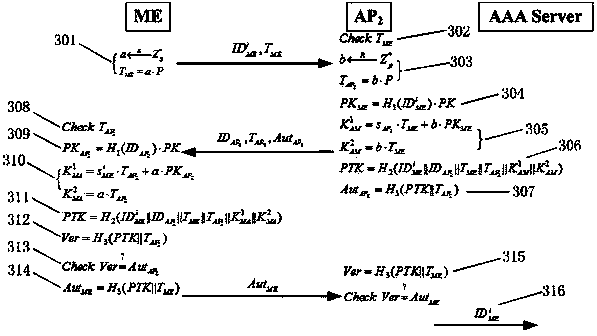
Authentication switching method with privacy protection in LTE (long term evolution)/LTE-A (LTE-advanced) network
InactiveCN103781067ARealize privacy protectionReduce handover authentication delaySecurity arrangementKey exchangeHash function
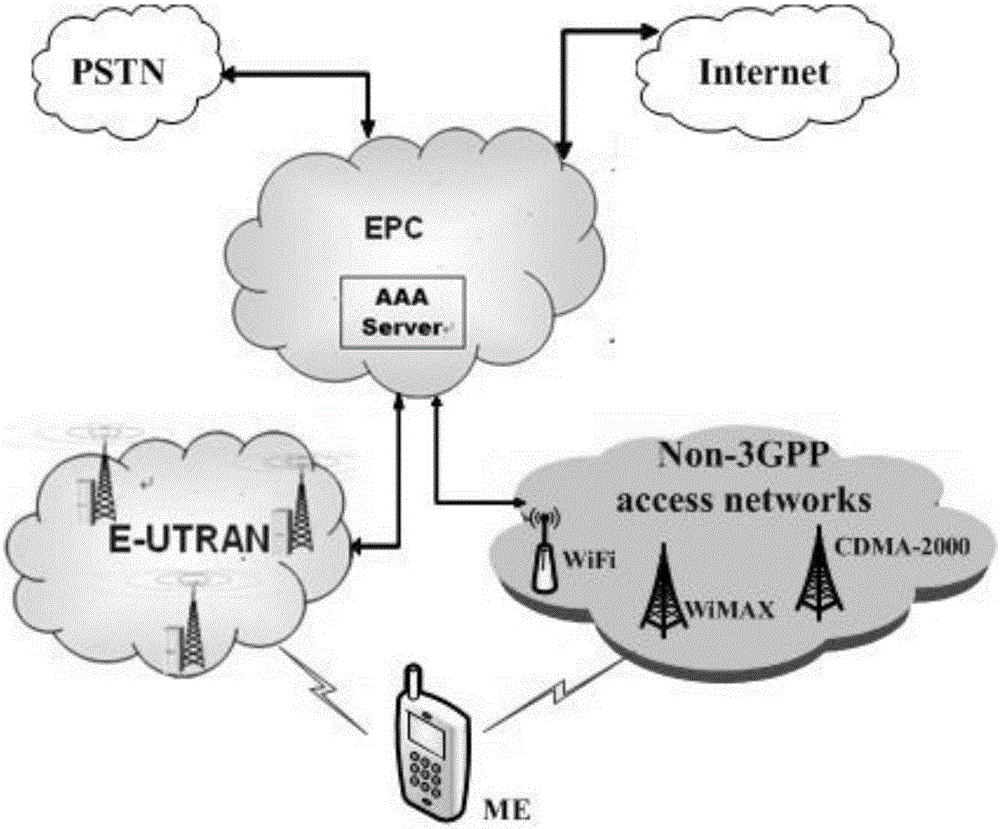
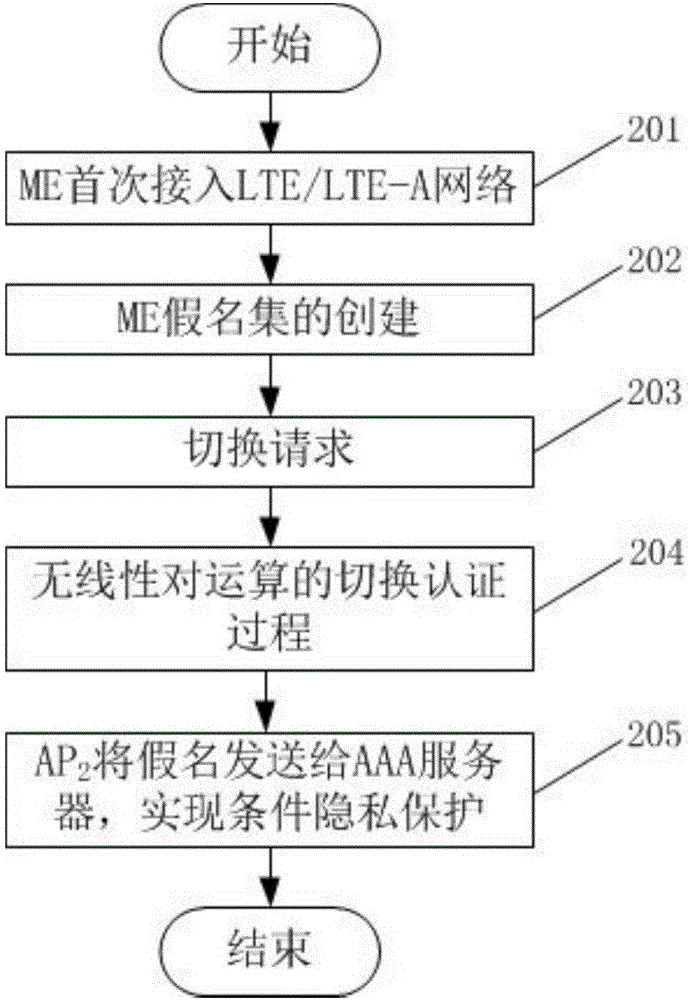
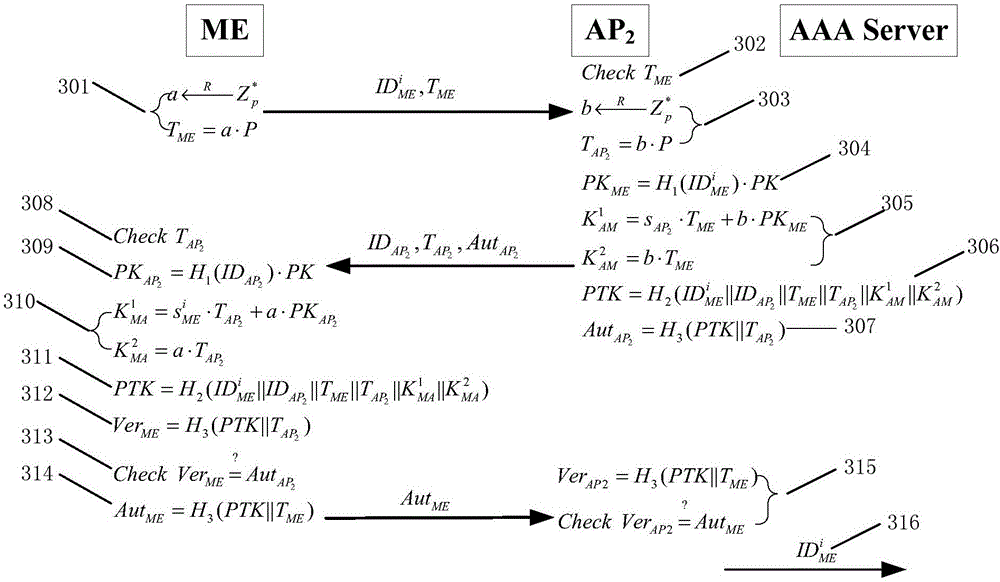
The invention discloses an authentication switching method with privacy protection in an LTE (long term evolution) / LTE-A (LTE-advanced) network. After ME (mobile equipment) is accessed to the LTE / LTE-A network for the first time and successfully finishes access authentication with an AAA (authentication, authorizing and accounting) server, the AAA server generates a pseudonym set for the ME. When the ME needs to be switched to a new AP (access point) due to movement, only one unused pseudonym needs to be selected from the pseudonym set to perform identity authentication, the real identity of the ME does not need to be provided, so that leakage of a user identity and position privacy can be avoided, and anonymity and untraceability are realized. In the authentication switching process, key agreement is realized based on a Diffie-Hellman key exchange algorithm, the mutual authentication process is finished by hash function value verification, bilinear pairing operation is omitted, and authentication delay is reduced.
Owner:NANJING UNIV OF SCI & TECH
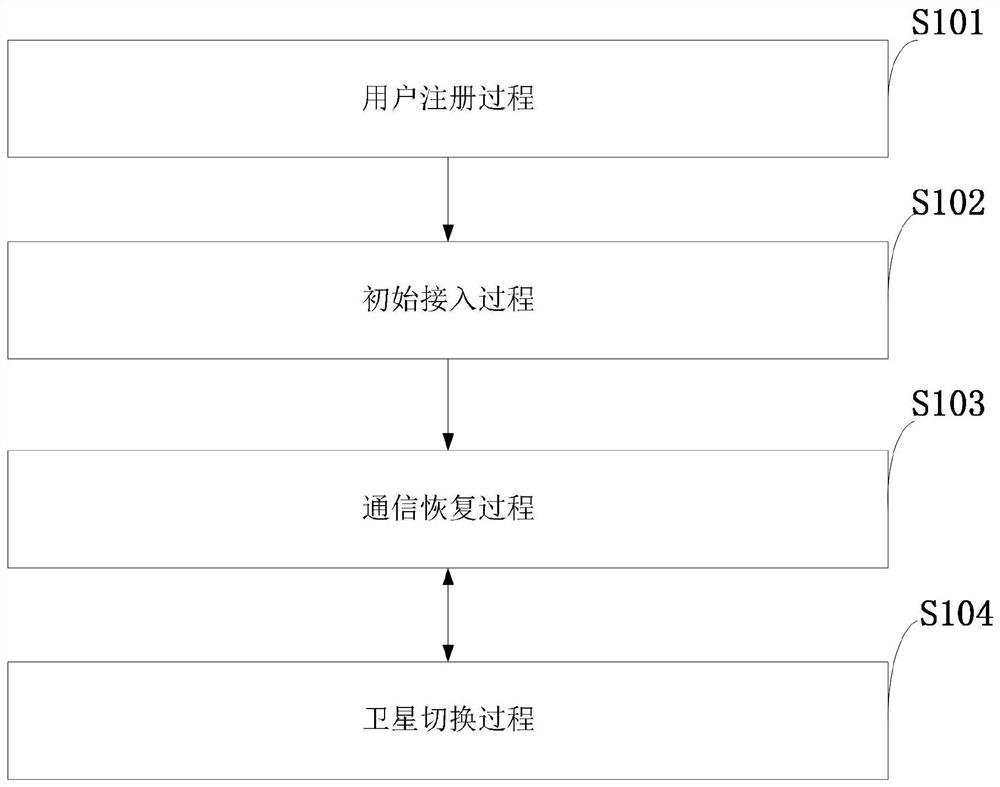
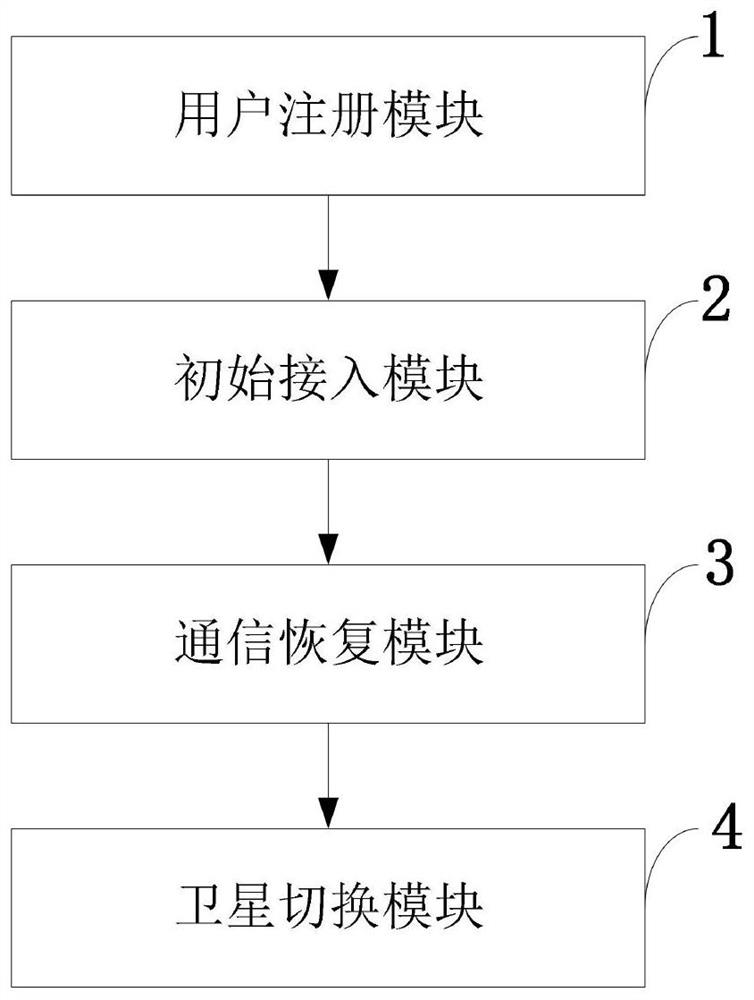
Access and switching authentication method and system in satellite network intermittent connection scene
ActiveCN112087750ASafe and efficient access authentication processReduce the number of interactionsNetwork topologiesSecurity arrangementHash functionTimestamp
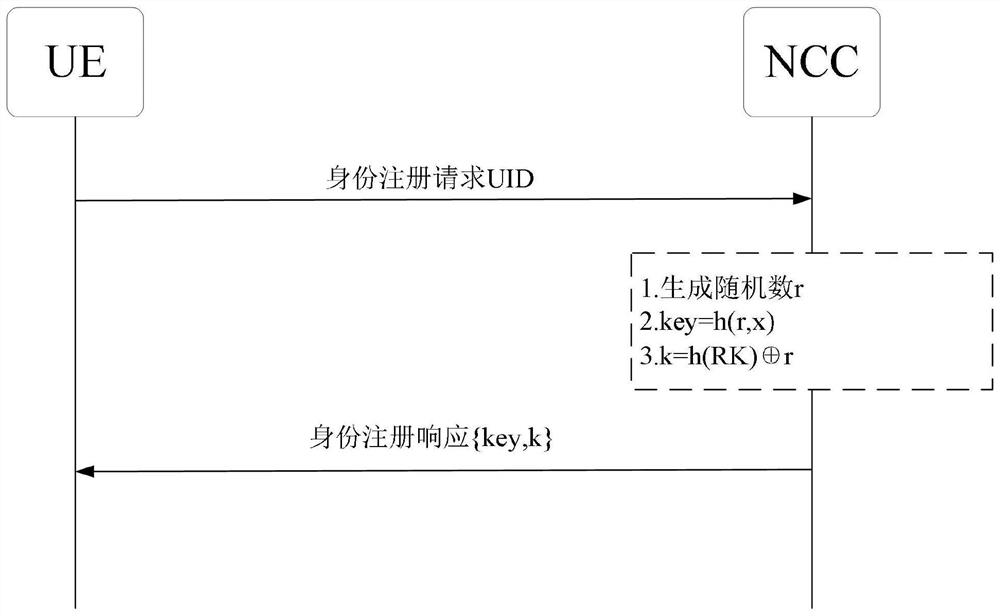
The invention belongs to the technical field of network security communication, and discloses an access and switching authentication method and system in a satellite network interrupted connection scene. The access and switching authentication method has the advantages that: simple hash and XOR operations are used for operation, and meanwhile, a terminal is guaranteed to be safely accessed to a satellite network through using a timestamp, a message authentication code, a random number and RES, and bidirectional authentication is realized while the communication overhead and the calculation overhead are reduced; based on a current session key of a mobile user UE and a satellite network, rapid communication recovery authentication after the UE and the satellite network are disconnected is realized, the unnecessary access authentication frequency is reduced, and the burden of the system is reduced; safe switching is achieved through utilizing random numbers and hash functions, and safe switching is achieved while the communication cost in the satellite switching process is reduced; and the user achieves anonymity by generating a temporary identity, and each successful authentication is refreshed for the next authentication.
Owner:XIDIAN UNIV
Identity-based authentication method for space-based network
ActiveCN113079016ASmall message sizeAvoid transmissionKey distribution for secure communicationUser identity/authority verificationTelecommunicationsEngineering
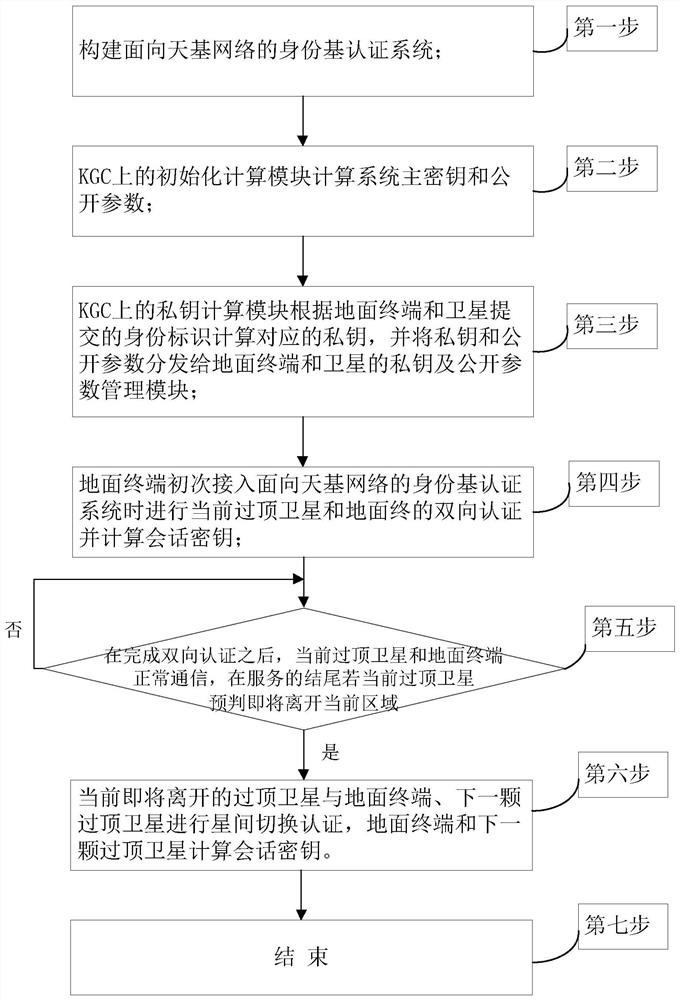
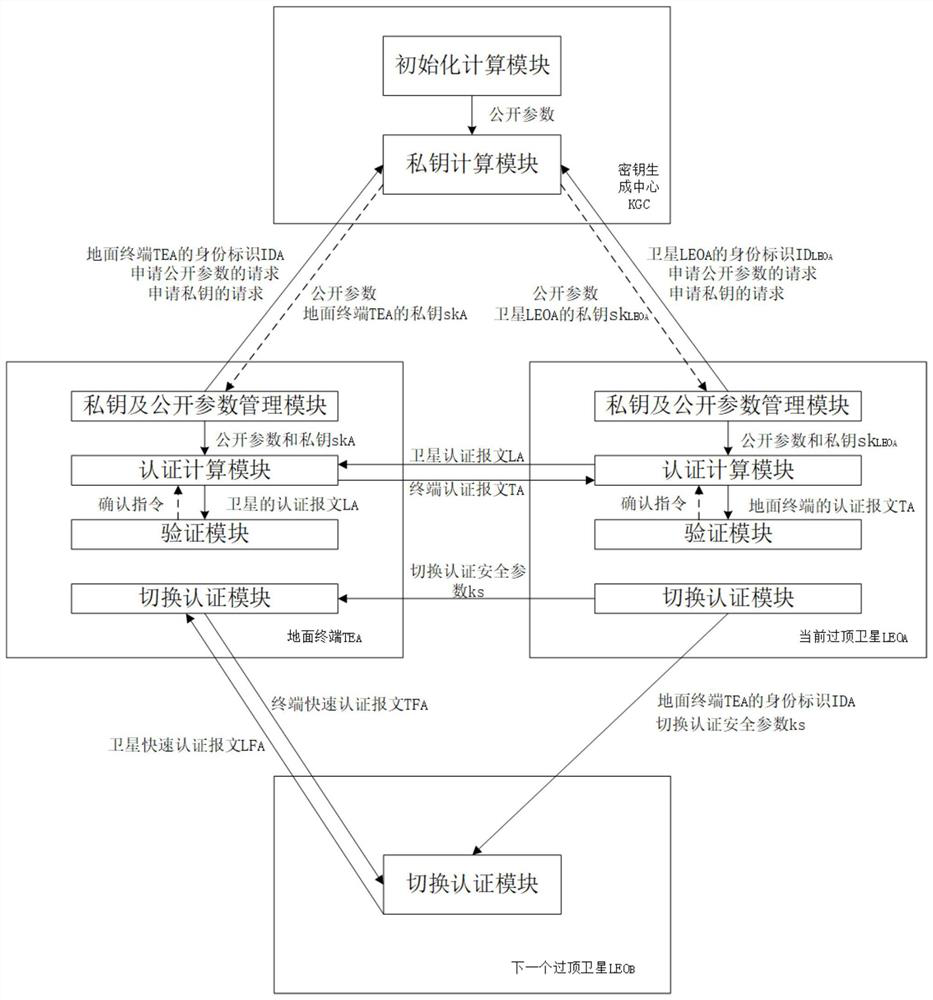
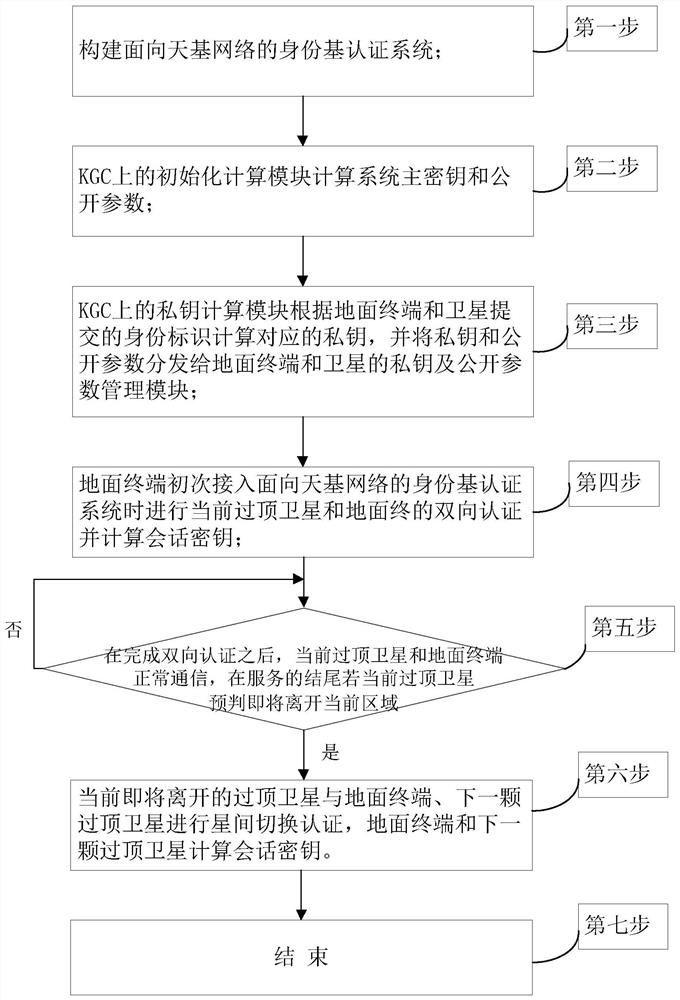
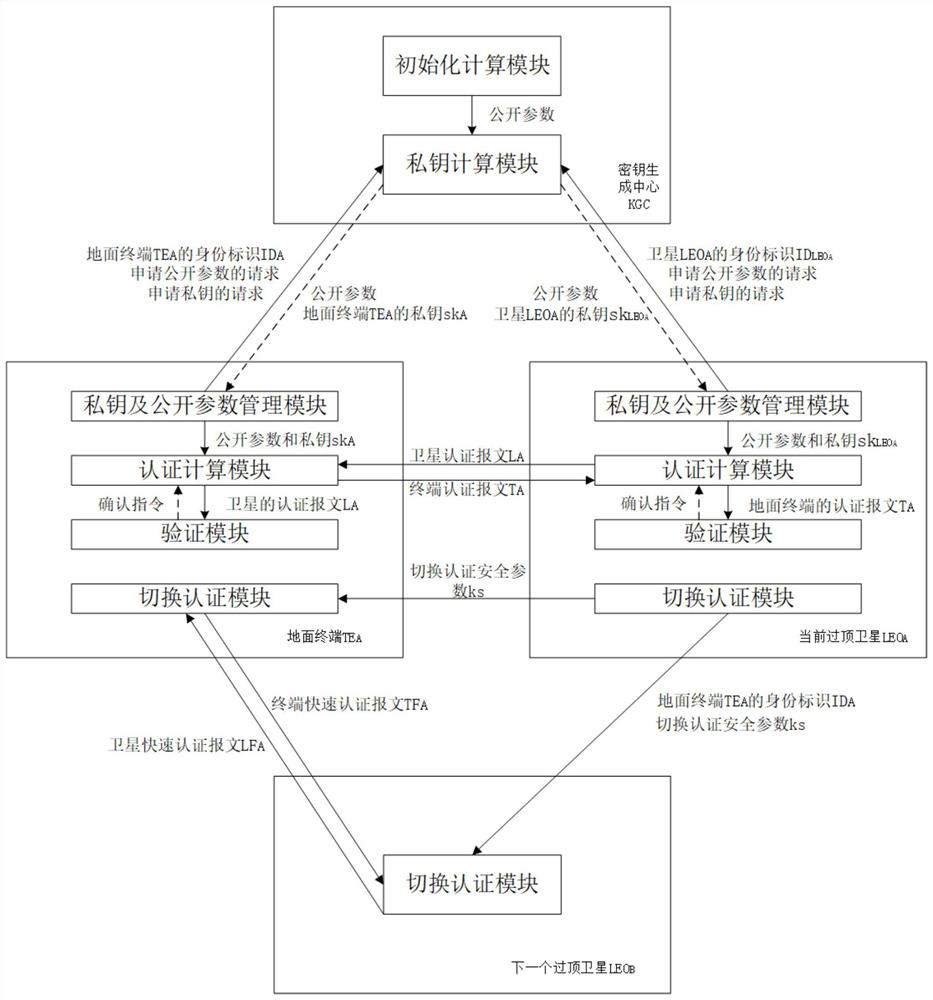
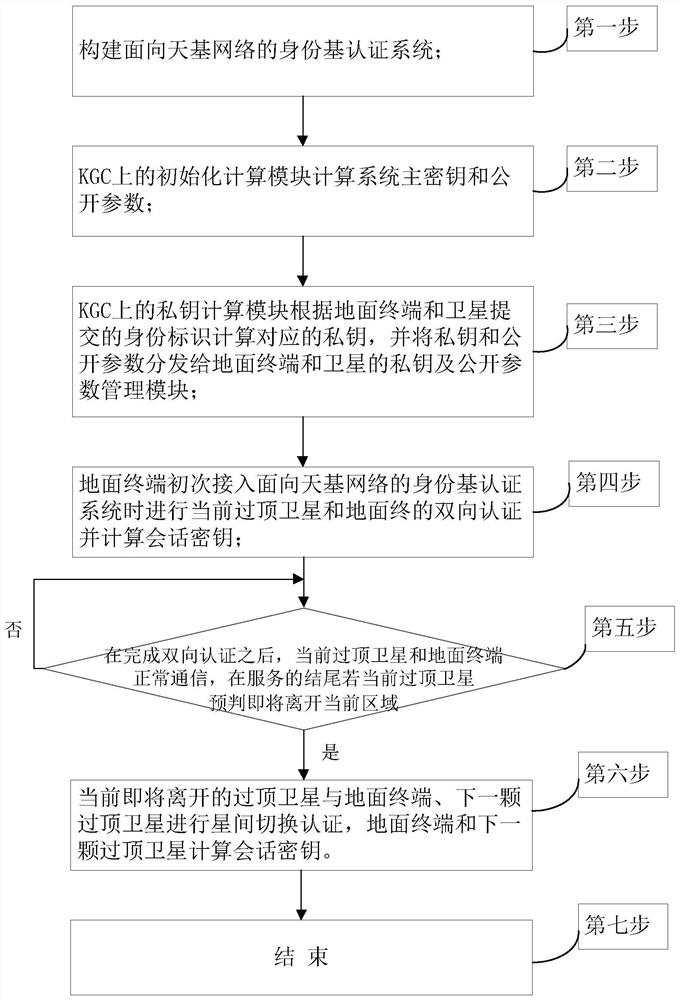
The invention discloses an identity-based authentication method for a space-based network, and aims to solve the problem of security authentication of a ground terminal and a satellite in the space-based network and improve the security of space-based network communication. According to the technical scheme, the method comprises the following steps: firstly, constructing an identity-based authentication system for a space-based network consisting of a ground terminal, a key generation center (KGC) and a low-orbit satellite; by an initialization calculation module of the KGC, calculating a system master key and public parameters; and by a private key calculation module of the KGC, calculating a corresponding private key and distributing the private key and the public parameters to the ground terminal and the satellite. When a terminal TEA gets access, bidirectional authentication and session key negotiation of a current overhead satellite LEOA and the TEA are carried out, then the LEOA and the TEA normally communicate with each other, if the LEOA determines that the LEOA is about to leave a current area at the end of service, inter-satellite switching authentication is carried out, if the LEOA determines that the LEOA is not about to leave the current area at the end of service, the LEOA and the TEA continue to communicate with each other. According to the invention, the size of the transmitted message is effectively reduced, and fast switching authentication and session key negotiation are realized while the security is ensured.
Owner:NAT UNIV OF DEFENSE TECH
Industrial Internet of Things security authentication method and system based on zero-knowledge proof
The invention provides an industrial Internet of Things security authentication method and system based on zero-knowledge proof, and relates to the technical field of security authentication, and the method comprises the steps: sending the identity information of terminal equipment to an authentication server through an edge computing node, generating an equipment certificate, and building an identity management information base; and the authentication server detects a computing resource occupancy rate of the terminal equipment according to the equipment authentication key, generates a zero-knowledge proof request, performs parallel verification, updates an equipment reputation score and predicts a next authentication session state. And selecting main and standby communication channels based on the prediction state, and triggering channel switching when the health degree is lower than a threshold value. And the authentication server determines a dynamic time slice allocation strategy according to the equipment reputation score, the service priority and the prediction state, and the edge computing node adaptively adjusts the size of the time slice to complete authentication request processing. According to the method, the authentication efficiency and security are improved, the computing resource consumption is reduced, and the system robustness is enhanced.

Owner:北京网藤科技有限公司
Combined handover authentication method and system used for goods escorting
InactiveCN104392339AAvoid private transfersStrong process controllabilityLogisticsSecret codeGeolocation
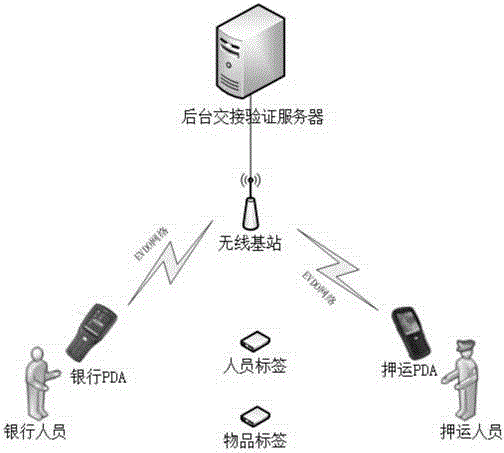
The invention discloses a combined handover authentication method and system used for goods escorting. The method is characterized by including the following steps that: (a) handover task information is pre-stored to a remote server; (b) handheld terminals transmit handover requests through a wireless network, detect geographic positions where signals are transmitted, and after conformation between the geographic positions and geographic positions pre-stored in the remote server are confirmed, opening codes are send back; (c) the handheld terminals open authentication interface display, and read several pieces of authentication tag information, are coupled with the remote server through the wireless network, and judge whether the obtained authentication tag information is correct or not through comparison, at the same time, download personnel information, and the method enters a manual authentication phase; and (d) physical handover is performed, and tag information of handover items is uploaded, and the handover terminates. The system can keep real-time communication with the remote server through the wireless network. According to the combined handover authentication method and system, an electronic fence is set, and information can be uploaded and downloaded on line, and the controllability, timeliness and reliability of a handover process can be ensured, and situations such as handover errors and omissions can be avoided; and the whole handover process has traceability, so that the whole handover process is safer and more reliable.
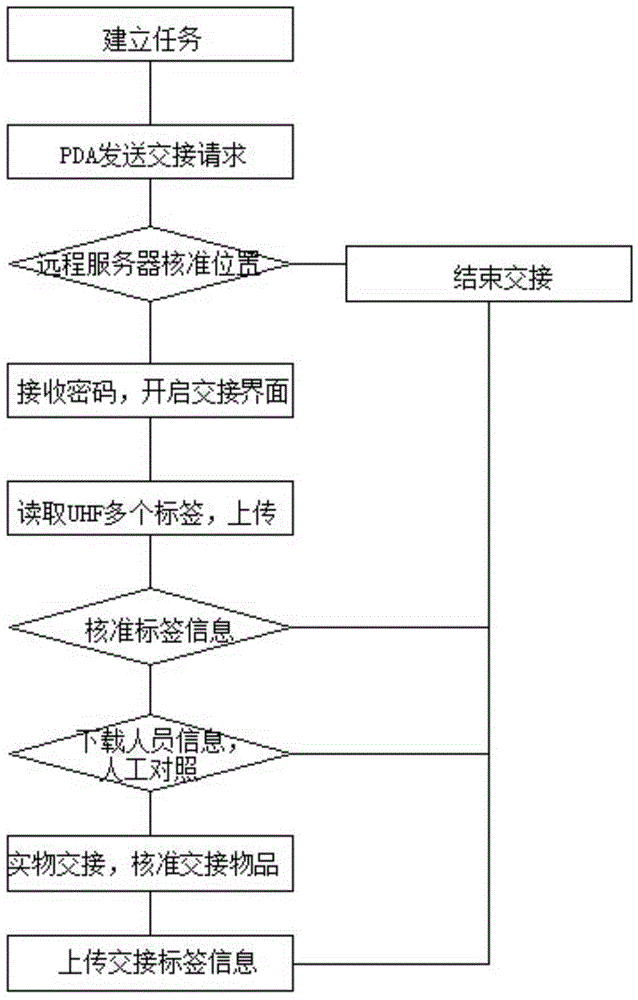
Owner:SUZHOU UNIV
Quick switching authentication method for low-orbit satellite communication network
ActiveCN112332900AReduce overheadGuaranteed continuityUser identity/authority verificationRadio transmissionTelecommunicationsHandover authentication
The invention discloses a quick switching authentication method for a low-orbit satellite communication network, which comprises the following steps that: a user terminal and a satellite terminal carry satellite inherent equipment information to register in a ground management center, and an original satellite selects a satellite switched by the user terminal according to the periodicity of the satellite to send a switching application request message; if successfully decrypting the authentication information of the user terminal, the switching satellite repliess a switching permission response message to the original satellite; the original satellite receives the switching permission response message of the switching satellite, generates switching preparation information and sends the switching preparation information to the user terminal; the user terminal receives the switching preparation message, determines the switching time, and sends a switching authentication request message to the switching satellite; the switching satellite receives the switching authentication request message and sends switching authentication response information to the user terminal; the user terminalreceives and verifies the switching authentication response information to complete a switching authentication process; According to the method, the security of the switching authentication process of the user terminal is ensured while the switching authentication time delay and the calculation overhead are reduced.
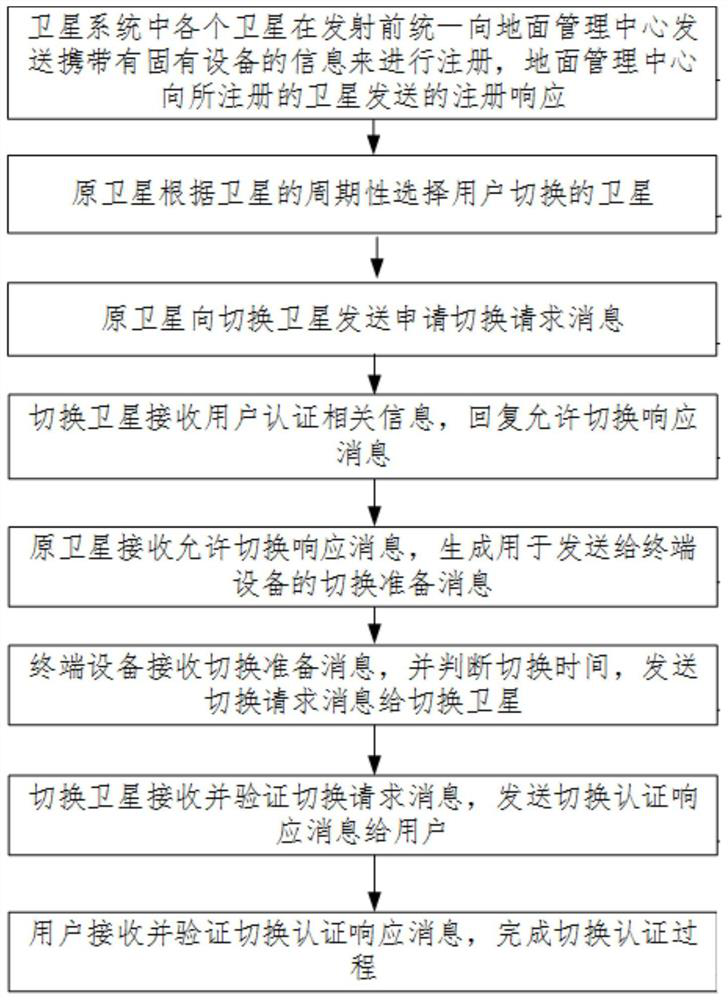
Owner:GUIZHOU AEROSPACE INST OF MEASURING & TESTING TECH
Two-way access authentication method for multi-layer-MAP oriented HMIPv6 network
ActiveCN105376230AShorten the lengthImplement two-way authenticationTransmissionSecurity arrangementShort signatureTrusted third party
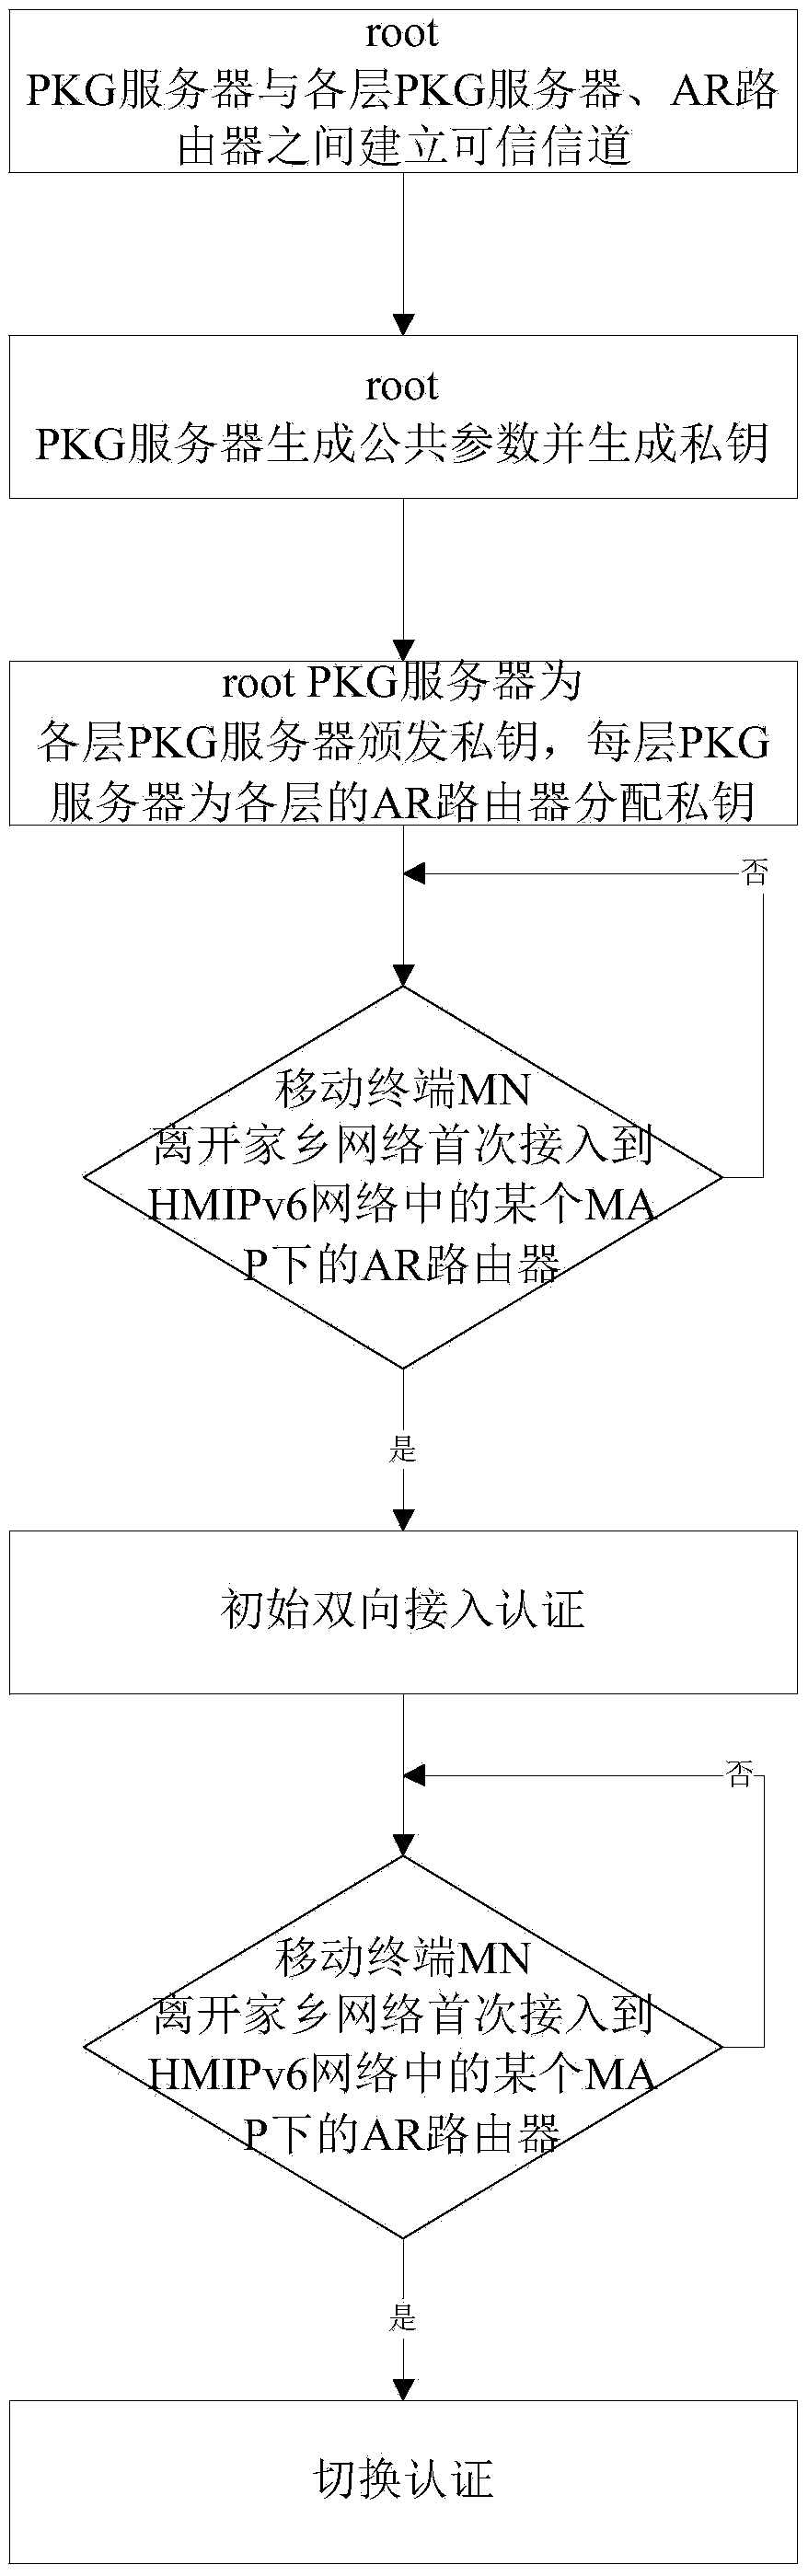
The invention provides a two-way access authentication method for a multi-layer-MAP oriented HMIPv6 network. The two-way access authentication method comprises the following steps that: a root PKG server is used as a trusted third party; a trusted channel is established among the root PKG server, PKG servers and AR routers in various layers; the root PKG server generates common parameters and private keys; the root PKG server issues the private keys to the PKG servers in the various layers according to identity information of the PKG servers in the various layers; the PKG server in each layer distributes the private key to the AR router in this layer according to identity information of the AR router in this layer; when a mobile node MN leaves a home homework and is accessed to the AR router under a certain MAP in the HMIPv6 network for the first time, initial two-way access authentication is carried out; and, when the mobile node MN is in a currently accessed foreign network and the AR router in the current MAP domain is switched into another MAP domain or another AR router, switching authentication is carried out. The invention provides a short signature scheme based on node certificate hierarchical identity; the security is based on the h-CDH problem; the short signature scheme has the advantages that: the lengths of the private keys are reduced along with increasing of hierarchical levels; and the lengths of the private keys are independent of the hierarchical levels.
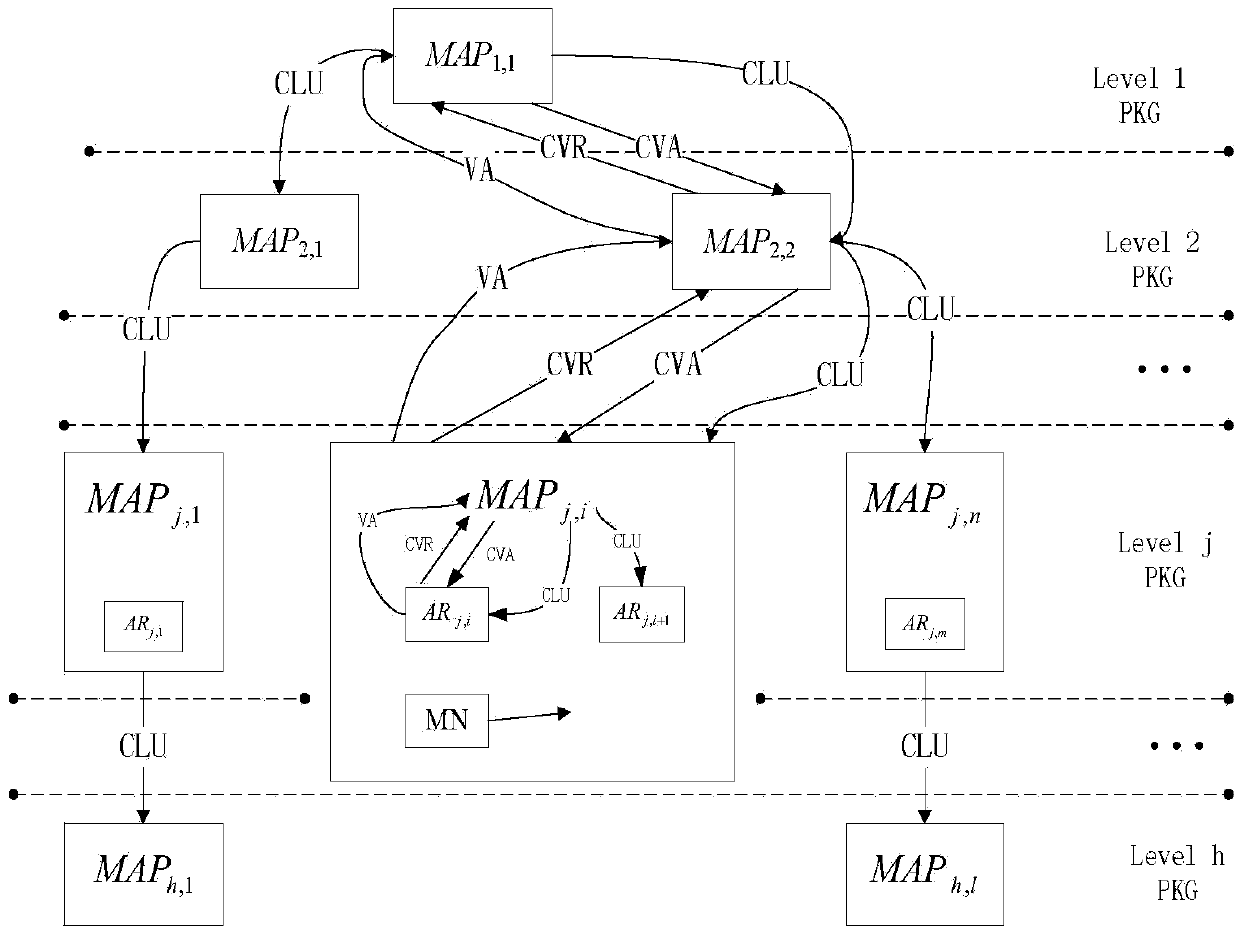
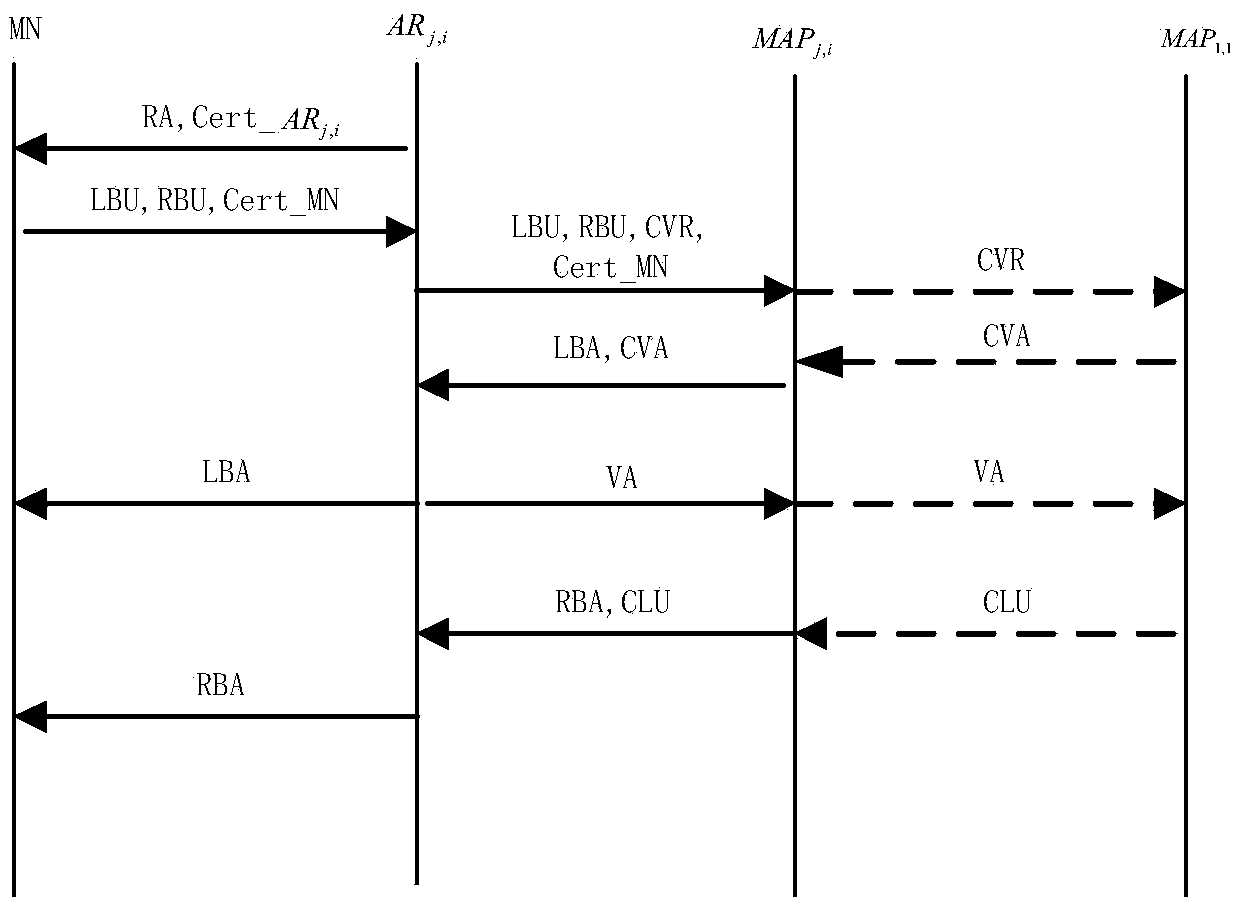
Owner:NORTHEASTERN UNIV
Cross-system non-inductive switching authentication method and device for e-commerce
The invention relates to the technical field of computer authentication, and discloses a cross-system non-inductive switching authentication method and device for e-commerce, electronic equipment and a storage medium. The method comprises the following steps: acquiring user behavior data, and generating a user behavior data set; extracting user behavior features, and constructing a feature vector group; matching a user behavior mode in combination with a historical abnormal file, and giving an initial score to an abnormal risk; if the score exceeds a threshold value, performing cross validation on the login time distribution and the operation instruction sequence, and determining an abnormal risk level; according to the risk level, matching an authentication strategy, and generating a targeted authentication process scheme; and issuing the scheme to the front end of the equipment for execution, and determining an authentication result. According to the method, through dynamic and accurate risk assessment and adaptive adjustment of the authentication strength, the problem of low user experience and safety caused by a fixed authentication strategy in the prior art is solved.

Owner:SHENZHEN HUAQIANG ELECTRONIC TRANSACTIONS NETWORK CO LTD
Data feedback method and system
ActiveCN111738736AImplement feedbackImprove experienceDevices with sensorCo-operative working arrangementsEmbedded systemHandover authentication
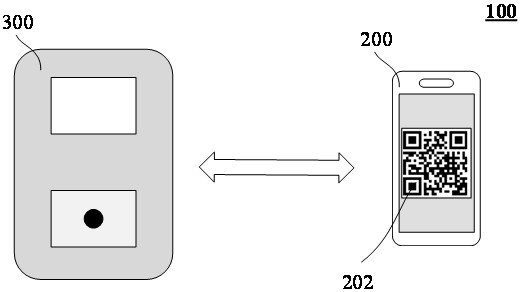
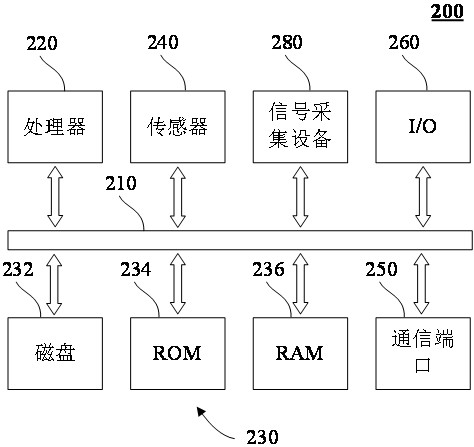
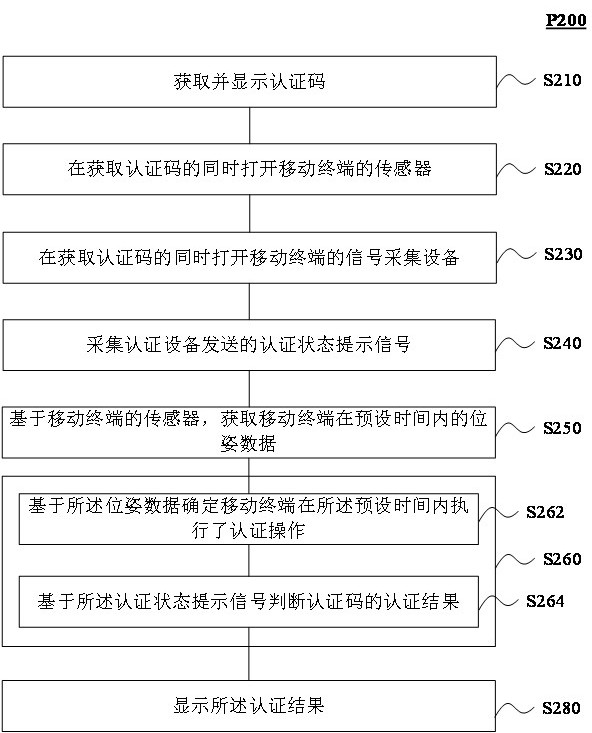
According to the data feedback method and system provided by the invention, after the mobile terminal calls out the authentication code, the pose data of the mobile terminal is acquired through the sensor of the mobile terminal, and the code scanning authentication state prompt signal of the authentication equipment is acquired through the signal acquisition equipment of the mobile terminal; whether the mobile terminal performs a code scanning authentication action or not is judged according to the pose data; and a code scanning authentication result is judged according to the acquired code scanning authentication state prompt signal, and the authentication result is displayed on a page of the mobile terminal. According to the method and the system, the code scanning authentication resultcan be fed back to the mobile terminal in real time in an offline state of the authentication equipment or the mobile terminal, and the mobile terminal is prompted to switch the authentication code after the code scanning is failed. Therefore, real-time feedback of data in an offline state is realized, and the user experience is improved.
Owner:ALIPAY (HANGZHOU) INFORMATION TECH CO LTD
Group access authentication and switching authentication method and application suitable for space-ground integration
ActiveCN112243235APrivacy protectionImprove authentication efficiencyNetwork topologiesSecurity arrangementPrivacy protectionEngineering
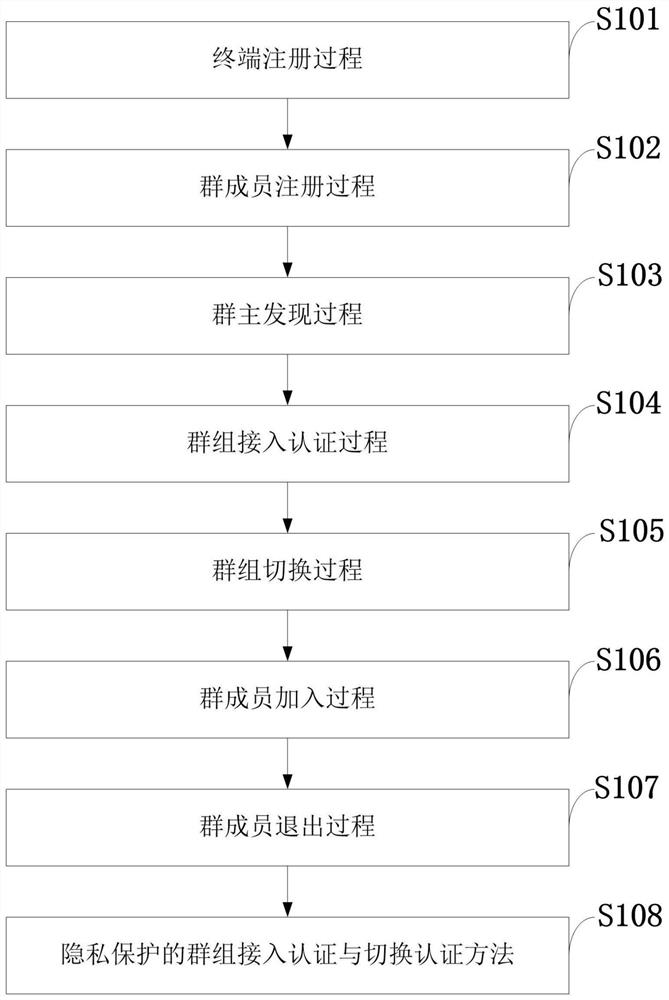
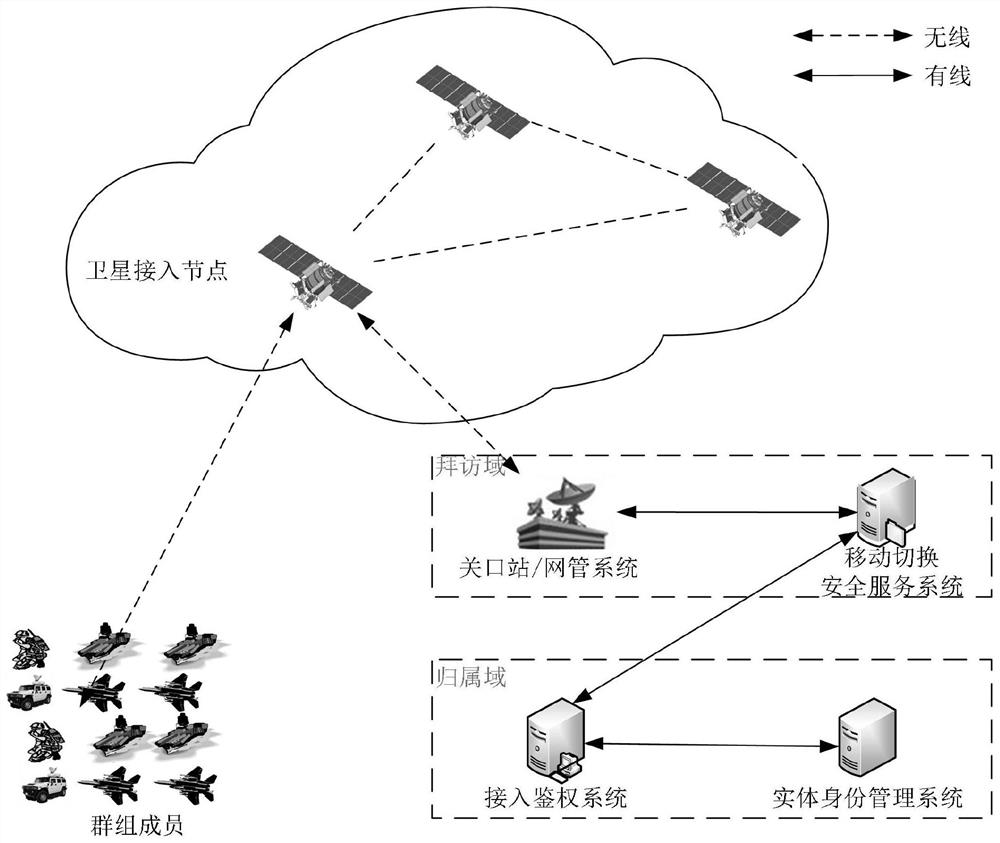
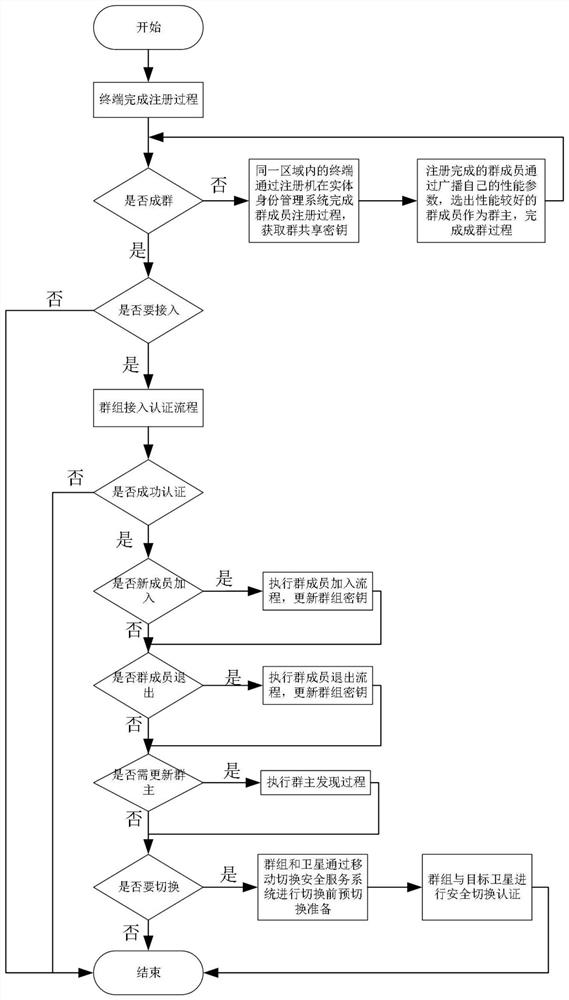
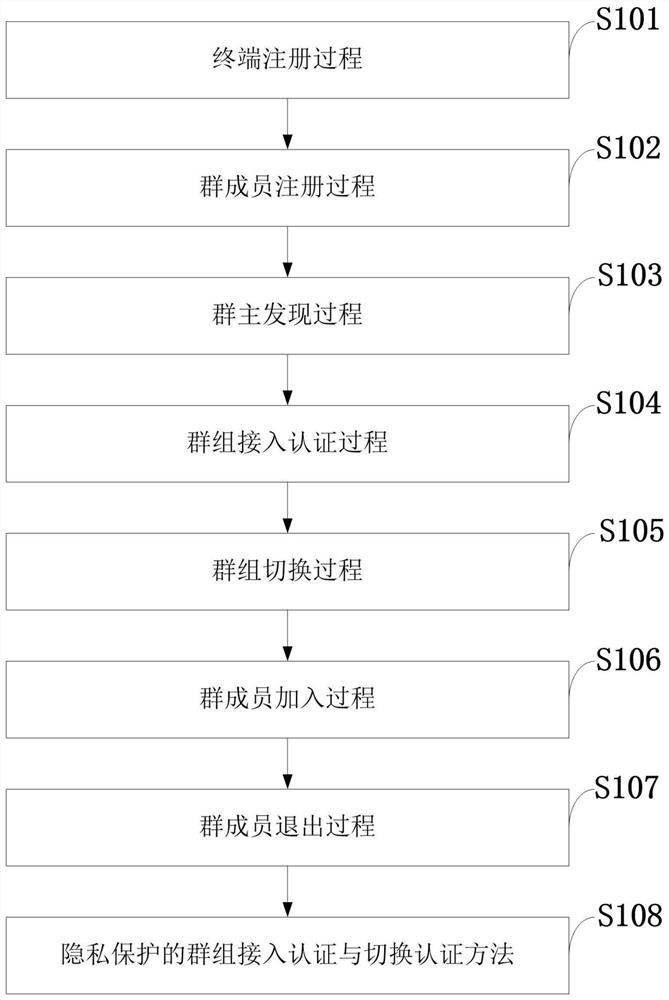
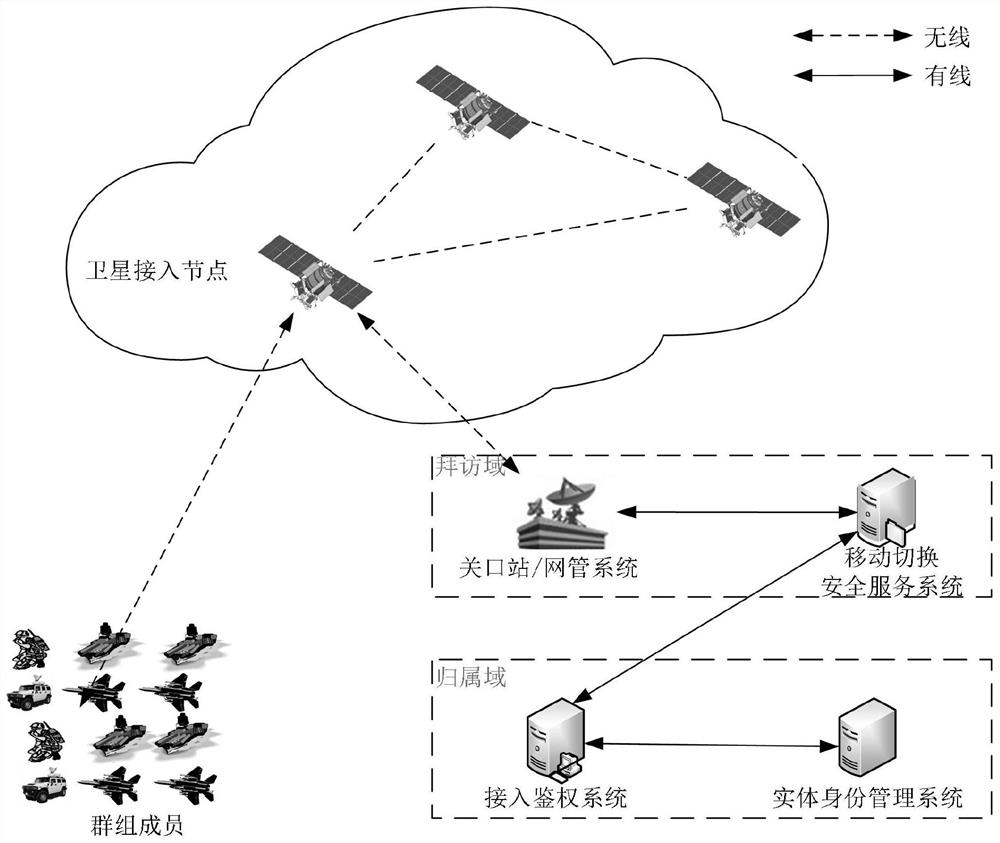
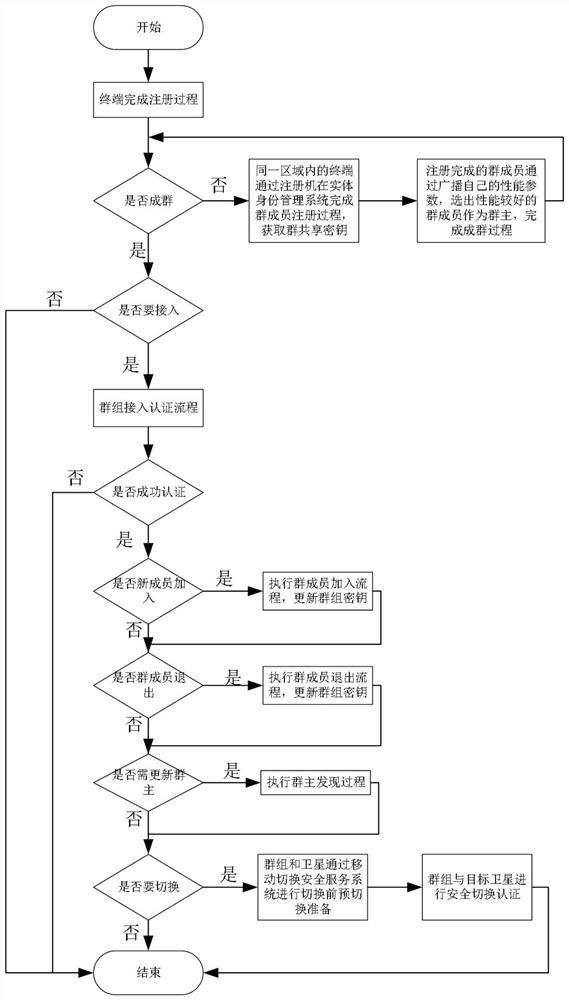
The invention belongs to the technical field of communication network security, and discloses a group access authentication and switching authentication method and application suitable for space-ground integration; the method comprises a terminal registration process, a group member registration process, a group owner discovery process, a group access authentication process, a group switching process, a group member joining process, and a group member quitting process. The invention discloses a privacy-protected group access authentication and switching authentication method. The method can beapplied to space-ground integrated group access authentication and switching scenes; the group owner discovery process is executed offline, so that the group owner can be selected regularly; massiveterminal access authentication and switching authentication are supported; joining and quitting of members in the group can be supported through the joining and quitting process of the group members,and the flexibility of the system is improved; through group authentication, the communication overhead, the calculation overhead and the signaling overhead can be effectively reduced; in addition, the privacy of the identity information of the terminal can be realized through a privacy-protected group access authentication and switching authentication method.
Owner:XIDIAN UNIV
Multi-type terminal access and handover authentication method and system, equipment and application
ActiveCN112235792AEnhanced anonymityDefense against replay attacksAssess restrictionNetwork topologiesAccess networkEngineering
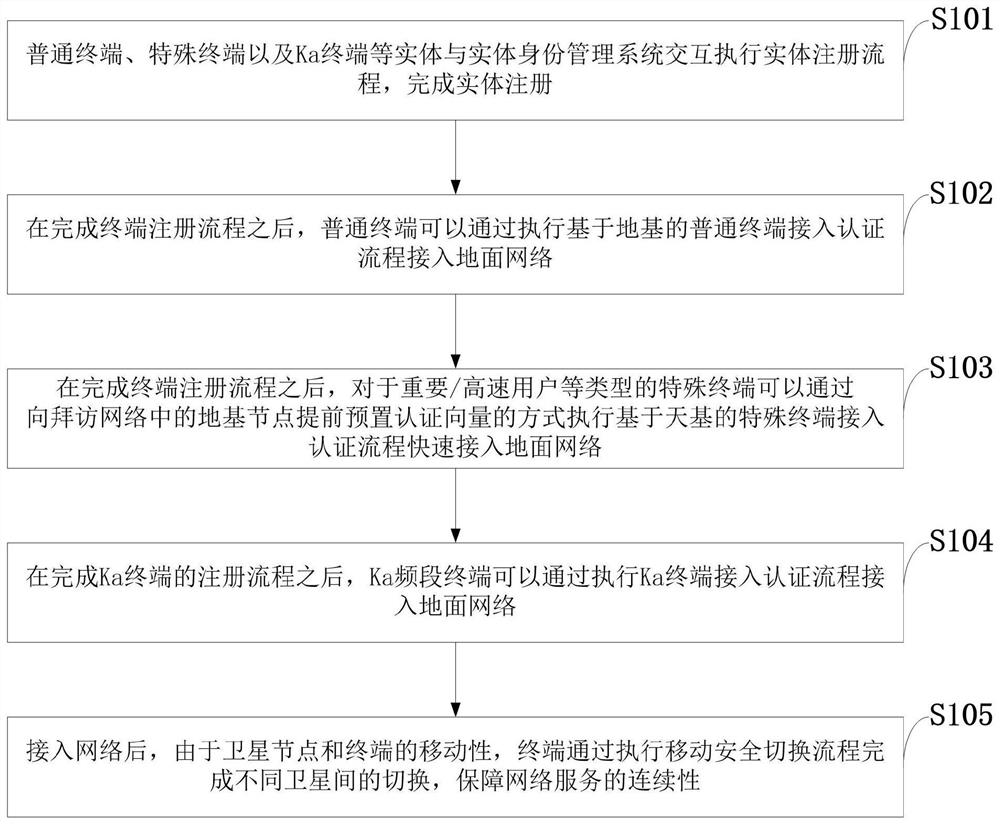
The invention belongs to the technical field of communication network security, and discloses a multi-type terminal access and handover authentication method and system, equipment and application. Themethod comprises the steps of entity registration; ground-based common terminal access authentication; space-based special terminal access authentication; ka terminal access authentication; terminalhandover authentication. According to the method, a common terminal can safely and efficiently access a ground network by executing a ground-based common terminal access authentication process; for special terminals, such as important / high-speed users and the like, a space-based special terminal access authentication process can be used to quickly access a network by presetting an authentication vector in advance without participation of a home network, so that the problem that network service cannot be provided due to faults of the home network is avoided; the access authentication process based on the Ka terminal is used for the Ka terminal, so that high reliability of network access of the Ka terminal is guaranteed, the access authentication efficiency is greatly improved, and access authentication and handover of various different types of terminals are realized.
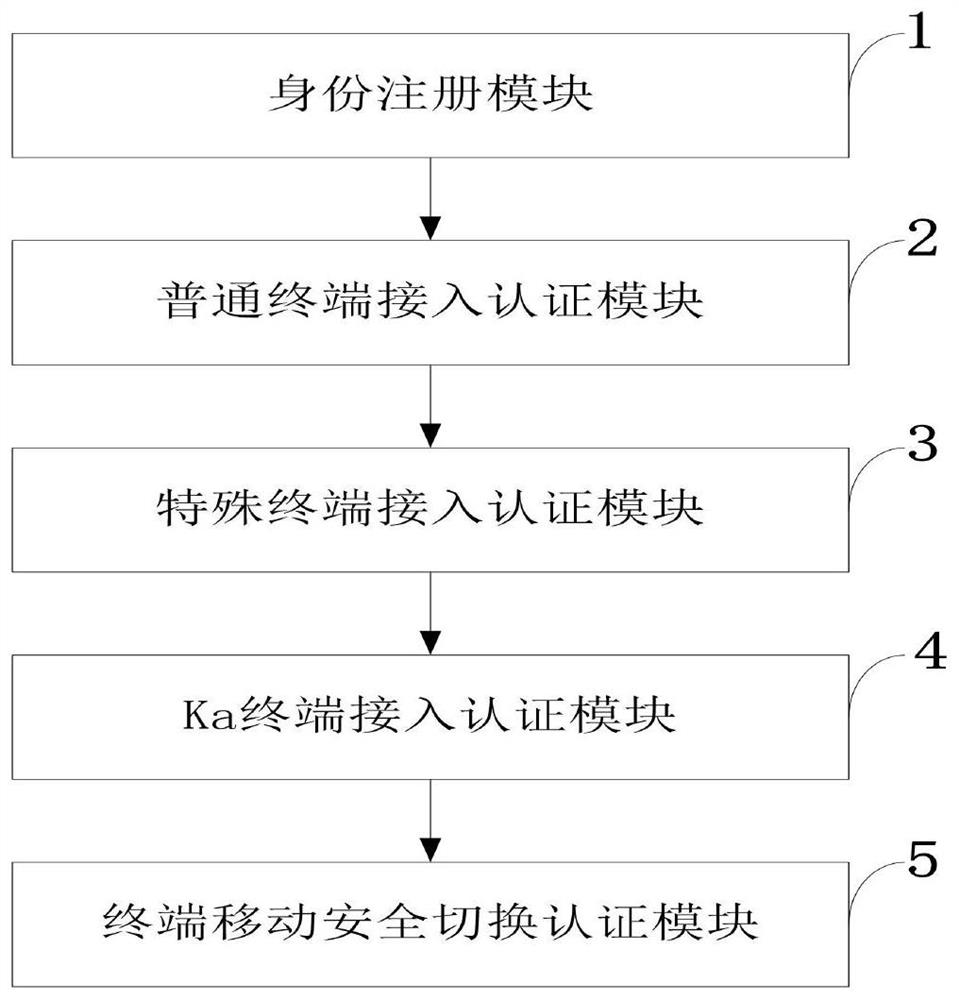
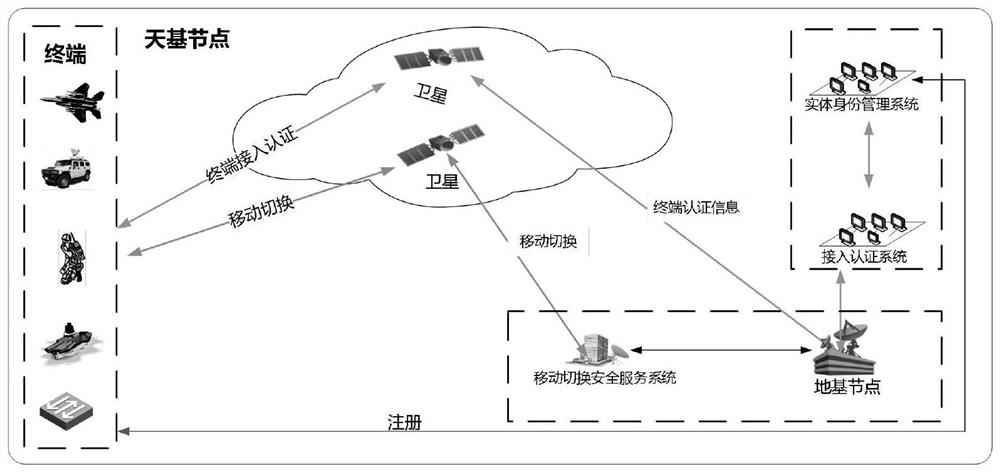
Owner:XIDIAN UNIV
Access authority management method and device, equipment and storage medium
PendingCN120145358ADigital data protectionInternal/peripheral component protectionOperational systemEngineering
The invention discloses an access authority management method and device, equipment and a storage medium, and relates to the technical field of information security, and the method comprises the steps: splitting the authority of an original superuser of an operating system through a minimum authority principle to construct a three-authority split model, and determining a security policy rule by using a policy model in a TE security model; performing user name login authentication, role switching authentication, user identifier permission authentication and biological feature identification authentication on the user information, and determining and recording an initial access permission corresponding to the obtained target permission user by using the three-right discrete model and a block chain technology; when it is monitored that the target permission user uses the initial access permission, identity verification and permission check are conducted on the target permission user through the zero-trust security model; and if the check result does not pass the representation, adjusting the initial access permission by using a machine learning model and a system environment to obtain a target access permission. The complexity of authority management is reduced; and the system security is improved.

Owner:SHANDONG LANGCHAO YUNTOU INFORMATION TECH CO LTD
Authentication method, device and equipment for Internet of Vehicles
PendingCN119997018AKey distribution for secure communicationParticular environment based servicesTrusted authorityMobile edge computing
The invention discloses an authentication method for the Internet of Vehicles, and the method comprises the steps: completing the authentication and key negotiation process of a vehicle and a road side unit through a trusted authority center TA under the condition that the vehicle and the road side unit are detected to be authenticated for the first time; under the condition that authentication is not carried out for the first time, the authentication of the vehicle is rapidly completed through the current road side unit, and a session key between the vehicle and the road side unit is updated; when it is detected that the authenticated vehicle moves and is switched to an unauthenticated area, data exchange and inspection between the road side unit of the current area and the road side unit authenticated last time are utilized; reliable central server auxiliary authentication is still needed when the vehicle accesses the Internet of Vehicles for the first time, then the authenticated vehicle accesses the Internet of Vehicles again, rapid re-authentication and switching authentication based on mobile edge computing are adopted, verification of the central server is not needed, the pressure of central authentication is relieved, and meanwhile the authentication efficiency is improved. The calculation and communication overhead of vehicle authentication is reduced, and the authentication efficiency is effectively improved.

Owner:CISDI INFORMATION TECH CO LTD
Method and system for handover authentication
ActiveUS8131296B2Unauthorised/fraudulent call preventionEavesdropping prevention circuitsClient-sideNetwork service
A handover authentication method includes performing, by a wireless network server, a first authentication between a client and the wireless network server via a first network gateway; obtaining first authentication keys for the wireless network server and the client based on the first authentication; determining, by the wireless network server, a need to handover the client from the first network gateway to a second network gateway; deriving, by the wireless network server and from the first authentication keys, a handover authentication key shared by the client and the wireless network server; obtaining, by the wireless network server, second authentication keys for the network server and the client; and serving, by the wireless network server, the client via the second network gateway.
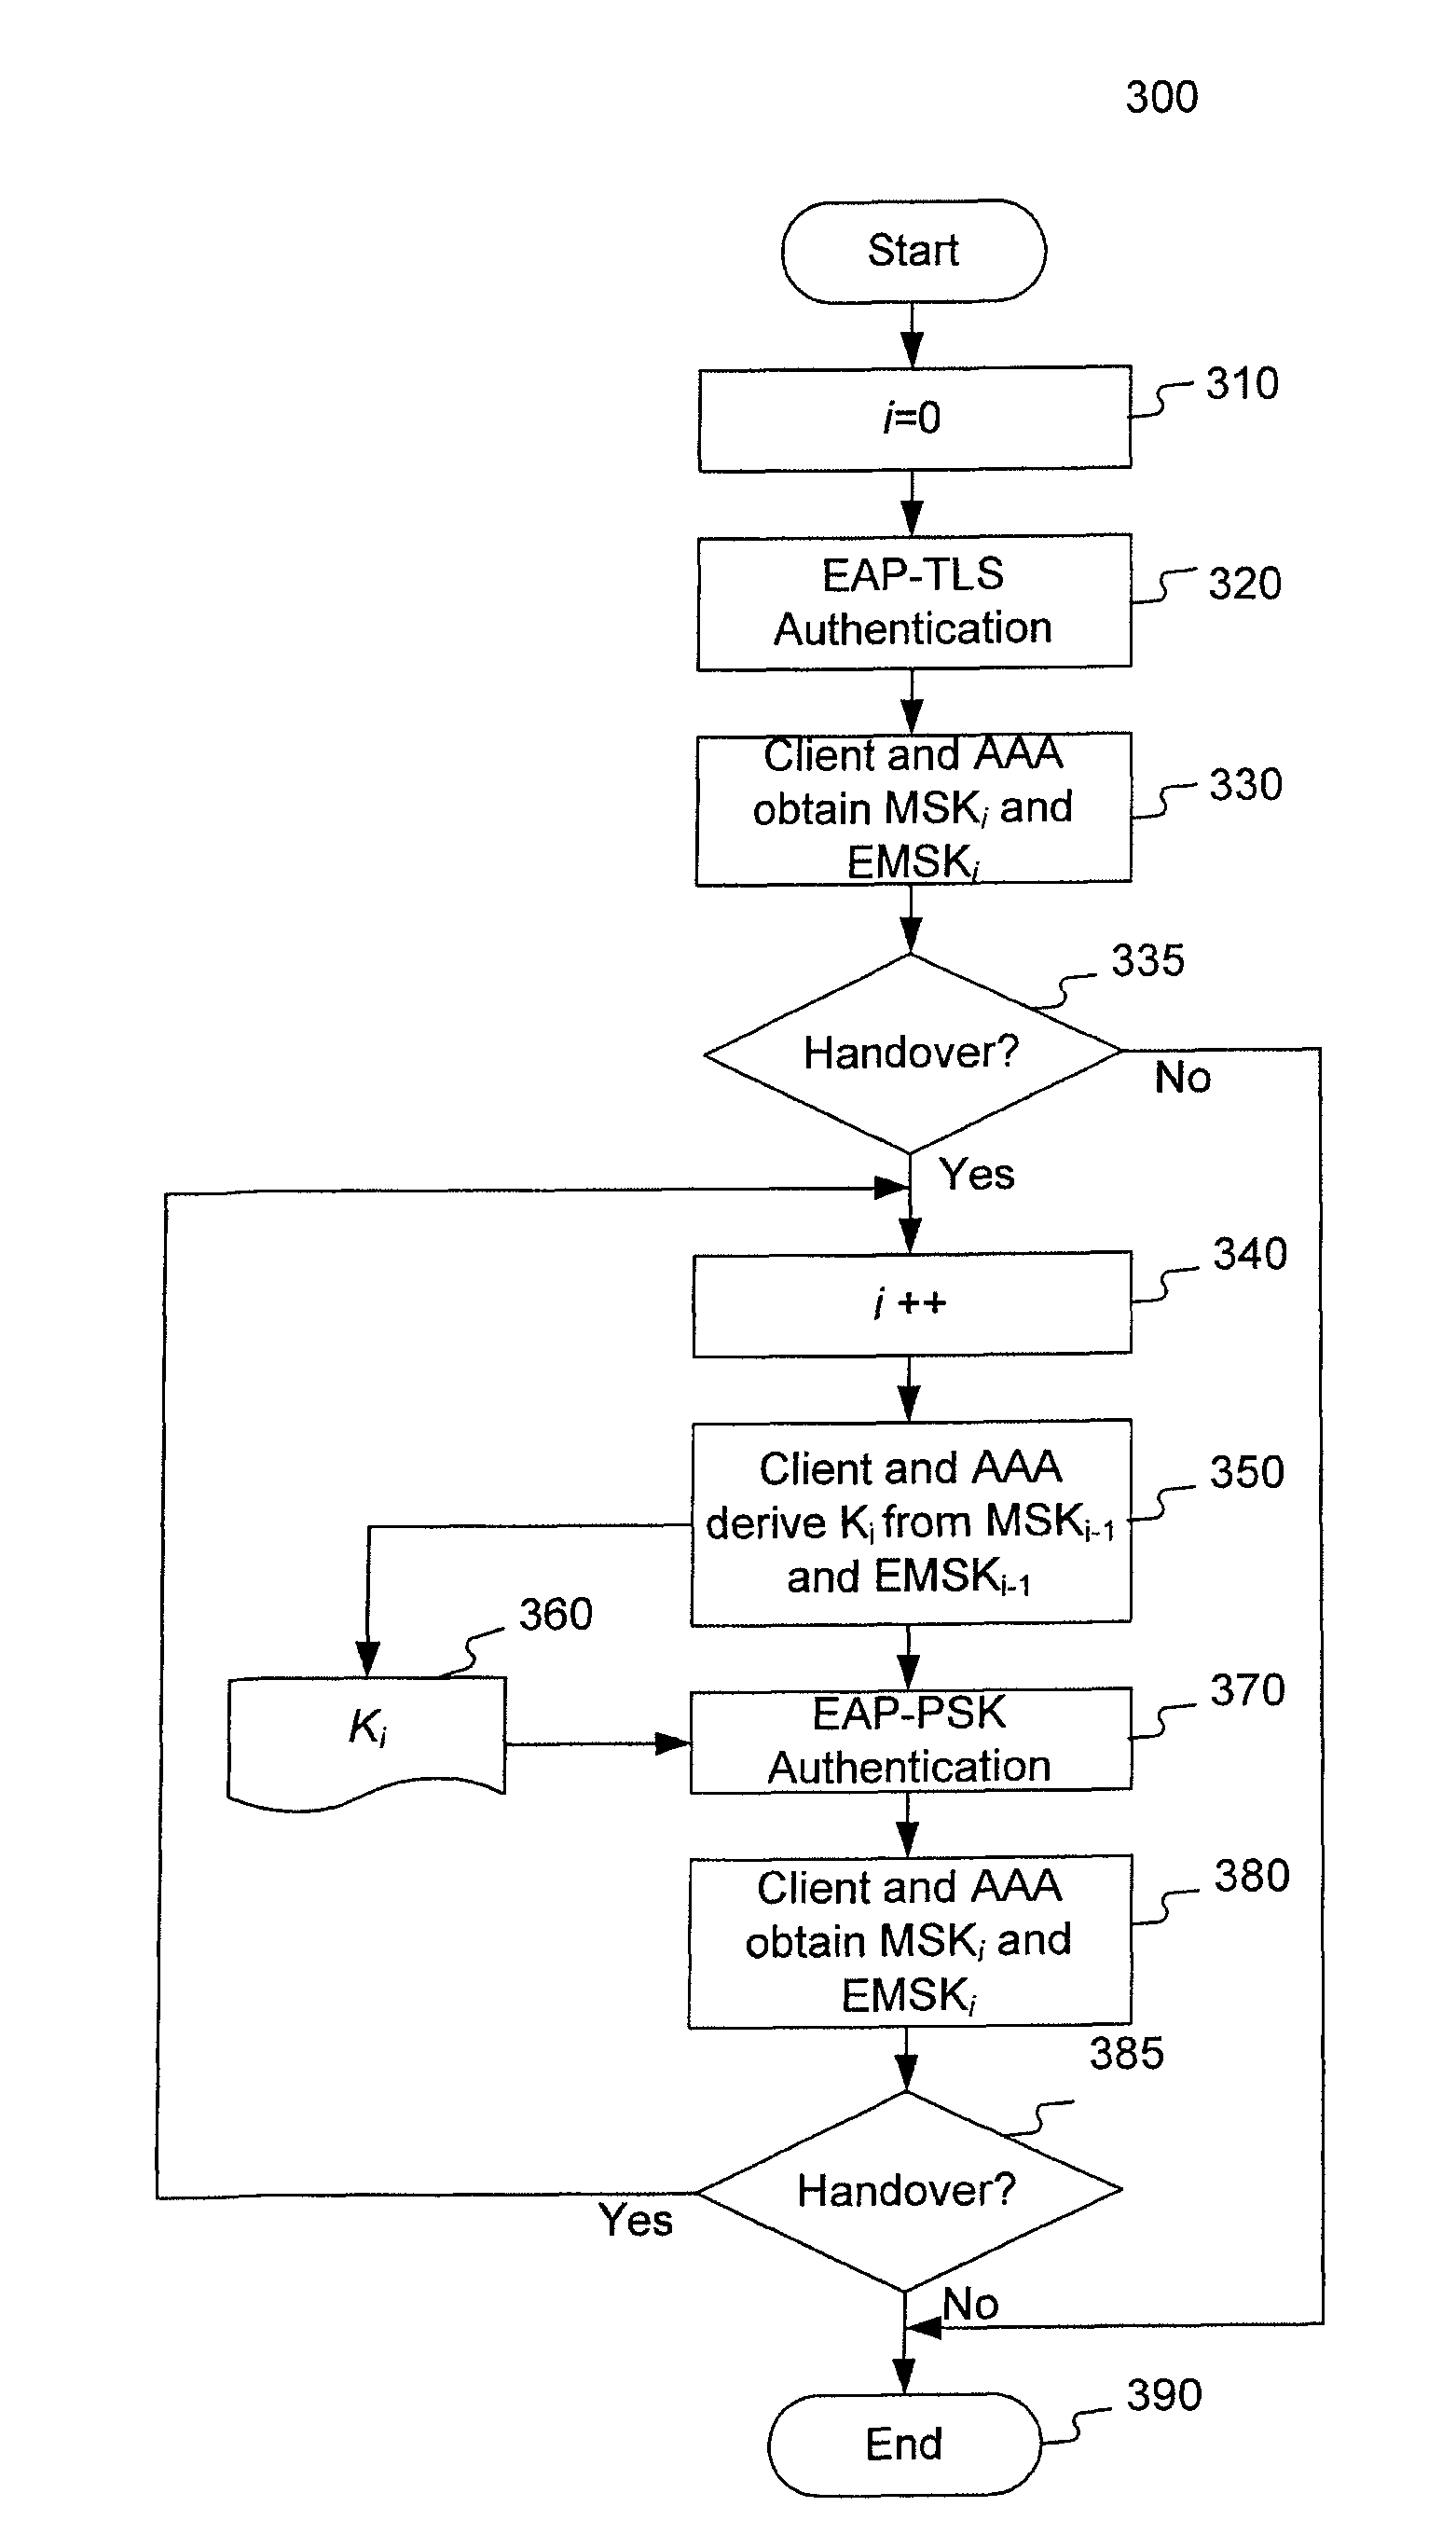
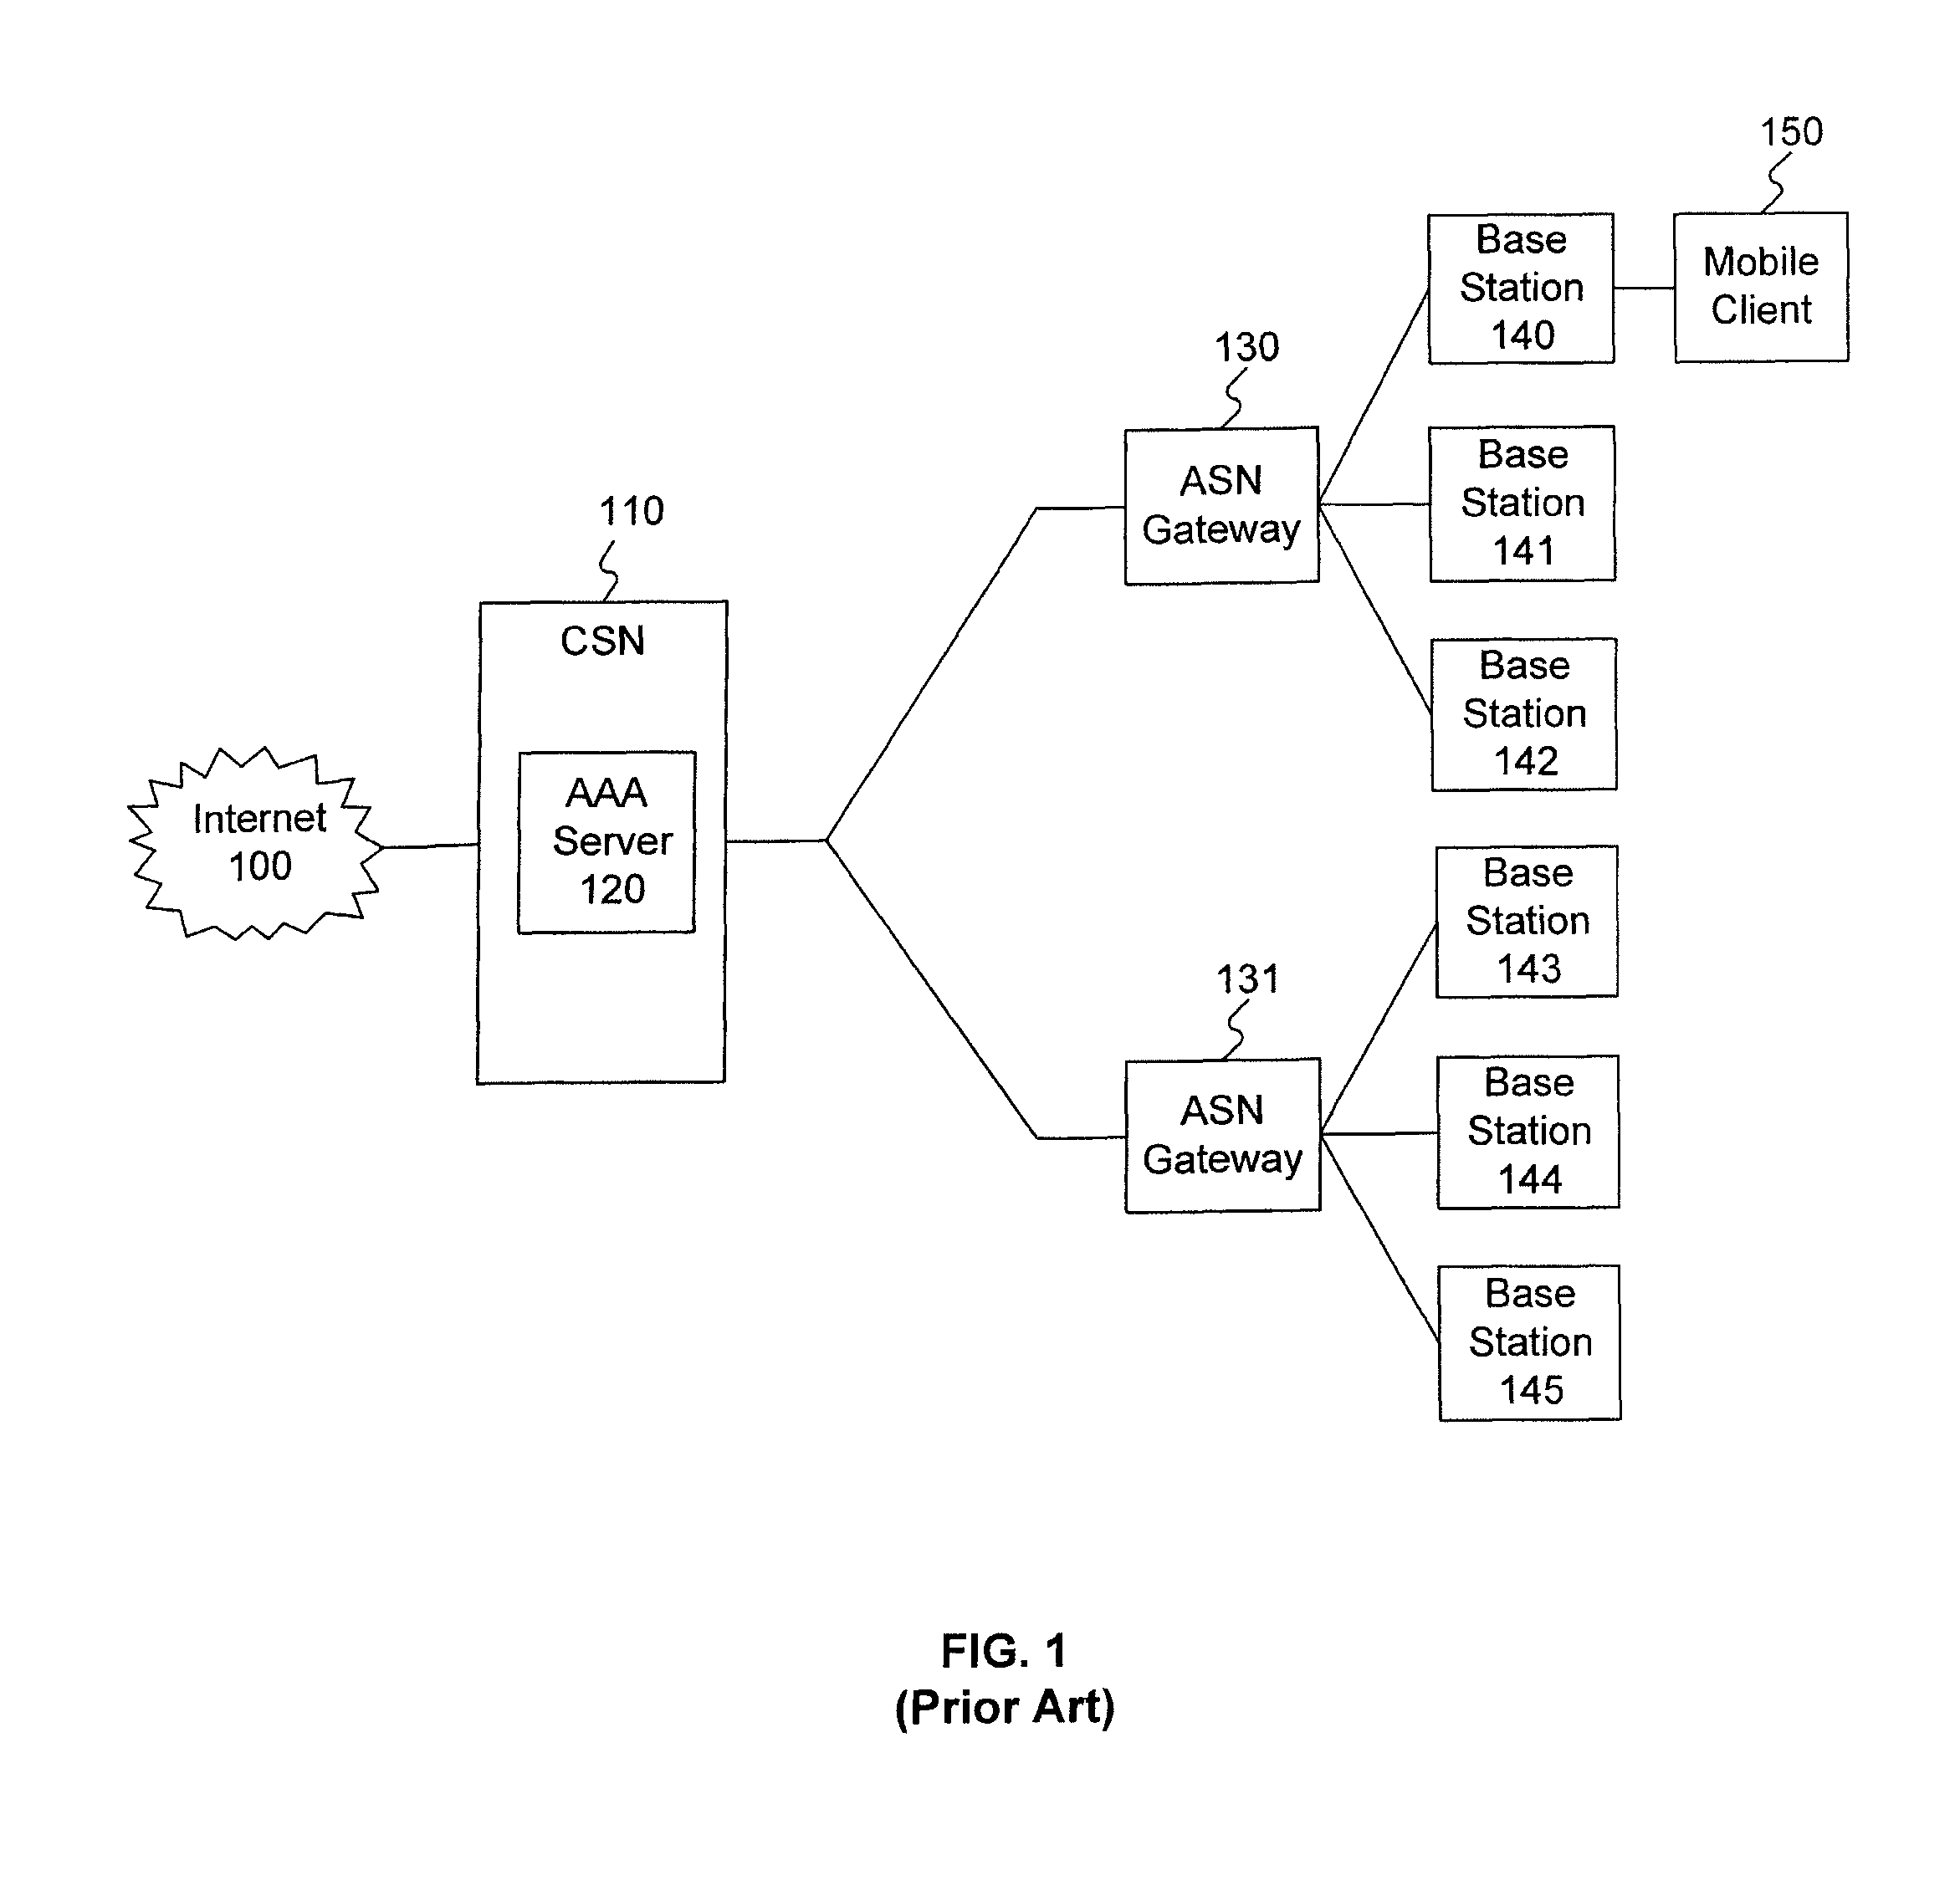
Owner:IND TECH RES INST
Lightweight cross-domain identity authentication method and system in Internet of Vehicles environment
ActiveCN119364359AParticular environment based servicesVehicle infrastructure communicationThe InternetEngineering
The invention discloses a lightweight cross-domain identity authentication method and a lightweight cross-domain identity authentication system in an Internet of Vehicles environment. The method comprises the following steps: a vehicle and each roadside unit register to a trusted mechanism; the vehicle and the first roadside unit authenticate each other to establish a first communication key; the to-be-cross-domain vehicle sends a cross-domain notification to the first roadside unit by using the first communication key, and the first roadside unit sends the cross-domain notification to the second roadside unit; the second roadside unit judges whether to communicate with the to-be-cross-domain vehicle for the first time or not based on the cross-domain notification; if yes, the second roadside unit obtains an authentication parameter of the vehicle to be subjected to domain crossing; if not, the second roadside unit reads an authentication parameter of the vehicle to be subjected to domain crossing; and the to-be-cross-domain vehicle travels to the domain of the second roadside unit, and the to-be-cross-domain vehicle and the second roadside unit perform mutual authentication based on the authentication parameter to establish a second communication key. According to the invention, seamless switching authentication between the cross-domain vehicle and the roadside unit can be ensured.

Owner:NANJING UNIV OF INFORMATION SCI & TECH
Multi-user authentication method and system for mobile communication scene and information processing terminal
PendingCN114286334AReduce the probability of congestionImprove securitySecurity arrangementNetwork architectureEngineering
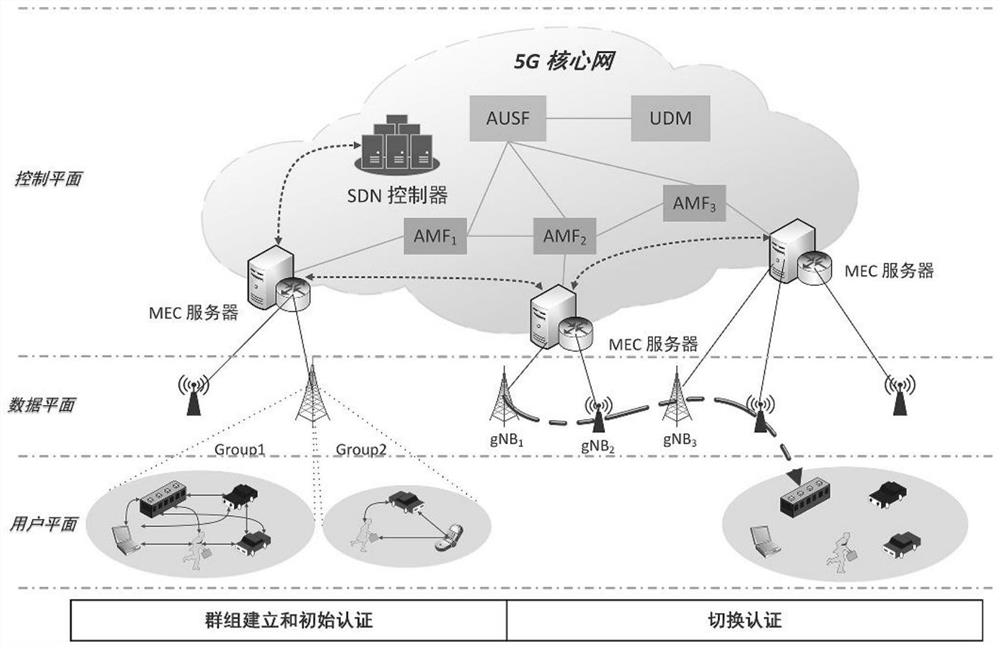
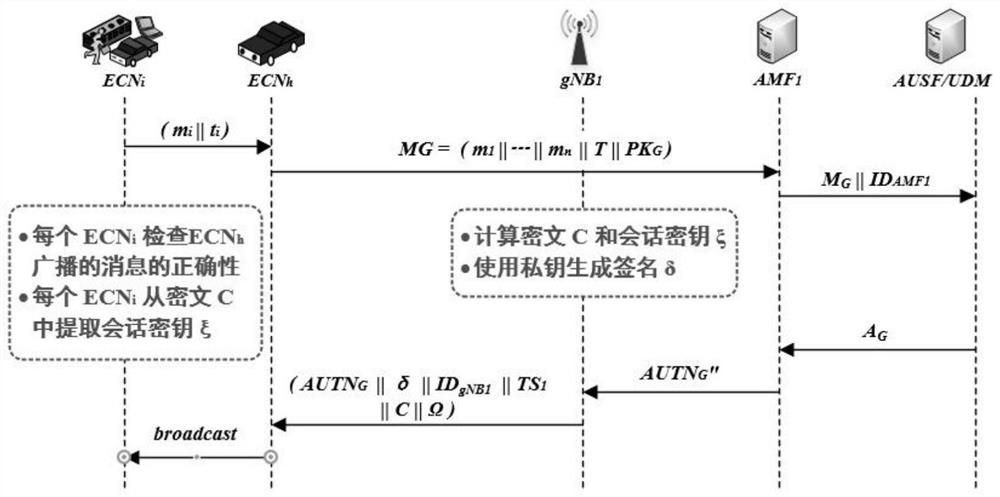
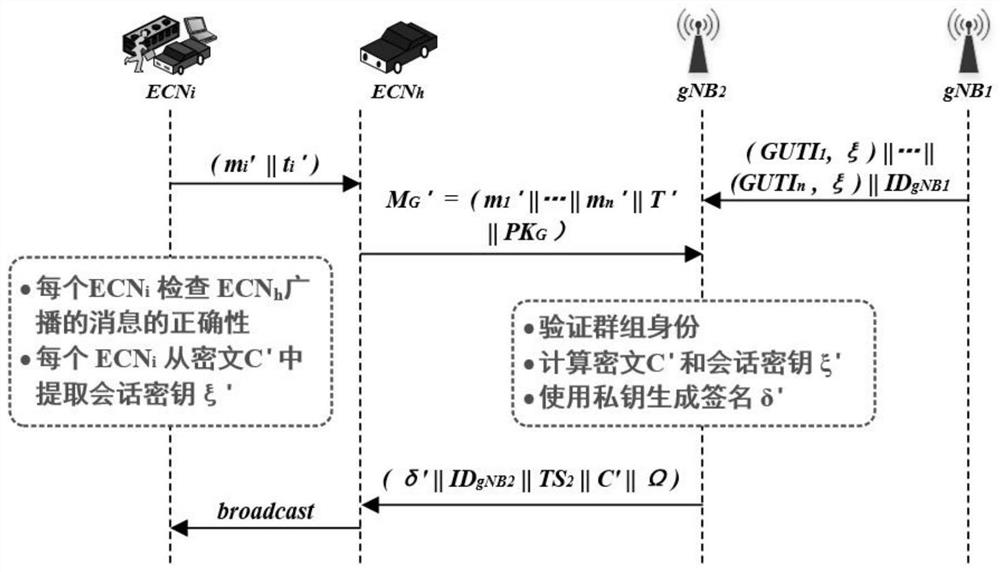
The invention belongs to the technical field of network communication, and discloses a multi-user authentication method and system for a mobile communication scene and an information processing terminal. An initial authentication stage; and switching the authentication stage. According to the method, a multi-user authentication scheme is designed by using an aggregation message authentication code with a detection function and a contribution-based broadcast encryption technology based on MEC and SDN technologies, so that the channel congestion probability is reduced, the calculation overhead and communication overhead of switching authentication are reduced, the switching authentication time delay is reduced, and the safety performance of group authentication is improved. According to the invention, the network architecture integrated by the SDN and the MEC server can monitor the network state in real time according to the dynamic topology of the user in advance to make a switching decision, a large amount of calculation overhead can be completed before switching authentication, and the switching authentication time delay is effectively reduced. And the group messages are aggregated, so that the number of times of signaling interaction can be effectively reduced, and the possibility of channel congestion is reduced.
Owner:XIAN UNIV OF POSTS & TELECOMM
Fast batch switching authentication method for predictability and aggregation promise proof
PendingCN119628836Areduce calculationReduce communication overheadKey distribution for secure communicationPublic key for secure communicationHash functionTimestamp
The invention discloses a rapid batch switching authentication method for predictability and aggregation promise proof, which realizes batch authentication of a plurality of user terminals by generating system parameters and secret keys through a trust mechanism and combining predictability promise and aggregation signature technologies. In the authentication process, the edge base station to be switched exchanges with the current communication edge base station through an encrypted message, verification information such as a pre-authentication certificate and a signature is generated through the user terminal, and identity authentication is completed step by step. The method comprises the following specific steps: a trust mechanism generates a private key, a public key, a pseudo identity and an expiration timestamp for each device; through multiple rounds of message exchange, the edge base station and the user terminal perform identity verification by using a shared key and a hash function; and finally carrying out efficient verification on a plurality of users through batch signature and aggregation commitment. According to the method, on the basis of ensuring the security, the speed of switching the authentication process is greatly improved, and the method is suitable for a large-scale network environment, especially in edge computing and mobile communication networks.

Owner:SHANGHAI MARITIME UNIVERSITY +1
UAV assistance-based Internet of Things equipment multi-cluster concurrent access and switching authentication method
ActiveCN119325088Aensure safetyAssess restrictionUser identity/authority verificationEmbedded systemHandover authentication
The invention discloses an Internet of Things equipment multi-cluster concurrent access and switching authentication method based on UAV assistance, and the method comprises the steps: achieving the offline registration of a UAV and each Internet of Things equipment cluster through a ground network, introducing a long-term shared key for the UAV in a registration stage, and introducing a PUF challenge value for each Internet of Things equipment cluster; in the unmanned aerial vehicle access verification stage, based on a shared key mechanism, the unmanned aerial vehicle safely and efficiently accesses the ground network; the Internet of Things equipment multi-cluster concurrent access authentication stage is based on a PUF mechanism, and the unmanned aerial vehicle assists the ground multi-cluster Internet of Things equipment to complete concurrent access authentication; when the new unmanned aerial vehicle is switched in the multi-cluster concurrent switching authentication stage of the Internet of Things equipment, the multi-cluster Internet of Things equipment can quickly and safely complete switching with the new unmanned aerial vehicle based on the shared key between the UAVs. According to the invention, safe and efficient multi-cluster concurrent access and switching authentication of the unmanned aerial vehicle assisted Internet of Things equipment are realized.

Owner:XIDIAN UNIV
Handover Authentication Method with Privacy Preservation in LTE/Lte‑A Networks
InactiveCN103781067BRealize privacy protectionReduce handover authentication delaySecurity arrangementKey exchangeHash function
The invention discloses a handover authentication method with privacy protection in an LTE / LTE-A network. After an ME accesses the LTE / LTE-A network for the first time and successfully completes access authentication with an AAA server, the AAA server generates a Pseudonym set; when ME needs to switch to a new AP due to movement, it only needs to select an unused pseudonym from the pseudonym set for identity authentication without providing the real identity of ME, thereby avoiding the leakage of user identity and location privacy , to achieve anonymity and untraceability. In the handover authentication process, the method negotiates keys based on the Diffie-Hellman key exchange algorithm, completes the mutual authentication process through hash function value verification, does not use bilinear pairing operations, and reduces authentication delay.
Owner:NANJING UNIV OF SCI & TECH
Security authentication method based on chameleon hash function
ActiveCN113890740AGuarantee authenticityAvoid Malicious OperationsKey distribution for secure communicationUser identity/authority verificationCommunications securityHash function
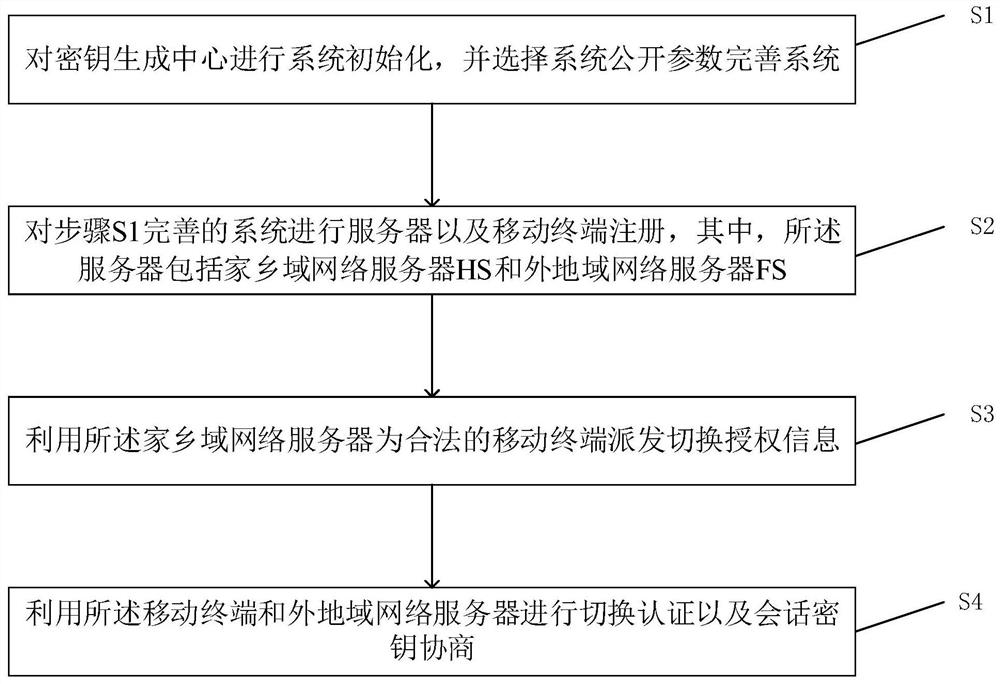
The invention discloses a safety certification method based on a chameleon hash function, which relates to the field of wireless communication safety certification of heterogeneous wireless networks and mainly comprises the following operation steps of: firstly, system initialization is performed on a key generation center to select the system public parameters and finish system establishment; the home domain network server HS completes registration; the foreign region network server FS completes registration; the mobile terminal MT completes registration; the home domain network server HS distributes switching authorization information to a legal and credible mobile terminal MT; and the mobile terminal MT and the foreign region network server FS complete authentication switching and session key negotiation. According to the method, the security real-time authentication of the mobile terminal and the foreign region network in the heterogeneous wireless network can be effectively realized, and the identity privacy of the mobile terminal and the resistance to temporary private key leakage and replay attacks are ensured. Moreover, in the authentication process, the mobile terminal consumes less resources.
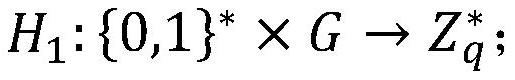
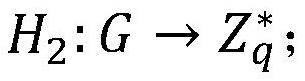
Owner:SOUTHWEST JIAOTONG UNIV
Group pre-handover authentication method based on fixed path, high-speed rail network communication platform
ActiveCN109769248BCorrect valid hashReduce switching overheadKey distribution for secure communicationUser identity/authority verificationPathPingEngineering
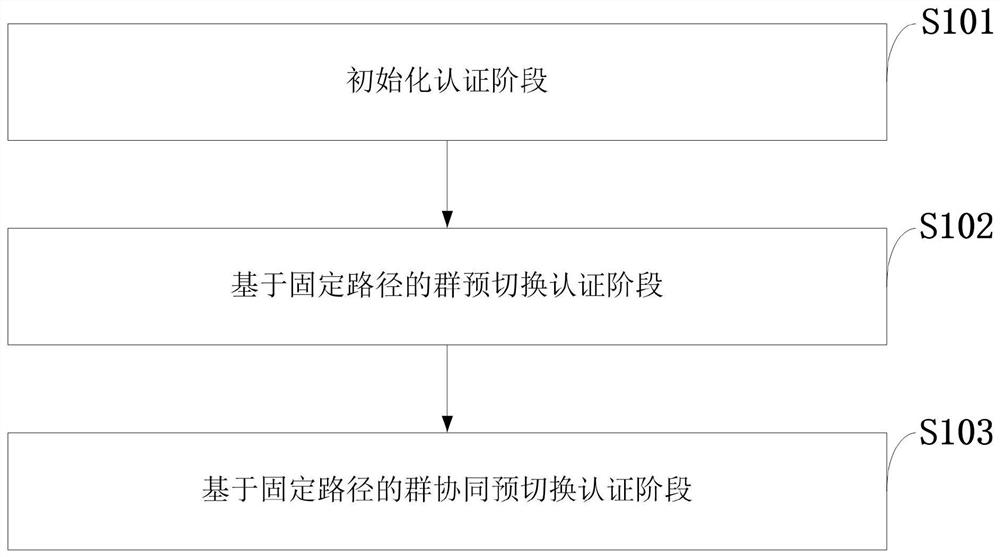
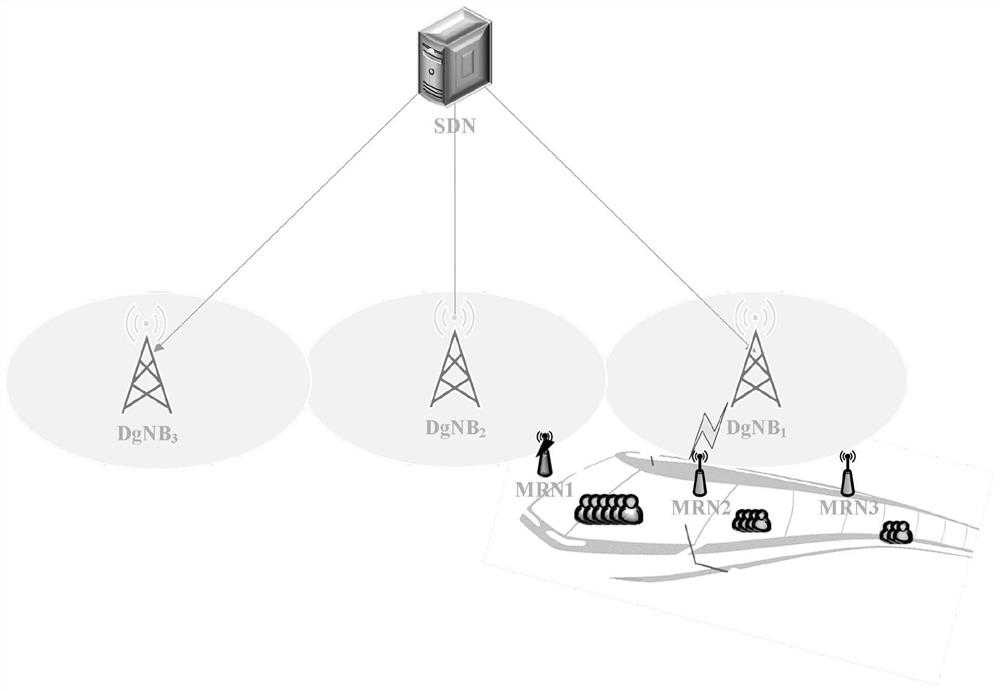
Owner:XIDIAN UNIV
UAV-assisted multi-cluster concurrent access and switching authentication method for IoT devices
The present invention discloses a method for concurrent access and handover authentication of multiple IoT devices assisted by UAVs. The method comprises: offline registration of the UAV and each IoT device cluster via a ground network. During the registration phase, a long-term shared key is introduced for the UAV and a PUF challenge value is introduced for each IoT device cluster. During the UAV access verification phase, based on a shared key mechanism, the UAV securely and efficiently accesses the ground network. During the concurrent access authentication phase of multiple IoT devices, based on a PUF mechanism, the UAV assists the ground multi-cluster IoT devices in completing concurrent access authentication. During the concurrent handover authentication phase of multiple IoT devices, when switching to a new UAV, based on the shared key between the UAVs, the multi-cluster IoT devices can quickly and securely complete the handover with the new UAV. The present invention implements secure and efficient UAV-assisted concurrent access and handover authentication of multiple IoT devices.

Owner:XIDIAN UNIV
Method and system for data feedback
ActiveCN111738736BImplement feedbackImprove experienceDevices with sensorCo-operative working arrangementsEngineeringHandover authentication
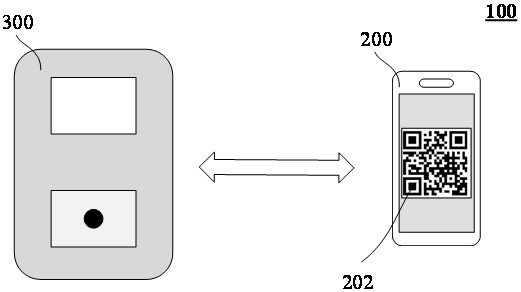
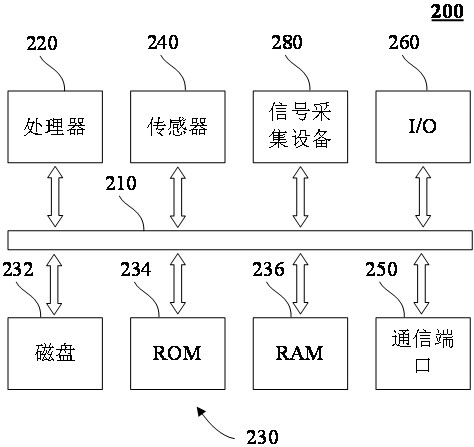
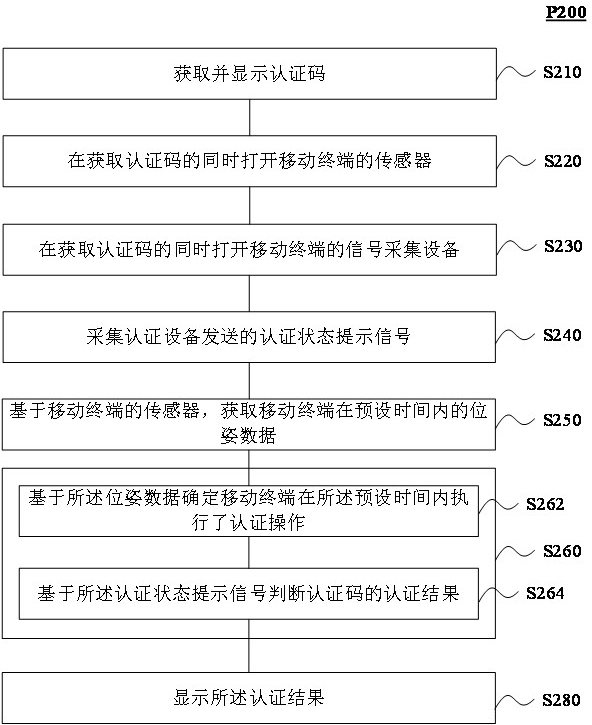
The data feedback method and system provided in this manual, after the mobile terminal calls out the authentication code, collect the pose data of the mobile terminal through the sensor of the mobile terminal, and collect the code scanning authentication status prompt signal of the authentication device through the signal collection device of the mobile terminal ; and judge whether the mobile terminal has made an action of scanning code authentication according to the pose data; judge the result of code scanning authentication according to the collected code scanning authentication status prompt signal, and display the authentication result on the page of the mobile terminal. The method and system can immediately feed back the code scanning authentication result to the mobile terminal when the authentication device or the mobile terminal is offline, and prompt the mobile terminal to switch the authentication code after the code scanning fails. In this way, real-time feedback of data in an offline state can be realized, and the user experience can be improved.
Owner:ALIPAY (HANGZHOU) INFORMATION TECH CO LTD
Ticket-based access layer handover authentication method for LTE-R vehicle-ground communication
ActiveCN108337661BAvoid participationReduce complexityKey distribution for secure communicationParticular environment based servicesCommunications securityIn vehicle
A kind of LTE-R vehicle-ground communication access layer switching authentication method based on ticket, its step mainly is: A, apply for ticket: vehicle-mounted mobile unit applies for and preserves target ticket and target base station ticket; B, X2 interface handover authentication: vehicle-mounted The mobile unit uses the target base station ticket to complete the authentication and key negotiation process with the target base station safely and efficiently, realizing fast handover across base stations and avoiding the participation of the source base station; The management entity completes the authentication process safely and efficiently, and completes the authentication and key negotiation process with the target base station with its help, avoiding the participation of the source mobile management entity and the source base station, and quickly realizing handover across mobile management entities; this method effectively realizes In the LTE-R system, the secure real-time access layer handover authentication of vehicle-ground wireless communication improves the efficiency of handover authentication on the basis of ensuring security.
Owner:SOUTHWEST JIAOTONG UNIV
Group pre-switching authentication method and device based on trusted relay
ActiveCN114390516AAchieve mutual authenticationPromote sustainable developmentSecurity arrangementTerminal equipmentTrunking
The invention discloses a group pre-switching authentication method and device based on a trusted relay, and the method comprises the steps: carrying out the group authentication of a user terminal through the trusted relay, and recording the information of the user terminal passing the authentication to a pre-switching set; predicting the track of the user terminal in the pre-switching set to obtain a target base station of the user terminal; and comparing the current base station coverage range of the user terminal with the position information of the user terminal, and switching the user terminal to a target base station by using a trusted relay when the position of the user terminal exceeds the current base station coverage range. The group pre-switching technology and the trusted execution technology are combined, group switching can be rapidly and safely carried out, it is guaranteed that the 5G network can provide smooth and safe communication experience for users in the train running process, the switching problem of mass terminal devices in the current 5G network in the high-speed moving process is solved, and the user experience is improved. The method is high in applicability and safety, and switching overhead consumption is reasonable.
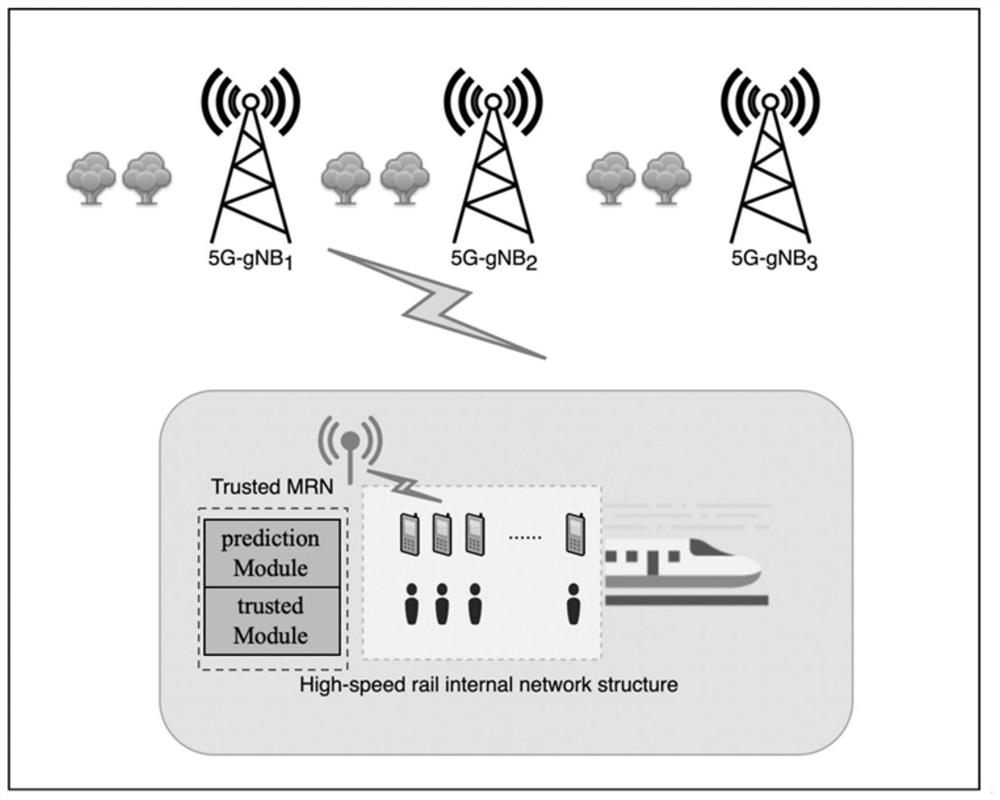
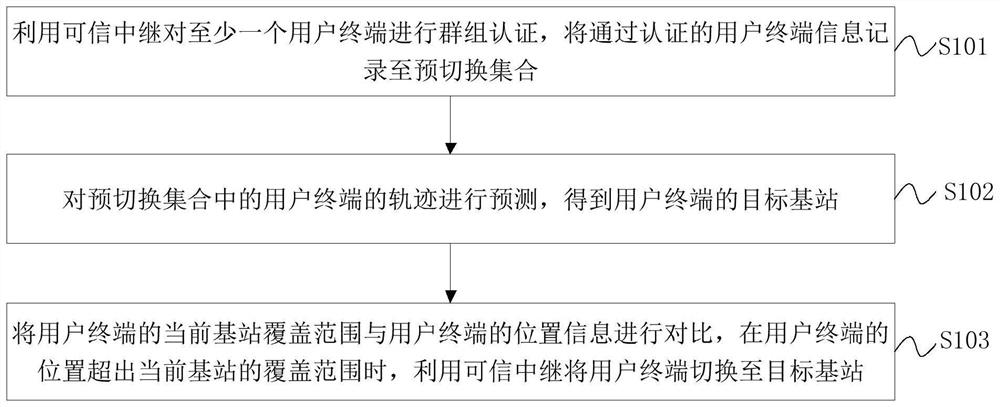
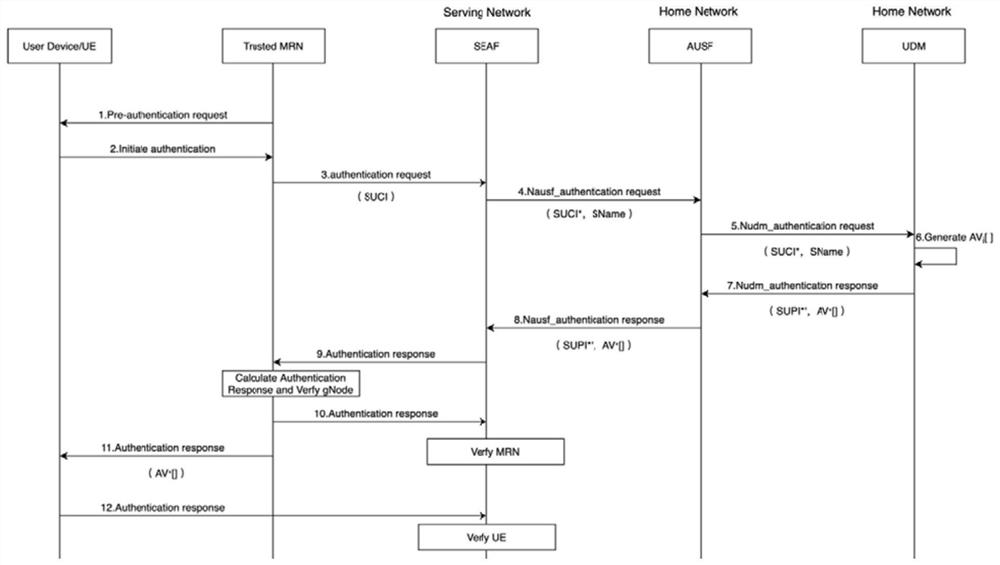
Owner:BEIHANG UNIV
An anonymous handover authentication method based on false identity in wireless network
ActiveCN106856605BSolve anonymous authenticationImplement a batch authentication strategyTransmissionSecurity arrangementThird partyInternet privacy
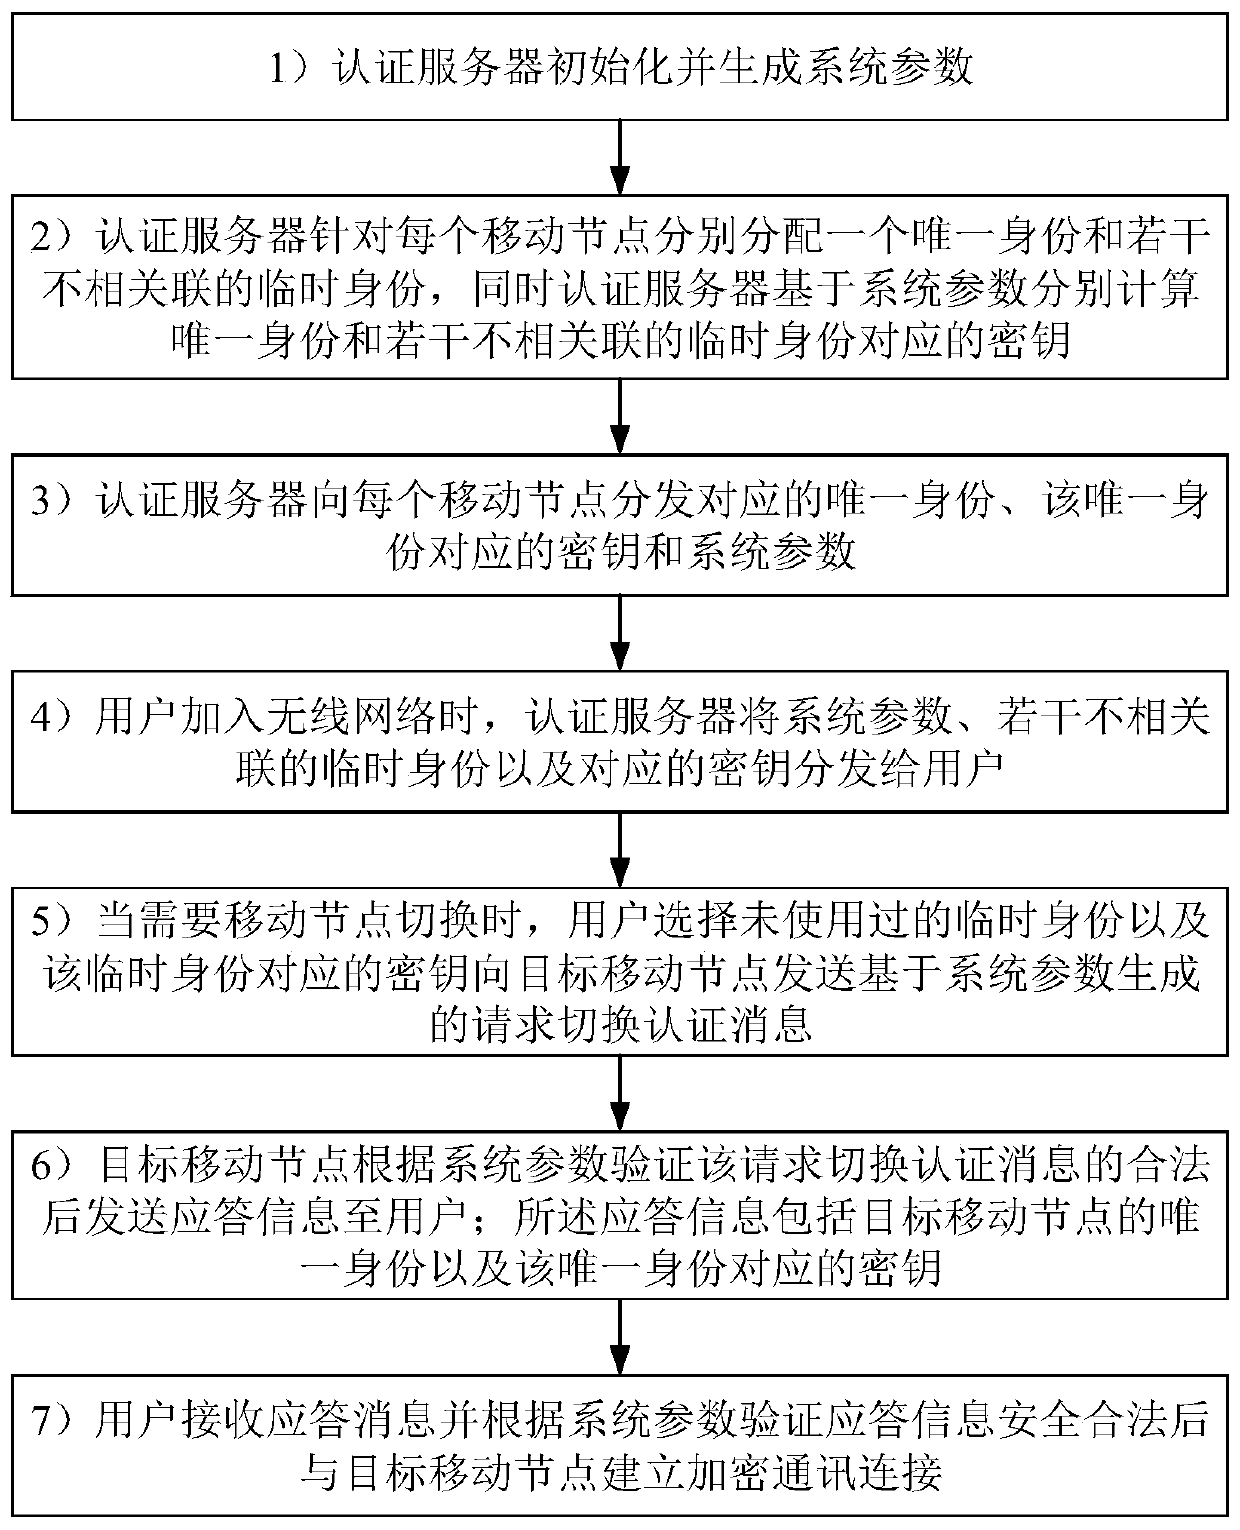
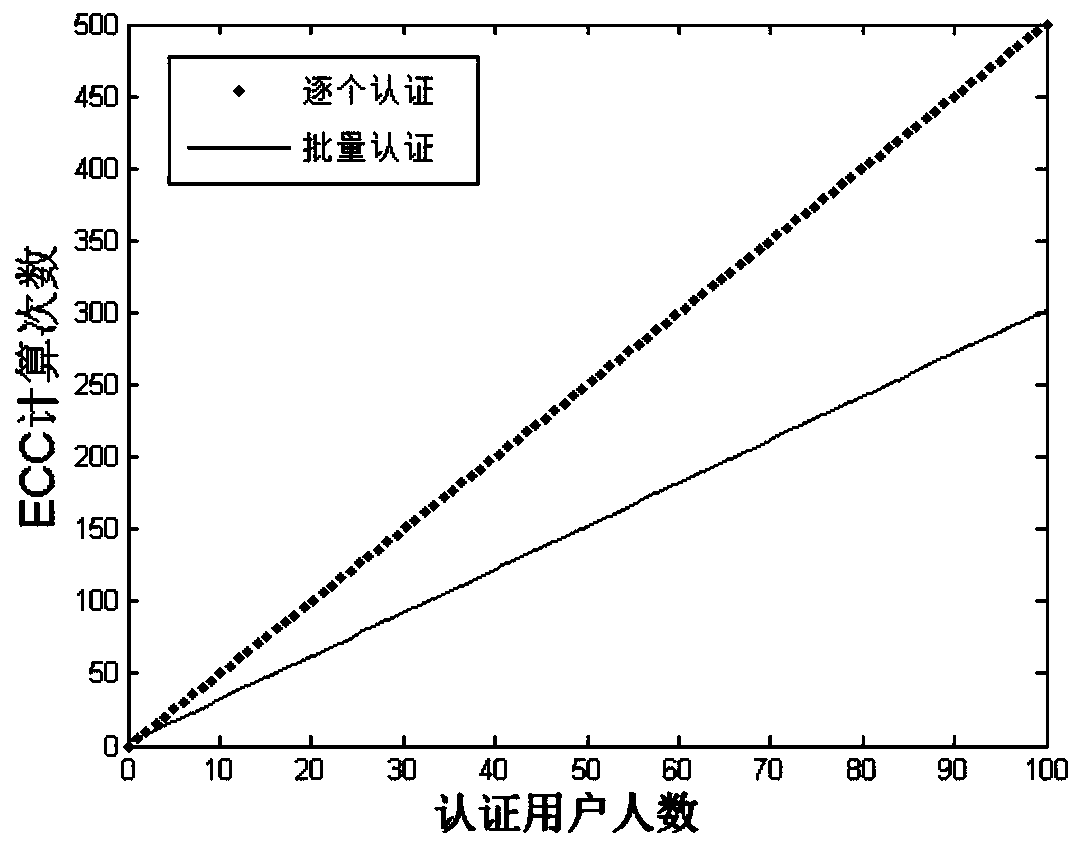
The invention discloses a false identity based wireless network anonymous switching authentication method, which comprises the steps that 1) an authentication server generates system parameters; 2) the authentication server respectively allocates a unique identity and temporary identity and a corresponding key for each mobile node; 3) the authentication server distributes the system parameters and the corresponding unique identities and keys to the mobile nodes; 4) the authentication server distributes the system parameters, the temporary identities and the keys to users; 5) the user sends a switching authentication request message to a target mobile node by selecting an unused temporary identity and key; 6) the target mobile node verifies the legitimacy of the switching authentication request message and then sends a response message to the user; and 7) the user verifies the response message to be safe and legal and then establishes encrypted communication connection with the target mobile node. According to the invention, participation of a third-party is not required, anonymous switching authentication is completed through twice handshaking, privacy information of the users is protected, batch authentication is supported, and the efficiency of simultaneous authentication requested by multiple users is improved.
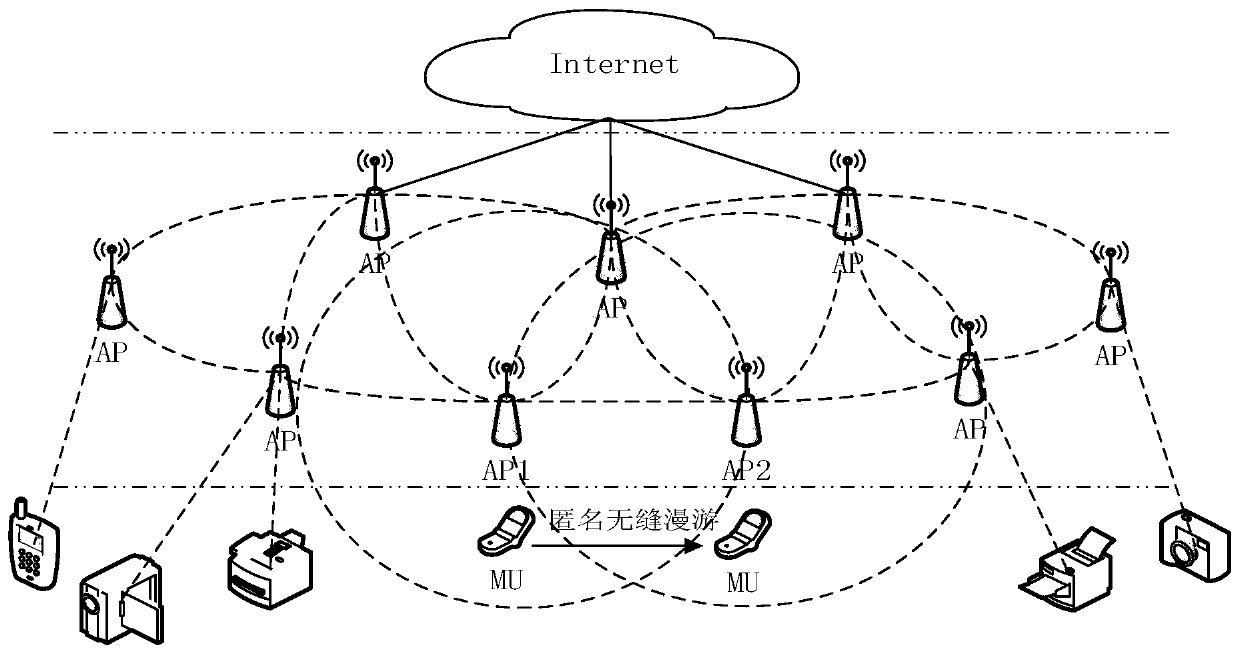
Owner:福建中信网安信息科技有限公司
An efficient switching authentication method based on the state secret SM9 supporting batch authentication
ActiveCN117459935BUser identity/authority verificationSecurity arrangementMan-in-the-middle attackAttack
The present application relates to a kind of efficient switching authentication method based on state secret SM9 supports batch authentication.First, system initialization is carried out and relevant parameters are disclosed, and the identity information and signature private key of user and access point joining network are obtained.In the process of user movement, when the signal of connected access point is lower than threshold value, user will request switching authentication to the access point with stronger signal.The authentication process of the method of the present application only needs 2 times of handshaking, and supports batch authentication in dense user scene, with higher authentication efficiency.Not only meet the security requirements such as bidirectional authentication and key consistency, traceability, anti-replay attack, anti-middleman attack and front / backward security, but also support state secret algorithm, with higher security.

Owner:FUJIAN NORMAL UNIV
Group access authentication and handover authentication methods and applications applicable to space-ground integration
ActiveCN112243235BPrivacy protectionImprove authentication efficiencyNetwork topologiesSecurity arrangementPrivacy protectionEngineering
Owner:XIDIAN UNIV
An identity-based authentication method for space-based networks
ActiveCN113079016BSmall message sizeAvoid transmissionKey distribution for secure communicationUser identity/authority verificationEngineeringNetwork communication
Owner:NAT UNIV OF DEFENSE TECH