

Patents
Literature
56 results about "Cyberinfrastructure" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
United States federal research funders use the term cyberinfrastructure to describe research environments that support advanced data acquisition, data storage, data management, data integration, data mining, data visualization and other computing and information processing services distributed over the Internet beyond the scope of a single institution. In scientific usage, cyberinfrastructure is a technological and sociological solution to the problem of efficiently connecting laboratories, data, computers, and people with the goal of enabling derivation of novel scientific theories and knowledge.
Electromagnetic pulse (EMP) hardened information infrastructure with extractor, cloud dispersal, secure storage, content analysis and classification and method therefor
ActiveUS8655939B2Improve the level ofImprove security levelDigital data processing detailsError detection/correctionElectromagnetic pulseContent analytics
A method and system processes data in a distributed computing system to survive an electromagnetic pulse (EMP) attack. The computing system has proximal select content (SC) data stores and geographically distributed distal data stores, all with respective access controls. The data input or put through the computing system is processed to obtain the SC and other associated content. The process then extracts and stores such content in the proximal SC data stores and geographically distributed distal SC data stores. The system further processes data to geographically distribute the data with data processes including: copy, extract, archive, distribute, and a copy-extract-archive and distribute process with a sequential and supplemental data destruction process. In this manner, the data input is distributed or spread out over the geographically distributed distal SC data stores. The system and method permits reconstruction of the processed data only in the presence of a respective access control.
Owner:DIGITAL DOORS
Secure digital information infrastructure
ActiveUS10652022B1Key distribution for secure communicationUser identity/authority verificationEngineeringInformation infrastructure
An authentication and encryption computer system is disclosed including processing devices, a network interface, and a data store. The authentication and encryption system is configured to maintain in the data store content common to a plurality of entities and content independently specified by each of the plurality of entities. The system is configured to receive a content request from an application executing on a mobile device, the content request comprising a secure access code corresponding to an entity, and the content request encrypted by the mobile device. An interface, comprising the content common to the plurality of entities, is customized to include content independently specified by the entity, wherein the content independently specified by the entity comprises a token value. A user request for an item presented via the interface is received and the token value is transferred to the entity.


Owner:OASIS MEDICAL
Transformer substation global Internet of Things system based on smart rod and 5G and operation method thereof
PendingCN112803594AReduce construction difficultyReduce management difficultyCircuit arrangementsInformation technology support systemCommunication unitInformation infrastructure
The invention discloses a transformer substation global Internet of Things system based on a smart rod and 5G and an operation method thereof. The transformer substation global Internet of Things system comprises a transformer substation monitoring center, the smart rod and information acquisition equipment, wherein the smart rod is internally provided with a power and environment management all-in-one machine and a hyper-fusion edge device; the power and environment management all-in-one machine is connected with the information acquisition equipment, acquires the information acquired by the information acquisition equipment, and monitors and judges the acquired information to obtain a monitoring and judging result; and the power and environment management all-in-one machine is connected with the hyper-fusion edge device, and after monitoring judgment result information is sent to the hyper-fusion edge device for convergence, calculation and / or storage processing, the processed information is transmitted to the transformer substation monitoring center through a 5G communication unit. According to the transformer substation global Internet of Things system, the intelligent rod and the 5G technology are combined, the intelligent rod is used for bearing the transformer substation global Internet of Things networking, the transformer substation information infrastructure construction can be realized, the transformer substation Internet of Things equipment can be flexibly accessed, managed and operated in a unified manner, and the construction and management difficulty of the transformer substation intelligent information infrastructure is reduced.


Owner:深圳电网智慧能源技术有限公司
National Health Information and Electronic Medical Record System and Method
InactiveUS20100153134A1Increase valueData processing applicationsPatient personal data managementInformation infrastructureDocument preparation
A system that creates a national health information infrastructure provides secure storage and retrieval of personal health information (PHI) while allowing health care providers to retain their preferred method of documentation (handwriting) for the majority of their documentation requirements. Unique codes associated with each handwritten document allow rapid access to the individual patient's PHI by healthcare providers. These unique codes also allow the system to associate the images of PHI documents with the individual (e.g. patient) to whom the PHI pertains.


Owner:ECAPABLE
Systems and methods for interconnected computing resources and event / activity identification information infrastructure using biometric identification of human proximity presence or presence
PendingCN119422143AUser identity/authority verificationInternal/peripheral component protectionBiologic AssaysEngineering
Interconnected computing enables the use of highly diverse environments that support a contemporary civilized operating framework. However, the computational productivity and credibility are disrupted by very immature organizations of this environment. Because current computing entity (e.g., resource) identification infrastructure designs lacking root identification reliability, these environments and their identity infrastructures are decentralized, and unnecessarily unreliable, unsecure, and inadequate of information. This reliability is achieved herein by a bioassay and activity-based portable identification and provenance infrastructure that is substantially accurate and authenticity guaranteed, close to the presence or the quality of the presence. The infrastructure provides ubiquitous available identification information, which can be commonly used in the identification process. Such biometric and activity-based identification information may be acquired contemporaneously and securely fused with or otherwise bound to an associated entity identification information set. This set is used to identify and evaluate entity suitability and / or authenticity, and / or to establish user identities (particular human entities) for individual, social and organizational activities.

Owner:ADVANCED ELEMENTAL TECHNOLOGIES INC
Method and System to Create a National Health Information Infrastructure
InactiveUS20100293001A1Digital data information retrievalDrug and medicationsPasswordProtected health information
A medication list management and electronic prescribing system incorporates a method of generating tamper-evident prescriptions on paper. Using password protected web pages, health care workers or patients can cause the transmission of machine-readable protected health information from the inventive system to another information management system using the tamper-evident prescriptions described. Non-participants can verify the authenticity of printed protected health information but are not able to create the automated transmission of this information from the inventive system to another information management system. This transmission of machine-readable protected health information has an economic value that is sufficient to be used as an inducement to health care providers across the industry to use a common information technology platform to accomplish such tasks.


Owner:ECAPABLE
Automatic driving system abnormal behavior detection method, automatic driving system degradation method and related equipment
The invention discloses an automatic driving system abnormal behavior detection method, an automatic driving system degradation method and related equipment, and the automatic driving system abnormal behavior detection method comprises the steps: detecting scene information, and outputting a scene classification label based on the scene information, the scene information comprises road information, traffic participant information, infrastructure information and / or temporary facility information, and the scene classification label is related to the own vehicle speed, the road information and the traffic participant information; a scene association threshold is determined based on the scene classification label, and the scene association threshold is in negative correlation with the severity level of a scene corresponding to the scene classification label after an accident occurs; and determining whether the vehicle has an abnormal behavior based on the scene information and the scene association threshold.


Owner:SZ ZHUOYU TECH CO LTD
Collection analysis and utilization linkage method for full life cycle of vulnerability intelligence
PendingCN121530613AKnowledge representationSecuring communicationCollection analysisCritical information infrastructure
The invention discloses a collection, analysis and utilization linkage method for the full life cycle of vulnerability intelligence, which comprises the following steps: respectively acquiring original vulnerability intelligence of a plurality of heterogeneous data sources, and carrying out standardization processing on the original vulnerability intelligence to obtain vulnerability description information; constructing an asset knowledge graph, wherein the asset knowledge graph is used for representing IT asset objects in the enterprise and dependency and deployment relationships among the IT asset objects; performing graph traversal query on the vulnerability description information based on an asset knowledge graph, and identifying an affected asset list affected by vulnerabilities; and according to a preset response strategy, generating a safety response instruction from the affected asset list and sending the safety response instruction to the safety protection system. According to the method, the asset knowledge graph is constructed and the multi-source vulnerability information is subjected to standardization and mapping correlation analysis, so that the accurate and rapid identification of the affected assets of the power system and the automatic response strategy generation are realized, and the efficiency and the accuracy of the vulnerability management of the key information infrastructure of the power grid are effectively improved.

Owner:HUANENG POWER INT INC +1
Secure digital information infrastructure
ActiveUS10979228B1Key distribution for secure communicationUser identity/authority verificationEngineeringInformation infrastructure
An authentication and encryption computer system is disclosed including processing devices, a network interface, and a data store. The authentication and encryption system is configured to maintain in the data store content common to a plurality of entities and content independently specified by each of the plurality of entities. The system is configured to receive a content request from an application executing on a mobile device, the content request comprising a secure access code corresponding to an entity, and the content request encrypted by the mobile device. An interface, comprising the content common to the plurality of entities, is customized to include content independently specified by the entity, wherein the content independently specified by the entity comprises a token value. A user request for an item presented via the interface is received and the token value is transferred to the entity.


Owner:OASIS MEDICAL
Non-technical source hierarchical rule base system and risk assessment method for critical information infrastructure
PCT designated stageWO2025251282A1Data processing applicationsOther databases indexingCritical information infrastructureRule-based system
Disclosed in the present invention are a non-technical source hierarchical rule base system and risk assessment method for critical information infrastructure. The present solution comprises: first, constructing a rule base of first-level index attributes and second-level rule attributes, so as to form a hierarchical rule base model; second, further classifying and analyzing non-technical source data, and using a confidence rule base model to assess non-technical source rule indexes and safety of a critical information infrastructure system; and finally, with regard to the safety risk situations of critical information infrastructure institutions, fusing and analyzing technical source information and non-technical source information, so as to provide a more accurate risk assessment result. On the basis of a critical information infrastructure safety assurance system, the present solution classifies rules into different levels, so as to improve the detection efficiency and accurate assessment of rule bases.

Owner:THE THIRD RES INST OF MIN OF PUBLIC SECURITY
Data cleaning method for ship information infrastructure fault diagnosis
PendingCN121255782ADigital data information retrievalSpecial data processing applicationsData setData pre-processing
The invention discloses a data cleaning method for ship information infrastructure fault diagnosis, and belongs to the field of data processing. The method specifically relates to a preprocessing method of ship information infrastructure monitoring data and a data cleaning method for distinguishing fault data and dirty data. Through data preprocessing, a consistent and complete data set is constructed for subsequent data cleaning. At the moment, abnormal values in the data set are divided into interference data and abnormal equipment states, the abnormal equipment state values have important significance for subsequent fault diagnosis, and the interference data can influence model training. According to the method, a mode of combining FP-Growth and DBSCAN algorithms is adopted, and the characteristics that cabin equipment is complex in coupling and one fault often generates derivative alarms are utilized, so that equipment fault points and interference points are reasonably distinguished. Through the ship information infrastructure fault diagnosis-oriented data cleaning method, the problems of fuzzy data quality and low model precision caused by application of traditional fault diagnosis to ship information infrastructures can be solved.

Owner:CHINA SHIPBUILDING RES INST (SEVENTH RES INST OF CHINA STATE SHIPBUILDING CORP)
Campus risk prevention and control system based on multi-modal data fusion and space-time modeling
The invention provides a campus risk prevention and control system based on multi-modal data fusion and space-time modeling, which relates to the technical field of campus safety management and comprises a multi-source data acquisition module, a space-time modeling module, a data fusion and alignment module, an intelligent risk analysis and early warning module and a visualization and linkage response module. The multi-source data acquisition module is used for acquiring multi-modal heterogeneous data from an existing campus information system and performing time sequence synchronization and desensitization processing; according to the method, multi-source data of existing campus videos, access control, wireless, consumption and mobile terminals and the like are integrated, monitoring blind areas and track breakpoints of a single data source are effectively eliminated through space-time alignment and semantic feature fusion, the accuracy and continuity of personnel positioning and track reconstruction are remarkably improved, existing information infrastructures of the campus are fully utilized, and the safety of the campus is improved. Special sensors or high-cost hardware do not need to be additionally installed on a large scale, deployment and maintenance cost is reduced, and the method can be suitable for campus scenes of different scales to be popularized and applied.

Owner:INTERNATIONAL COLLEGE OF RENMIN UNIVERSITY OF CHINA (SUZHOU RESEARCH INSTITUTE)
Asset fault identification method
PendingCN110765486ASave time and costSave labor costCharacter and pattern recognitionDigital data protectionInformatizationPrediction probability
The invention discloses an asset fault identification method, which is used for carrying out fault detection on information infrastructure assets. The method comprises: installing the baseboard management controller on the managed assets; constructing an operation and maintenance data network and an out-of-band management system, to obtain the managed asset operation information data collected bythe baseboard management controller; labeling and preprocessing the managed asset operation information data; and inputting the preprocessed managed asset operation information data into a constructedclassification model based on cost-sensitive learning so as to output a prediction probability that the asset is an equipment fault, and comparing the prediction probability with a set threshold value so as to judge whether the asset is fault equipment or not. According to the invention, the method solves a problem that a worker cannot quickly and accurately judge the fault equipment in the assetequipment and the defects of a fault sample in the prior art, achieves the informatization management of assets, and improves the work efficiency.


Owner:ELECTRIC POWER RESEARCH INSTITUTE, CHINA SOUTHERN POWER GRID CO LTD +1
Secure digital information infrastructure
ActiveUS20210111893A1Key distribution for secure communicationUser identity/authority verificationEngineeringInformation infrastructure
An authentication and encryption computer system is disclosed including processing devices, a network interface, and a data store. The authentication and encryption system is configured to maintain in the data store content common to a plurality of entities and content independently specified by each of the plurality of entities. The system is configured to receive a content request from an application executing on a mobile device, the content request comprising a secure access code corresponding to an entity, and the content request encrypted by the mobile device. An interface, comprising the content common to the plurality of entities, is customized to include content independently specified by the entity, wherein the content independently specified by the entity comprises a token value. A user request for an item presented via the interface is received and the token value is transferred to the entity.


Owner:OASIS MEDICAL
Railway information infrastructure safety management and control system based on data processing
The invention provides a railway information infrastructure security management and control system based on data processing. The system improves comprehensive detection and dynamic defense capabilities for railway network security threats. The method comprises the following steps: firstly, collecting network behavior elements at the edge of a network in real time by deploying a storage, calculation and transmission integrated unit, and generating a behavior chain data set by adopting clustering compression; thirdly, performing time sequence verification of compliance, credibility and logicality on the behavior chain based on a three-white baseline, and outputting a risk level and an attack path; and finally, in combination with a software-defined network controller, implementing multi-level elastic defense strategies such as link blocking, access control and information recording according to risk levels, and dynamically adjusting a detection threshold and an acquisition frequency through a closed-loop optimization mechanism. Through a sensing-evaluation-defense-optimization closed loop structure, the safety protection precision, the response efficiency and the resource adaptation capability of the railway information system are remarkably improved.

Owner:CHENGDU NOSAI INFORMATION TECHNOLOGY CO LTD
Abnormal access behavior identification method and system of power key information infrastructure system
The invention relates to the technical field of electric power monitoring, and provides an abnormal access behavior identification method and system for an electric power key information infrastructure system, and the method comprises the following steps: S1, collecting access log data, network flow data and system operation state data in the electric power key information infrastructure system, wherein the access log data comprises user identity information, access time and an access resource address; s2, cleaning, format conversion and feature extraction are performed on the collected data, noise and redundant information in the data are removed, the data in different formats are uniformly converted into formats suitable for analysis, and key features capable of reflecting access behavior features are extracted. By constructing an accurate normal access behavior model and adopting a scientific and reasonable deviation degree calculation method and a threshold judgment mechanism, normal access behaviors and abnormal access behaviors can be effectively distinguished, and the false alarm situation caused by fluctuation of the normal access behaviors is reduced.

Owner:国网思极网安科技(北京)有限公司
Information infrastructure management tools with extractor, storage and data release control functions and segmental data stores
Method and system of organizing and processing data in a distributed computing system having designated, distributed data stores for sensitive content (e.g., trade secrets) or select content (e.g., critical content). Sensitive / select data is extracted via configurable filters and stored in the designated data stores, sometimes subject to security controls, with limiting distribution functions and controlled release of the sensitive / select data. Distribution is limited due to designated, configurable filters.

Owner:DIGITAL DOORS INC
Key information infrastructure abnormity monitoring method and device
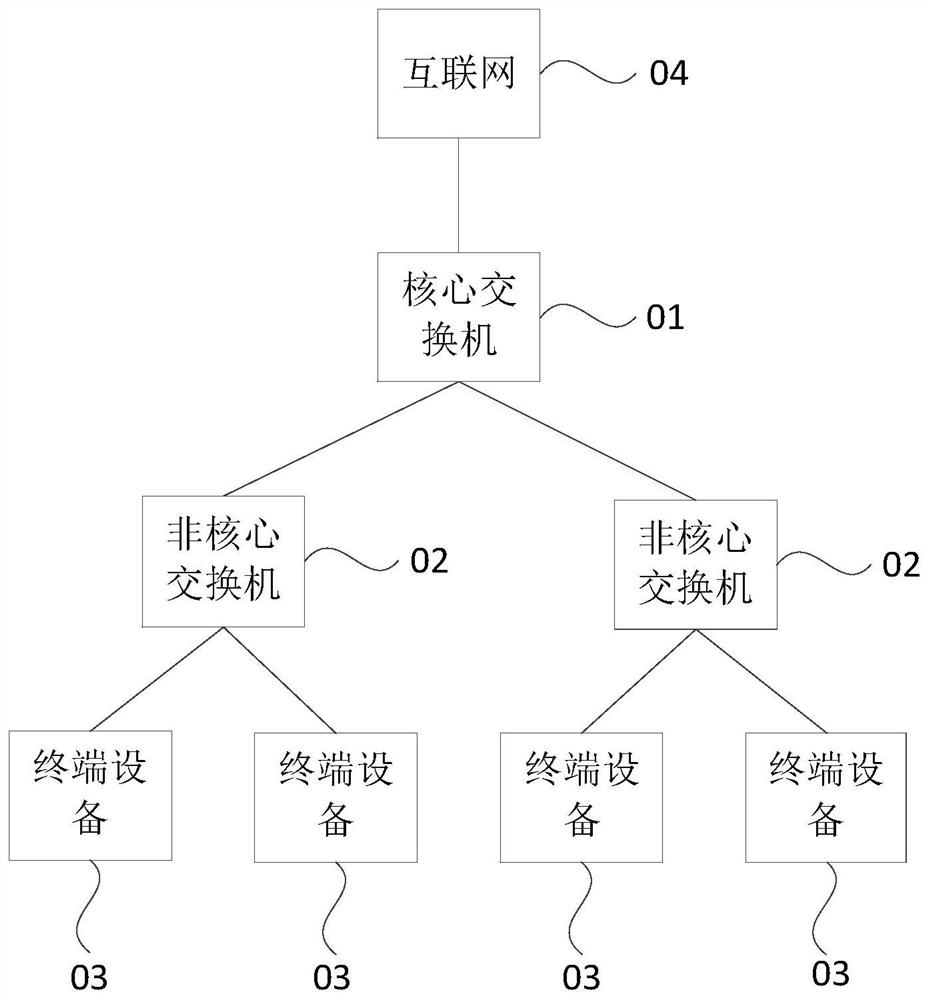
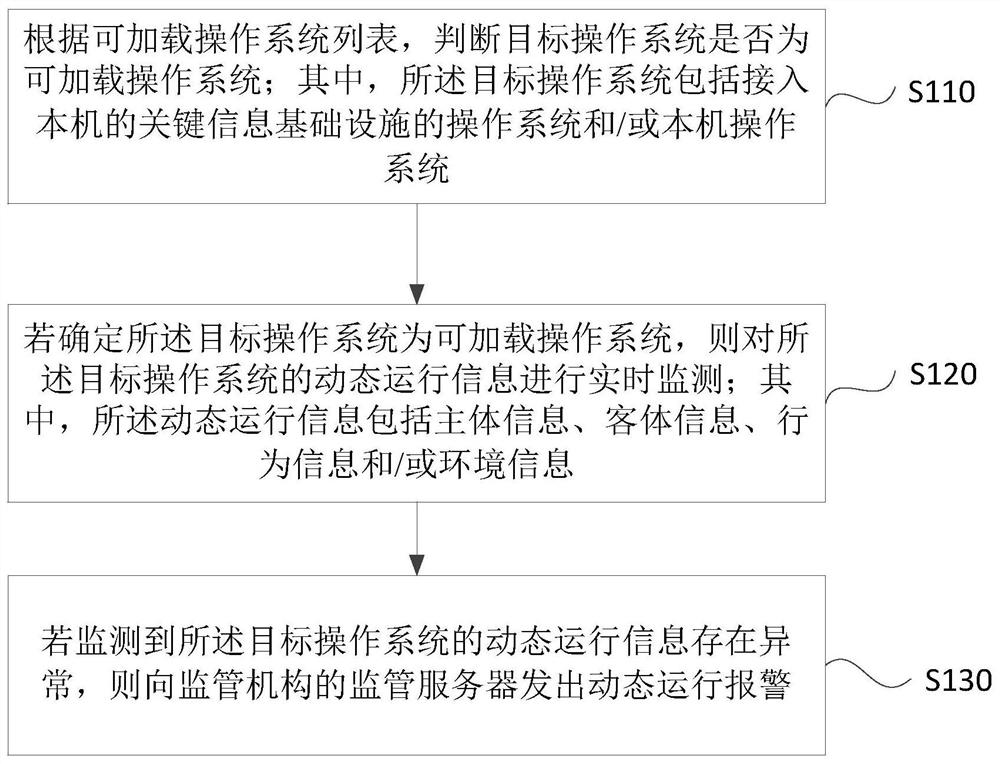
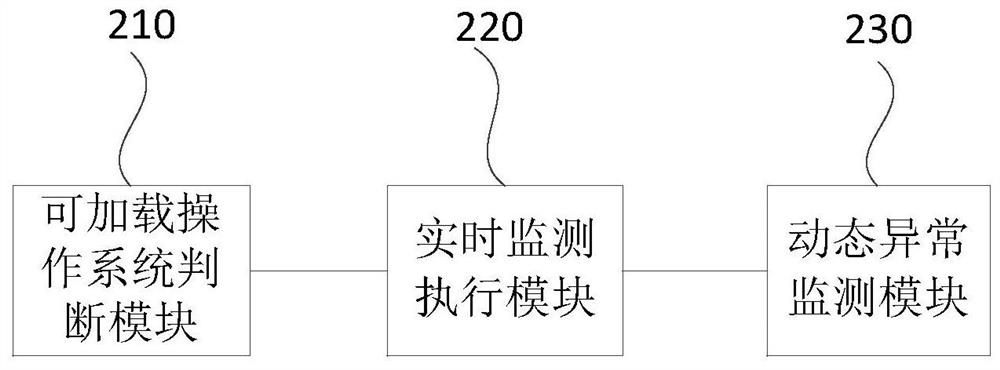
The embodiment of the invention discloses a key information infrastructure abnormity monitoring method and device, electronic equipment and a storage medium, and the method comprises the steps: judging whether a target operating system is a loadable operating system or not according to a loadable operating system list, wherein the target operating system comprises an operating system accessing a key information infrastructure of a local machine and / or a local operating system; if yes, monitoring the dynamic operation information of the target operation system in real time, wherein the dynamic operation information comprises subject information, object information, behavior information and / or environment information; and if it is monitored that the dynamic operation information of the target operating system is abnormal, sending a dynamic operation alarm to a supervision server of a supervision mechanism. According to the technical scheme provided by the embodiment of the invention, the dynamic operation information in the key information infrastructure is effectively monitored, and meanwhile, the communication connection with the supervision server of the supervision mechanism is established, so that the supervision mechanism can obtain the abnormal state of each key information infrastructure in time.
Owner:EVERSEC BEIJING TECH
Intelligent city information infrastructure planning system
PendingCN112115641AImprove efficiencyReduce labor costsDesign optimisation/simulationMulti-objective optimisationInfrastructure planningIntelligent city
The invention relates to an intelligent city information infrastructure planning system, which comprises a geographic information identification module for acquiring an image of a to-be-planned area and identifying various construction lands and infrastructures in the to-be-planned area through a convolutional neural network; the parameter calculation module is used for obtaining candidate planning point coordinates of the target infrastructure and calculating a planning score of the target infrastructure according to the candidate planning point coordinates and preset infrastructure evaluation parameters; the planning point position optimization module is used for acquiring candidate planning point coordinates of all the target infrastructures in the to-be-planned area, calculating planning scores of all the target infrastructures, carrying out multiple times of optimization according to an optimization algorithm, calculating the sum of the planning scores after each time of optimization, and obtaining a planning result; and taking the candidate planning point coordinates corresponding to all the target infrastructures when the sum of the planning scores is the highest as final infrastructure planning coordinates. Compared with the prior art, the method has the advantages of improving the efficiency of target infrastructure point selection in urban planning, reducing the laborcost in urban planning and the like.


Owner:TONGJI UNIV
A mechanical data import and export device with booster balance self-locking
ActiveCN111969364BEliminate the risk of human error operationEfficient import and export efficiencyCoupling device detailsInterprogram communicationControl engineeringInteractive technology
The invention discloses a mechanical data import and export device with force-increasing balance self-locking, which is characterized in that it includes a servo motor (1), a support frame (2), a reducer (3), and a screw slide rail assembly (4 ), position switch (5), booster balance self-locking linkage device, information storage device (9), shift block (11), lead screw (18), coupling (19), output shaft (20). The low-power servo motor is connected to the reducer, lead screw, slide rail, and balance push rod to drive the force-increasing balance self-locking linkage device, so that the sliding gold-plated pin is stable, and the high-precision docking and fixed gold-plated pin completes a data conduction. Using artificial intelligence to efficiently solve the problem of inefficient data interaction in the existing isolated network, fill the gap in the efficient data interaction technology of the isolated network, and provide a new solution for the national key information infrastructure field to ensure national security and national security. Infrastructure and other information security.


Owner:北京力普信风科技有限公司
Power monitoring system vulnerability index prediction method based on text classification and related device
PendingCN121479789AData processing applicationsPlatform integrity maintainanceElectric power systemSemantic feature
The invention discloses an electric power monitoring system vulnerability index prediction method based on text classification and a related device, and belongs to the technical field of electric power monitoring system vulnerability evaluation. The method comprises the following steps: firstly, constructing an evaluation system comprising specific environment indexes of a power system, extracting deep semantic features of a vulnerability description text through a lightweight pre-training language model DistilBERT, and realizing parallel prediction of multiple indexes such as attack vectors and permission requirements by adopting a multi-task learning framework. And carrying out interpretability analysis on a model decision process by combining an integrated gradient algorithm, and identifying key semantic features influencing a prediction result. According to the method, the automation level and the result credibility of vulnerability assessment are effectively improved, and intelligent technical support is provided for security protection of power key information infrastructures.

Owner:STATE GRID ANHUI ELECTRIC POWER CO LTD +3
Railroad facility management support system, railroad facility management support method, and railroad facility management support program
To provide a railroad facility management support system in which the distance between two points along a railroad route can be calculated more accurately than before without visiting the site.SOLUTION: A railroad facility management support system 80 comprises a request acceptance unit 84, a retrieval processing unit 85, a distance calculation unit 86, a support information generating unit 87, and a data transmission unit 88. The request acceptance unit 84 accepts a distance calculation request including facility identification information for identifying one facility and another facility installed or planned to be installed, and a calculation instruction of the distance between two facilities. The retrieval processing unit 85 acquires the absolute positions of the facilities identified by the facility identification information from the absolute position information-based information and also acquires the kilometric position of the specified facilities from facility information. The distance calculation unit 86 calculates the distance between the two facilities using the absolute positions of them. The support information generating unit 87 generates support information including the kilometric position between the two facilities and the distance between the two facilities. The data transmission unit 88 transmits the support information.SELECTED DRAWING: Figure 7

Owner:MITSUBISHI ELECTRIC CORP
Mechanical data import and export device with reinforcement balance self-locking function
ActiveCN111969364AImplement import and exportComplete Behavior AuditCoupling device detailsInterprogram communicationLinkage (mechanical)Control engineering
The invention discloses a mechanical data import and export device with a reinforcement balance self-locking function. The device is characterized by comprising a servo motor (1), support frame (2), speed reducer (3), a lead screw slide rail assembly (4), position switch (5), a reinforcement balance self-locking linkage device, an information storage device (9), a shifting block (11), a lead screw(18), a coupling (19) and an output shaft (20). The import and export device is connected with a speed reducer, a lead screw, a sliding rail and a balance push rod through a low-power servo motor todrive the reinforcement balance self-locking linkage device, so that a sliding gold-plated contact pin is stably butted and fixed at high precision to finish one-time data conduction. The problem thatexisting isolation network data interaction is low in efficiency is efficiently solved in an artificial intelligence mode, the blank of the isolation network efficient data interaction technology isfilled up, a new solution is provided for the field of national key information infrastructure, and national safety, national infrastructure and other information safety are guaranteed.


Owner:北京力普信风科技有限公司
Fault information processing system and electronic equipment
The invention provides a fault information processing system and electronic equipment, and belongs to the technical field of information infrastructure. The system comprises a control unit, a data collection unit and a data storage unit on a main control unit, the control unit comprises a bus interface, and the data collection unit comprises a management unit. The control unit is configured to switch the multiplexer to the control unit through a selection signal, so that the bus interface is connected with the management unit through the multiplexer to form an I2C channel, the control unit is used as an I2C master end, and the management unit is used as an I2C slave end; when the main control unit is abnormal, the integrated HDT software is called, fault information is obtained through the I2C channel, and the fault information is stored in the data storage unit; and when the fault information collection is completed, sending the fault information to an external device, and carrying out fault analysis and processing. According to the invention, the control unit is used as the main end of the data collection unit for fault collection, so that the fault positioning time is shortened.

Owner:HYGON INFORMATION TECH CO LTD
Geographic sales allocation system for estimating the source of pharmaceutical sales
This invention provides a correspondence relationship extraction system that automatically extracts rationally linked medical institutions by calculating the geographical distance between pharmacies / drugstores and medical institutions using their latitude and longitude information, and setting appropriate distance thresholds based on the patient's travel range according to whether the institution is in an urban or rural area, as well as a method for estimating sales by medical institution on a recording medium. [Solution] The information processing system 100 normalizes the address information of pharmacies and medical institutions 110, obtains latitude and longitude using a geographic information API or the like 120, extracts medical institutions within a predetermined distance from the pharmacy 150, calculates a score inversely proportional to the distance to the extracted medical institutions 160, and allocates the pharmacy sales to each medical institution according to the score ratio 170. Furthermore, by outputting the allocation results and linking them with an analysis support platform, a probability model, and a sales support visualization tool 180, it provides an information infrastructure that contributes to understanding prescription practices, sales evaluation, and the advancement of marketing measures.

Owner:TCROSS INC
Method for detecting and updating website asset inactivation based on http response
ActiveCN110932928BTimely supervisionMitigating Inadequate Regulatory SituationsWeb data indexingTransmissionDomain nameRegulatory authority
The present invention provides a method for detecting and updating website asset inactivation based on HTTP response: it includes the following steps: obtaining the domain name of the website to be detected; Active status code, the website status is normal, the website does not need to be updated, the process is over, obtain the redirected website domain name, judge whether the redirected website domain name is the same as the website domain name to be detected, and crawl the redirected website title, hosting Unit and domain name filing information; the present invention mainly solves the problem that the website supervised by the network security supervision department is inactivated but cannot be updated in time. Most of the websites supervised by the regulatory authorities belong to critical information infrastructure. When the domain name and IP of the website are replaced, but the supervised unit fails to report to the regulatory department in time, the regulatory department will not conduct network security and other aspects of the new website. Supervision will lead to the problem of inadequate website security supervision.

Owner:HANGZHOU ANHENG INFORMATION TECH CO LTD
Method and system for nuclear power plant key information infrastructure asset management
The invention belongs to the field of nuclear power, and particularly relates to a nuclear power plant key information infrastructure asset management method and system, and the method comprises the steps: 1, designing a nuclear power plant key information infrastructure asset data field list; 2, intelligently drawing a network topological graph according to the nuclear power plant key information infrastructure asset data; 3, off-line acquisition, processing and storage are carried out on nuclear power plant key information infrastructure asset data; and 4, performing preventive maintenance analysis on the nuclear power plant key information infrastructure asset data. According to the invention, comprehensive, efficient and safe management of nuclear power plant key information infrastructure assets can be realized, and emergency purchase and equipment replacement frequency can be reduced by identifying problems in advance and taking measures.

Owner:CNNC NUCLEAR POWER OPERATION MANAGEMENT CO LTD
Key information infrastructure safety operation system and acquisition device
PendingCN121923793AUser identity/authority verificationBiological modelsCritical information infrastructureMarkov algorithm
The invention belongs to the technical field of safety operation, and particularly relates to a key information infrastructure safety operation system and an acquisition device, the system depends on a federated node network and a dual uplink criterion to realize whole-process safety management and control; the federated node network comprises a federated monitoring node subnet and a dynamic security mapping chain, the subnet is composed of multiple types of function nodes, and the mapping chain is constructed based on a block chain algorithm; the edge monitoring module analyzes a device state and distinguishes uplink and unuplink devices, and the risk assessment module combines a hidden Markov algorithm and an HSV mapping space to generate a risk map; the uplink monitoring module completes uplink judgment, real-time abnormity monitoring and downlink processing; through an SEIR model, a voting algorithm and the like, equipment identity verification, risk gradient visualization, abnormal early warning and dynamic uplink-downlink management and control are achieved, it is ensured that uplink equipment continuously meets the safety criterion, and the operation safety and stability of key information infrastructures are improved.


Owner:ZHEJIANG ZHENENG ELECTRIC POWER
Secure digital information infrastructure
ActiveUS20210111894A1Key distribution for secure communicationCustomer relationshipEngineeringInformation infrastructure
An authentication and encryption computer system is disclosed including processing devices, a network interface, and a data store. The authentication and encryption system is configured to maintain in the data store content common to a plurality of entities and content independently specified by each of the plurality of entities. The system is configured to receive a content request from an application executing on a mobile device, the content request comprising a secure access code corresponding to an entity, and the content request encrypted by the mobile device. An interface, comprising the content common to the plurality of entities, is customized to include content independently specified by the entity, wherein the content independently specified by the entity comprises a token value. A user request for an item presented via the interface is received and the token value is transferred to the entity.


Owner:OASIS MEDICAL
Website asset inactivation detection and updating method based on HTTP response
ActiveCN110932928ATimely supervisionMitigating Inadequate Regulatory SituationsWeb data indexingData switching networksDomain nameWeb site
The invention provides a website asset inactivation detection and updating method based on HTTP response. The website asset inactivation detection and updating method comprises the following steps: acquiring a to-be-detected website domain name; requesting the domain name to obtain an HTTP state code from a server; judging whether the website belongs to an inactive state code, if the website belongs to the inactive state code, the website state is normal, the website does not need to be updated, the process is ended, obtaining a redirected website domain name, judging whether the redirected website domain name is the same as a to-be-detected website domain name, and crawling a title, a host unit and domain name record information of the redirected website; the method mainly solves the problem that the website supervised by the network security supervision department is inactivated but cannot be updated in time. Most websites supervised by a supervision department belong to key information infrastructures, and when domain names and IPs of the websites are replaced and supervised units do not report the websites to the supervision department in time, the supervision department cannotsupervise new websites in the aspects of network security and the like, so that the problem that the website security is not supervised in place is solved.

Owner:HANGZHOU ANHENG INFORMATION TECH CO LTD