

Patents
Literature
1146 results about "Functional safety" patented technology
Efficacy Topic
Property
Owner
Technical Advancement
Application Domain
Technology Topic
Technology Field Word
Patent Country/Region
Patent Type
Patent Status
Application Year
Inventor
Functional safety is the part of the overall safety of a system or piece of equipment that depends on automatic protection operating correctly in response to its inputs or failure in a predictable manner (fail-safe). The automatic protection system should be designed to properly handle likely human errors, hardware failures and operational/environmental stress.
Method and system for analyzing and evaluating electromagnetic interference in power application environment
PendingCN119575013AMeasuring interference from external sourcesEnvironmental/reliability testsData setElectric power system
The invention relates to the technical field of electromagnetic compatibility, in particular to a power application environment electromagnetic interference analysis and evaluation method and system, and the method comprises the following steps: recording the position coordinates of a plurality of power devices based on power grid operation data, collecting the current and voltage data of the operation of the devices, and measuring the electromagnetic field intensity data of a plurality of positions of a power grid; an electromagnetic environment data set is generated. According to the method, the operation data and the electromagnetic field intensity of the power equipment are recorded, the understanding ability of the electromagnetic environment is enhanced, the shielding effect of various materials is accurately evaluated by combining the analysis of the shielding materials, the design and operation of the power equipment are optimized, and the electromagnetic sensitivity of the equipment is evaluated. According to the method, the dynamic distribution of the electromagnetic field is simulated and predicted, the electromagnetic field mode causing a fault is identified, and risk equipment predicted through real-time monitoring and data analysis is combined, so that the stability and safety of a power system are improved, the anti-interference capability is enhanced, and the operation efficiency and function safety of power facilities are improved.

Owner:ELECTRIC POWER SCI RES INST OF STATE GRID XINJIANG ELECTRIC POWER CO LTD
System and method for analyzing cyber security postures and real-time asset validation for critical infrastructure
PCT designated stage expiredWO2024241287A2Platform integrity maintainanceMachine learningData miningConnected device
In an aspect, system and method for analyzing cybersecurity posture for an OT infrastructure is disclosed. The method comprises categorizing a plurality of devices of one or more plants of the OT infrastructure into a plurality of levels, based on an exposure of each device to a communication network, identifying CVEs of components of the plurality of devices, at each level. The method comprises assigning a severity value to the one or more CVEs of components and determining a plant cybersecurity posture score (PCPS) for the one or more plants. The method comprises computing a critical infrastructure cybersecurity posture score for the OT infrastructure. The method comprises applying remediation to one or more vulnerable components based on a prioritization sequence. In another aspect, system and method for real- time asset validation of connected devices in the OT infrastructure is performed based on the device critical parameters, cybersecurity parameters, and functional safety parameters.


Owner:ABB (SCHWEIZ) AG
Security design method of chip, electronic equipment and storage medium
PendingCN118940687AImprove test efficiencyensure safetyCAD circuit designSpecial data processing applicationsSecurity designHemt circuits
The embodiment of the invention relates to the technical field of chip design, and discloses a security design method of a chip, electronic equipment and a storage medium, the method comprises the following steps: obtaining a first circuit design code, and analyzing the first circuit design code to generate a circuit netlist; determining a register list according to the circuit net list; according to the register list, error injection points of each module are extracted to generate an error injection point list; according to the error injection point list, error simulation is conducted on the chip to judge whether the diagnosis coverage rate of the chip meets the function safety design condition or not, if not, the circuit design code is iteratively modified till the diagnosis coverage rate of the chip meets the function safety design condition, the chip testing efficiency can be improved, and the safety of the chip is guaranteed.

Owner:SUTENG INNOVATION TECHNOLOGY CO LTD
Functional safety for system-on-chip arrangements
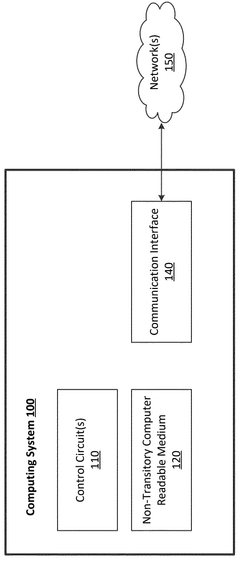
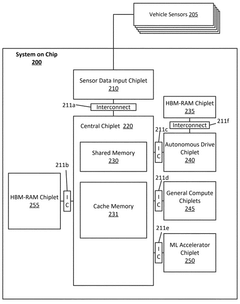
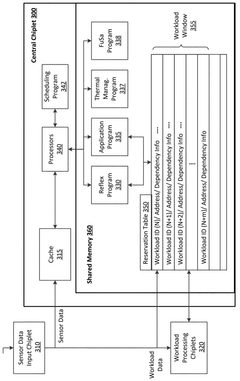
A sensor data input chiplet obtains sensor data from a sensor system. A central chiplet executes a functional safety program to dynamically compare and verify output of workloads being executed by a set of workload processing chiplets, where the workloads are executed across the set of workload processing chiplets based on the sensor data.

Owner:MERCEDES BENZ GROUP AG
Dynamic fault-tolerant control method and system based on expected function security mechanism
PendingCN120681157ABiological modelsKnowledge representationFault detection algorithmDecision control
The invention provides a dynamic fault-tolerant control method based on an expected function safety mechanism, and the method comprises the steps: 1, selecting the model of a sensor, and enabling the sensor to be distributed at the periphery of a vehicle body; 2, building a decision algorithm model, carrying out environment scene recognition, planning a driving path and speed according to data obtained by a sensing layer, evaluating safety risks of different decisions, and carrying out judgment and decision making on various conditions; 3, control interfaces of a vehicle power system, a steering system and a braking system are established, and the electronic control unit converts a decision control instruction output by the decision algorithm model into actual vehicle operation through the control interfaces; 4, performing an expected function safety mechanism, performing real-time monitoring on state parameters of the vehicle, and analyzing detection data through a fault detection algorithm; 5, implementing a fault tolerance strategy; and 6, continuously monitoring the actual driving state and the system response condition of the vehicle, and adjusting the fault tolerance strategy.

Owner:DONGFENG MOTOR GRP +1
Security Escrow System
Various aspects of the disclosure relate to enforcing dynamically updated network security policies in real-time (or upon an identified update) from multiple organizations and anonymously analyze computing system configuration information uploaded from third-party computing systems. An analysis engine monitors compliance information and compare the compliance information against the security rules and / or requirements for one or more enterprise networks. A visualization providing a network map with a visual representation of each product system service system may include communication links between internal applications and / or computing systems and drill-down capability to identify issues as they are occurring or are predicted to occur. The security escrow system may include a mechanism to automatically enable / disable access between third party networks and one or more enterprise computing systems in real-time based on identified compliance information.

Owner:BANK OF AMERICA CORP
Multi-core AMP architecture inter-core communication method and system based on high-security embedded real-time operating system
PendingCN119440869Asimplify complexitysave energyInterprogram communicationProgram loading/initiatingComputer architectureMulticore architecture
The invention provides a multi-core AMP architecture inter-core communication method and system based on a high-security embedded real-time operating system, and the method comprises the steps: respectively operating an authentication version of a Quhua high-security embedded real-time operating system on an AMP heterogeneous multi-core platform, and guaranteeing the real-time performance of a task while providing functional security. And two driving interface mechanisms of IPC Not ify and IPC RPMsg are provided, so that the real-time performance of inter-core communication of the multi-core AMP architecture is improved. The IPC Not ify transmits messages based on the HW mailbox of the HW fifo and interrupts the receiving of core messages, and has low time delay; and a heterogeneous multi-core synchronization function is supported, so that a user does not need to concern the starting sequence of the AMP heterogeneous multi-core system and mainly focuses on development of inter-core communication application programs of the user. The IPC RPMsg provides a two-way communication link based on a channel between the cores, and supports large data volume communication interaction between the cores. A universal shared memory area is configured, and a spinlock technology is adopted to synchronize multi-core operation and prevent multi-core access conflicts. A method for sharing the same physical device by multiple cores is provided, and the problem of insufficient device hardware resources is solved.


Owner:SHANGHAI HUAYUAN CHUANGXIN SOFTWARE CO LTD
Business processing method and device
PendingCN119583077AKey distribution for secure communicationInternal/peripheral component protectionOperational systemSafe operation
The invention discloses a service processing method and device, relates to the technical field of security, can meet the information security requirement of a functional security operating system, improves the security of service processing, and is easy to implement. According to the method, a functional security operating system (a first security operating system) with high functional security and high information security requirements can be migrated to a security world, and high-security and high-credibility services can be processed in the security world. A functional secure operating system (second secure operating system) deployed in a non-secure world can access a TEEOS to execute services through a secure TEE proxy technology, or access a local secure service to execute services.

Owner:YINWANG INTELLIGENT TECHNOLOGIES CO LTD
Risk processing method based on automatic driving, readable storage medium and program product
ActiveCN120135225AExternal condition input parametersDriver input parametersControl systemTesting Methods
The invention provides a risk processing method based on automatic driving, a readable storage medium and a program product, the method is applied to a vehicle, the vehicle is provided with a highly automatic driving (HAD) master control system and an HAD auxiliary control system which are used for controlling automatic driving of the vehicle, and the functional safety level of the HAD master control system is higher than that of the HAD auxiliary control system; the method comprises the steps that under the condition that it is determined that the current operation environment of a vehicle is in a design operation domain of an L3-level conditional automatic driving system, the vehicle is prevented from changing lanes within the user reaction duration after a current control system for automatic driving of the vehicle is controlled to be switched from an HAD main control system to an HAD auxiliary control system; and under the condition that a user takeover instruction is not received, if the operation duration of the HAD auxiliary control system is greater than the user response duration, executing a minimum risk strategy matched with the current operation environment.

Owner:ZHEJIANG GEELY HLDG GRP CO LTD +1
Power supply control method, target domain controller and storage medium
The invention provides a power supply control method, a target domain controller and a storage medium, and relates to the technical field of automatic driving and functional safety. The method is applied to a target domain controller which is connected with multiple power supplies. The method comprises the following steps: determining an automatic driving level of an automatic driving system of a target vehicle; if the automatic driving level is higher than or equal to the target level, determining an effective power supply in the multiple paths of power supplies; if the effective power supply comprises a reference power supply, using the reference power supply to supply power to the target domain controller; and if the effective power supplies do not include the reference power supply, using any one of the effective power supplies to supply power to the target domain controller. The problem of potential safety hazards existing in a single power supply method is avoided, power redundancy is provided for the target domain controller, and it is ensured that the target domain controller can obtain stable and reliable power supply when the automatic driving system is at the key level.

Owner:BEIJING YINWO AUTOMOBILE TECH CO LTD
Power error monitoring and reporting within a system on chip for functional safety
ActiveUS12164370B2Hardware monitoringPower supply for data processingVoltage regulationEmbedded system
Methods, systems and apparatuses may provide for technology that includes a system on chip (SoC) having an integrated voltage regulator and a power management controller, and a first communication path coupled to the power management controller, wherein the first communication path is to carry power error information to the power management controller. The technology may also include a second communication path coupled to an error pin of the SoC, wherein the second communication path is to carry the power error information to the error pin, and wherein the power error information is associated with the integrated voltage regulator.

Owner:INTEL CORP
Test case dynamic priority scheduling method for automobile electronic chip
The invention relates to the field of task queue scheduling of automobile chips, in particular to a test case dynamic priority scheduling method for automobile electronic chips. Comprising the following steps: analyzing standard test data of the automobile electronic chip, and organizing a structured data set associated with the physical layout of the chip; identifying failure clusters and noise points on the structured data set by using a data clustering algorithm; extracting geometric and position features of the failure cluster, classifying the failure cluster into a known failure mode by using a classifier, performing correlation analysis on the failure mode, an upstream key process step and an equipment log, and establishing a causal relationship; calculating a function security risk score for each chip; and when the function security risk score is higher than a preset risk threshold value, generating and executing a dynamic task rearrangement instruction, and dynamically improving the execution priority of the test case. According to the method, the priority is dynamically selected according to the function security risk score through the dynamic task rearrangement instruction, so that the test time is saved, and the coverage depth and quality of the test are improved.

Owner:JIANGSU HAINA ELECTRONICS TECH CO LTD
Function safety cloud platform for rail transit real-time control system and control method
PendingCN119440850Aimprove securityImprove reliabilityResource allocationSoftware simulation/interpretation/emulationCommunications securityVirtualization
The invention relates to a functional security cloud platform and a control method for a rail transit real-time control system, the cloud platform follows a fault-security principle during design and meets the requirements of EN50129 functional security SIL4 level, and the cloud platform comprises a communication gateway used for providing a unified access entrance; the safe real-time virtualization system is used for virtual management, clock self-inspection and interrupt distribution; the security middleware runs in a virtual machine distributed by the security real-time virtualization system and is used for security clock verification, CPU memory self-check result verification, security communication, security voting, cycle control and application management; and the cloud management platform is matched with a virtual machine management module in the secure real-time virtualization system to jointly realize management of virtualization resources. Compared with the prior art, the method has the advantages of high safety, high reliability, high availability, high maintainability, high performance and the like.

Owner:CASCO SIGNAL LTD
Apparatus, system, and method of functional safety
For example, an apparatus may include a motherboard including a functional processing core configured to perform a functionality having a Functional Safety (FuSa) level; a FuSa transceiver configured to communicate with an external safety-island processor, which is external to the motherboard; and a FuSa controller configured to establish a FuSa connection with the external safety-island processor according to the FuSa level, to send FuSa information corresponding to the functionality of the functional processing core to the external safety-island processor via the FuSa transceiver, and to control one or more FuSa operations of the functional processing core based on one or more control messages received from the external safety-island processor via the FuSa transceiver.

Owner:INTEL CORP
Vehicle-mounted controller memory monitoring method based on differential redundancy
The invention provides a vehicle-mounted controller memory monitoring method based on differential redundancy, and relates to the technical field of electric monitoring, and the method comprises the following steps: constructing a multi-dimensional graph representation and feature dictionary of a memory region; utilizing reinforcement learning to adaptively optimize a monitoring strategy according to a real-time state and a prediction risk; executing multi-level differential verification of context awareness, and taking a verification result as an observation evidence; performing deep fault probability prediction and interpretability analysis by adopting a graph neural network; through Bayesian or fuzzy logic intelligent fusion verification observation and model prediction, high-confidence risk assessment is realized; and active protection instructions such as predictive error correction and fault isolation are generated and triggered based on an evaluation result and closed-loop feedback. According to the scheme, prediction, adaptation, efficient verification and intelligent decision making are integrated, the foreseeability, adaptability, efficiency and robustness of vehicle-mounted memory monitoring are remarkably improved, and a comprehensive and advanced guarantee is provided for function safety and information safety of a vehicle.


Owner:CHONGQING YISHI INTELLIGENT TECHNOLOGY CO LTD
Multi-dimensional security fusion risk assessment method and related equipment
The invention discloses a multi-dimensional safety fusion risk assessment method and related equipment, and relates to the technical field of automatic driving, and the method comprises the steps: obtaining a first data set and a second data set of a target system; performing functional security risk analysis, expected functional security risk analysis and information security risk analysis on the first data set to identify a hazardous event of the target system; based on the second data set, establishing a dynamic scene model, and obtaining a threat level of the hazard event through the dynamic scene model; constructing a multi-dimensional risk matrix according to the hazard event, the dynamic scene model and the threat level; and obtaining a risk value of the hazard event based on the multi-dimensional risk matrix, and performing risk grade division according to the risk value to obtain a multi-dimensional security risk assessment result of the target system.

Owner:VOYAH AUTOMOBILE TECH CO LTD
Safe torque cut-off and electronic star sealing device and elevator system
The invention discloses a safe torque cut-off and electronic star sealing device and an elevator system, relates to the technical field of elevators, and is used for realizing STO and electronic star sealing functions. Aiming at the problem that a common contactor-free scheme at present cannot ensure the function safety, the invention provides the safe torque cut-off and electronic star sealing device, and the STO and electronic star sealing functions of an elevator are ensured through a safe torque cut-off module and an electronic star sealing module. Meanwhile, failure detection is carried out on the two newly-added modules through the control module, and a mutual detection mechanism between the control module and the safe torque cut-off module is established. When any one of the three newly added modules fails, the failure can be detected and the STO or electronic star sealing function is triggered. On the basis, all modules used for replacing a traditional contactor to achieve STO and electronic star sealing functions in the device establish failure detection mechanisms, so that the device can meet the requirement of the elevator for the function safety level.

Owner:INVT POWER ELECTRONICS SUZHOU CO LTD
A microprocessor fault recovery device and method, and a chip
The present invention provides a microprocessor fault recovery device and method, and a chip, including a microprocessor CPU with a dual-core lock-step structure, a field backup module, and a safety management module; when running to a preset recovery point in the program code, the field backup module records the location of the recovery point and the values of important parameters in the current field environment; when receiving a CPU fault indication, the safety management module notifies the CPU to suspend operation and notifies the field backup module to restore the field; the field backup module overwrites the corresponding current data with the backup data; after receiving a successful response to field recovery, the safety management module adjusts the program counter to the location of the recovery point and restarts the CPU. The present invention can quickly bring the system back to a safe operating state when a CPU error occurs, thereby improving the robustness of automotive-grade functional safety.

Owner:XINKE INTEGRATED CIRCUIT (SUZHOU) CO LTD
MCU function safety realization system based on domain controller
The invention provides an MCU function security implementation system based on a domain controller, and relates to the technical field of domain controllers, the system realizes dual backup storage and on-site execution of program codes by combining a security MCU without a built-in program memory with at least two redundant plug-in nonvolatile storage units, and the security of the MCU is improved. Consistency verification is carried out on key codes or data in the running process, and system failure caused by single-point storage faults or data tampering is effectively prevented; meanwhile, read-write operation without losing data during power failure is isolated through the independent data storage unit, and resource conflict and interference between program execution and data storage are avoided; the ASIL D-level power management unit supporting two-way fault monitoring is matched, resetting can be triggered in time or the MCU enters a safe state when a power supply is abnormal or an MCU internal fault occurs, and therefore a high-reliability and high-safety domain controller MCU system is constructed on the hardware architecture level, and the capacity of the MCU for meeting the ASIL D function safety level in a plug-in storage scene is improved.

Owner:CHINA FAW CO LTD
Business processing methods, and apparatuses
PCT designated stage expiredWO2025044529A1Key distribution for secure communicationInternal/peripheral component protectionOperational systemSafe operation
Business processing methods, and apparatuses, which relate to the technical field of security, and can meet the information security requirement of a functional safety operating system, thus improving the security of business processing, and being easy to implement. The methods can migrate a functional safety operating system (a first safety operating system) having high functional safety and high information security requirements to a secure world, such that high-security and highly-trusted businesses can be processed in the secure world; a functional safety operating system (a second safety operating system) deployed in a non-secure world can access a TEEOS to execute businesses by means of a secure TEE proxy technology, or access a local security service to execute businesses.

Owner:YINWANG INTELLIGENT TECHNOLOGIES CO LTD
Intelligent redundancy control system and method based on functional safety
The invention provides an intelligent redundancy control method based on functional safety, and the method comprises the steps: 1, collecting key parameters in real time, and outputting a safety score S according to a fuzzy logic formula S = 0.3 XTnorm + 0.2 Vstable + 0.5 Cdelay; 2, preprocessing the key parameters, the safety score, the environmental data and the historical fault records, constructing a risk assessment model through the preprocessed data, and performing risk grade division; 3, triggering redundancy strategy adjustment according to the risk level and the safety score; and step 4, when the redundancy strategy is adjusted to a high-risk scene, triggering switching logic through hardware interruption, and completing redundancy control. According to the technical scheme provided by the invention, the problems that the existing scheme is high in cost, slow in response, incapable of adapting to a dynamic risk environment and easy to cause simultaneous failure of multiple nodes are effectively solved.

Owner:DONGFENG MOTOR GRP +1
Vehicle expected function safety data driven closed-loop solving method, system and equipment and storage medium
PendingCN120806628AInternal combustion piston enginesDesign optimisation/simulationData-drivenTesting Methods
The invention discloses a vehicle expected function safety data-driven closed-loop solving method, system and equipment and a storage medium, belongs to the technical field of vehicle expected function safety, and solves the technical problem that in the prior art, a closed-loop expected function safety problem solving method for carrying out data driving on actually occurring hazardous events is lacked. Acquiring driving data before and after the vehicle encounters the hazard event; performing functional deviation analysis and trigger condition induction on the preprocessed driving data; making a multi-dimensional system optimization scheme; and when a hazard event occurs in the vehicle, performing recharge analysis on the driving data to obtain a residual risk which cannot accept an expected response and a residual risk which can accept an expected response, updating a multi-dimensional system optimization scheme, optimizing a vehicle function module, performing hazard identification and risk assessment, and putting the vehicle into operation after the vehicle passes the hazard event. The method is used for realizing system function boundary continuous expansion and safety capability evolution, and guaranteeing the expected function safety of the vehicle in the whole service cycle.

Owner:JILIN UNIVERSITY
Chip security mechanism evaluation method and computer equipment
ActiveCN119557928AImprove efficiencyImprove stabilityInternal/peripheral component protectionMachine learningHistorical modelEmbedded system
The invention discloses a chip security mechanism evaluation method and computer equipment. The method comprises the following steps: acquiring test data of chips of the same series and historical models; extracting characteristic variables of test data of chips of historical models, and establishing a prediction model based on machine learning for evaluating the validity of a chip security mechanism; acquiring test data of a novel chip with the same data structure as the sample data; and inputting the test data of the novel chip into the established prediction model for prediction, and outputting a prediction result as an index of the validity of the chip security mechanism. According to the invention, rapid function security detection and evaluation can be realized for the same series of novel chips, and the function security detection efficiency and stability of the novel chips in a small sample scene are remarkably improved.

Owner:CHINA ELECTRONICS RELIABILITY AND ENVIRONMENTAL TESTING INSTITUTE ((THE FIFTH INSTITUTE OF ELECTRONICS MINISTRY OF INDUSTRY AND INFORMATION TECHNOLOGY) (CHINA SAIBAO LABORATORY)
Access control method realized through hardware firewall and in-chip hardware firewall
The embodiment of the invention provides an access control method realized through a hardware firewall and a hardware firewall in a chip, the method comprises the following steps: receiving an access request initiated by an access end to an accessed end through a firewall filter layer corresponding to the access end, the access request carrying a permission identifier and an access address; determining a target access area from a plurality of access areas of an accessed end corresponding to the firewall filter layer according to the access address; the access authority of the access request is determined according to the authority identification and the target access area, and each access area is pre-configured with a mapping relation between the authority identification allowed to be accessed and the corresponding access authority. Through the embodiment of the invention, the problems that a hardware firewall is single in function and limited in authority control and function security effect can be solved, the access end and the accessed end are controlled at the same time by setting the authority identifier and the corresponding access authority, and the information security and the function security of the whole chip system are improved.

Owner:SANECHIPS TECH CO LTD
Functional safety for system-on-chip arrangements
PCT designated stage expiredWO2024260605A1Program initiation/switchingHardware monitoringWorkloadEmbedded system
A sensor data input chiplet obtains sensor data from a sensor system. A central chiplet executes a functional safety program to dynamically compare and verify output of workloads being executed by a set of workload processing chiplets, where the workloads are executed across the set of workload processing chiplets based on the sensor data.
Owner:MERCEDES BENZ GROUP AG
Functional safety in autonomous driving
PendingJP2025083347ABiological neural network modelsAnti-collision systemsFunctional safetyReal-time computing
To meet requirements for improvement of a vehicle having autonomous driving capability.SOLUTION: Autonomous driving of a vehicle in which computerized perception by the vehicle, including of its environment and of itself (e.g., egomotion), is used to autonomously drive the vehicle and, additionally, can also be used to provide feedback to enhance performance, safety, and / or other attributes of autonomous driving of the vehicle (e.g., when certain conditions affecting the vehicle are determined to exist by detecting patterns in or otherwise analyzing what is perceived by the vehicle), by adjusting autonomous driving of the vehicle, conveying messages regarding the vehicle, and / or performing other actions concerning the vehicle.SELECTED DRAWING: Figure 1

Owner:VAYAVISION SENSING LTD
Integrated circuit, resource access control method, device and medium
PendingCN119416256Aensure safetyimprove securityDigital data protectionInternal/peripheral component protectionEngineeringSecurity properties
The embodiment of the invention discloses an integrated circuit, a resource access control method, equipment and a medium, and the method comprises the steps: in response to a received resource access request sent by a requester, based on pre-configured access authority control information, determining whether the requester has an access authority for a resource party corresponding to an access address requested by the requester, and obtaining a first determination result; and in response to the request party having the access authority to the resource party, determining whether the request party has the operation authority to the access address based on pre-configured security control information and security attribute information in the resource access request to obtain a second determination result, and processing the resource access request based on the second determination result, according to the invention, the security of functions with high security level requirements can be effectively guaranteed, and the information security and the function security can be improved.

Owner:XG TECHNOLOGIES PTE LTD
Intelligent network connection automobile threat perception test method and system based on endogenous safety
ActiveCN119071086Aimprove accuracyguarantee fairnessInstruments for road network navigationNavigation by speed/acceleration measurementsIntelligent NetworkTest execution
The invention discloses an intelligent network connection automobile threat perception test method and system based on endogenous safety, and the method comprises the steps: constructing a plurality of standard parts which are the same as a tested part in category according to the category of the tested part in an intelligent network connection automobile, and carrying out the initialization of the tested part and the standard parts; standardized cases are distributed to the initialized tested piece and the standard piece for multiple rounds of testing, testing results of the tested piece and the standard piece are obtained in each round of testing, and after the testing is executed, a judgment result of the tested piece is obtained according to a judgment method and a judgment basis for all the testing results; and outputting and feeding back the judgment result. Based on a dynamic, heterogeneous and redundant architecture of endogenous security, vulnerability / defect sensing, discovery and preliminary positioning of key parts of a vehicle can be completed without depending on a prior knowledge base, and an integrated guarantee is provided for functional security and network security.

Owner:ZIJIN ZHILIAN (NANJING) TECHNOLOGY CO LTD
Rail transit safety computer platform supporting multiple applications and control method
PendingCN119512694Asimple designVersatilityResource allocationPlatform integrity maintainanceMultiple applicationsEmbedded system
The invention relates to a rail transit safety computer platform supporting multiple applications and a control method, the platform follows a fault-safety principle during design, supports multiple applications and conforms to an EN50129 functional safety SIL4 level, and the computer platform comprises a communication gateway used for providing a unified access entrance; the MPU operation subsystem comprises a redundant backup A system and a redundant backup B system, each system comprises two MPU units, and each MPU unit comprises a platform management virtual machine and N application virtual machines; the switching unit is used for switching the main and standby states of the A system and the B system; and the redundant network is respectively connected with the communication gateway, the MPU operation subsystem and the switching unit to realize internal communication. Compared with the prior art, the method has the advantages of supporting multiple applications, enabling the whole system to be more flexible and the like.

Owner:CASCO SIGNAL LTD
Motormeter screen operation state monitoring method, intelligent cabin and vehicle thereof
PendingCN119078515AImprove reliabilityimprove securityVehicle componentsTransmissionMicrocontrollerDashboard
The invention discloses an automobile instrument screen operation state monitoring method, an intelligent cabin and a vehicle thereof, and the method comprises the steps: periodically querying the operation state of an automobile instrument screen module MFD through an IIC communication protocol by using a microcontroller unit MCU in a cabin domain controller CSC; judging whether the message interaction between the MCU and the MFD is successful or not; and when the heartbeat signal is detected to be lost, the microcontroller unit MCU performs hard wire resetting on the automobile instrument screen module MFD through the hard wire IO. In conclusion, the requirement for the safety integrity level of the automobile is considered, the safety of the automobile in the running process is remarkably improved through accurate fault detection and timely recovery measures, the requirement for functional safety is met, potential accidents caused by instrument screen faults are reduced, and the safety of the automobile is improved. And higher-level safety guarantee is provided for drivers and passengers.

Owner:CHINA FAW CO LTD +1